
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
45 results
confluencePot preview

confluencePot

GitHubsifalcon/confluencepot

Simple Honeypot for Atlassian Confluence (CVE-2022-26134)
defensive-toolsvulnerability-analysis
204 years ago
cryptoptic preview

cryptoptic

GitHubnationwide-group-oss/cryptoptic

CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
code-analysisconfiguration-auditingcryptography+6
7 days ago
leaky-vessels-dynamic-detector preview
Archived

leaky-vessels-dynamic-detector

GitHubsnyk/leaky-vessels-dynamic-detector

eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
cloud-securitycontainer-securitydefensive-tools+3
1051 year ago
fil-c preview

fil-c

GitHubpizlonator/fil-c

Fil-C: completely compatible memory safety for C and C++

defensive-toolsdynamic-code-analysisvulnerability-analysis
3.9k13h 24m ago
HandleKatz preview

HandleKatz

GitHubcodewhitesec/handlekatz

PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
defensive-toolsmemory-forensicspayload-generation+3
5973 years ago
memhunter preview

memhunter

GitHubmarcosd4h/memhunter

Live hunting of code injection techniques
defensive-toolsincident-responsemalware-analysis+1
3837 years ago
RegEx-DoS preview

RegEx-DoS

GitHubjagracey/regex-dos

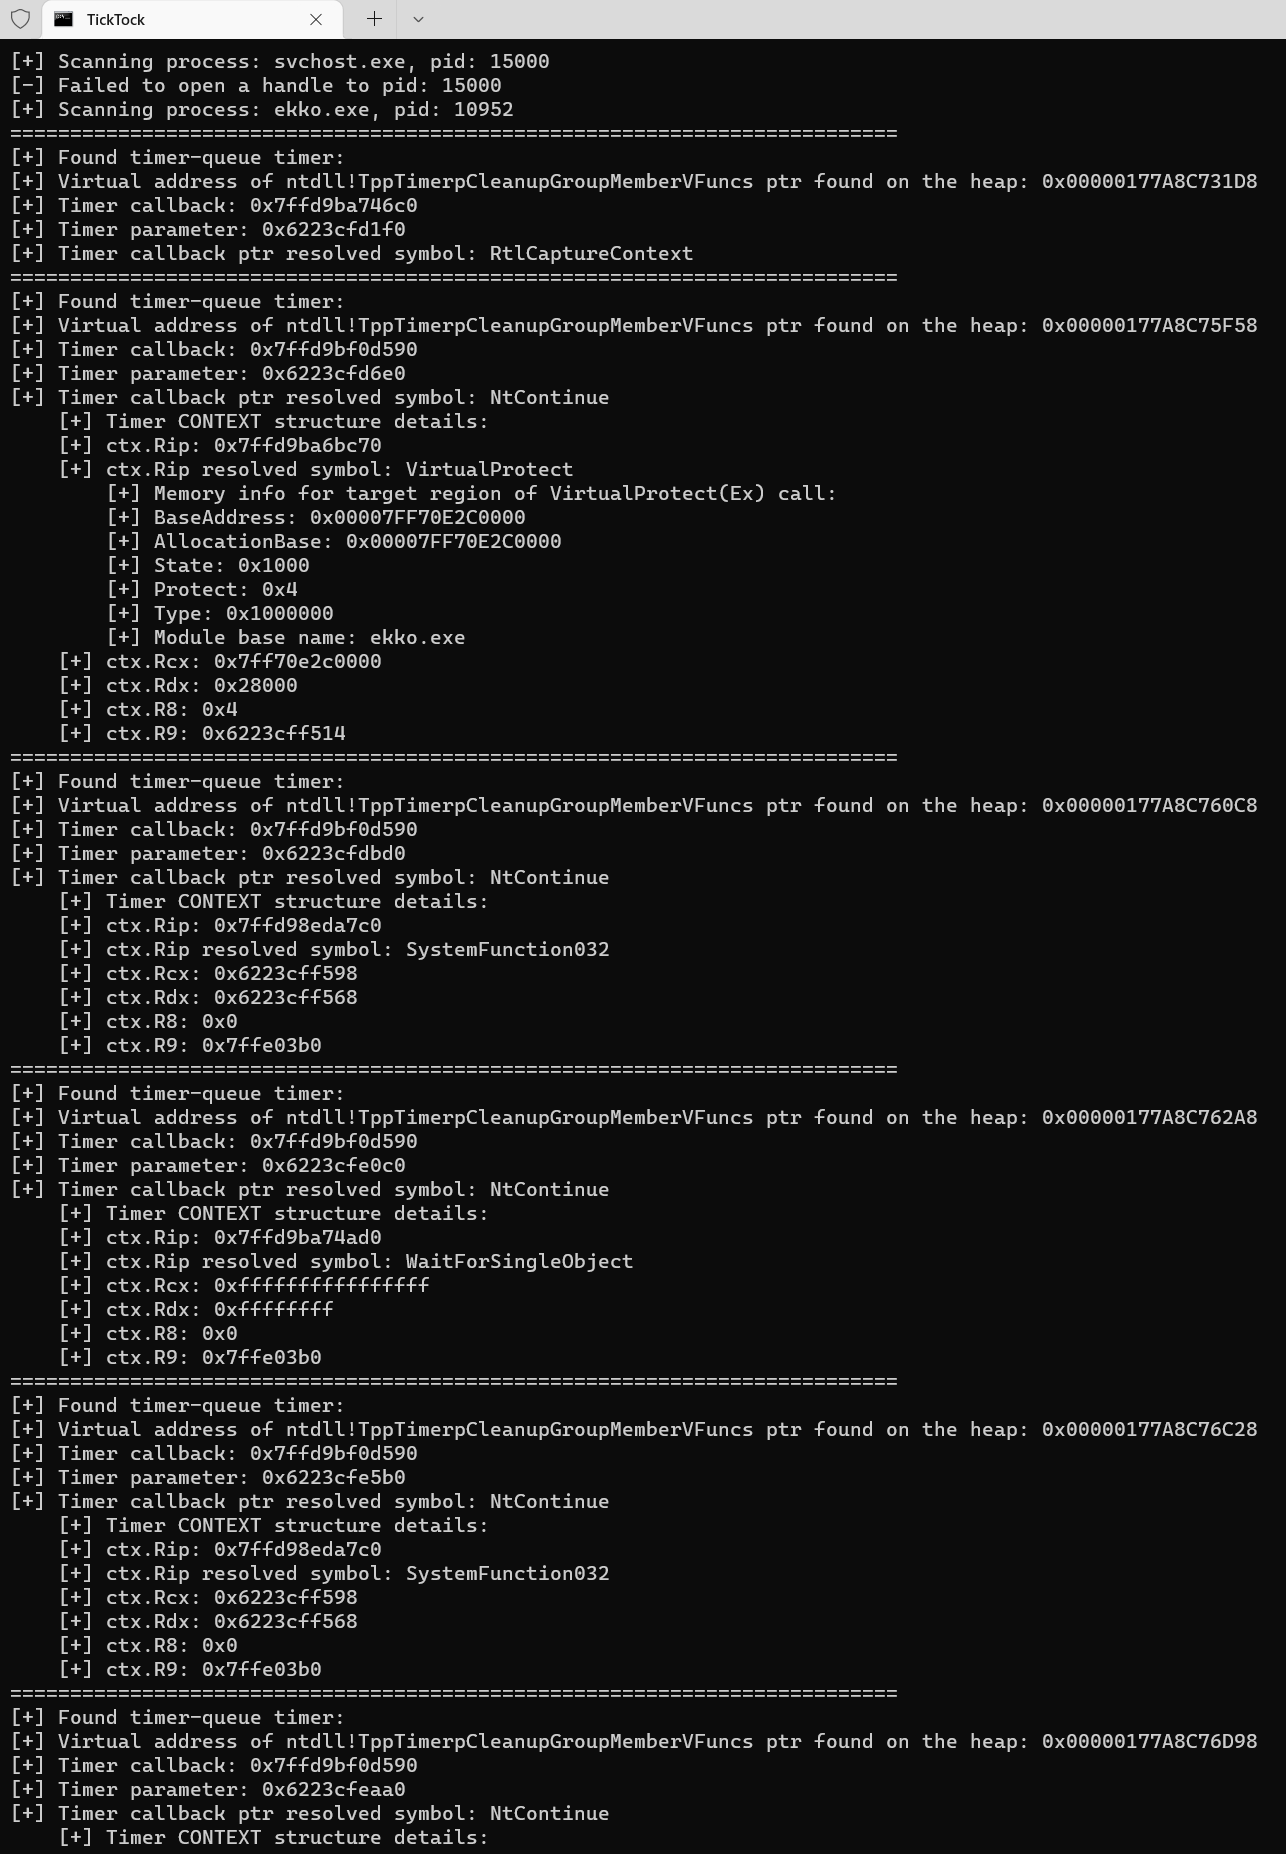
👮 👊 RegEx Denial of Service (ReDos) Scanner
defensive-toolsdevsecopsstatic-code-analysis+2
1828 years ago
TickTock preview

TickTock

GitHubwithsecurelabs/ticktock

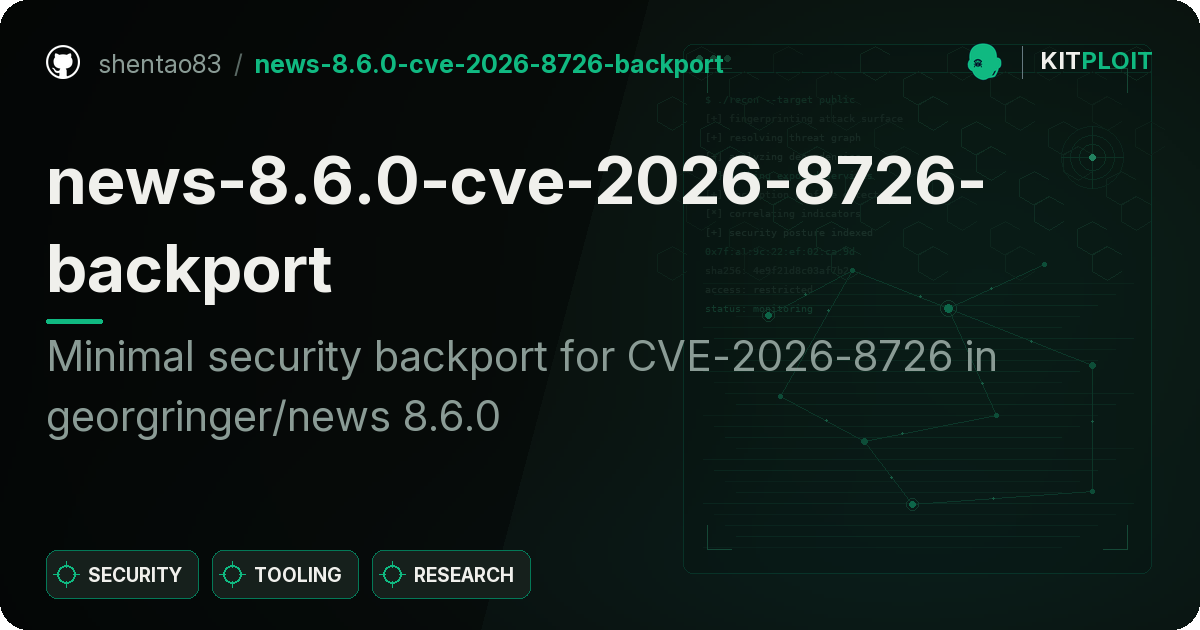
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…

defensive-toolsmalware-analysismemory-forensics
1133 years ago
antipwny preview

antipwny

GitHubrvazarkar/antipwny

A host based IDS written in C# Targetted at Metasploit
defensive-toolsintrusion-detectionmalware-analysis+3
4412 years ago
news-8.6.0-cve-2026-8726-backport preview

news-8.6.0-cve-2026-8726-backport

GitHubshentao83/news-8.6.0-cve-2026-8726-backport

Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
database-securitydefensive-toolsstatic-code-analysis+3
10 days ago
CVE-2025-23134_fixes_code preview

CVE-2025-23134_fixes_code

GitHubthrilokh-q123/cve-2025-23134_fixes_code

The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().
code-analysiscryptographydefensive-tools+2
18 days ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
22 years ago
cobol-shield preview

cobol-shield

GitHubluiscastellanos-dev/cobol-shield

Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity

defensive-toolsdevsecopsstatic-code-analysis+2
1 month ago
EDRSandblast-GodFault preview
Archived

EDRSandblast-GodFault

GitHubgabriellandau/edrsandblast-godfault

EDRSandblast-GodFault

defensive-toolsexploitationmemory-forensics+4
2733 years ago
Out-FINcodedCommand preview

Out-FINcodedCommand

GitHubdanielbohannon/out-fincodedcommand

POC Highlighting Obfuscation Techniques used by FIN threat actors based on cmd.exe's replace functionality and cmd.exe/powershell.exe's stdin command…

command-and-controldefensive-toolseducation+2
1089 years ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
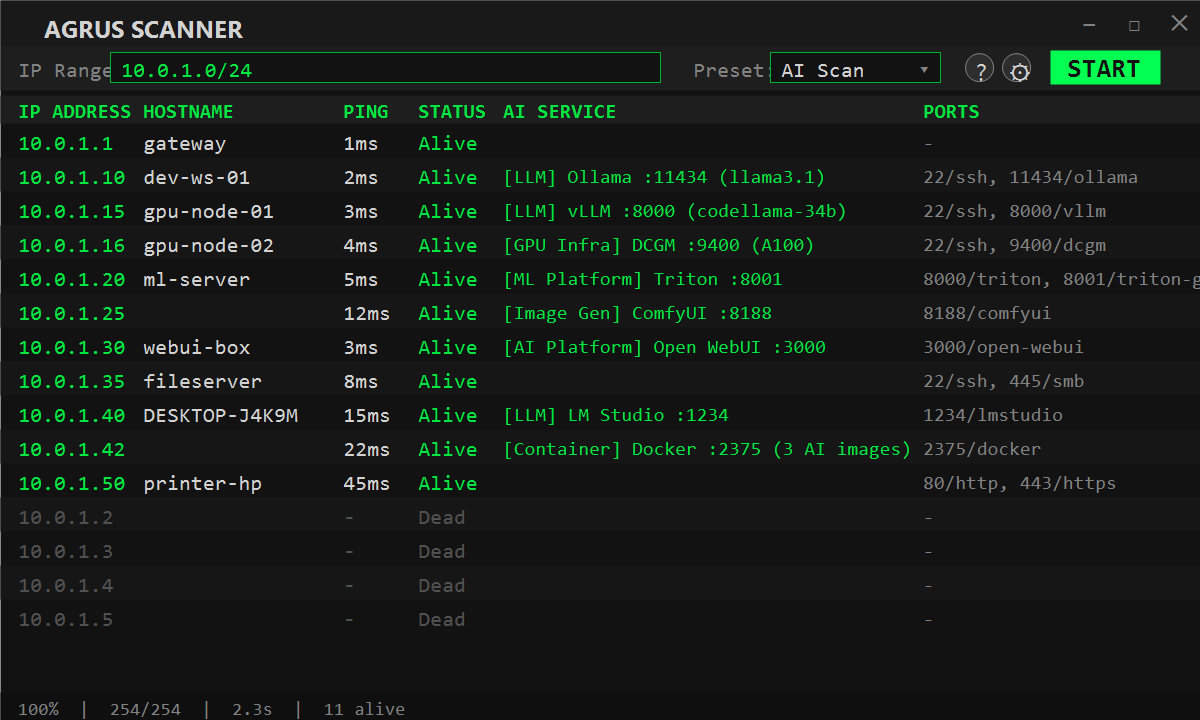
AgrusScanner preview

AgrusScanner

GitHubnybaywatch/agrusscanner

Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
ai-securitydefensive-toolsinformation-gathering+6
264 days ago
uefi_bootkit_softlanding preview

uefi_bootkit_softlanding

GitHubares-sys/uefi_bootkit_softlanding

First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…

defensive-toolsdigital-forensicsfirmware-analysis+5
1 month ago
Previous123Next