

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 openresty/lua-resty-limit-traffic
Lua library for limiting and controlling traffic in OpenResty/ngx_lua
 mirage/qubes-mirage-firewall
Minimal unikernel firewall for QubesOS that filters network traffic, implements NAT, and communicates via Qubes DB and qrexec.
 ghaziwali/hulios
A Rust-based transparent Tor proxy that routes all system traffic through the Tor network enhanced security, proper DNS isolation, and modern Linux…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 objective-see/lulu
Open-source macOS firewall that monitors and controls network connections, blocking unauthorized outbound and inbound traffic with per-application…
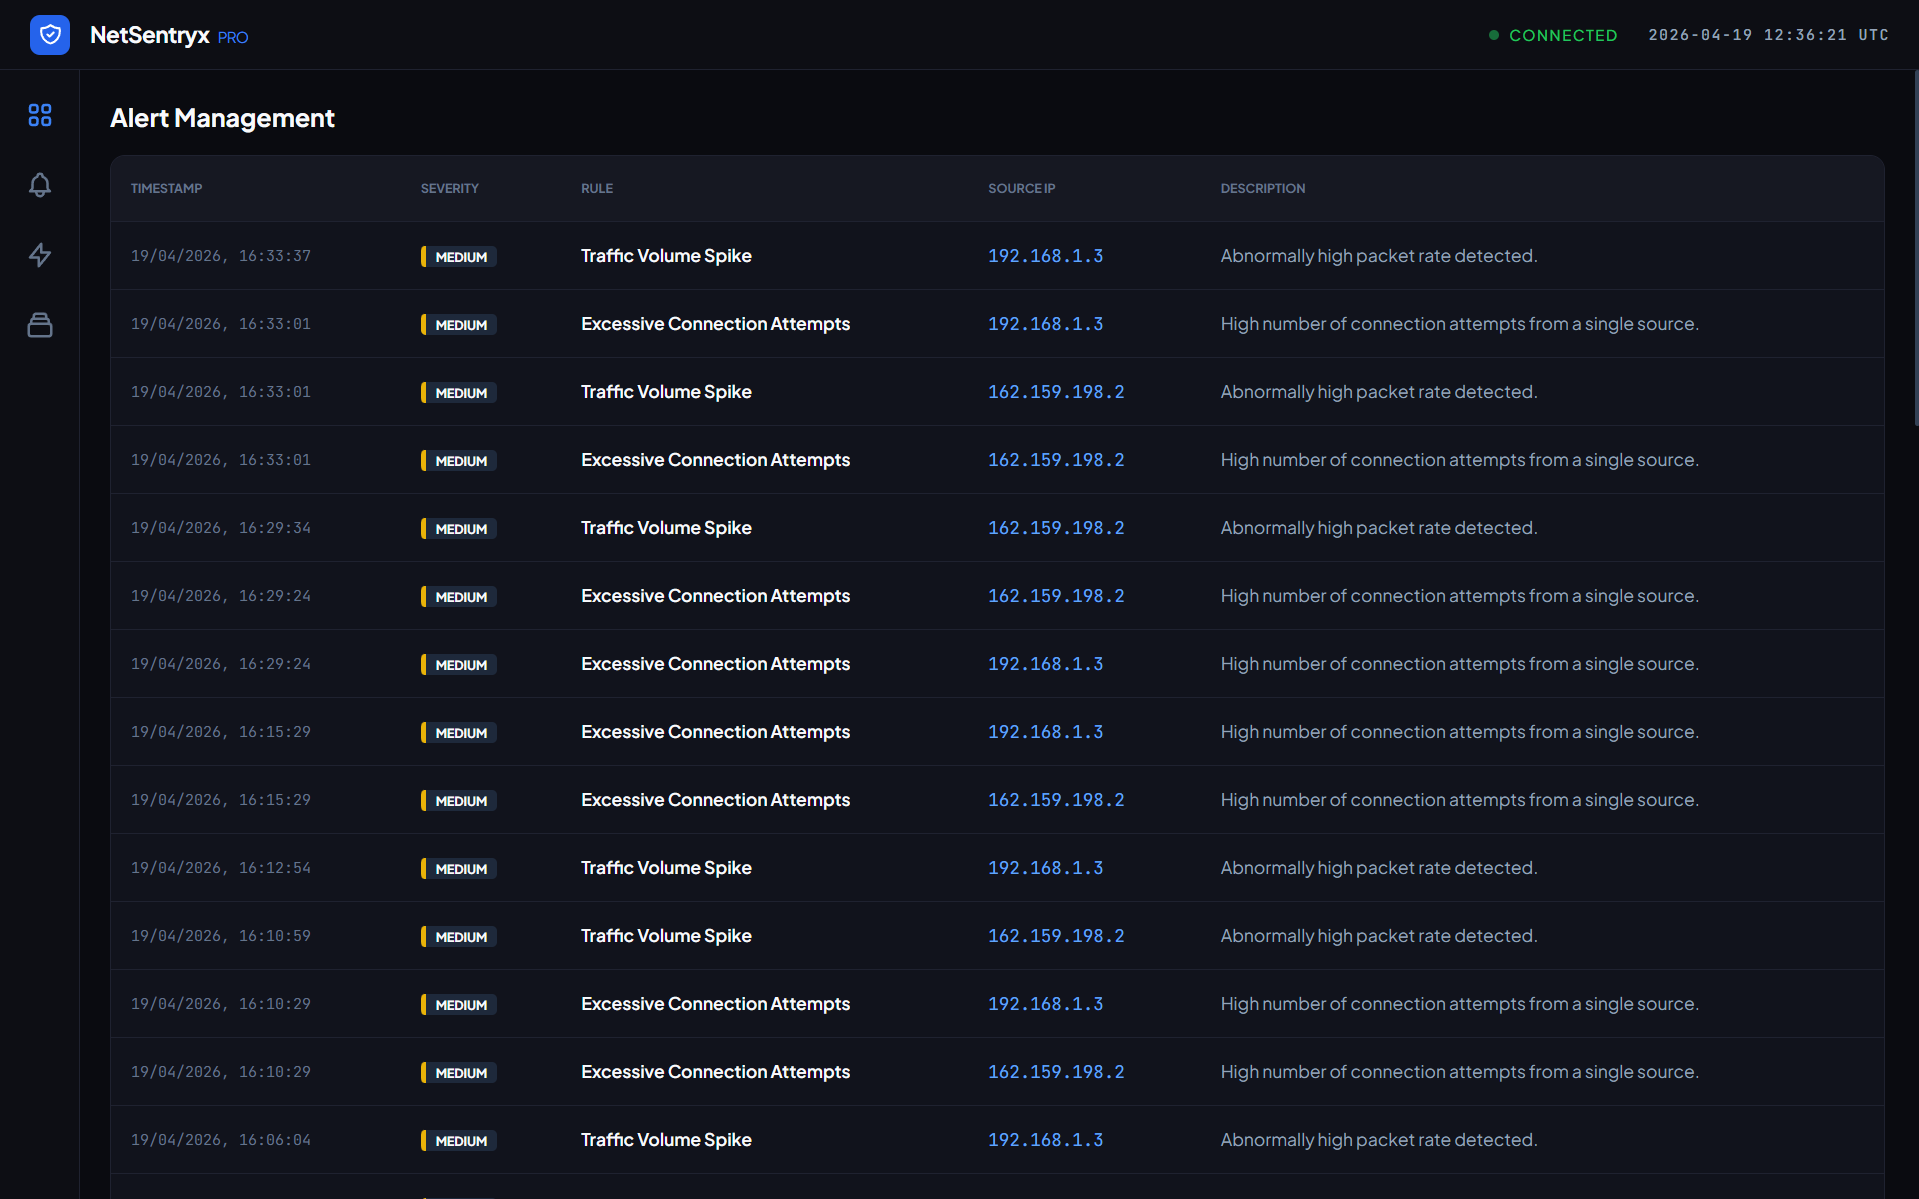 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 vxfemboy/ghostport
A high-performance port spoofing tool built in Rust. Confuse port scanners with dynamic service emulation across all ports. Features customizable…
 corelight/zeek-mercury-npf
Zeek plugin generating Mercury NPF fingerprints for TCP, TLS/DTLS, QUIC, HTTP, SSH, OpenVPN, and STUN to support network security monitoring.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 corelight/corelightforsentinelone
Corelight Dashboards and Parsers for Sentinel One Singularity
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.
 snort3/snort3
Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…