
CVE-2026-87902-Toolkit
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
defensive-toolseducationexploitation+8
1
tc4dy/cve-2026-87902-toolkitWordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
 kwilck/copyfail
Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 amdisrar/cve-2026-31431-mitigation
Temporary mitigation for Linux kernel local privilege escalation CVE-2026-31431 (AF_ALG interface)
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
 kougyokugentou/cve-2021-1675
A small powershell script to disable print spooler service using desired state configuration
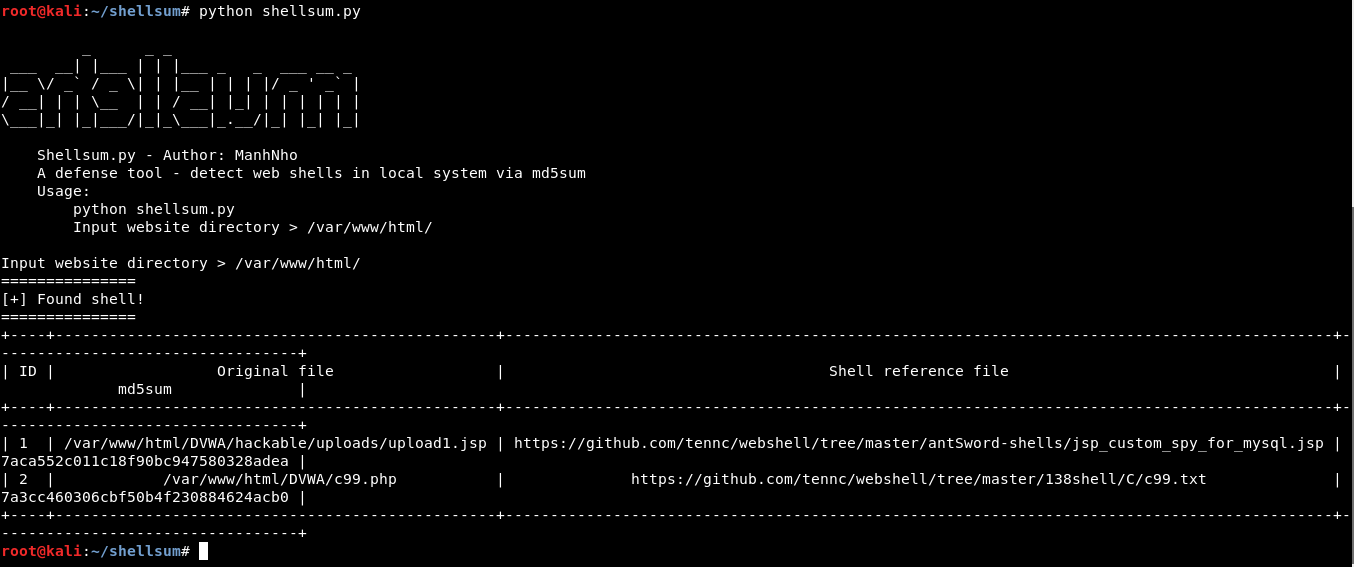 manhnho/shellsum
A defense tool - detect web shells in local directories via md5sum