

C2IntelFeeds
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
command-and-controldefensive-toolsincident-response+6
749
drb-ra/c2intelfeedsAutomatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 ooni/probe-cli
Go measurement engine and CLI for detecting Internet censorship and network interference, running OONI network tests and reporting results to the…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 specterops/bloodhound
Six Degrees of Domain Admin
 nybaywatch/agrusscanner
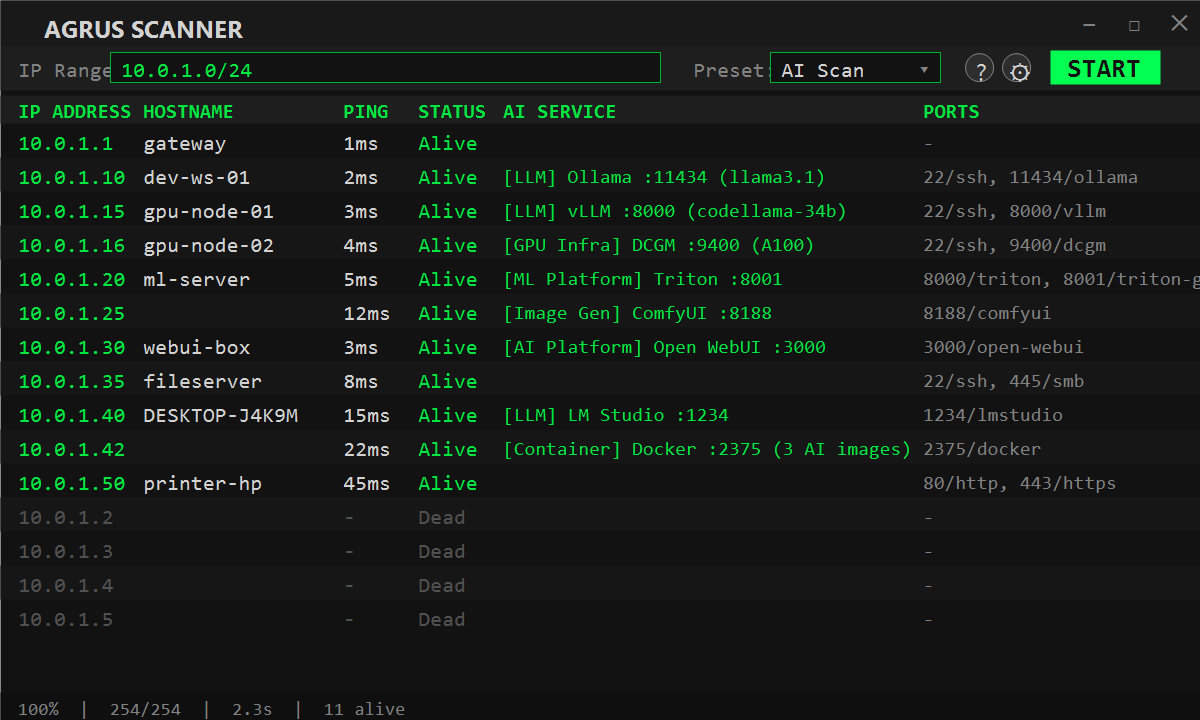
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 outflanknl/redelk
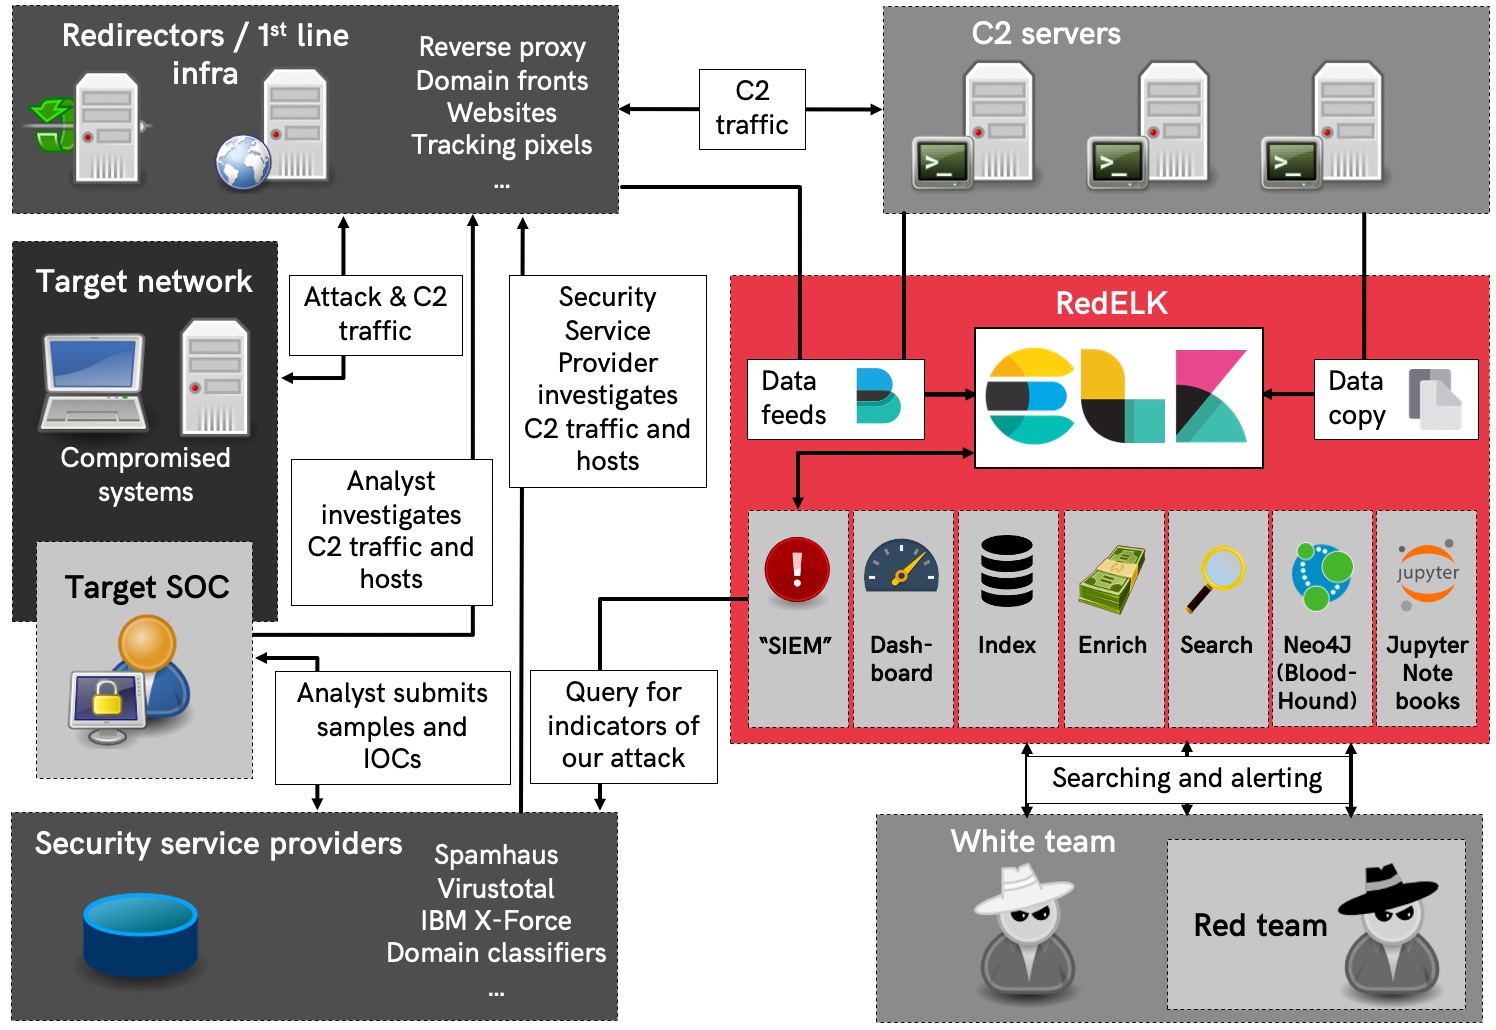
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
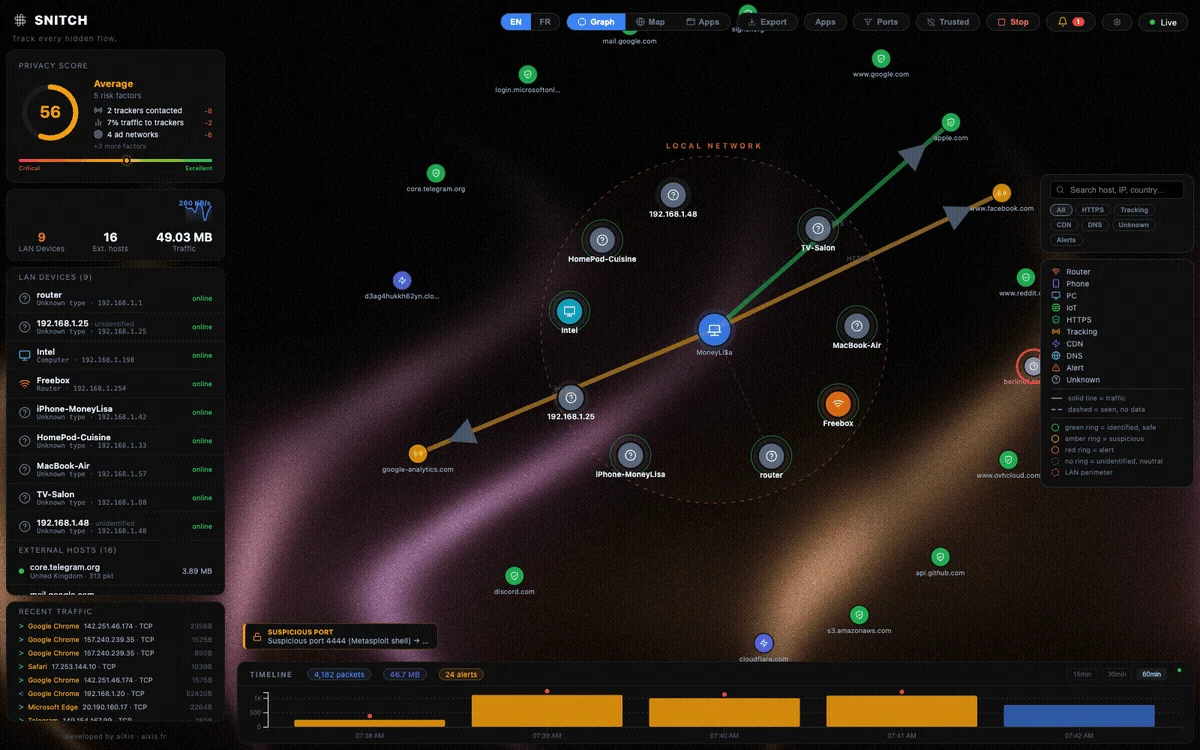 aixisstudio/snitch
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 ransomlook/ransomlook
Yet another Ransomware gang tracker
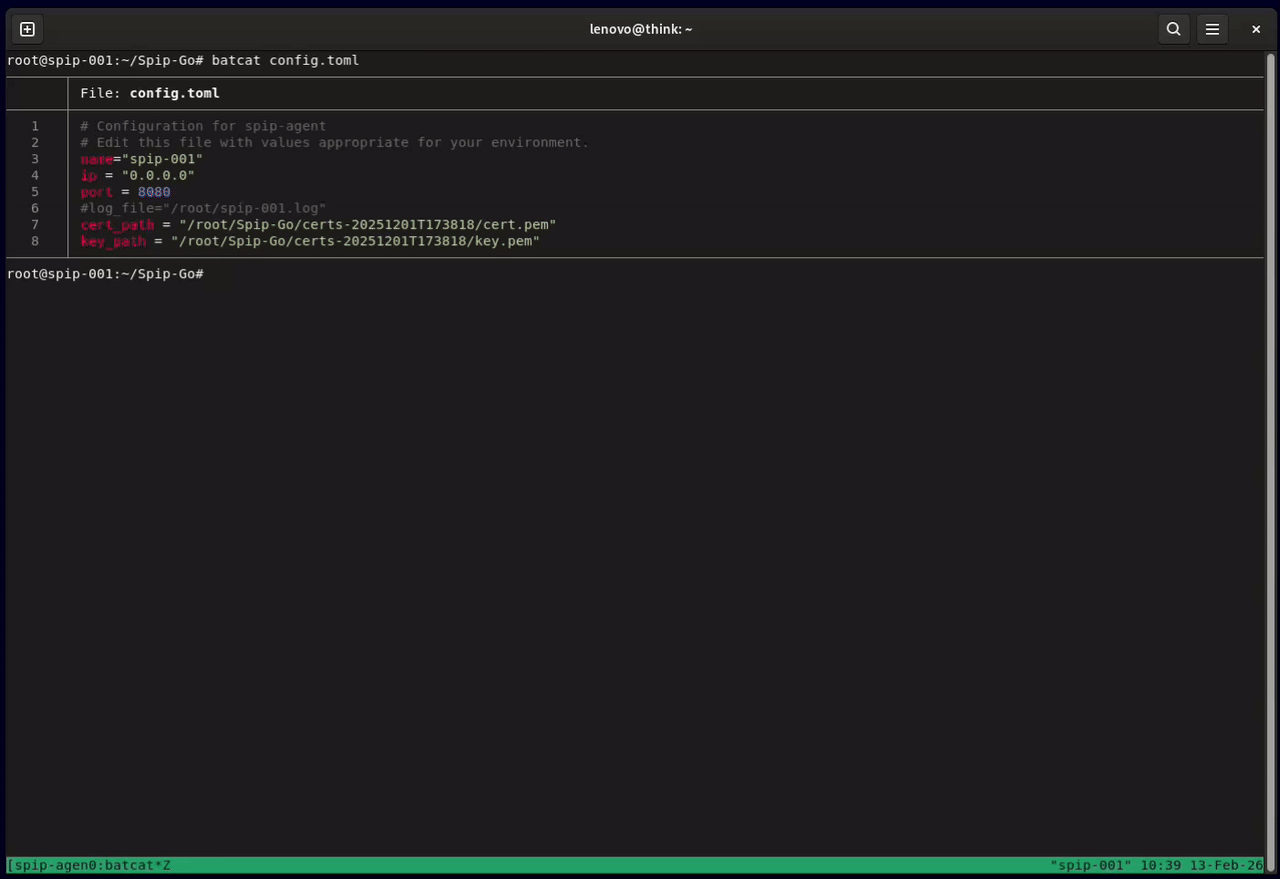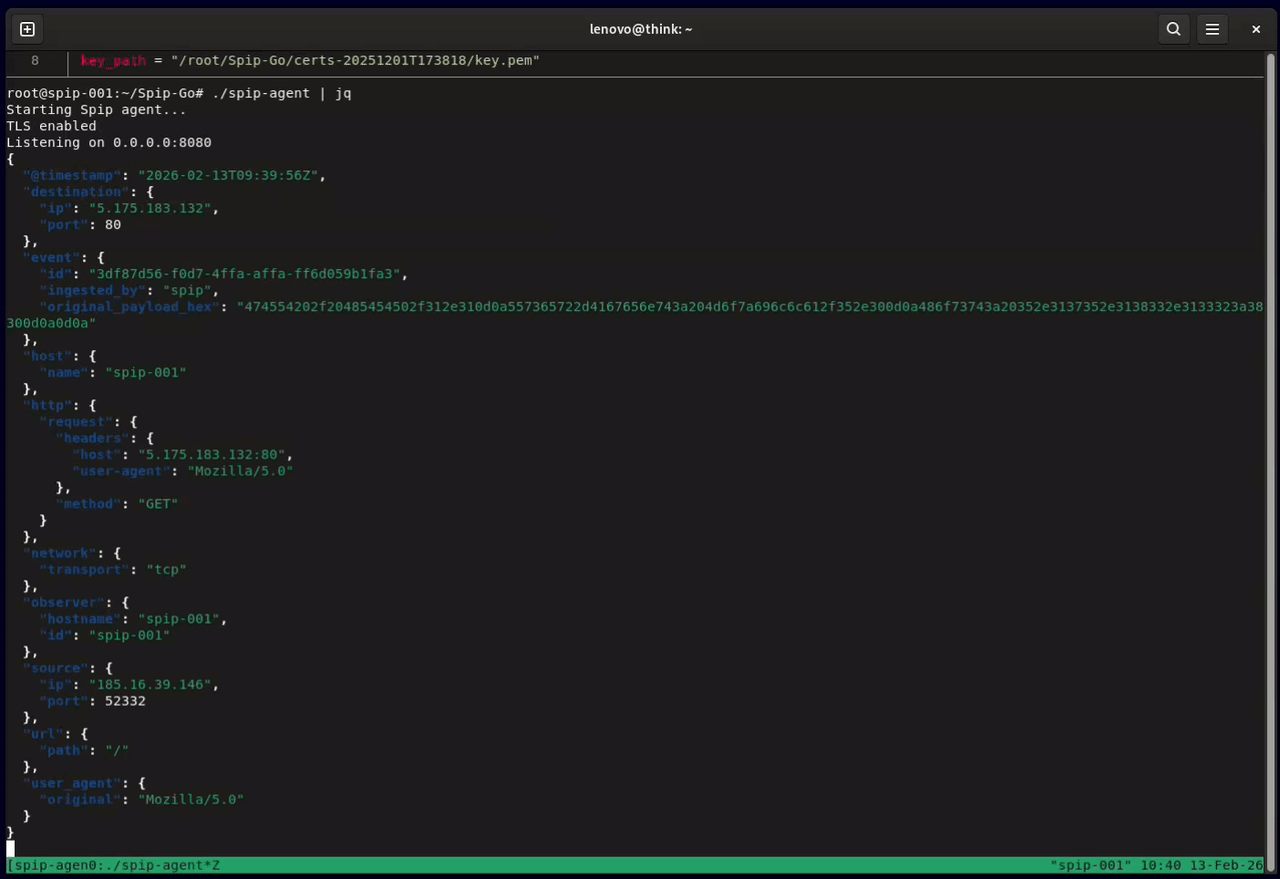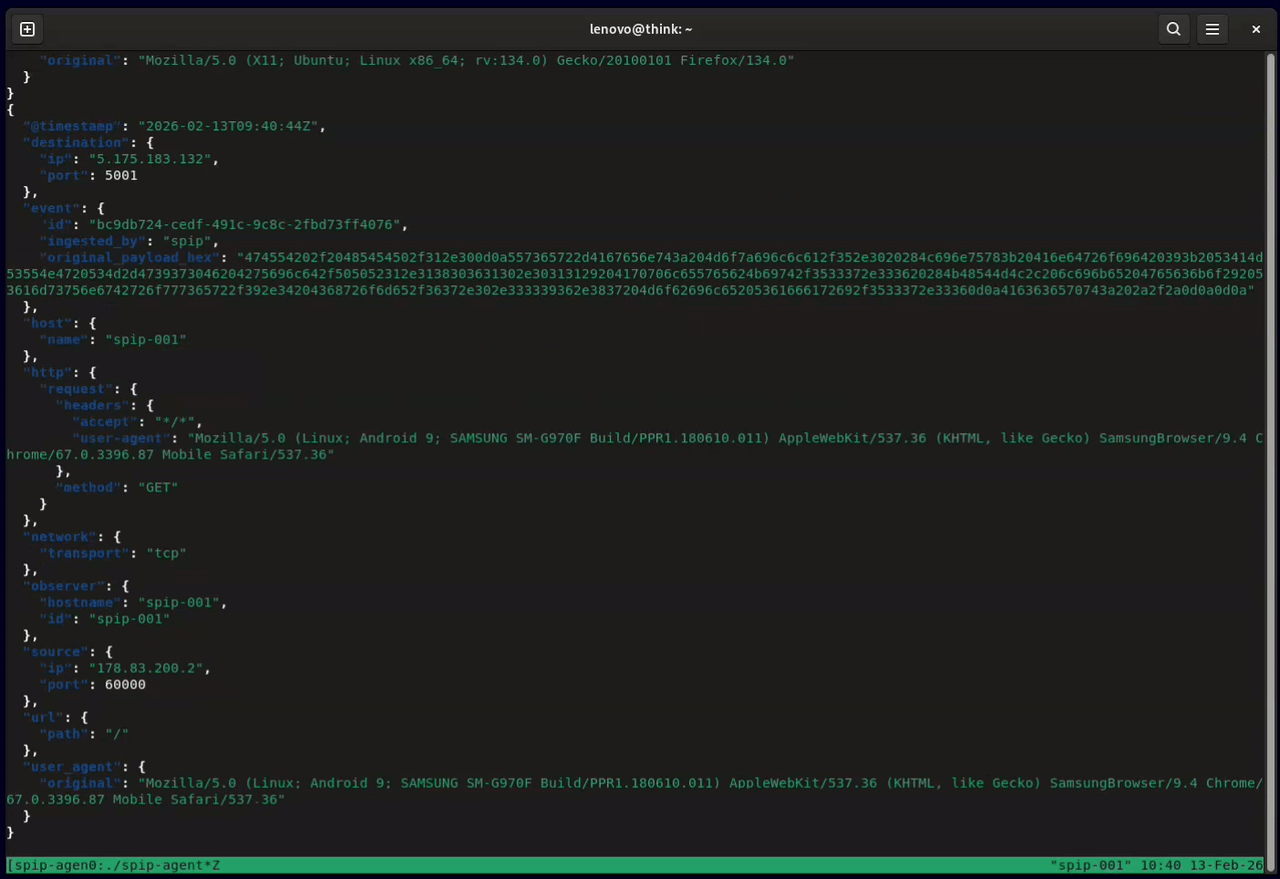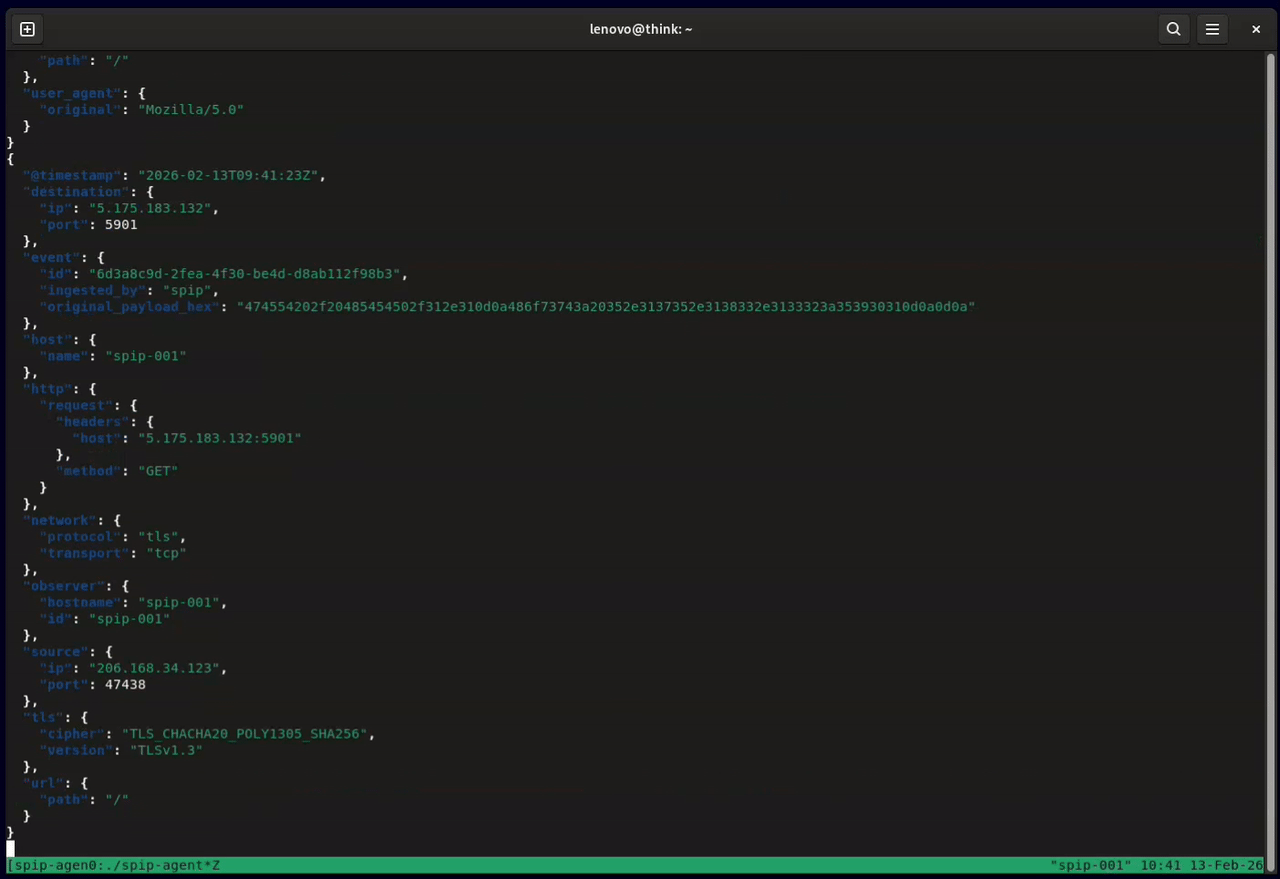 honeylabshq/spip-go
Spip network sensor written in Go
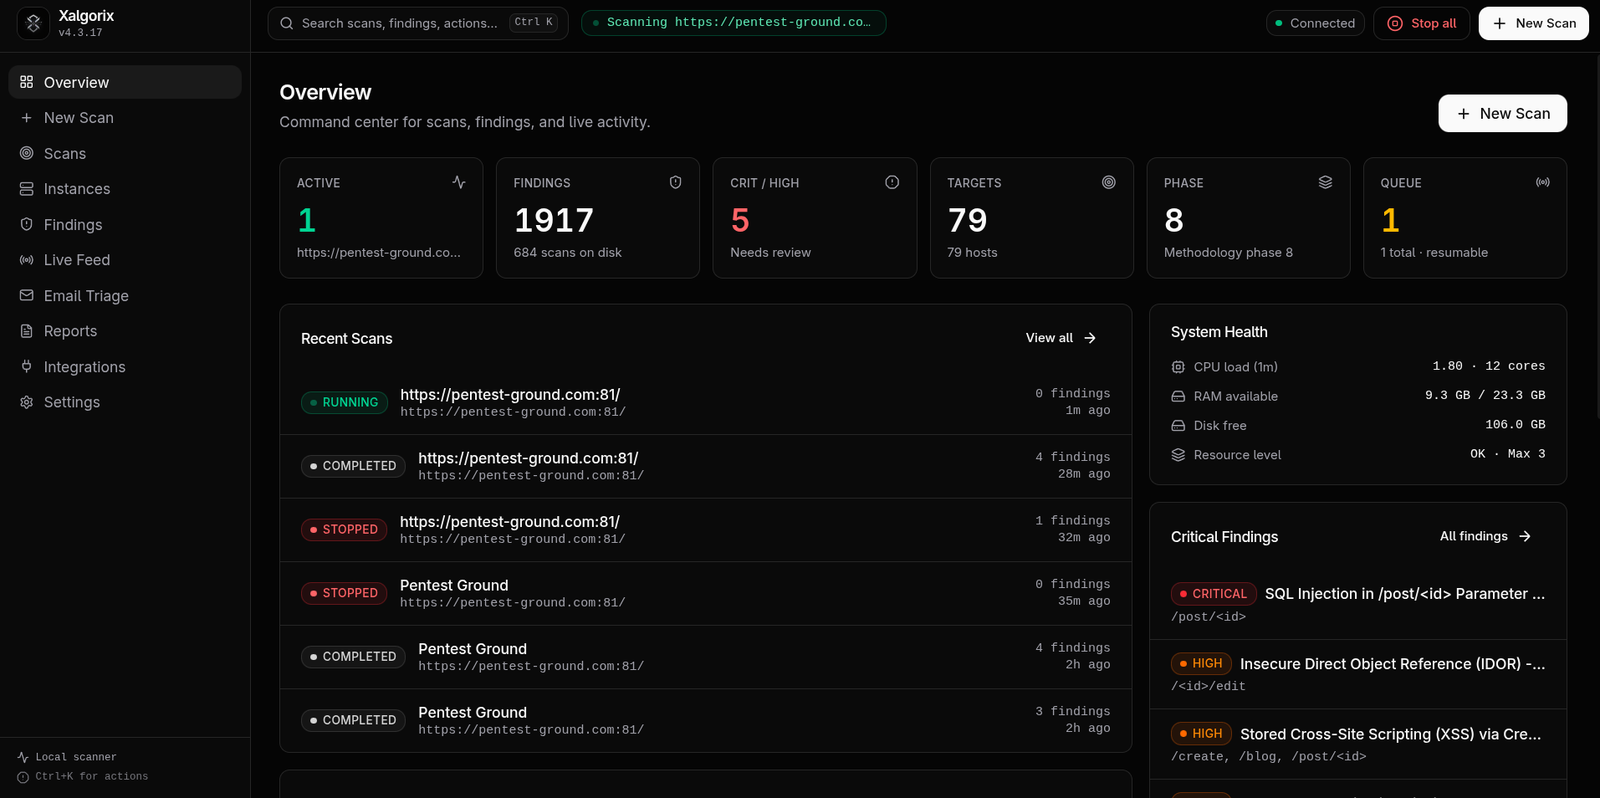 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 mziqudhd92/honeypot-auditor
Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like an honeypot — using Honeyscore,…