CVE-2026-42978-PoC-Research

Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.

Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.

CVE-2026-34990 — CUPS <= 2.4.16 Local Privilege Escalation

Python PoC reproducing the CUPS 2.4.16 local-printer flaw: captures the Local auth token via a rogue IPP endpoint, creates a file:// printer, and…

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…

Defensive notes on CVE-2022-24637 in Open Web Analytics before 1.7.4, covering unauthenticated information disclosure, privilege escalation impact,…

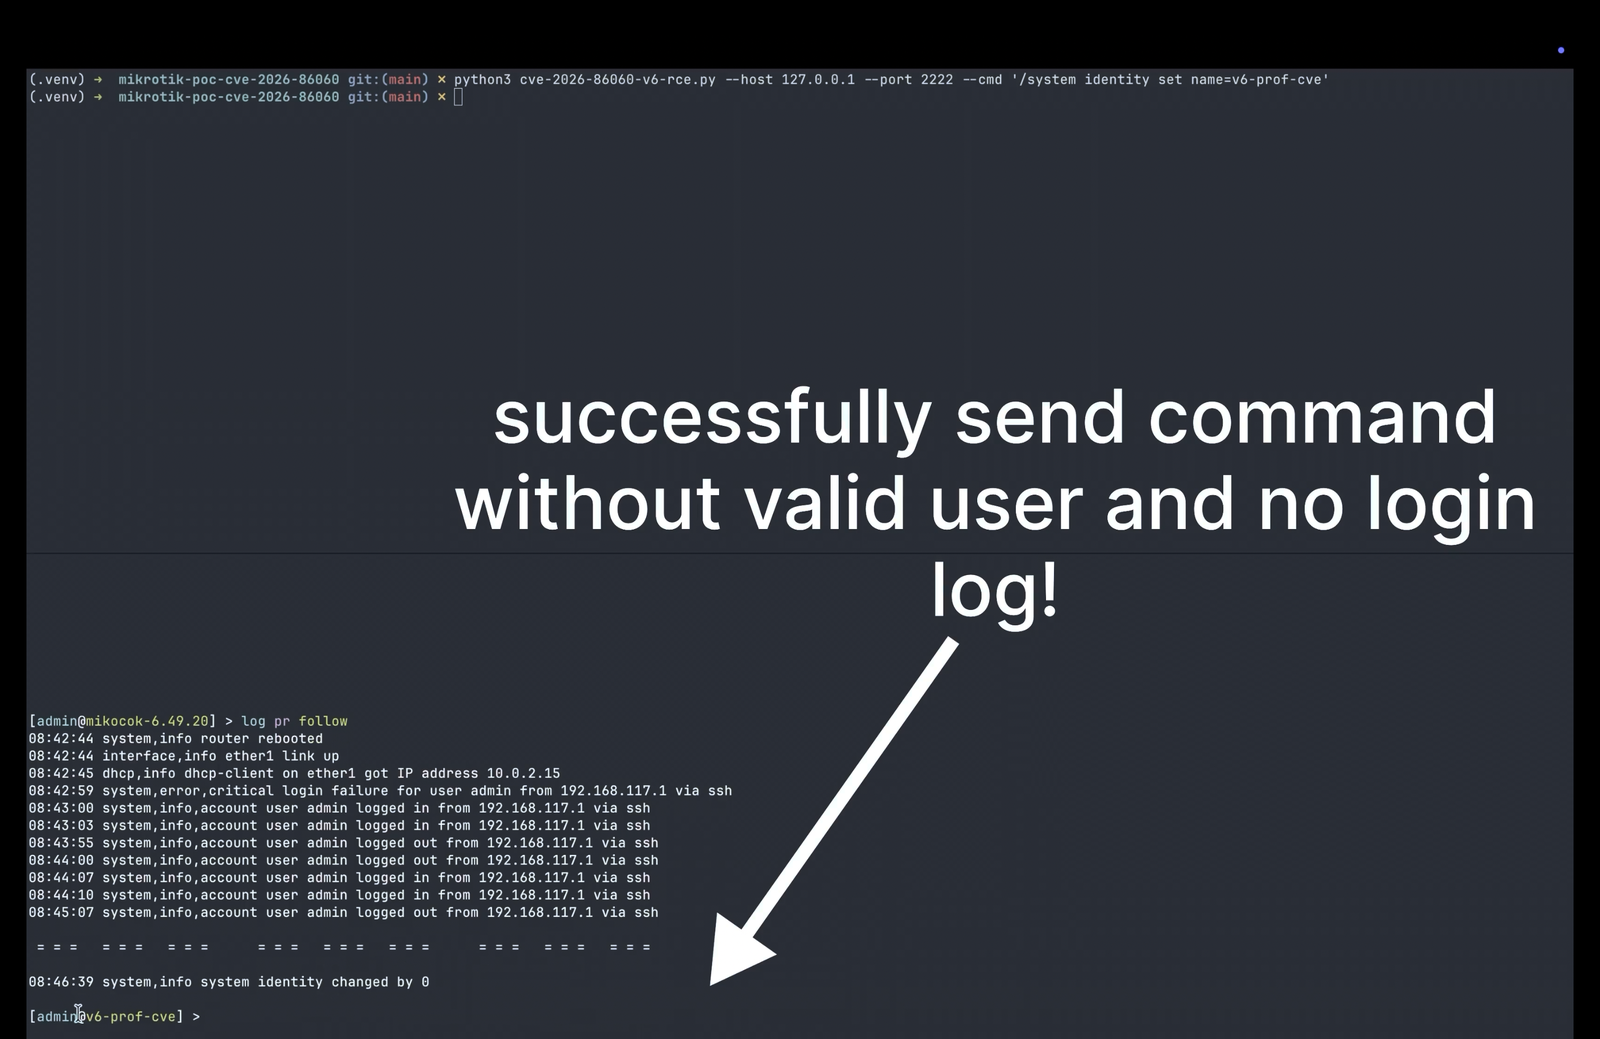
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…

Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…

Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.

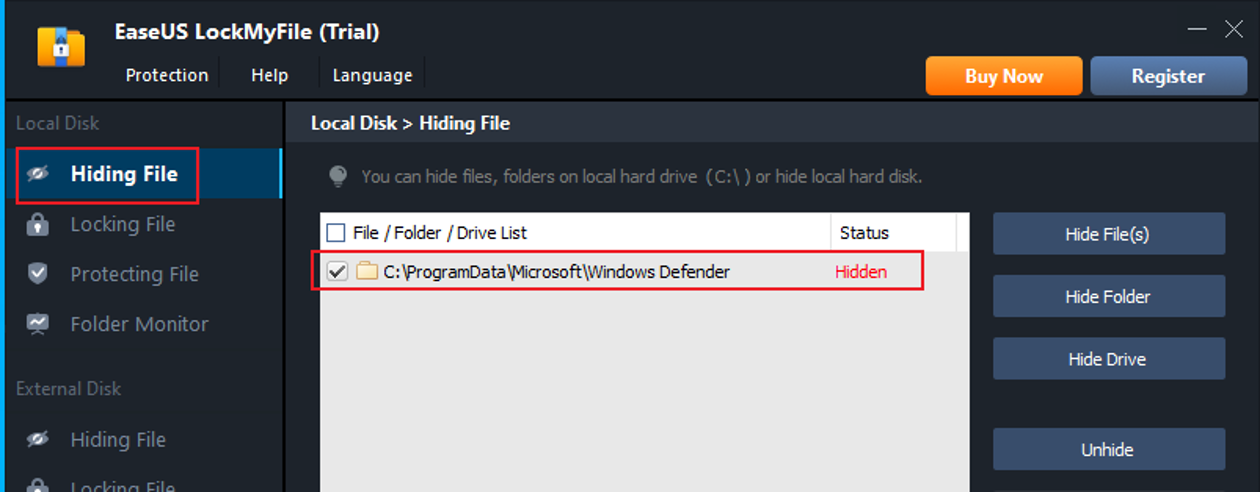
Proof-of-concept demonstrating methods to disable or bypass Windows Defender by hiding, locking, or protecting its folders, enabling persistence…

Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…

Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…

Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)

Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…

Tracking PinTheft (CVE-2026-43494, CVE-2026-43502), the RDS zerocopy double-free privilege escalation

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy