

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
478
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
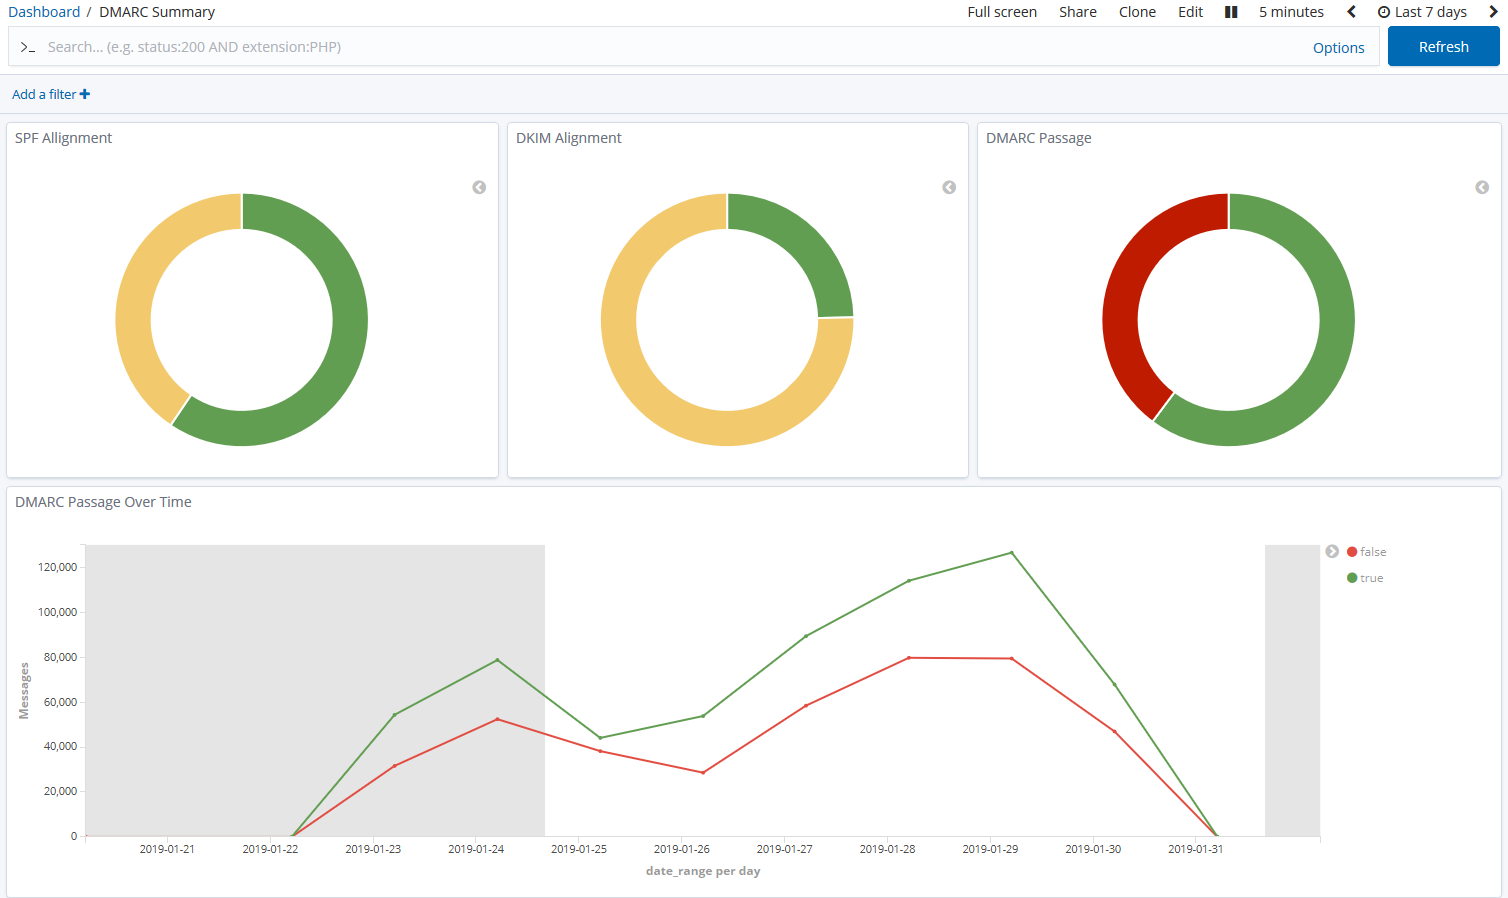 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Neutralizing CISA active Linux kernel CVEs (CVE-2025-39964, CVE-2026-53266, CVE-2025-39682) via modern eBPF, module disarmament, and containerd user…
 coactionbrittlemaidenhair51/cve-2026-42978-poc-research
Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 vedantk6403/koobe-guard
Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
 mahfuzreham/ovswrap-cve-2026-64531-mitigation-tool
Shell script that detects vulnerable Open vSwitch kernel modules, blocks automatic loading, removes the affected module, and verifies mitigation…
 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 hnytgl/cve-2026-42945
这是一个面向防守和内网排查的 CVE-2026-42945 静态检测工具,用于检查 NGINX ngx_http_rewrite_module 相关配置是否存在高风险 rewrite 组合。
 soksofos/wazuh-nginx-cve-2026-42945-sca-lab
Centralized Wazuh SCA Assessment for CVE-2026-42945 on NGINX Servers
 philfry/cve-2026-31431-ftrace
Kernel module using ftrace to block AF_ALG/AEAD requests, mitigating CVE-2026-31431 without requiring LSM BPF. Provides logging and easy compilation…
 kwilck/copyfail
Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…
 deadrabbit92/mitigate-copy-fail.yml
Mitigates CVE-2026-31431 (Copy Fail) by unloading and blacklisting algif_aead kernel module if it is loadable and has no active references.
 webhosting4u/copy-fail_detect_and_mitigate_cve-2026-31431
Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…