
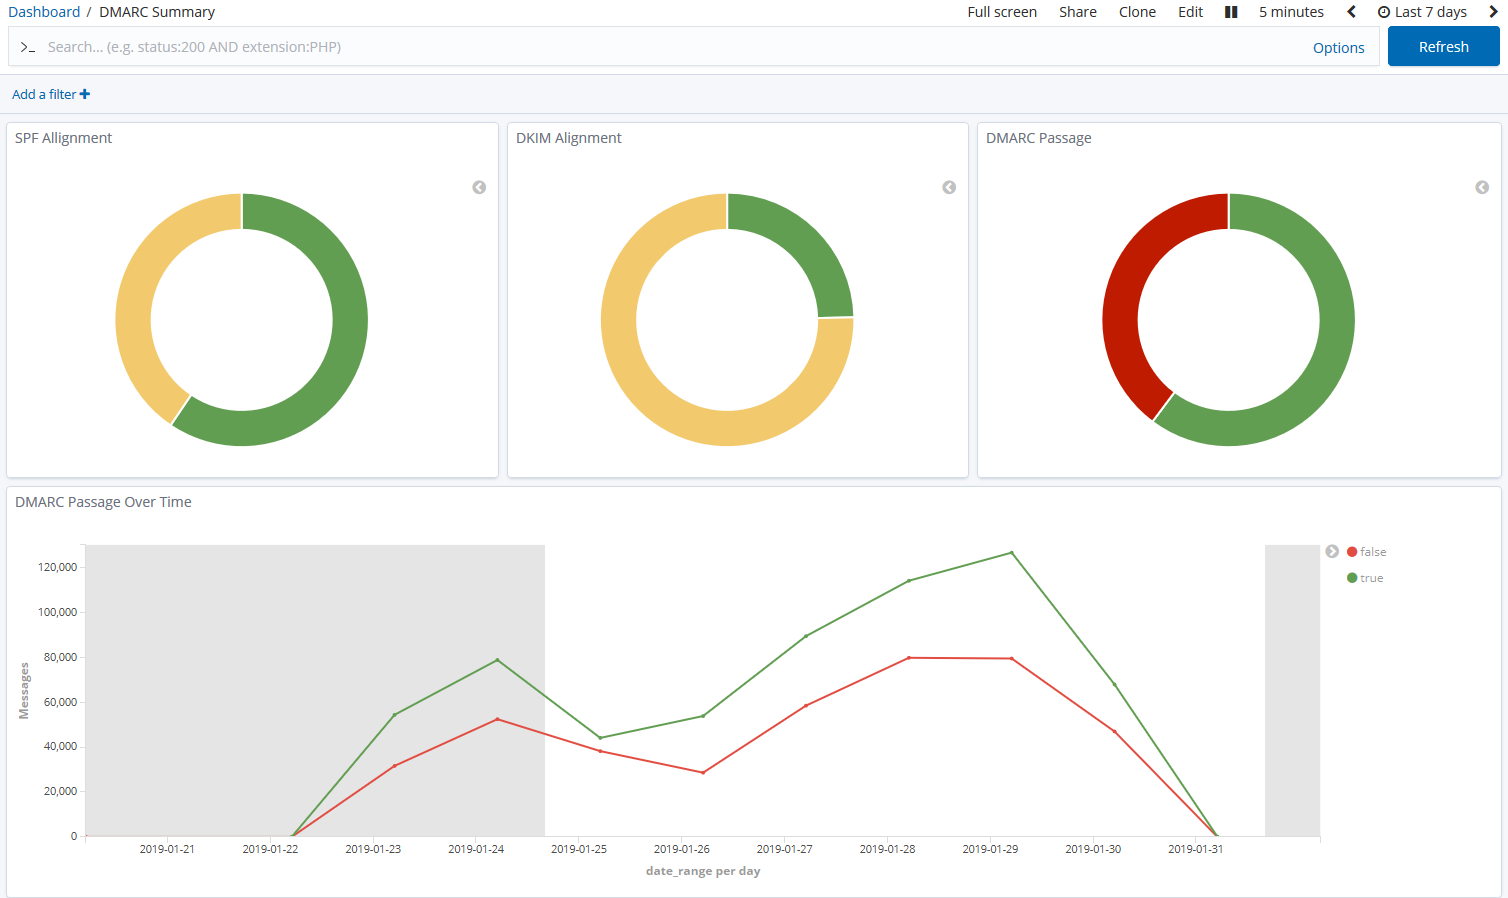
parsedmarc
 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
authenticationdefensive-toolsdns-analysis+2
1.3k
domainaware/parsedmarcA Python package and CLI for parsing aggregate and forensic DMARC reports
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 liske/needrestart
System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…
 xhowenma/rope
Defense framework enforcing routed origin policy to prevent indirect prompt injection in tool-using LLM agents, with deterministic origin checks and…
 debajyoti0-0/cve-2026-64600
A C-based Linux security utility for detecting, safely verifying (Proof of Concept), and mitigating CVE-2026-64600 (RefluXFS). It provides kernel…
 zerodayvpn/cve-2026-24291
About 2026 Guide: Bypass User Account Control Prompts on Windows 11
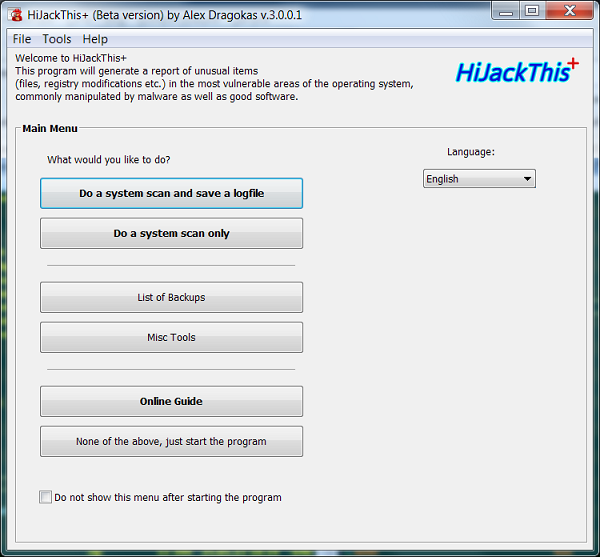 dragokas/hijackthis
A free utility that finds malware, adware and other security threats
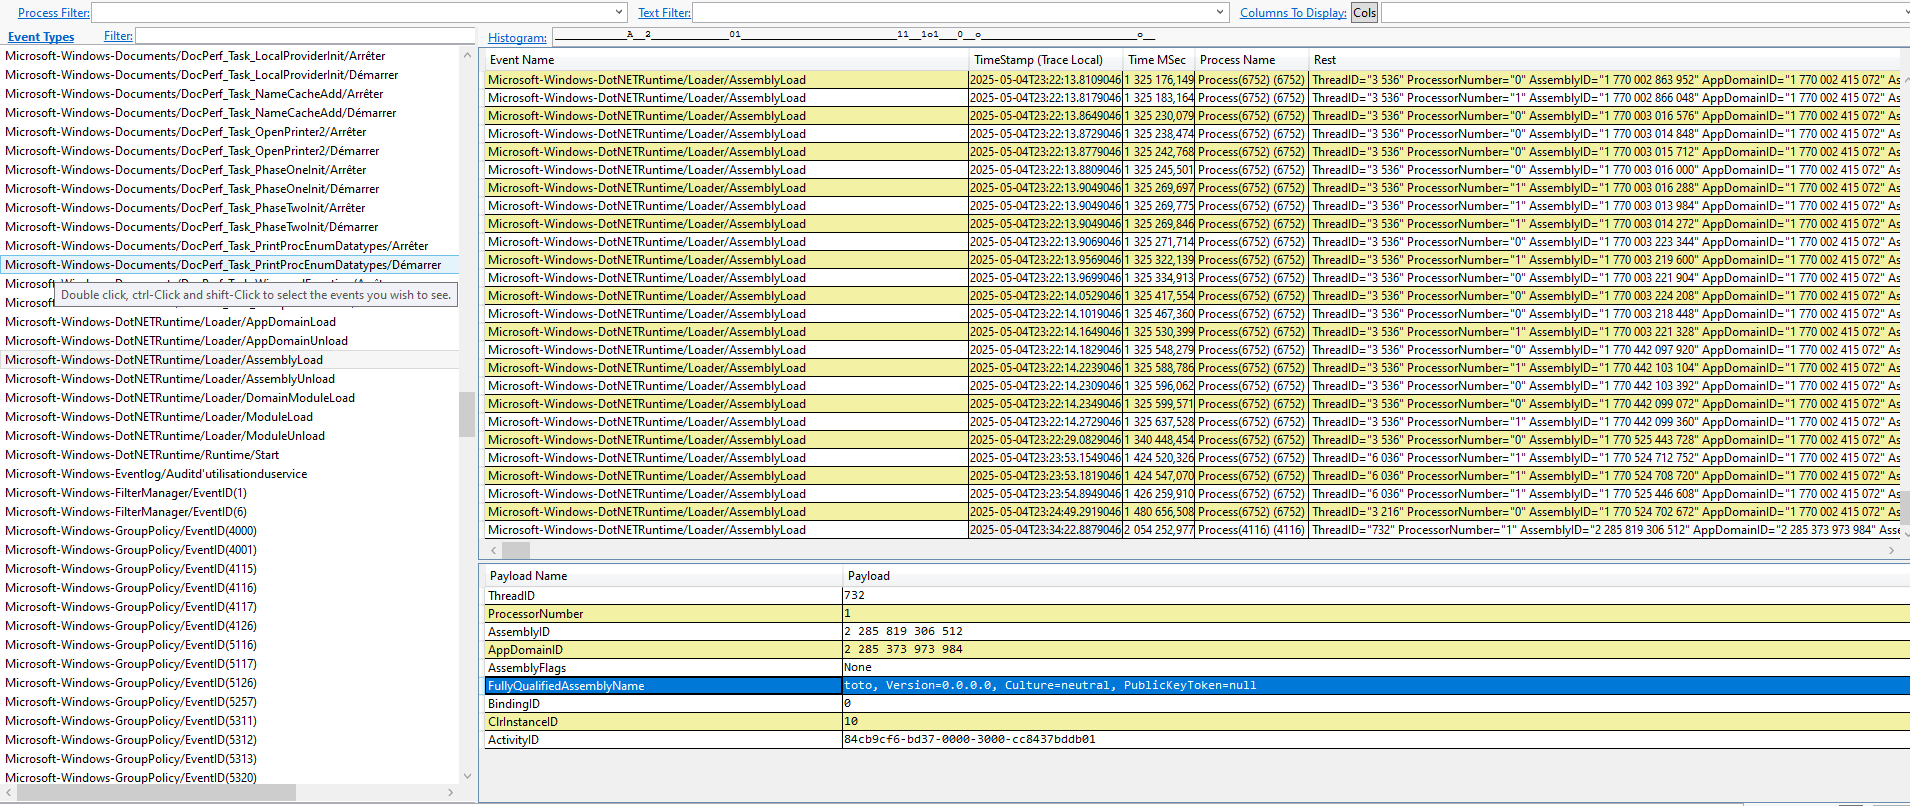 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 sreejaputhan/cpanel-control-plane-exposure-check
Defensive exposure assessment tool for identifying externally accessible cPanel, WHM, and Webmail management interfaces related to CVE-2026-41940.
 shizuku198411/cve-2026-0300
Non-destructive exposure survey tool for assessing PAN-OS User-ID Authentication Portal surfaces related to CVE-2026-0300, performing safe HTTP(S)…
 paniclock/paniclock
Instantly disable Touch ID and lock your Mac with one click or keyboard shortcut.
 loresuso/psc
the ps utility, with an eBPF twist and container context
 gmh5225/zeropoint
This PowerShell script detects indicators of compromise for CVE-2025-53770 — a critical RCE vulnerability in Microsoft SharePoint. Created by…
 almogopp/disable-ipv6-cve-2024-38063-fix
A PowerShell script to temporarily mitigate the CVE-2024-38063 vulnerability by disabling IPv6 on Windows systems. This workaround modifies the…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
 sq00ky/smb-session-spoofing
Windows service that creates fake SMB sessions to simulate high-privilege user logons, luring attackers into honeypot machines for early detection…
 bohops/rogueassemblyhunter
Rogue Assembly Hunter is a utility for discovering 'interesting' .NET CLR modules in running processes.