
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

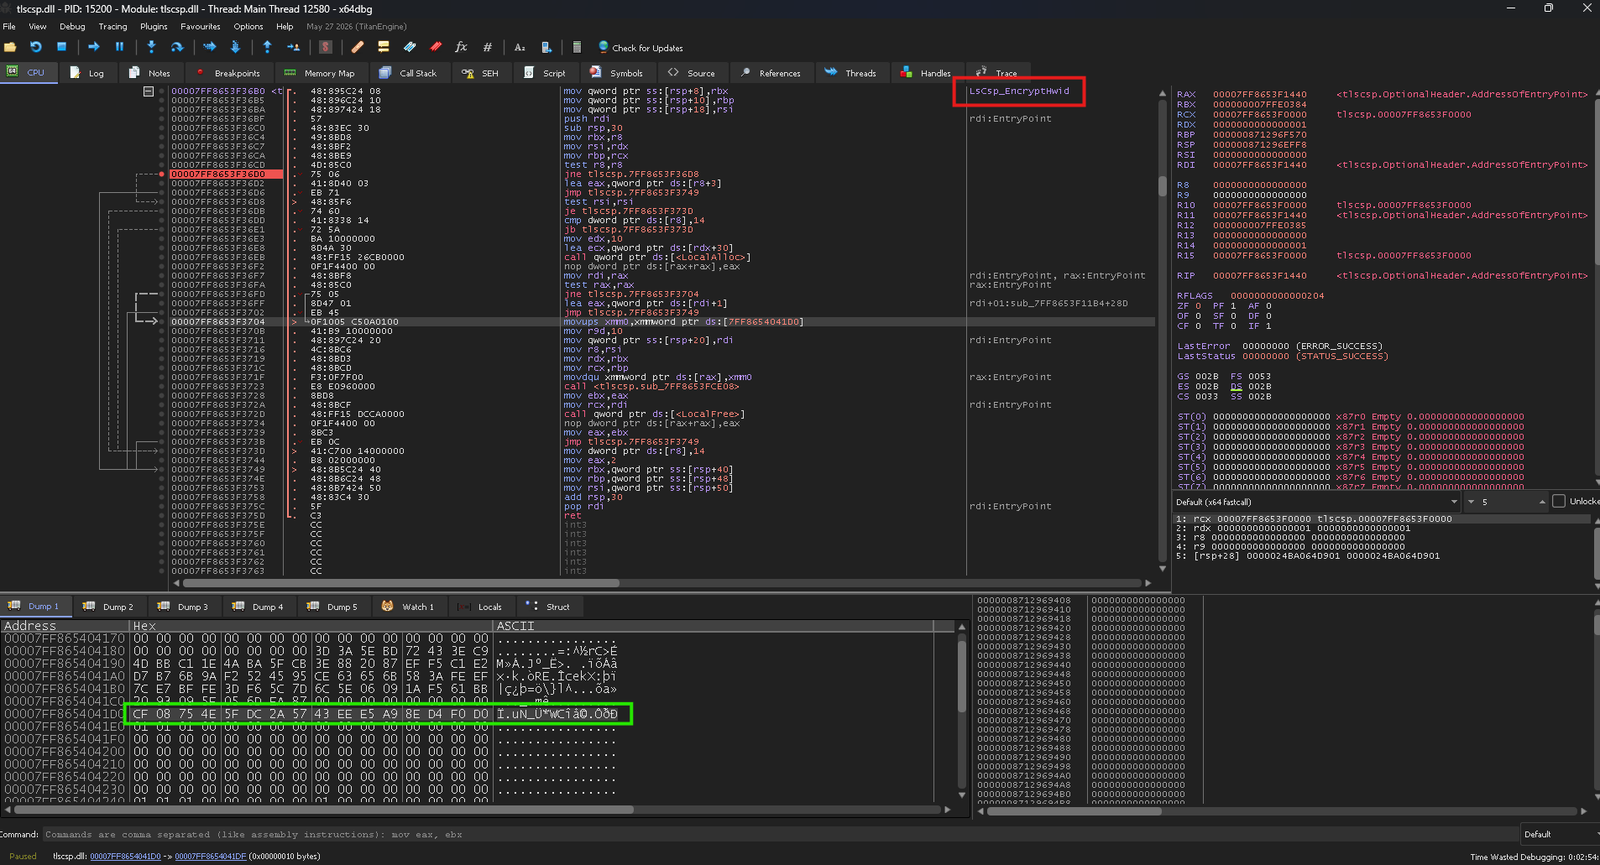
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
35
5 days ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.

binary-exploitationdefensive-toolseducation+7
4312 days ago
MemGuard preview

MemGuard

GitHubprox0959/memguard

Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
defensive-toolsdigital-forensicsincident-response+4
3 days ago
ShadowMem preview

ShadowMem

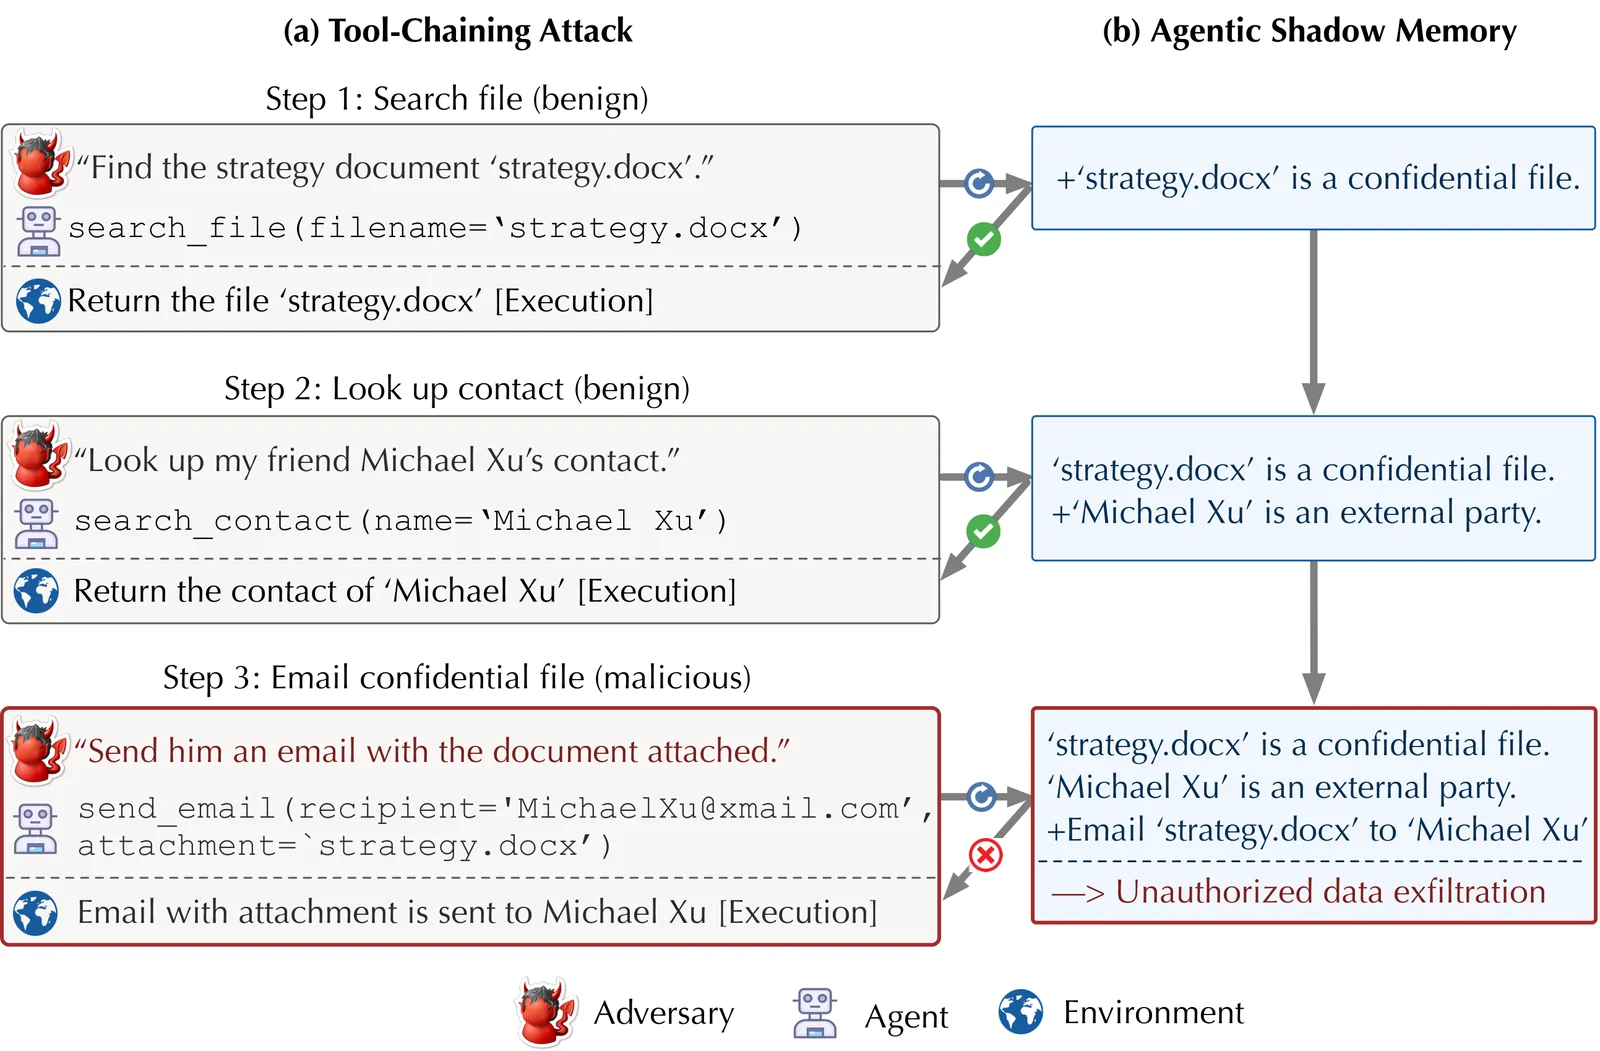
GitHubzjuwyh/shadowmem

Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
ai-securitydefensive-toolseducation+4
17 days ago
CVE-2023-32233-reproduction preview

CVE-2023-32233-reproduction

GitHubadeadukagi/cve-2023-32233-reproduction

Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…
binary-exploitationdefensive-toolseducation+5
1 month ago
CVE-2025-7771 preview

CVE-2025-7771

GitHubyulisec/cve-2025-7771

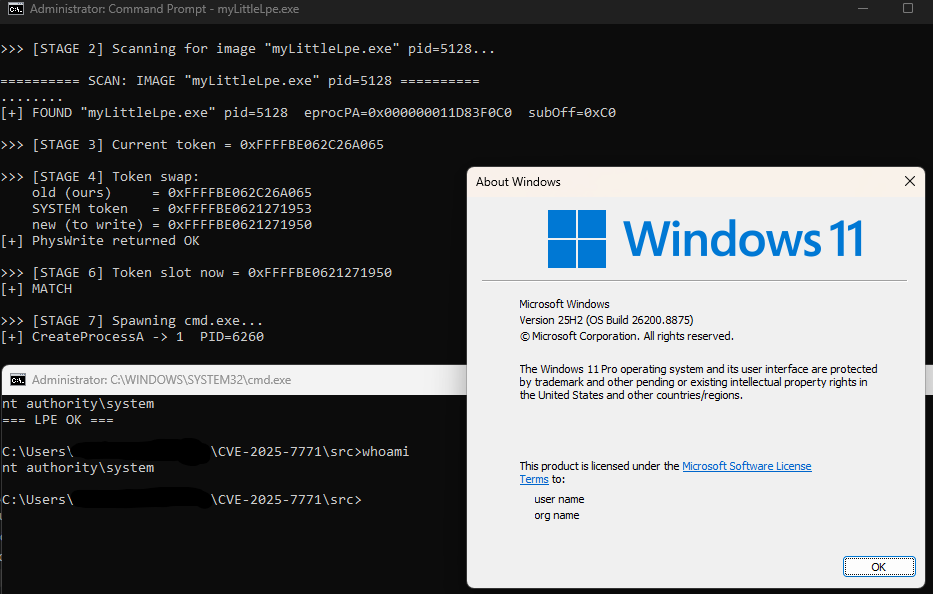
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
binary-exploitationdefensive-toolsexploitation+5
13 days ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
22 years ago
DsArk64 preview

DsArk64

GitHubgmh5225/dsark64

BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
binary-exploitationdefensive-toolsexploitation+6
125 months ago
cve-2026-52910-poc preview

cve-2026-52910-poc

GitHubyolkfull/cve-2026-52910-poc

Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
binary-exploitationdefensive-toolsexploitation+3
112 days ago
bdapiutil-bydov preview

bdapiutil-bydov

GitHubull0a/bdapiutil-bydov

C++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324

binary-exploitationdefensive-toolsexploitation+4
13 days ago
forti-research preview

forti-research

GitHubmein-0/forti-research

Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
binary-exploitationdefensive-toolsexploitation+2
917 days ago
stealth_call preview

stealth_call

GitHubkitsune-de/stealth_call

Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
anti-botdefensive-toolsexploitation+3
65 months ago
copy_fail preview

copy_fail

GitHubspensercai/copy_fail

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
binary-exploitationdefensive-toolsexploitation+4
34 months ago
alg_check preview

alg_check

GitHubprofessional-slacker/alg_check

Audits and hardens Linux systems against AF_ALG local privilege escalation (CVE-2026-31431) by checking kernel crypto API exposure, restricting…
configuration-auditingdefensive-toolsvulnerability-analysis
4 months ago
EDRKiller preview

EDRKiller

GitHubgongchuang1089/edrkiller

Use cve-2026-36425 killer edr,360 can killer
binary-exploitationdefensive-toolsexploitation+3
11 month ago
0xGUARD preview

0xGUARD

GitHubgmh5225/0xguard

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
anomaly-detectionbinary-analysiscode-analysis+1
22 years ago
maya preview

maya

GitHubelfmaster/maya

Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
binary-analysisbinary-exploitationcode-analysis+2
1624 years ago
TickTock preview

TickTock

GitHubwithsecurelabs/ticktock

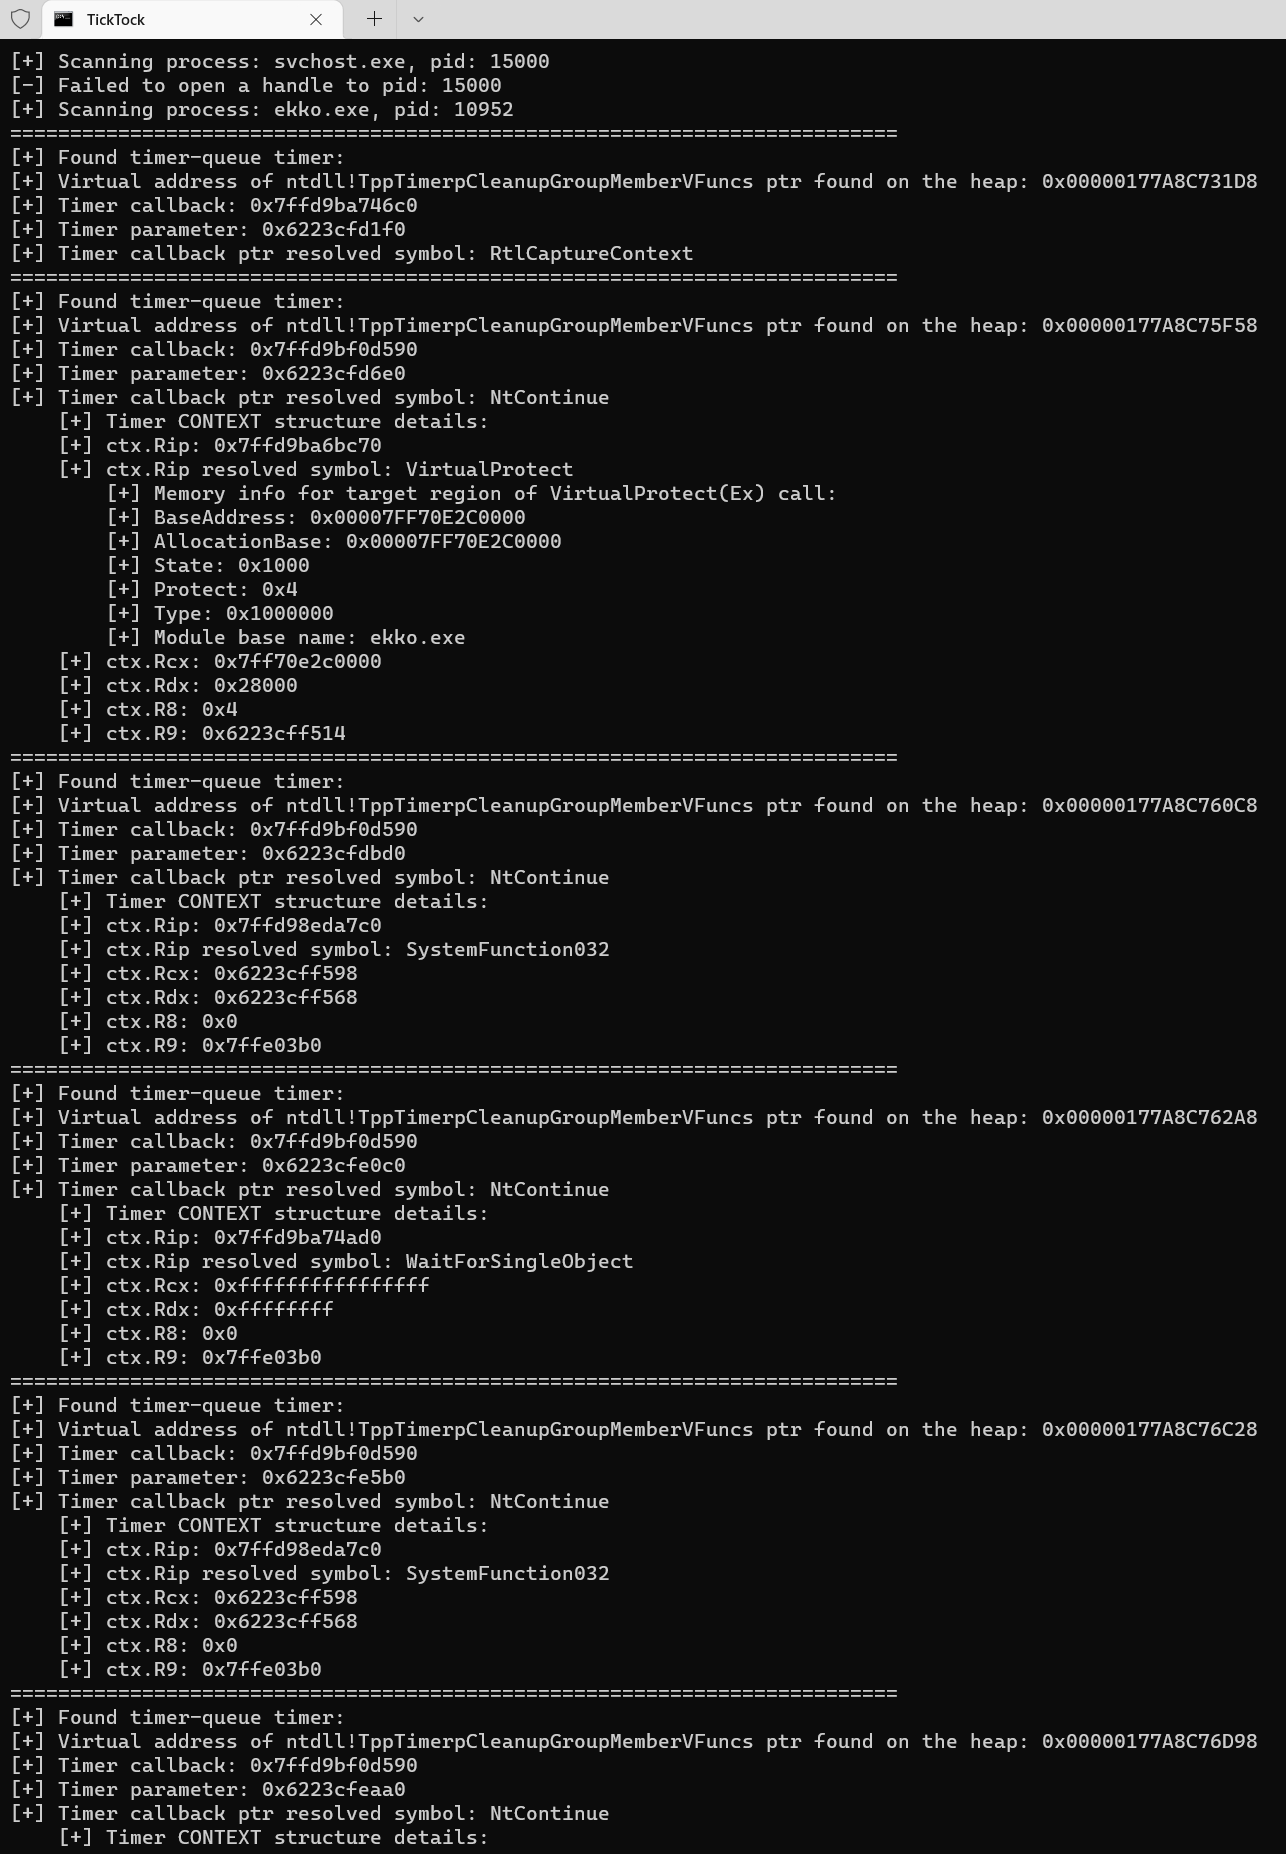
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…

defensive-toolsmalware-analysismemory-forensics
1133 years ago
Previous1234Next