bpfjailer
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
authentication-authorizationconfiguration-auditingcontainer-security+3
36
facebookincubator/bpfjailereBPF LSM based Mandatory Access Control and jailer
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 jonny-jhnson/ldapmon
Proof-of-concept telemetry collector for Windows LDAP client activity via ETW, logging structured events to Event Viewer with a Sentinel parser for…
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.
 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
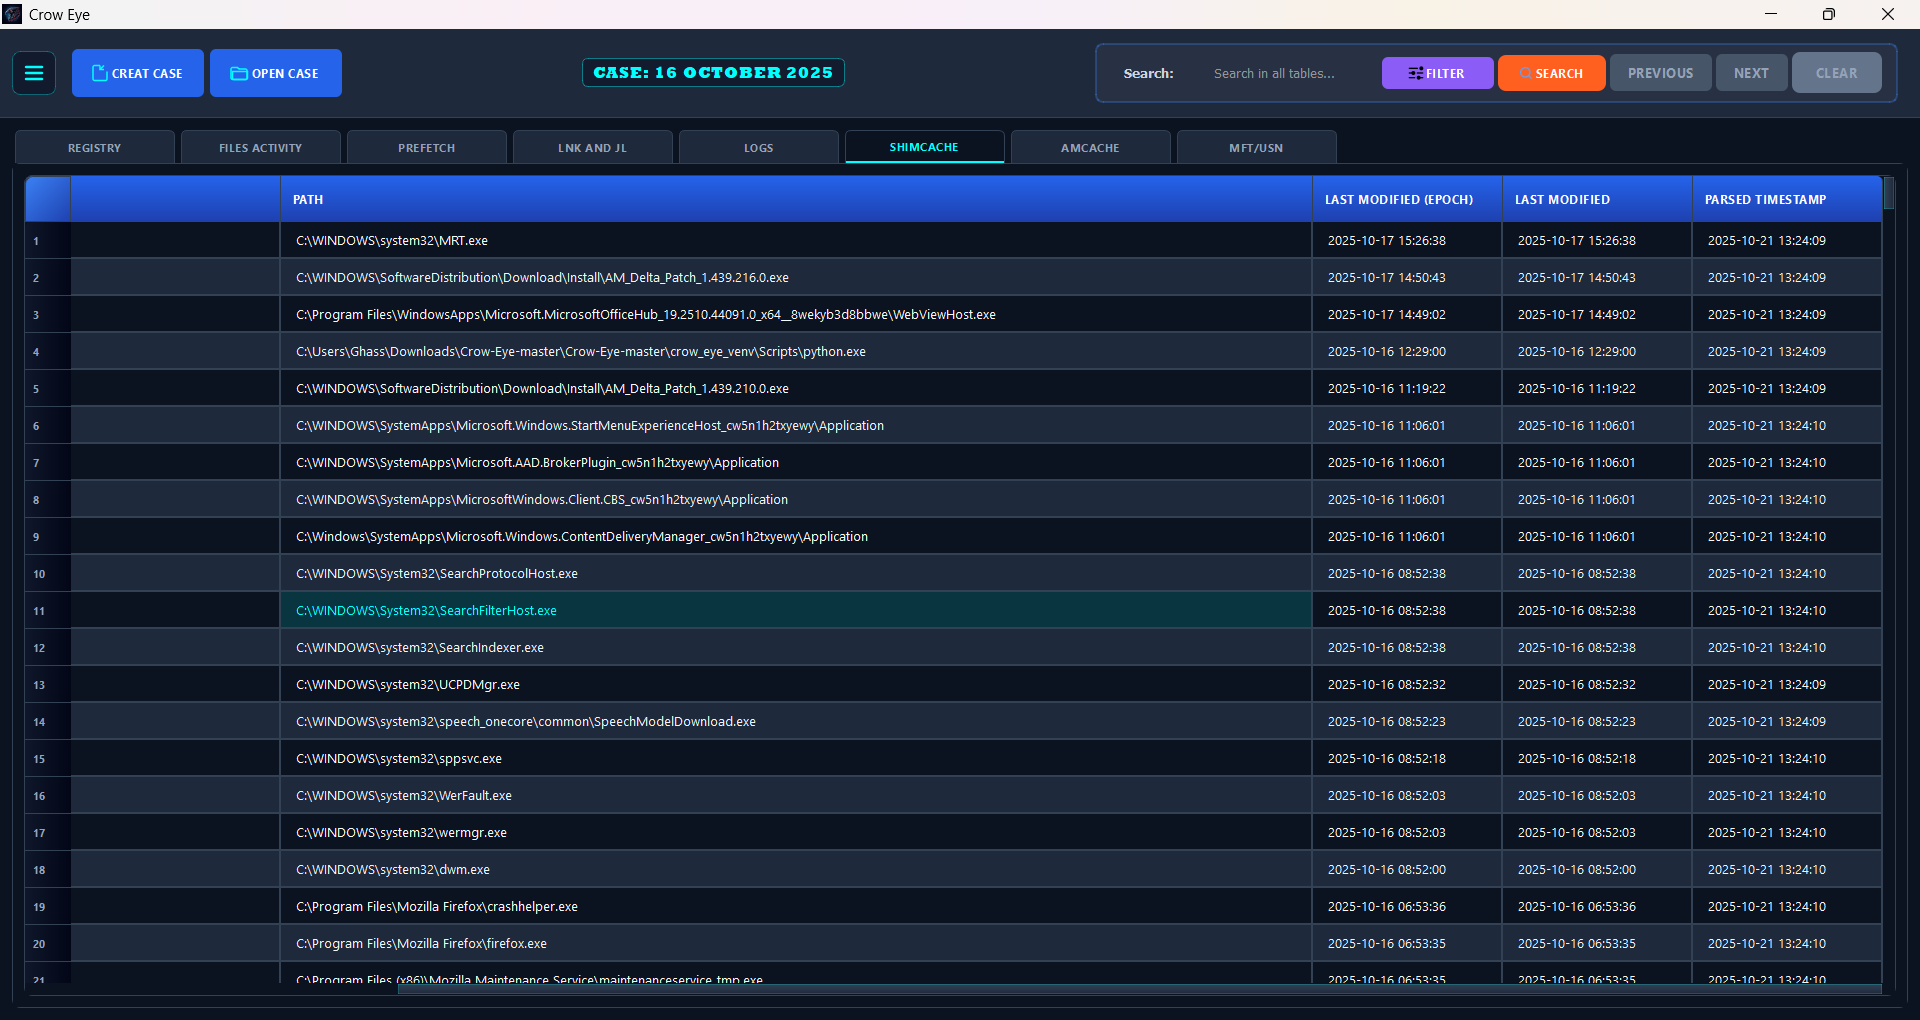 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
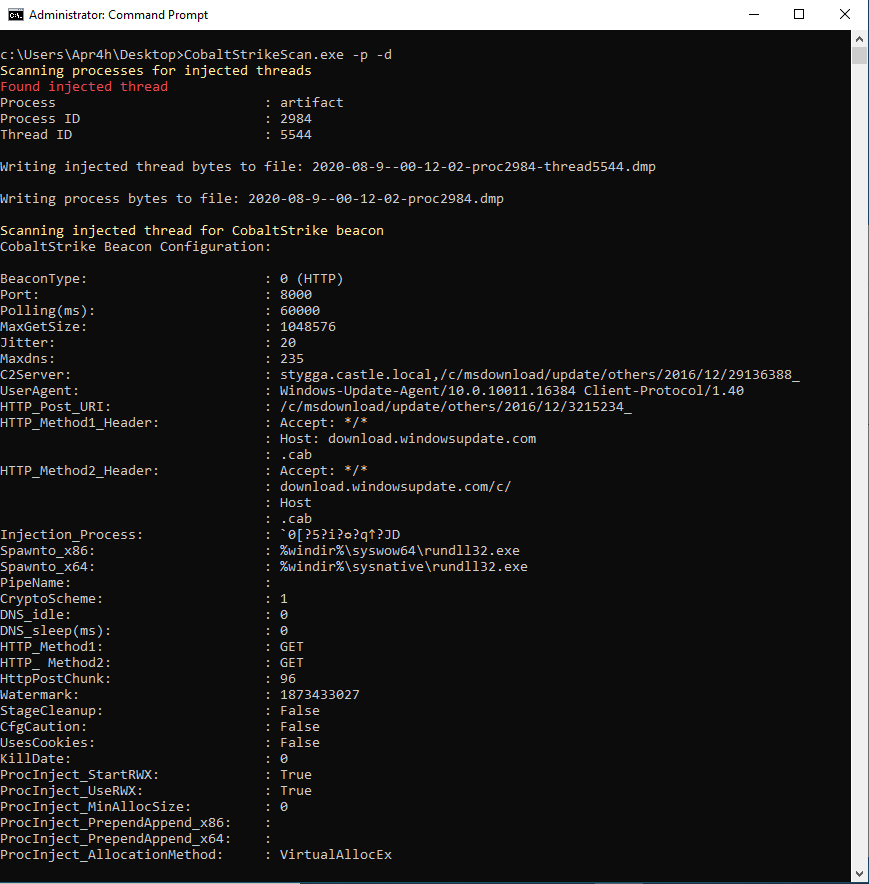 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
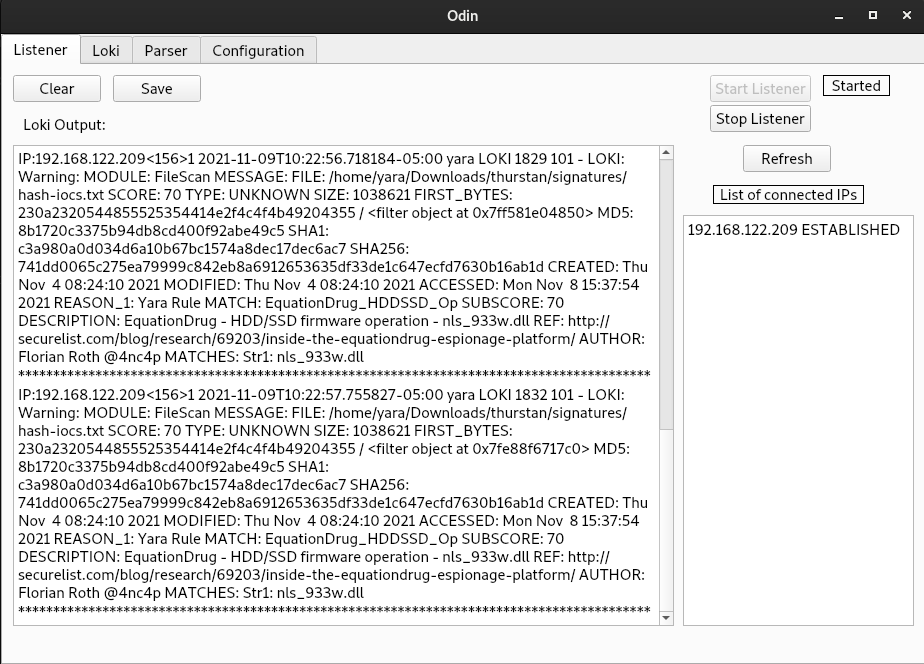 hamza-megahed/odin
Centralized IoC scanner that deploys Loki across endpoints, collects detection results, and parses logs into CSV for incident response and forensic…