
mirth-connect-security-poc
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
defensive-toolseducationexploitation+4
abhinavagarwal07/mirth-connect-security-pocWorking PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
 princeaikinsbaidoo/cve-2022-24637
Defensive notes on CVE-2022-24637 in Open Web Analytics before 1.7.4, covering unauthenticated information disclosure, privilege escalation impact,…
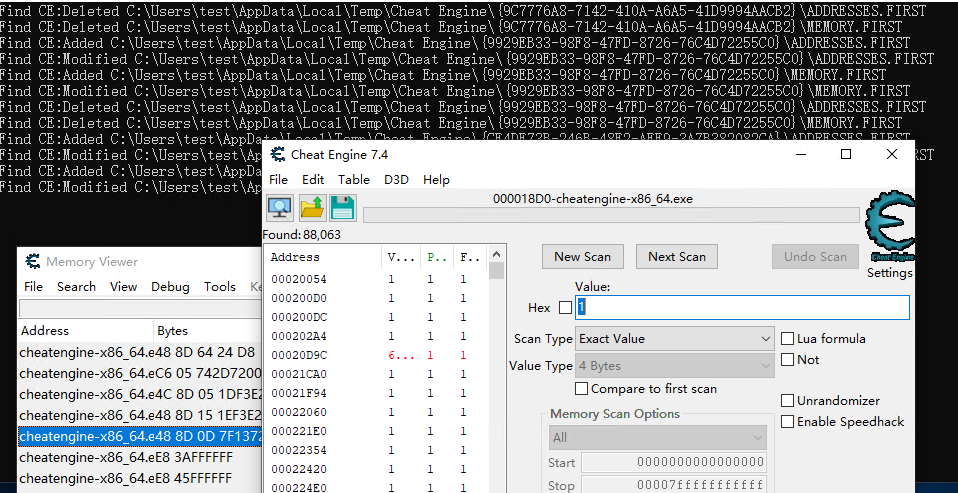 gmh5225/detection-cheatengine
Detects CheatEngine process activity by monitoring file system changes with ReadDirectoryChangesW, providing a lightweight anti-cheat mechanism for…
 xoessie/cve-2026-83548-sonicwall-sma1000-analysis
Vulnerability Analysis of CVE-2026-83548 affecting SonicWall SMA1000 security systems.
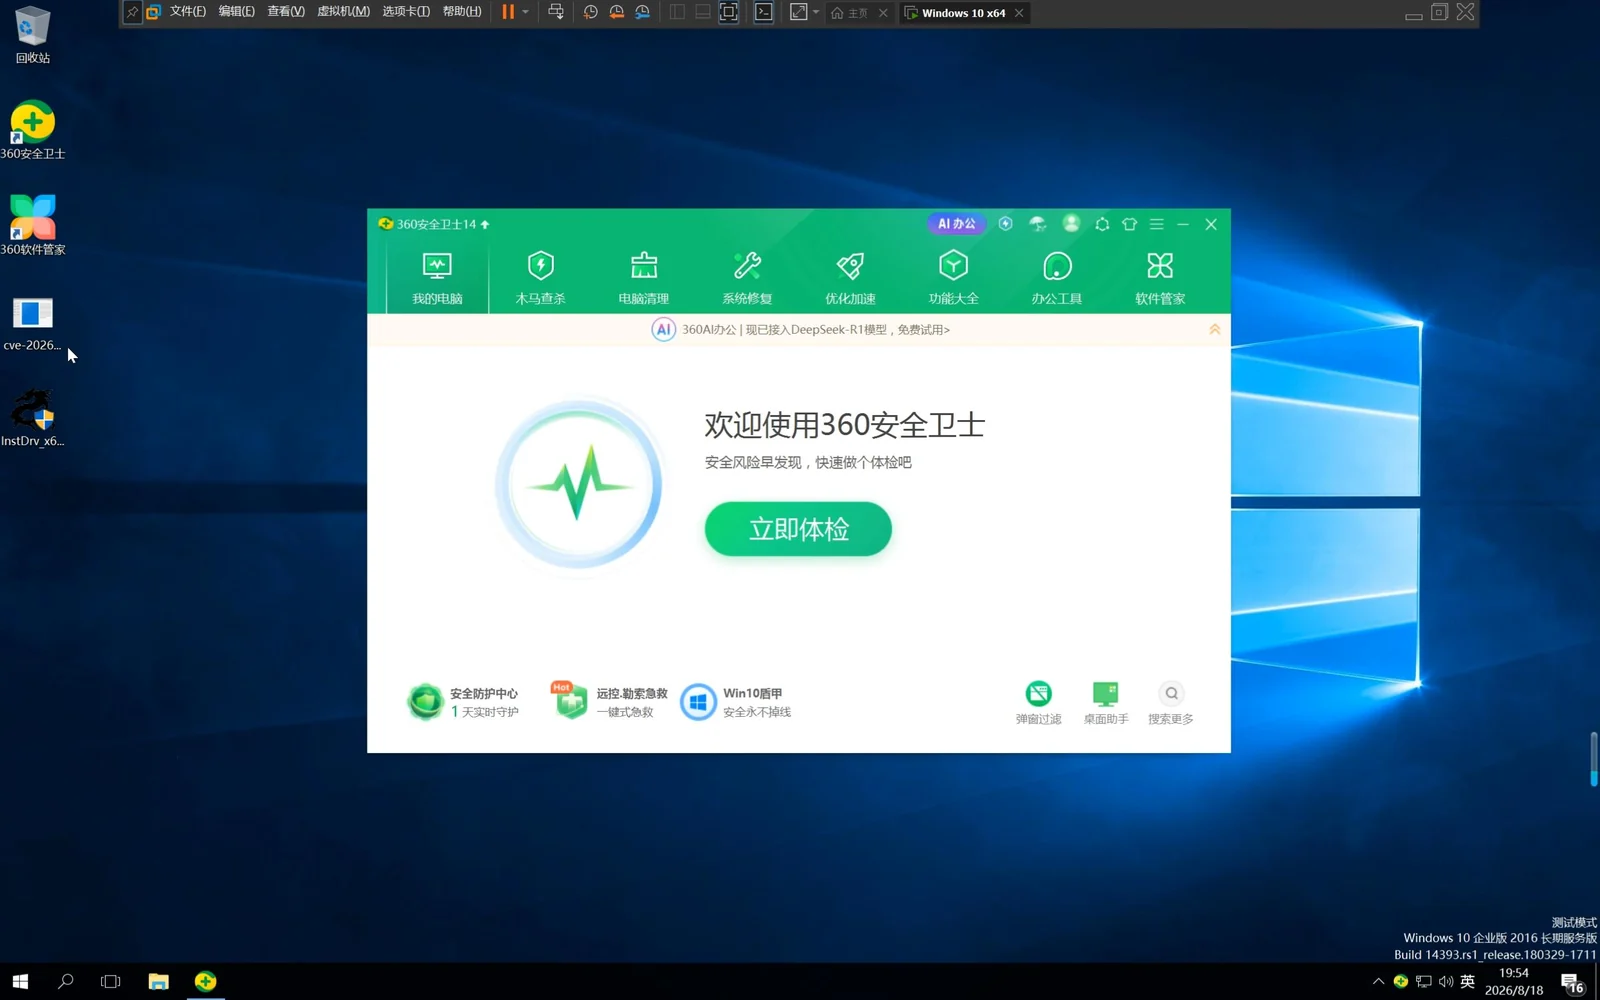 gongchuang1089/edrkiller
Use cve-2026-36425 killer edr,360 can killer
 tang-yikai/copy-fail-mitigation-with-bpftrace
CVE-2026-31431, AKA Copy Fail, can be mitigated in one-line with bpftrace
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 oauth2-proxy/oauth2-proxy
A reverse proxy that provides authentication with Google, Azure, OpenID Connect and many more identity providers.
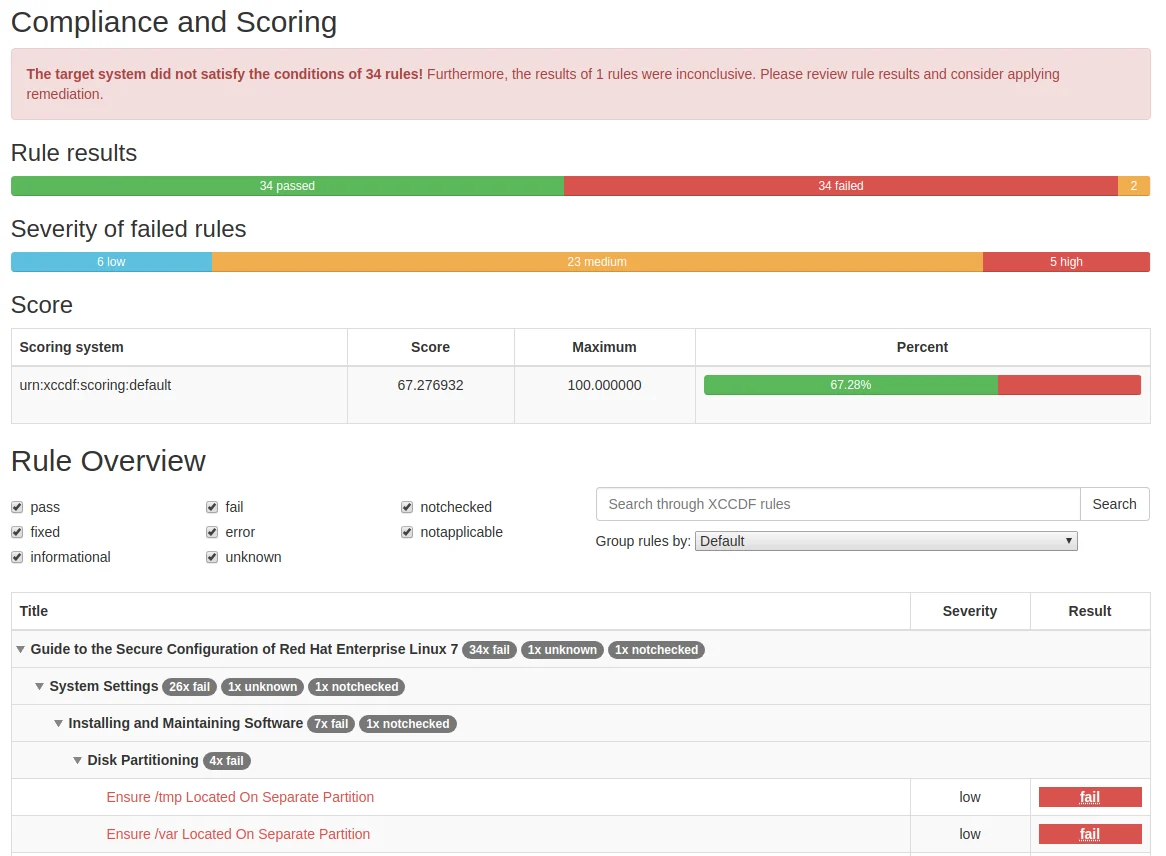 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
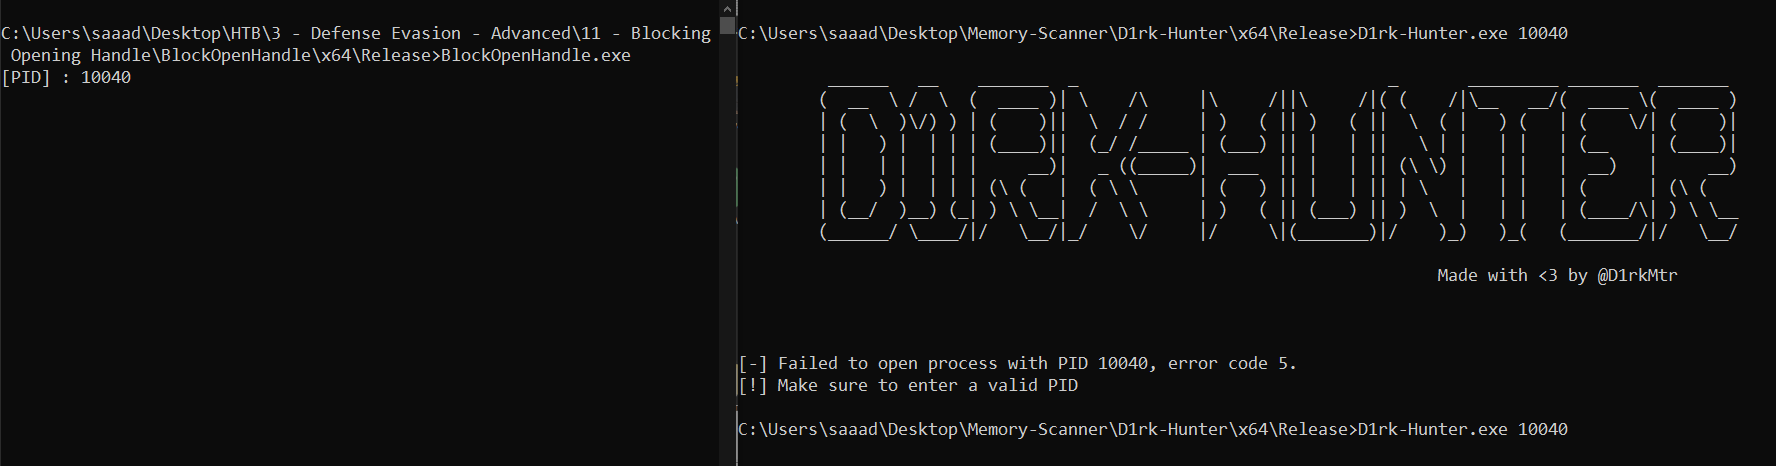 saadahla/blockopenhandle
Block any Process to open HANDLE to your process , only SYTEM is allowed to open handle to your process ,with that you can avoid remote memory…
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
 scoubi/bloodsocer
Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…