
CVE-2026-87902-Toolkit
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
defensive-toolseducationexploitation+8
tc4dy/cve-2026-87902-toolkitWordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 auditinfra-io/o1js-scan
Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
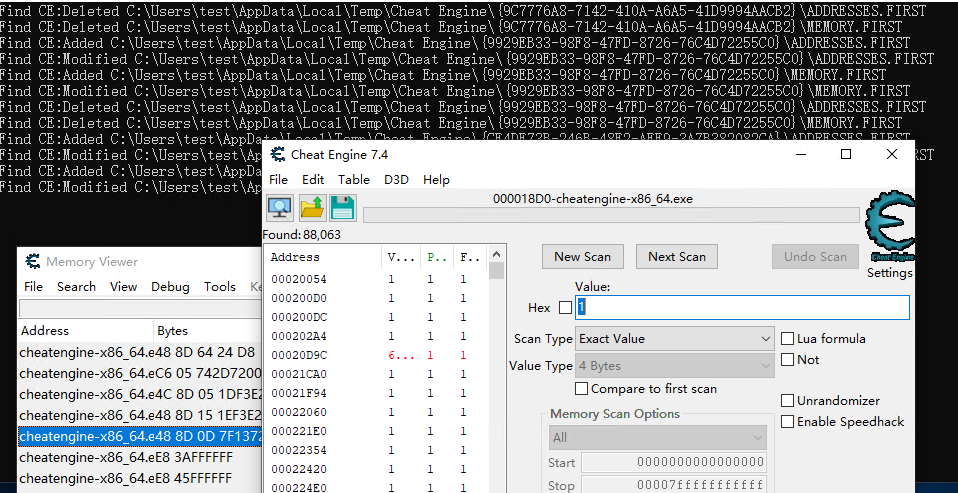 gmh5225/detection-cheatengine
Detects CheatEngine process activity by monitoring file system changes with ReadDirectoryChangesW, providing a lightweight anti-cheat mechanism for…
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…
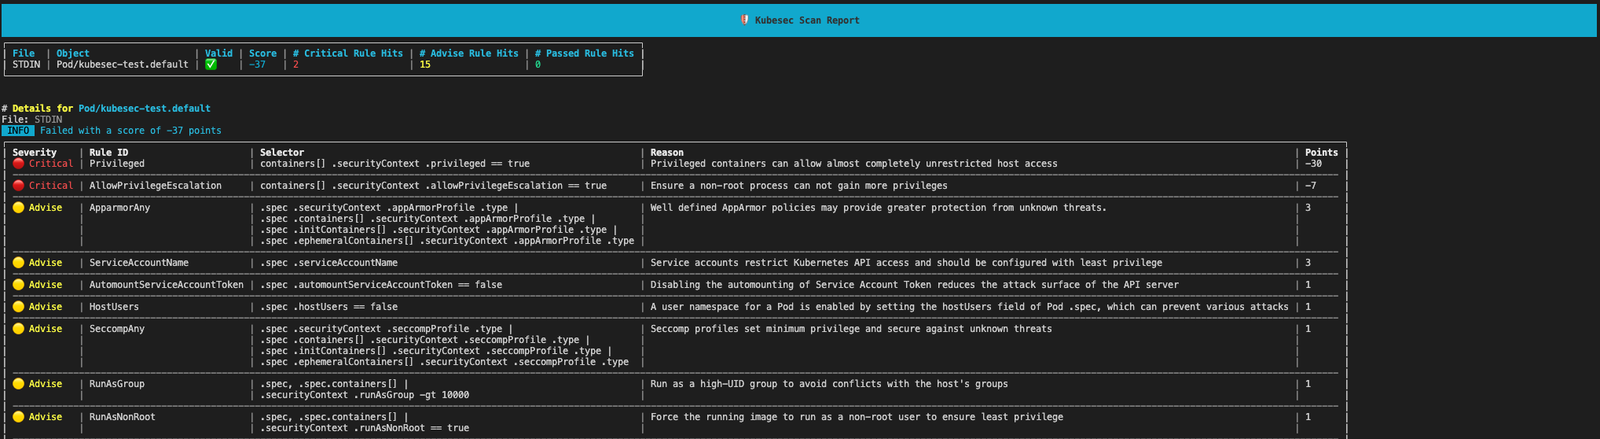 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 keerthivasan-sankar/secure-vault-for-commercial
secure vault for your files
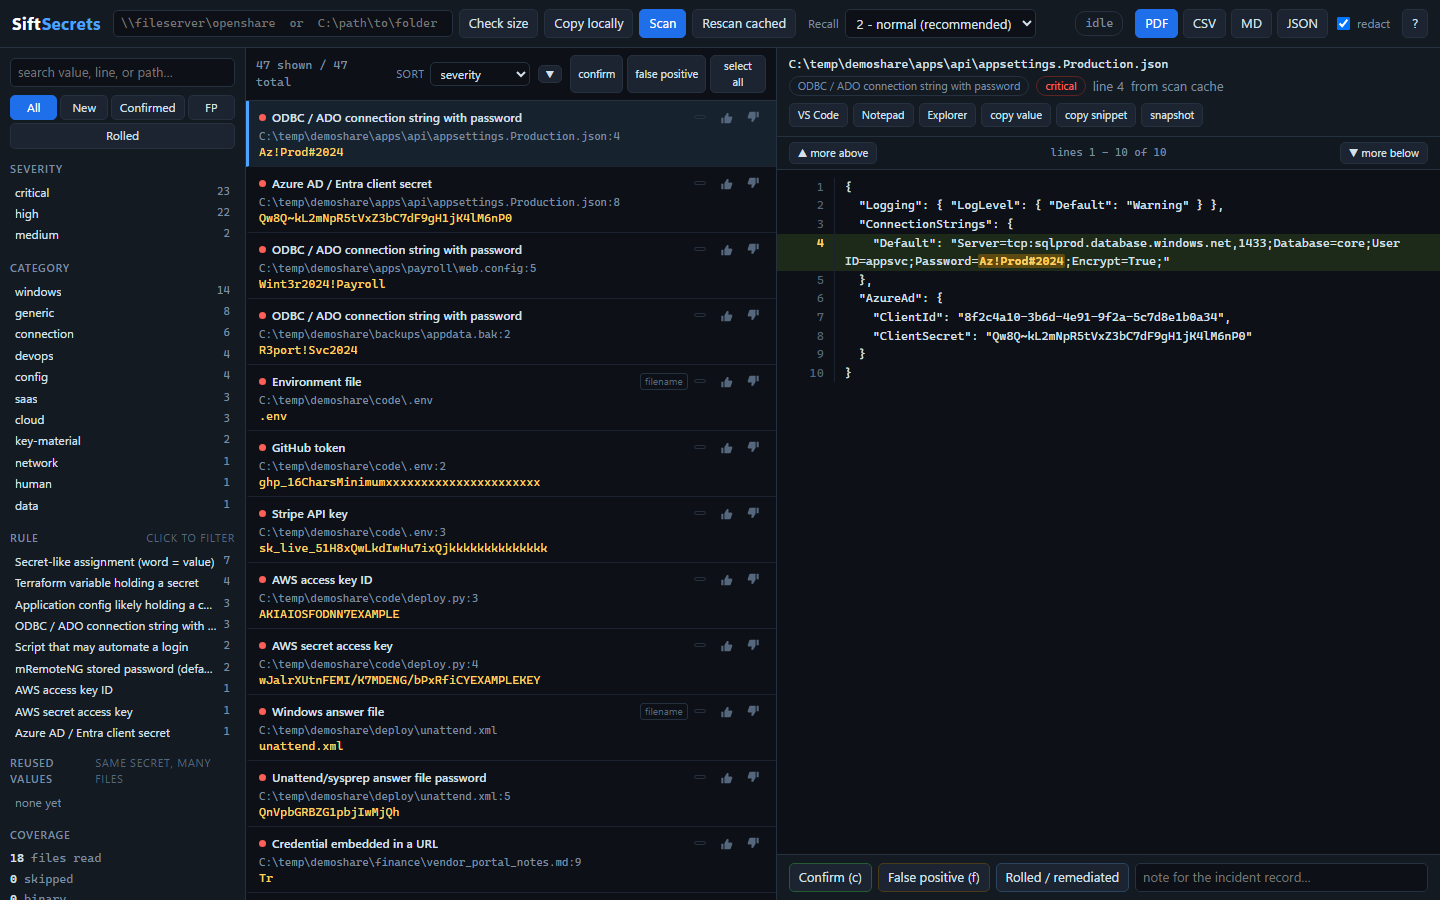 hotstartlabs/sift
Credential and sensitive-data exposure triage for file shares
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
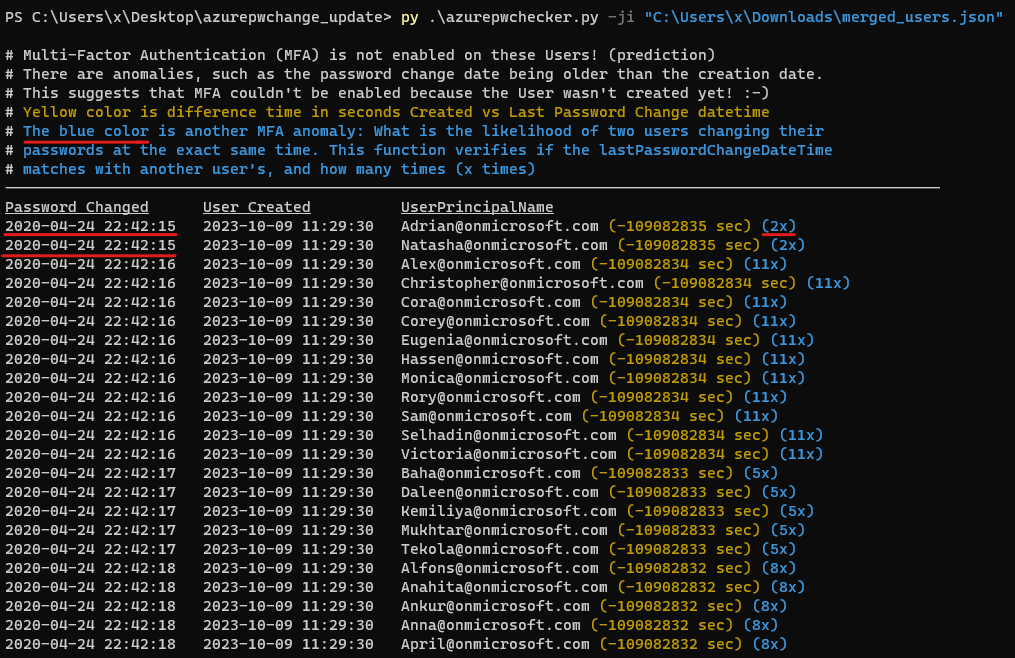 quahac/azure-ad-password-checker
Azure AD Password Checker
 cybercentrecanada/cart
Python implementation of the CaRT library for (un)inerting files.