

MemGuard
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
defensive-toolsdigital-forensicsincident-response+4
prox0959/memguardZero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
 wavestone-cdt/edrsandblast
Weaponizes vulnerable signed drivers to bypass EDR kernel callbacks, object callbacks, ETW TI provider, and userland hooks for LSASS memory dumping…
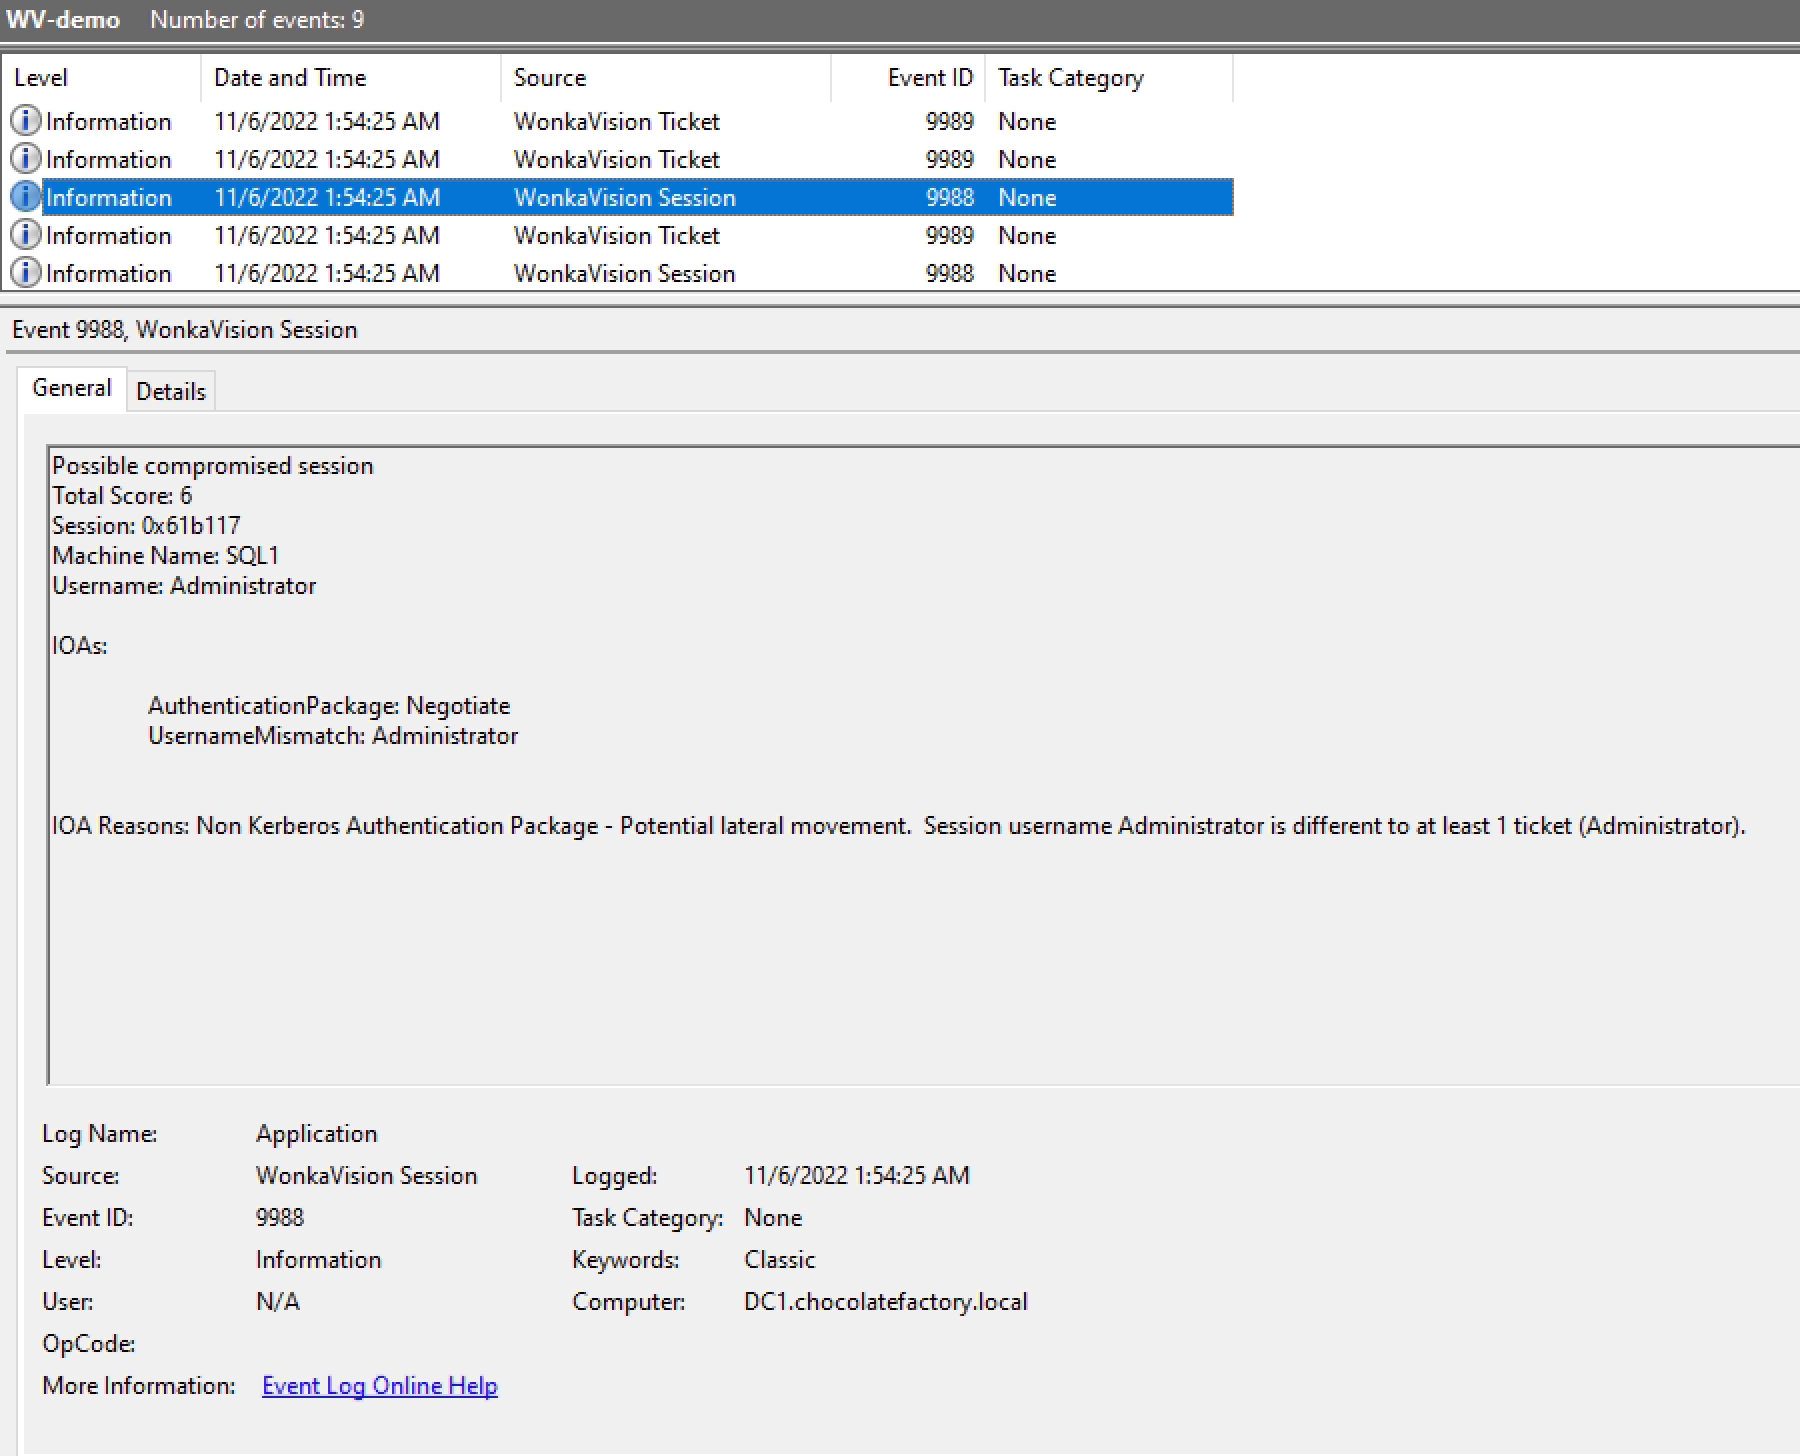 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
 rankthree/soc-detection-t1003.001-cve-2021-40444
SOC detection rules and content for T1003.001 LSASS credential dumping and CVE-2021-40444 exploitation activity.
 xacone/bestedrofthemarket
Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).