
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
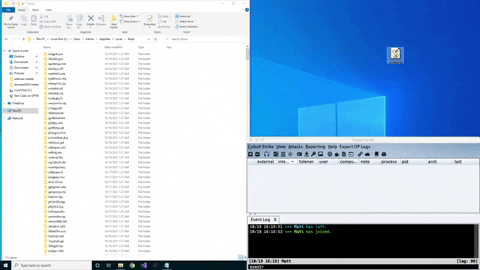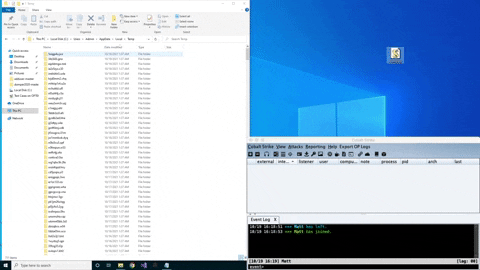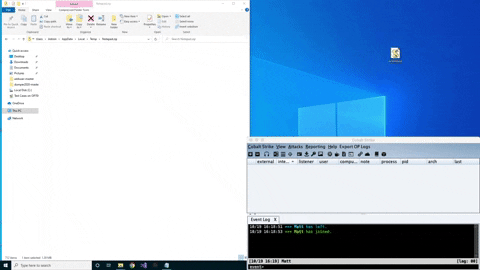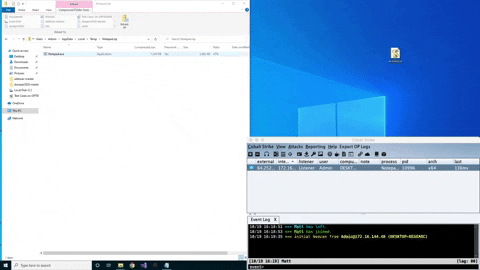 tylous/zipexec
A unique technique to execute binaries from a password protected zip
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 blacksnufkin/ghostdriver
yet another AV killer tool using BYOVD
 danielbohannon/invoke-cradlecrafter
PowerShell Remote Download Cradle Generator & Obfuscator
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…