
cowrie
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
defensive-toolsincident-responseinformation-gathering+3
6.5k6 days ago
cowrie/cowrieCowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 idnahacks/goodhound
Uses Sharphound, Bloodhound and Neo4j to produce an actionable list of attack paths for targeted remediation.
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 mziqudhd92/honeypot-auditor
Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like a low-interaction honeypot — Shodan…
 pwndexter/sharpedrchecker
C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…
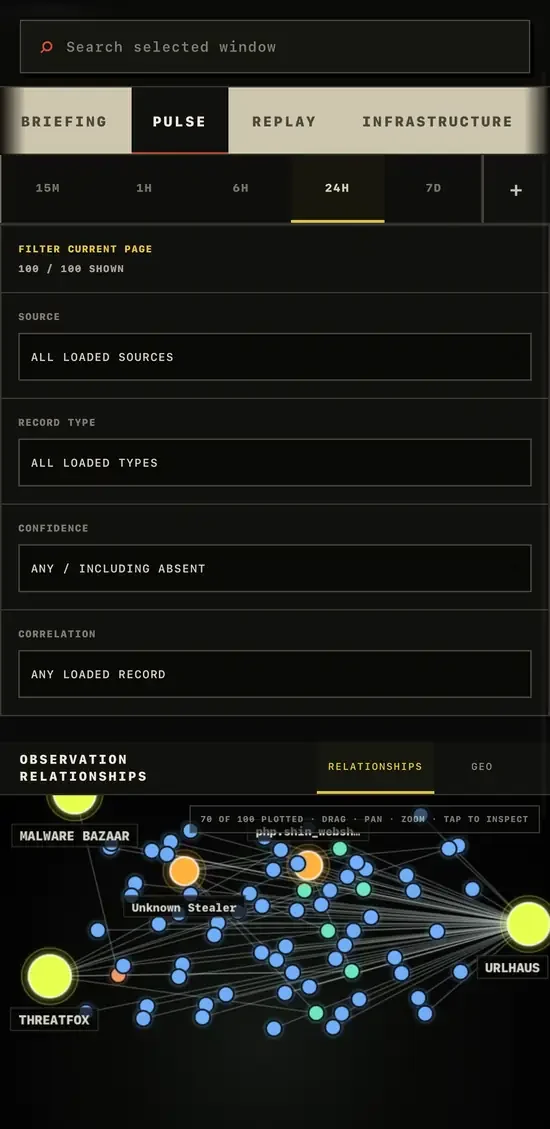
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
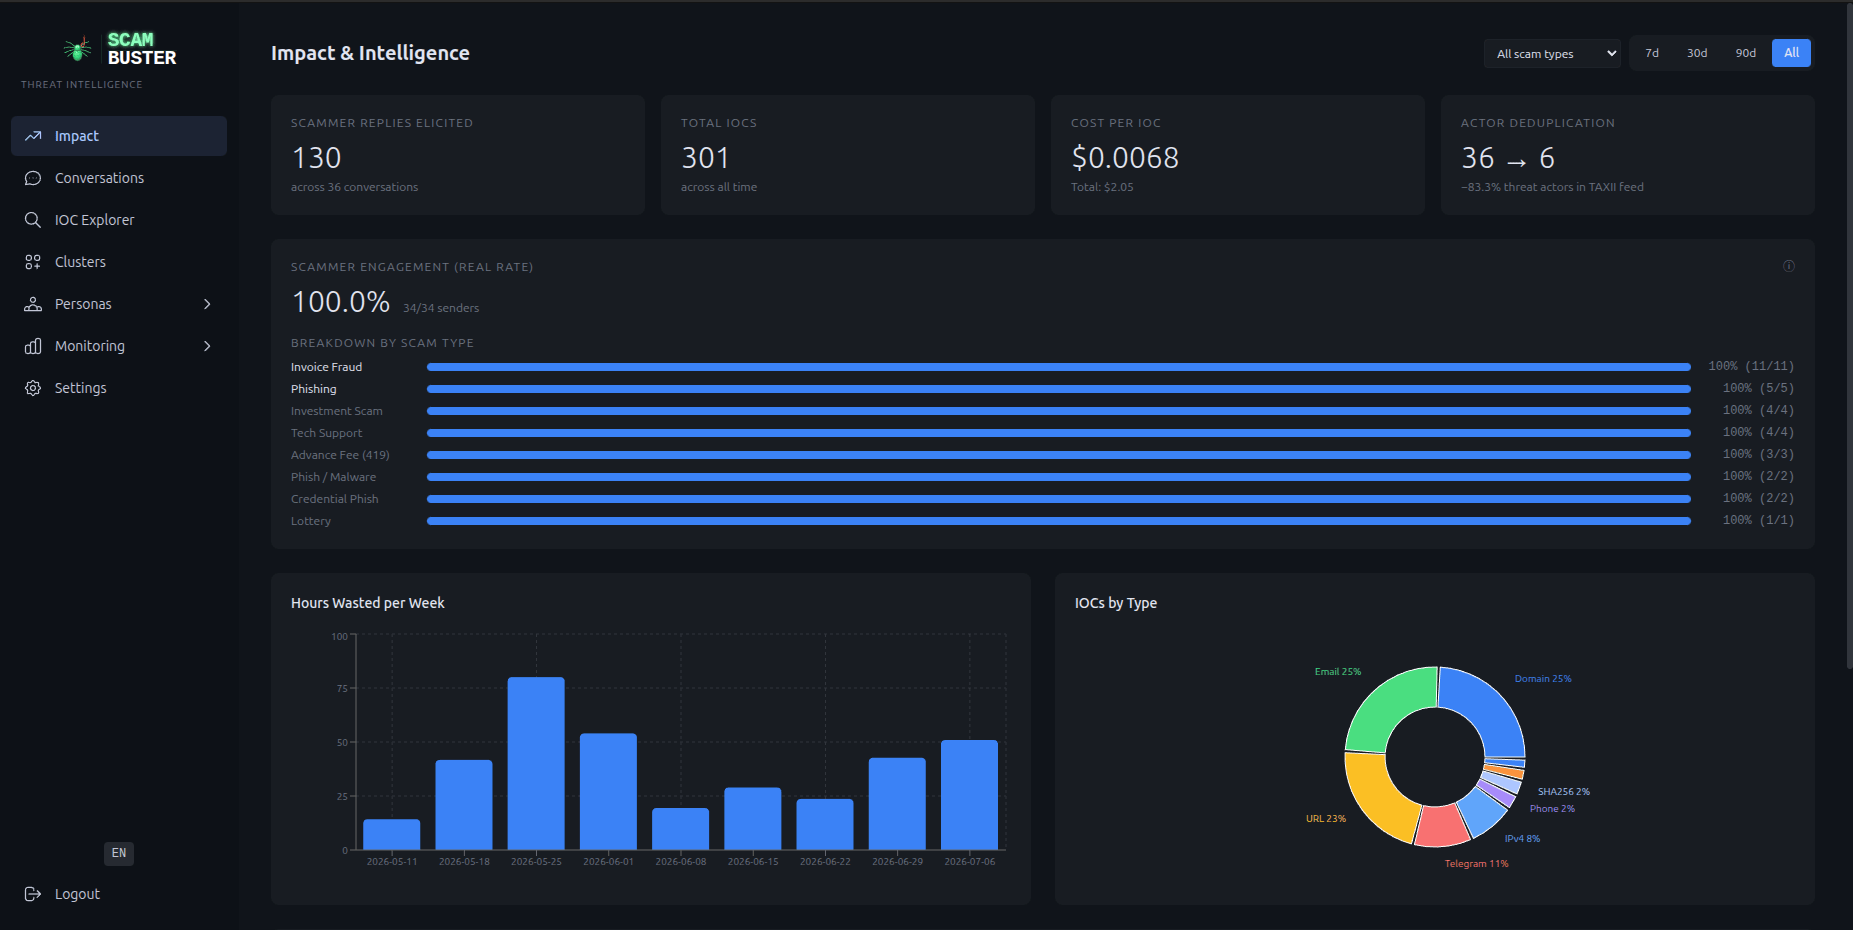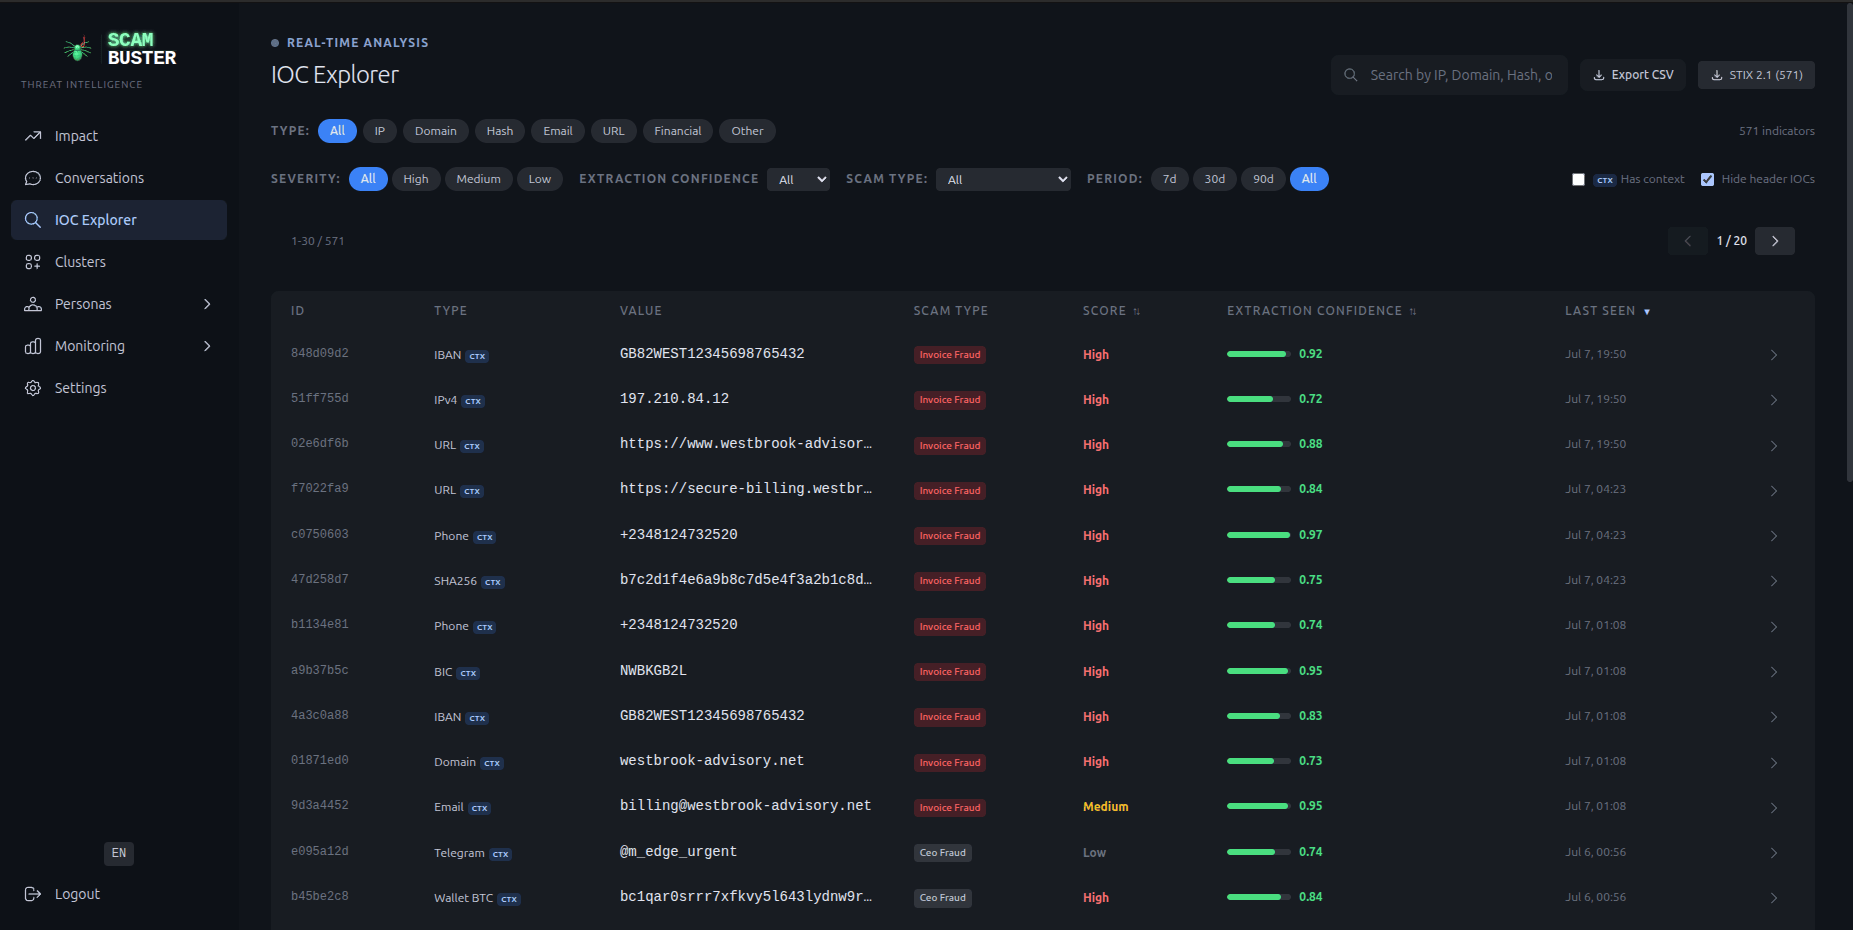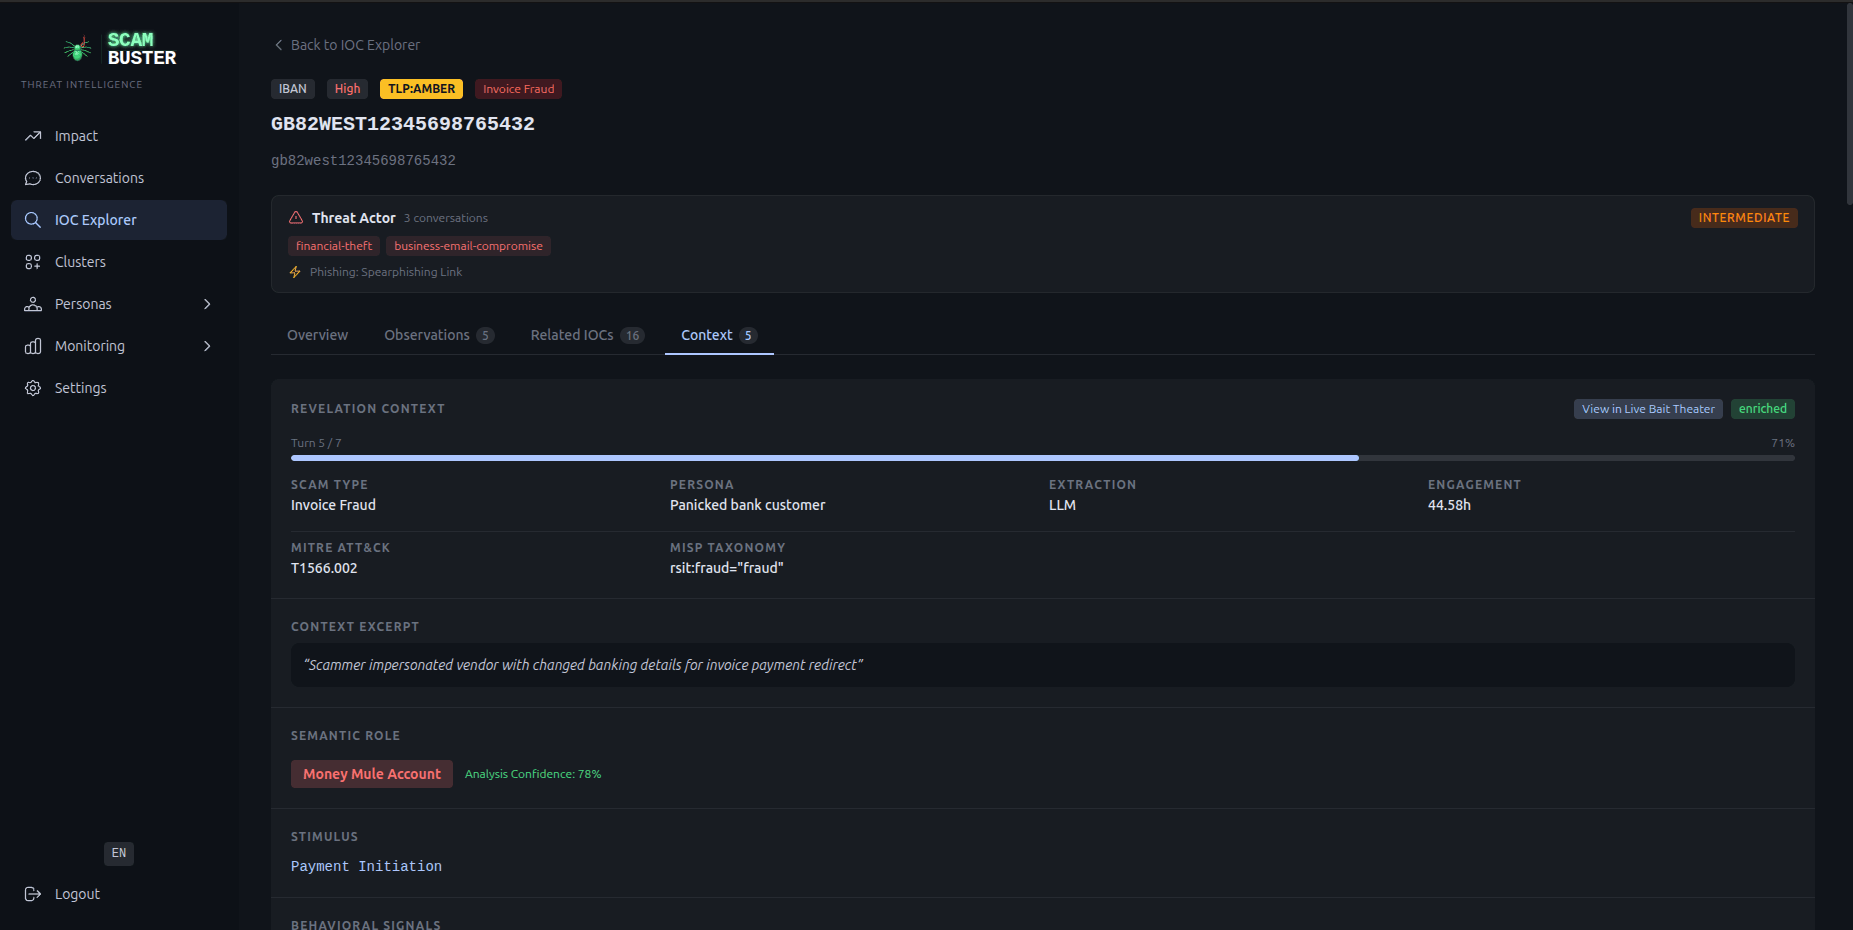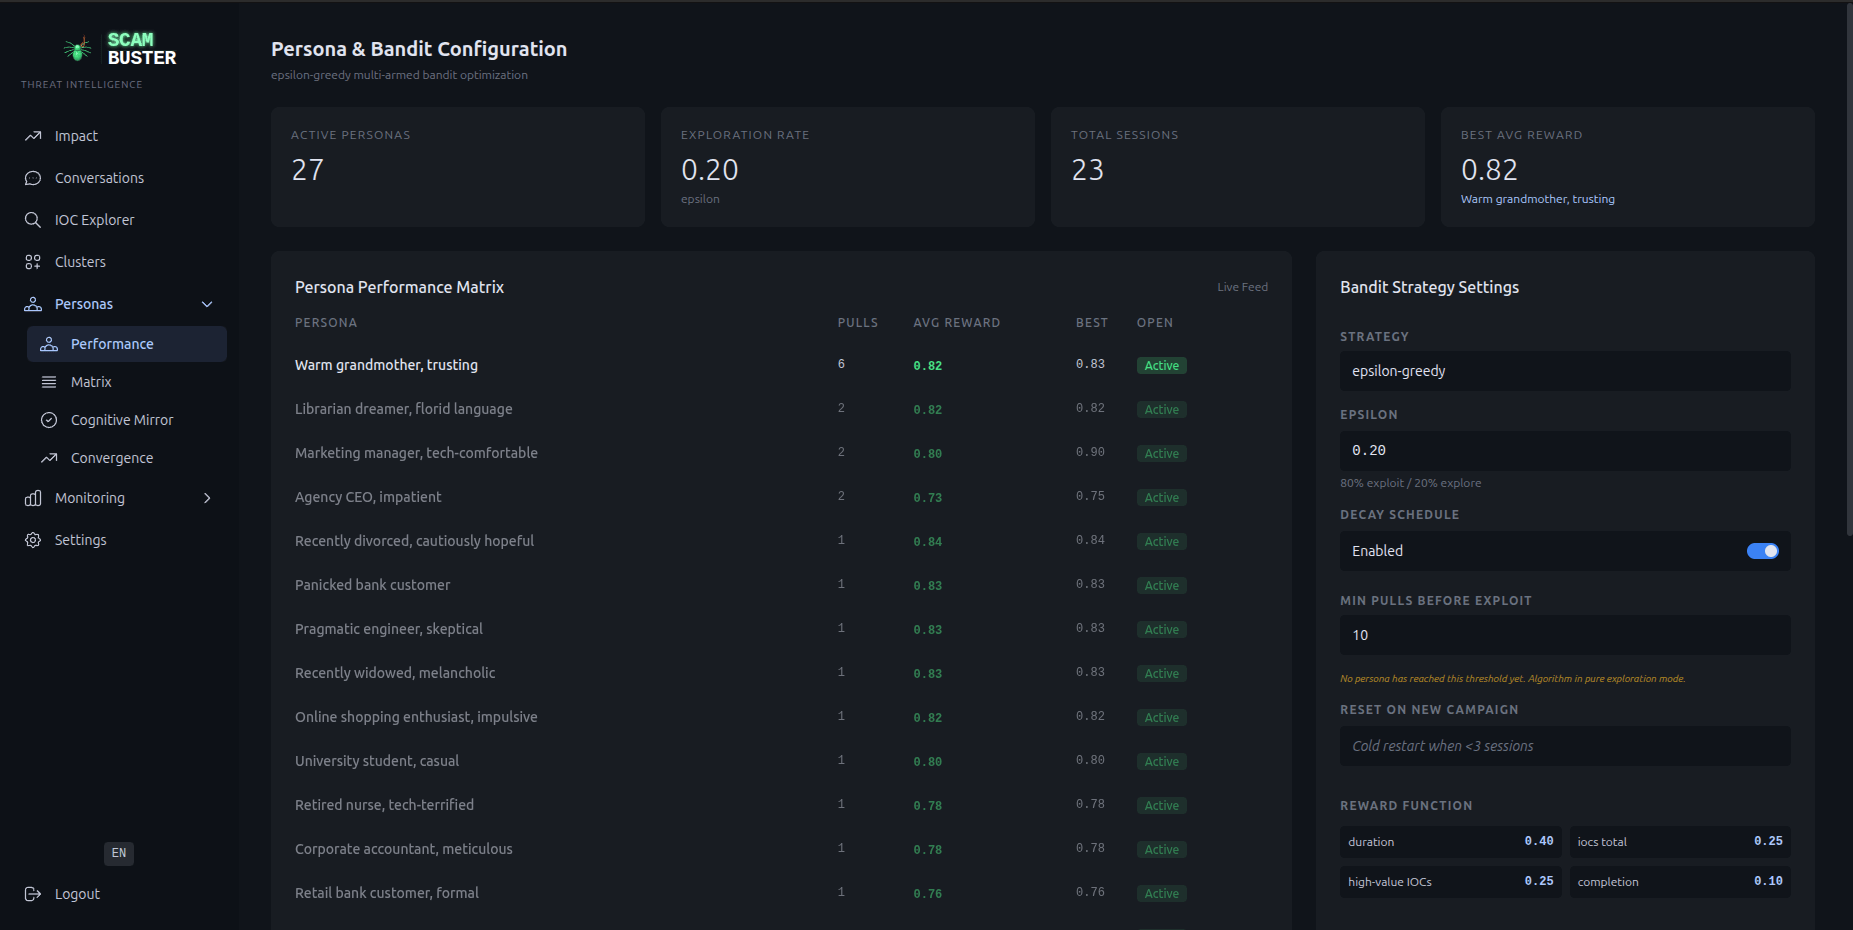 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
 specterops/bloodhound
Six Degrees of Domain Admin
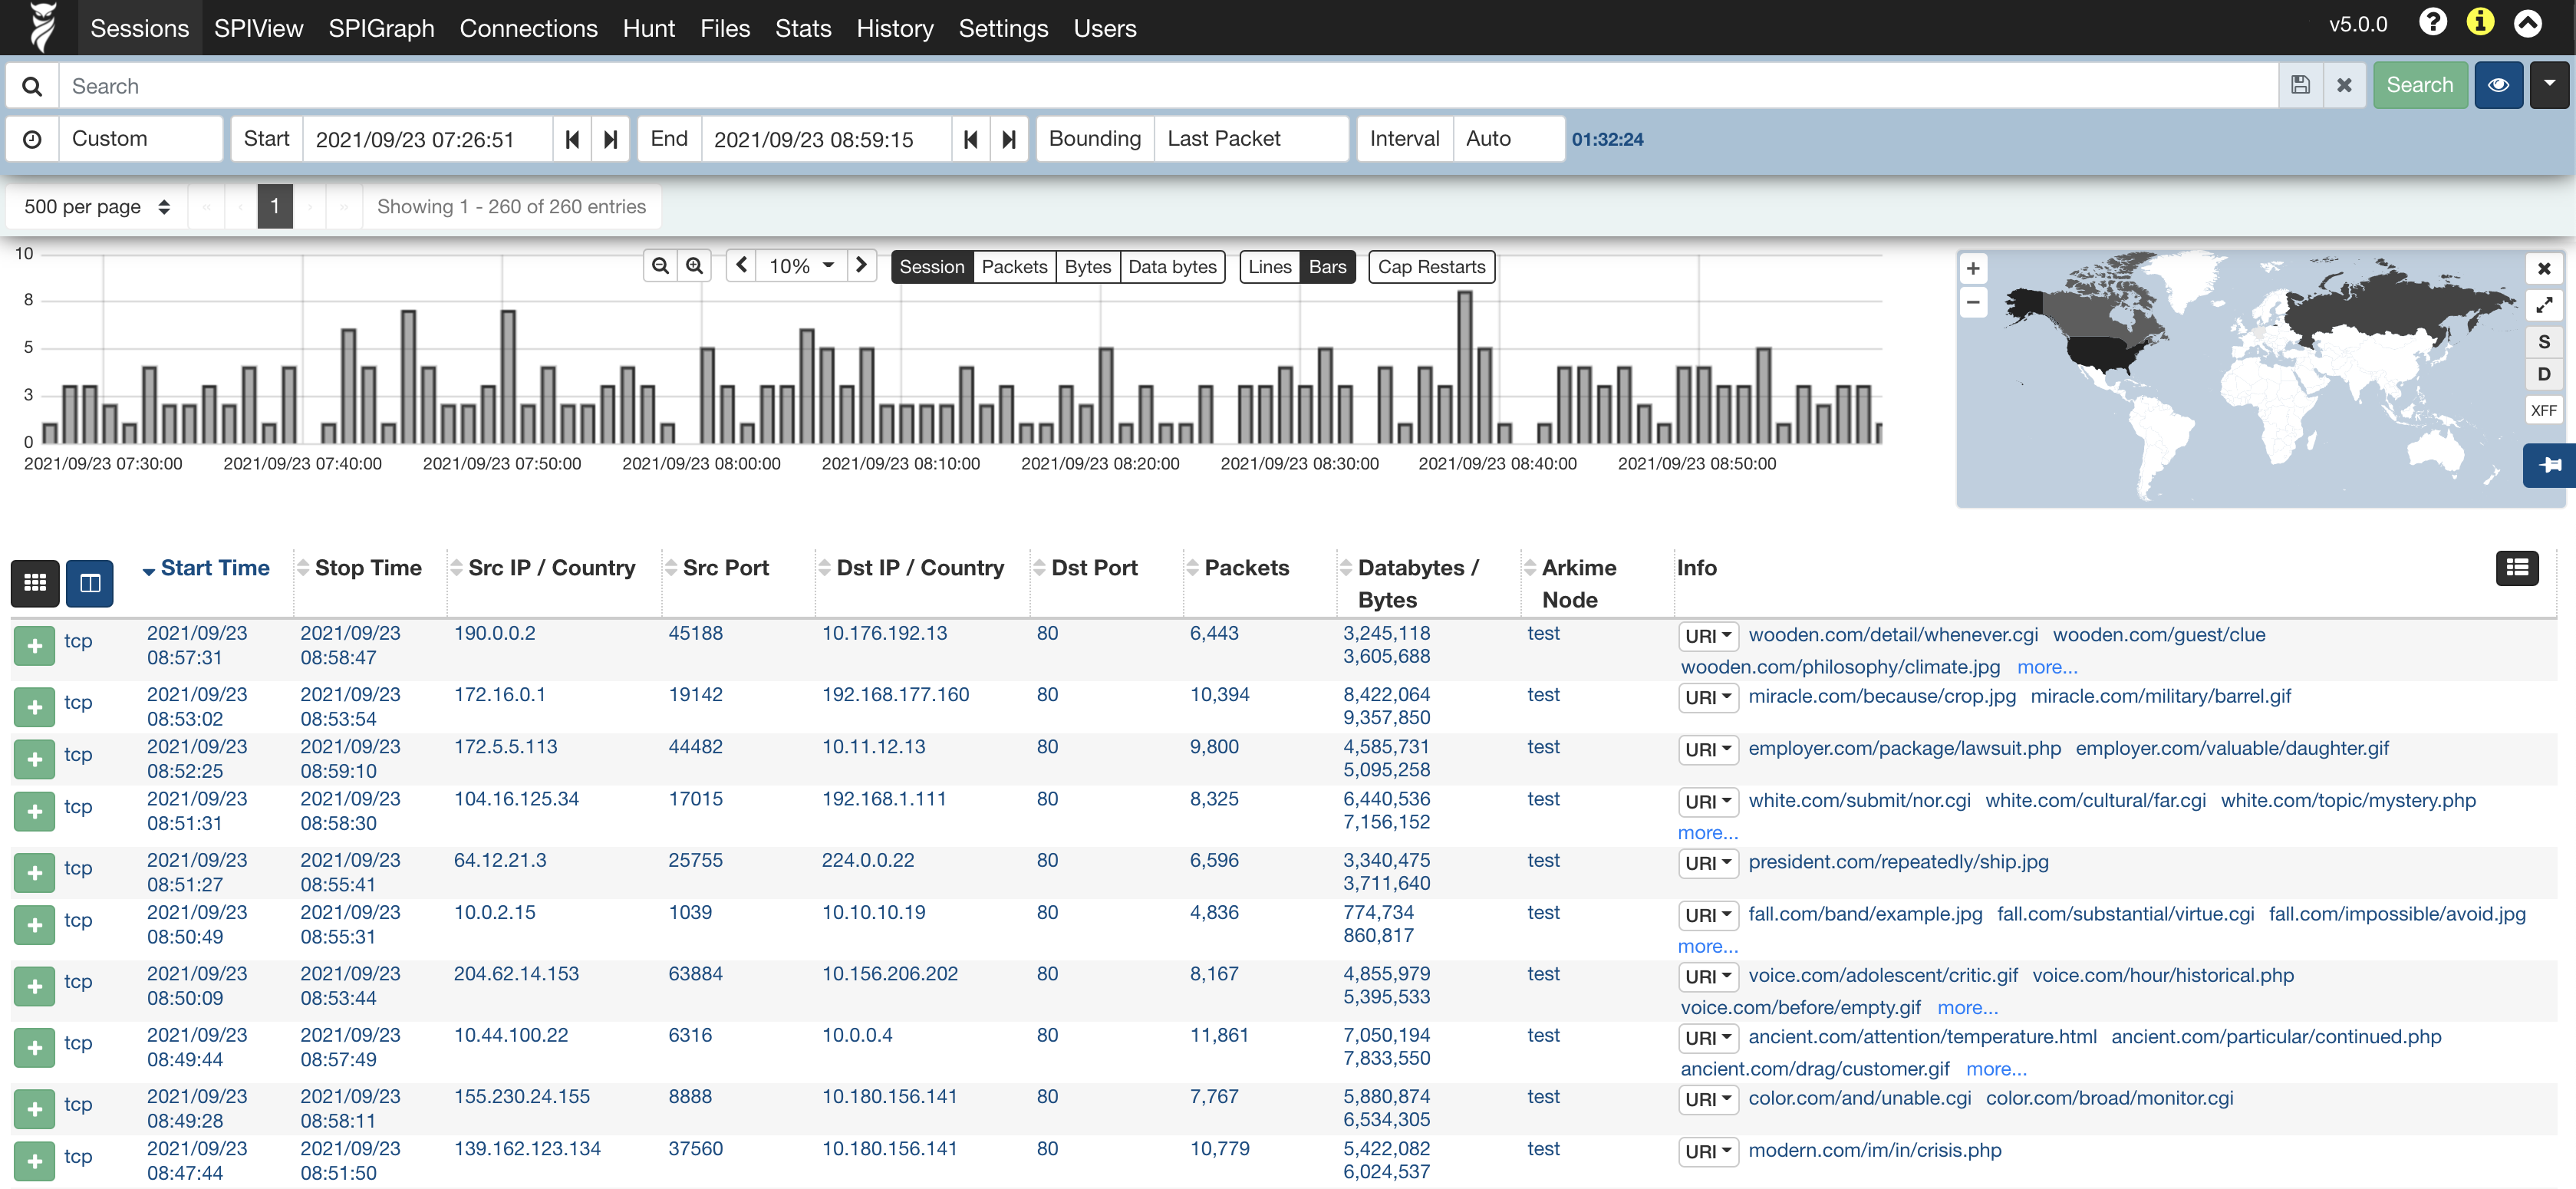 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 ransomlook/ransomlook
Yet another Ransomware gang tracker
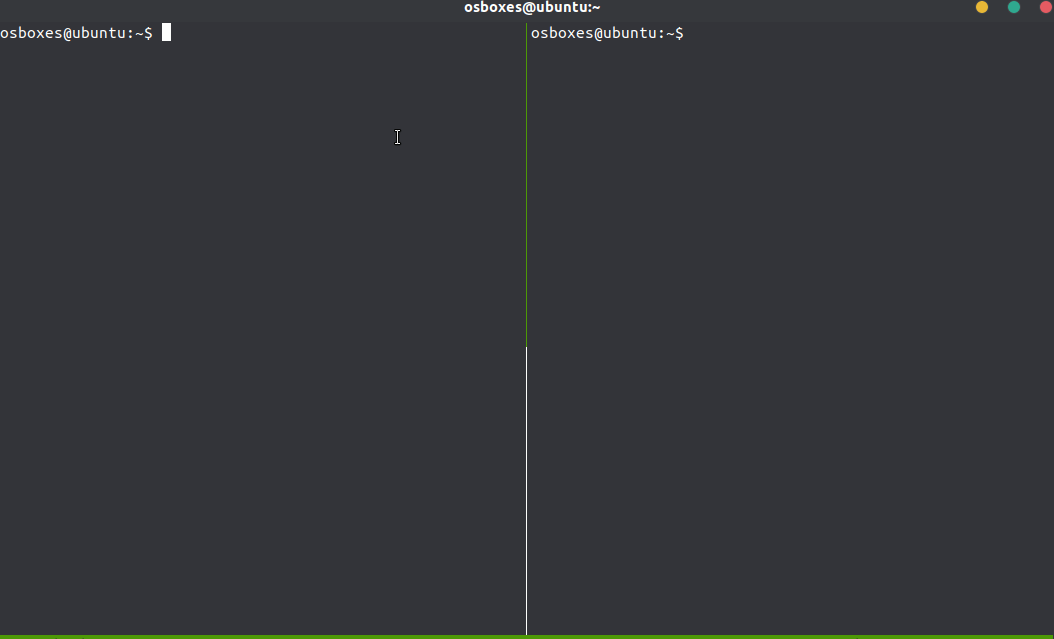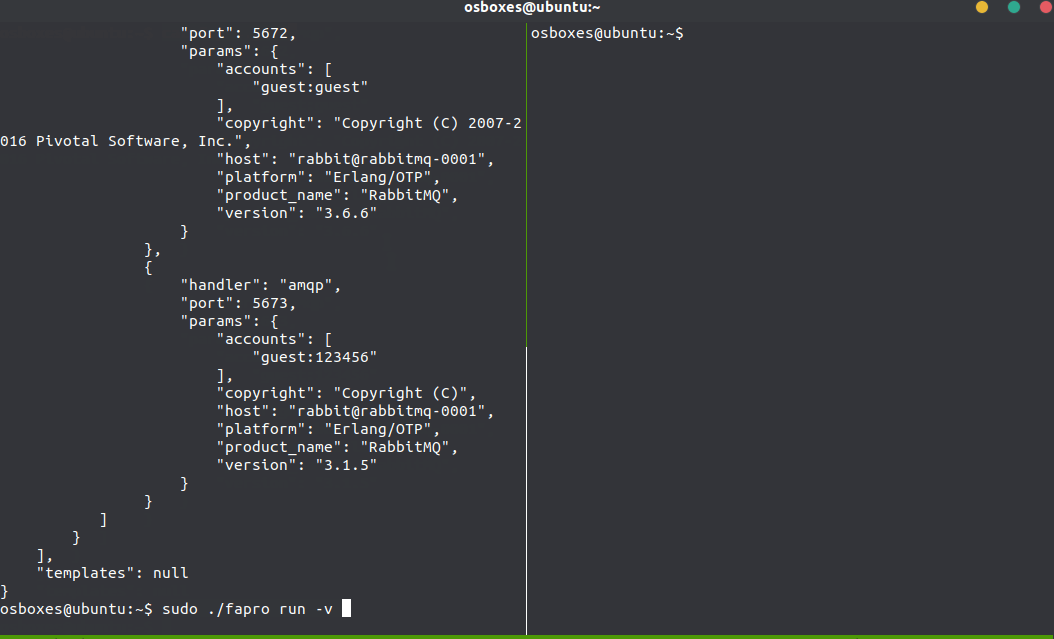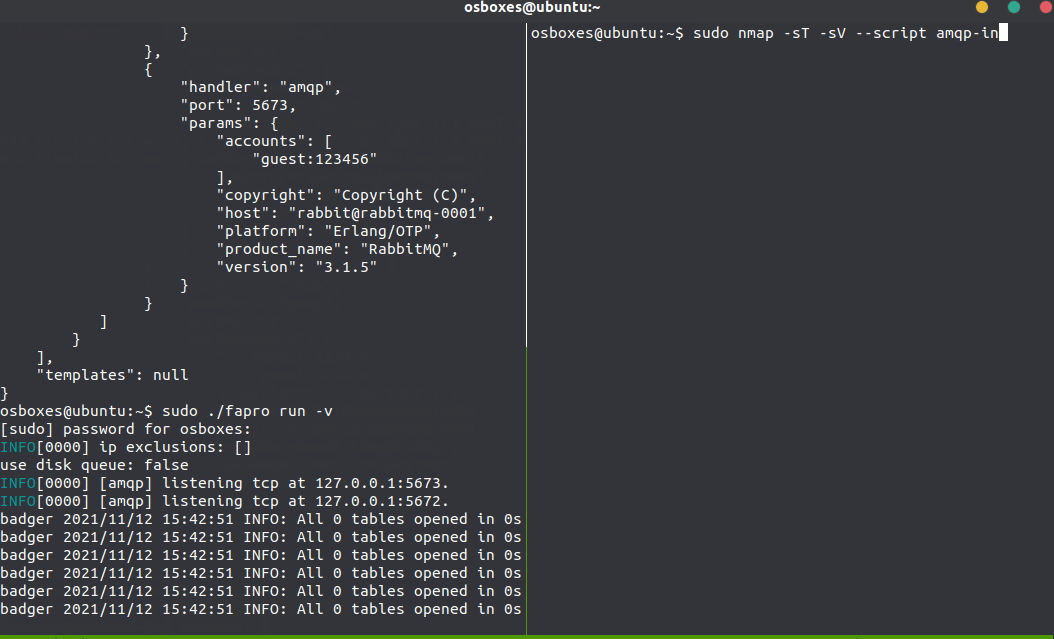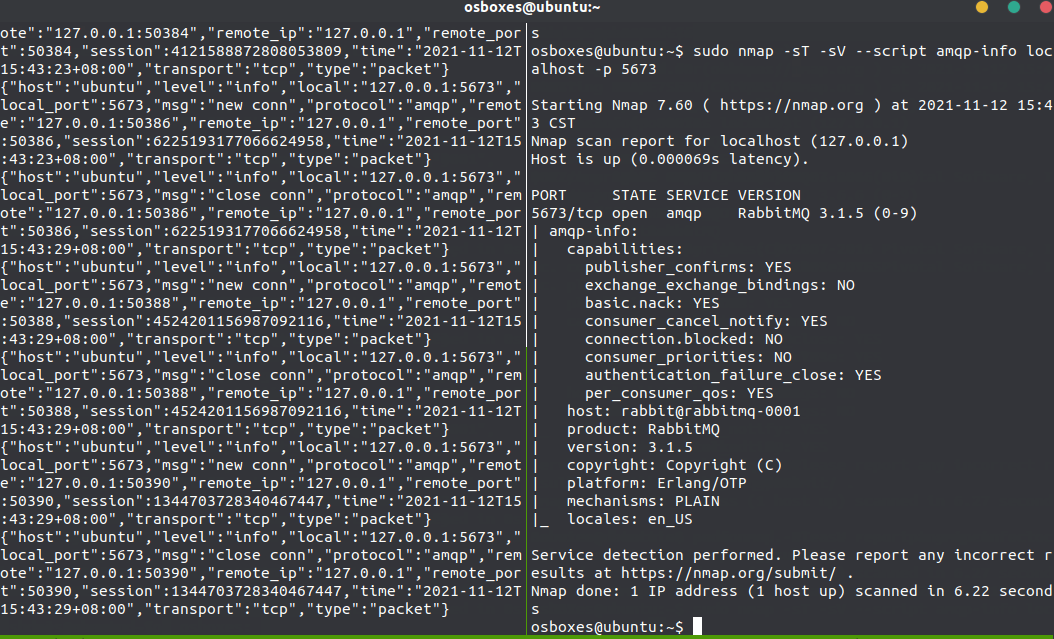 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
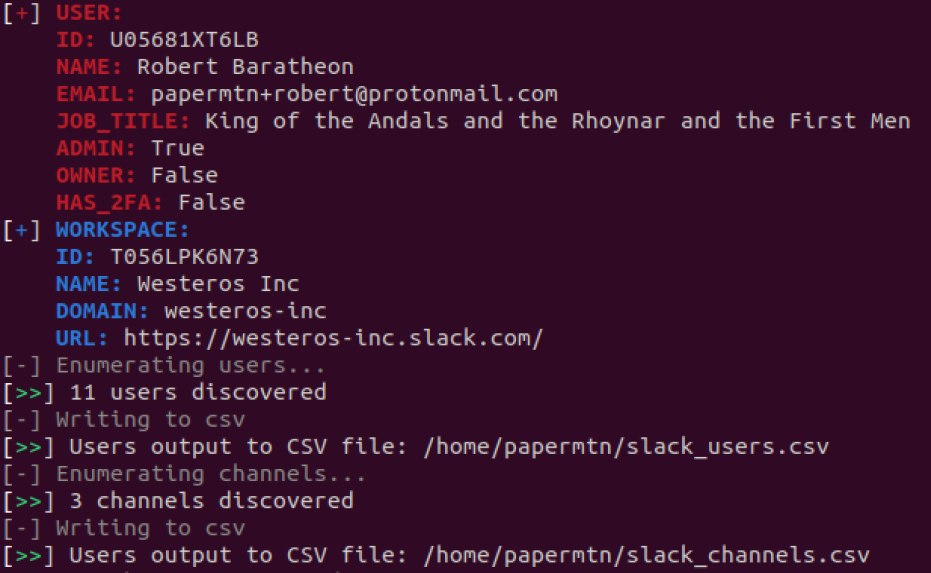 papermtn/slack-watchman
Slack enumeration and exposed secrets detection tool
 spinfosecurity/rail-ot-protector
Rail-OT-Protector (ROP) — free, open-source cybersecurity scanning tool for rail and transit OT/SCADA networks. PowerShell + Bash scanners for…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
