QuickAssist_UAC_Bypass

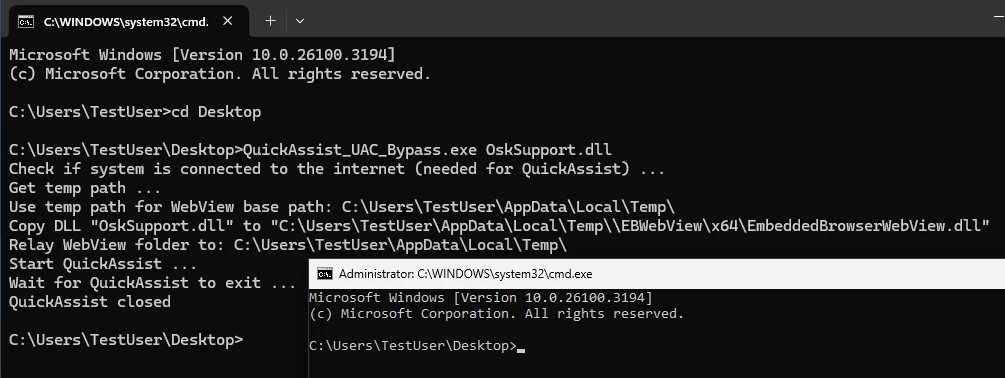
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

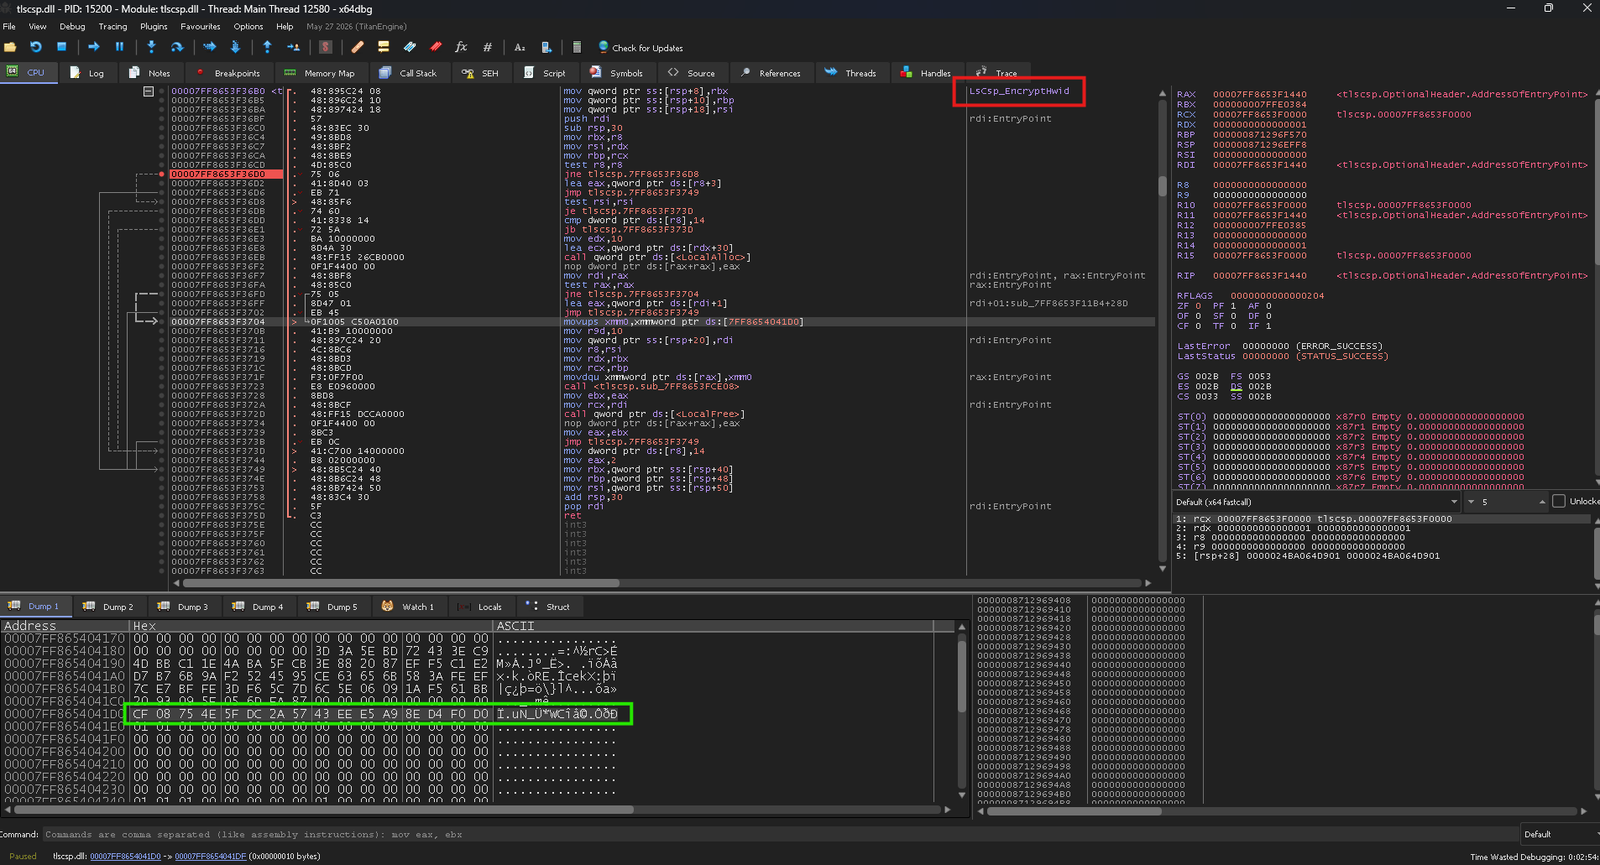
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

Debugger utilizing stealth hooks to hide from debugger detection

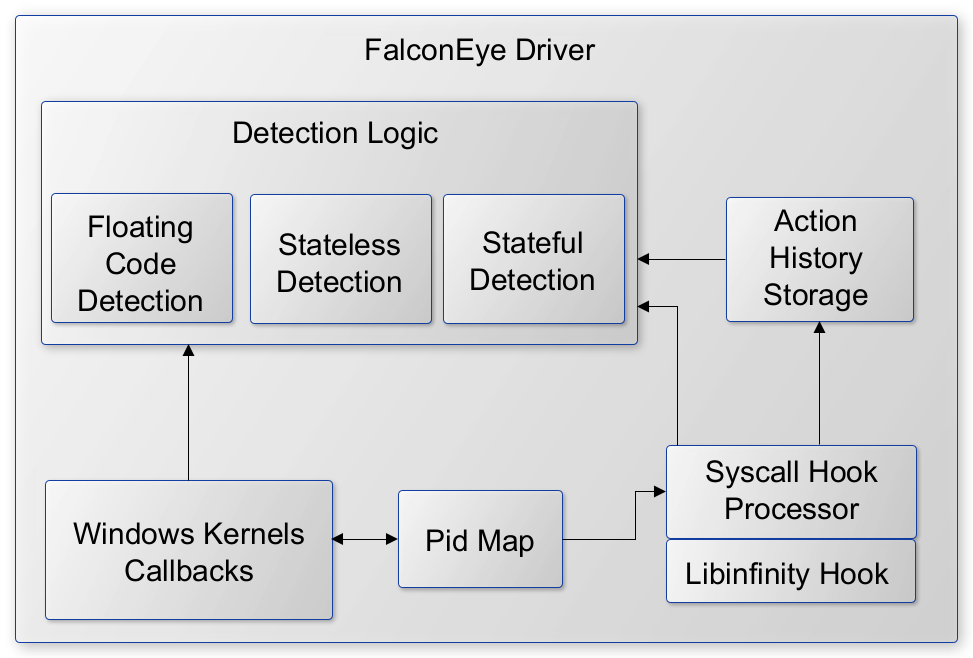
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection

Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.


Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…

Memory API proxy via signed mozglue.dll

Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…

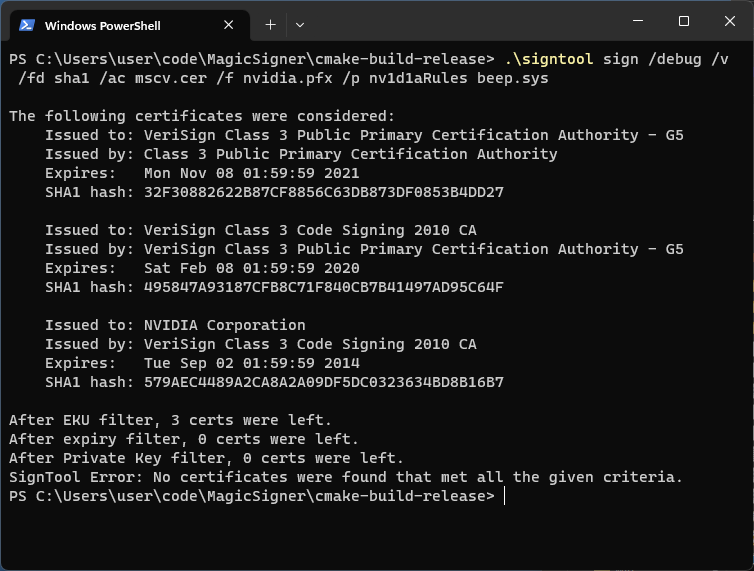
Signtool for expired certificates

Generate an obfuscated DLL that will disable AMSI & ETW

LoadLibrary for offensive operations