
jetty-line-check
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
configuration-auditingdefensive-toolsstatic-analysis+4
xiaoqimikko/jetty-line-checkCVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
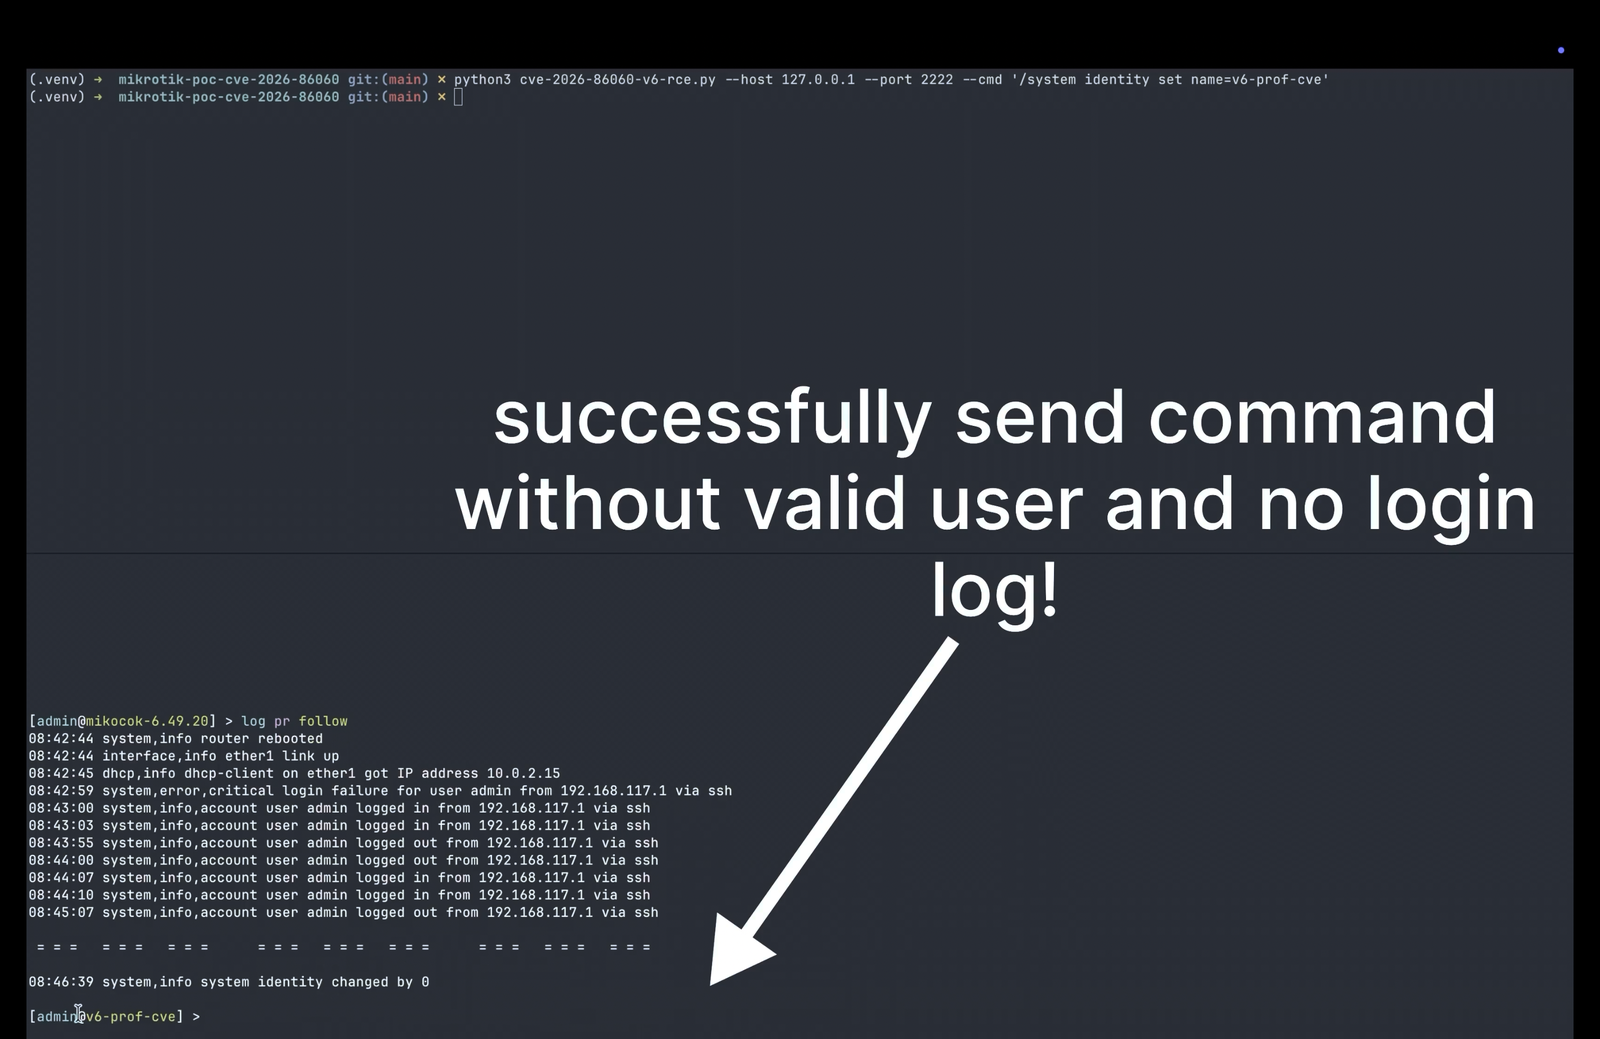 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 bara-almustafa/cve-2026-34990-poc
CVE-2026-34990 — CUPS <= 2.4.16 Local Privilege Escalation
 ermensonx/sudotimewarp-cve-2026-96512-
Reproduction and PoC scripts for CVE-2026-96512 (SudoTimeWarp), where the caller's TZ shifts sudoers NOTBEFORE/NOTAFTER windows, plus mitigation…
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 aoripus-ltd/zapscape-fix
Generic kernel live patch for the KVM/x86 shadow-MMU use-after-free (Zapscape, CVE-2026-64561)
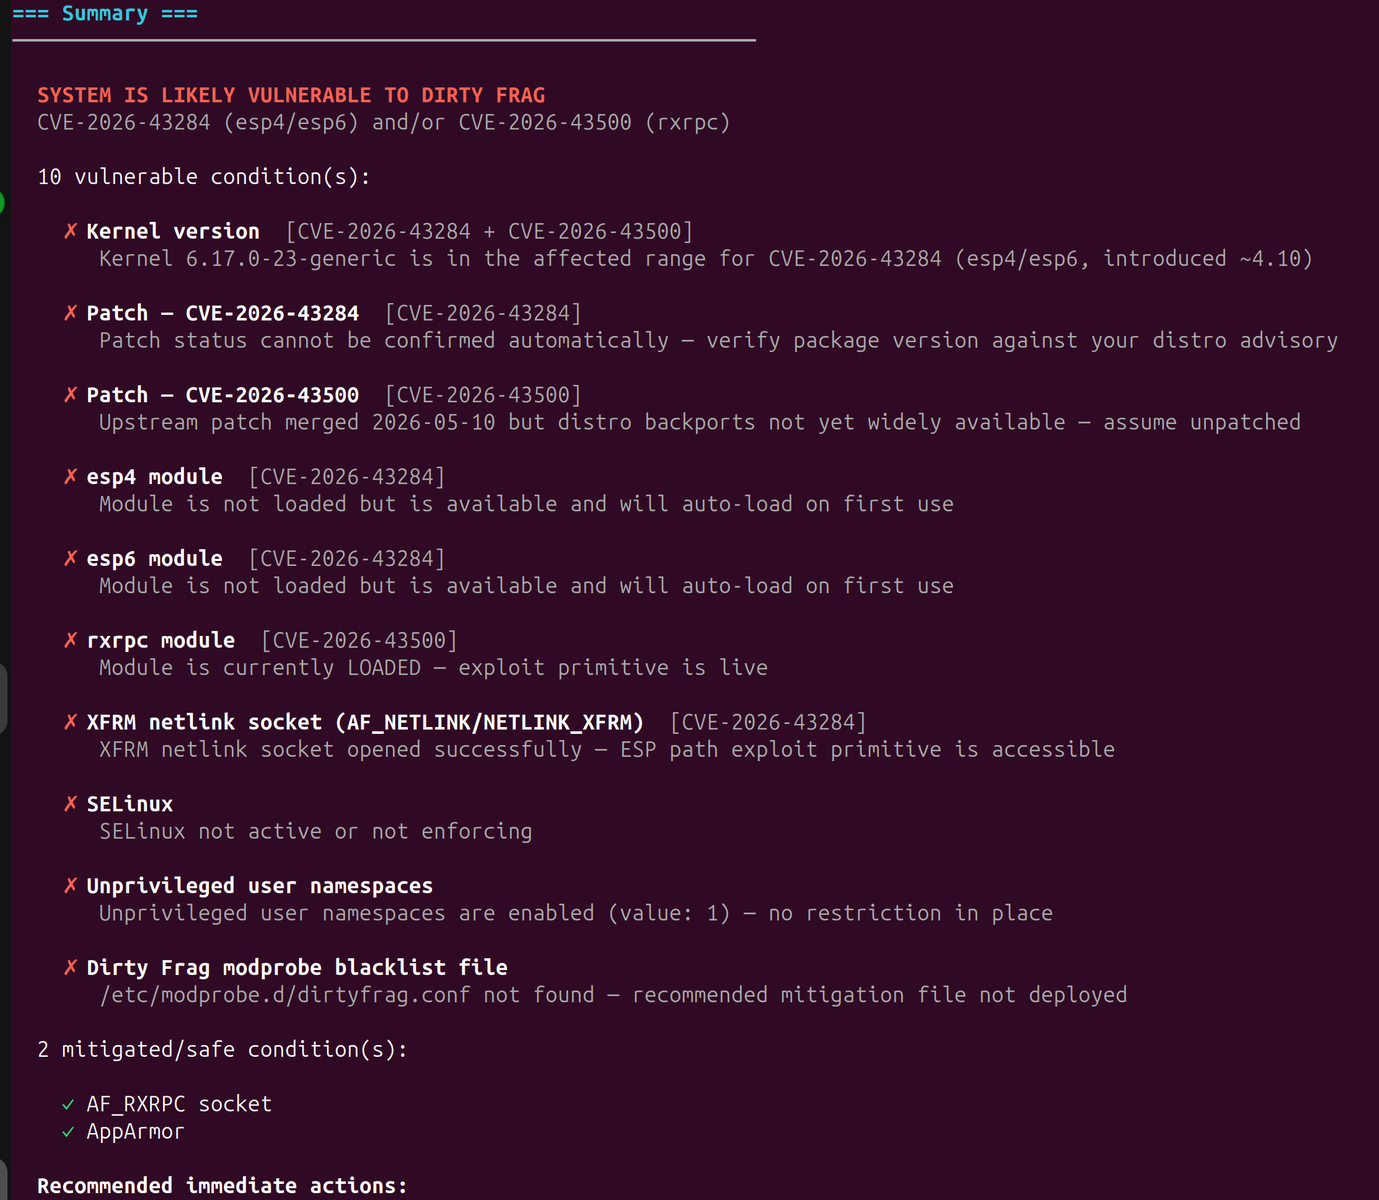 liamromanis101/dirtyfrag-detector
CVE-2026-43284/CVE-2026-43500 'DirtyFrag' Benign patch & mitigation detection script
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 danindiana/cve-2026-32746-mitigation
Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
 detect-defenselab/cve-2026-31431-detection-defense
Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…