
CVE-2023-49070
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
command-and-controldefensive-toolsexploitation+5
bardlaudian/cve-2023-49070Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
 ml-k-eng/cve-2023-38831-exploit-and-detection
This repository has both an attack detection tool and a Proof-of-Concept (PoC) Python script for the WinRAR CVE-2023-38831 vulnerability.
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 ridsoliveira/fix-cve-2023-36884
PowerShell script to apply Microsoft's recommended registry-based workaround for CVE-2023-36884, mitigating remote code execution risk on Windows…
 borsch-appreciator/soc235---atlassian-confluence-broken-access-control-0-day-cve-2023-22515
SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…
 ig-labs/edr-alpc-block-poc
Blocking Windows EDR agents by registering an own IPC-object in the Object Manager’s namespace (CVE-2023-3280, CVE-2024-5909, CVE-2024-20671)
 aka76bm/google-chrome-emergency-update
Emergency Chrome update information and tools for CVE-2023-7024 and other critical vulnerabilities
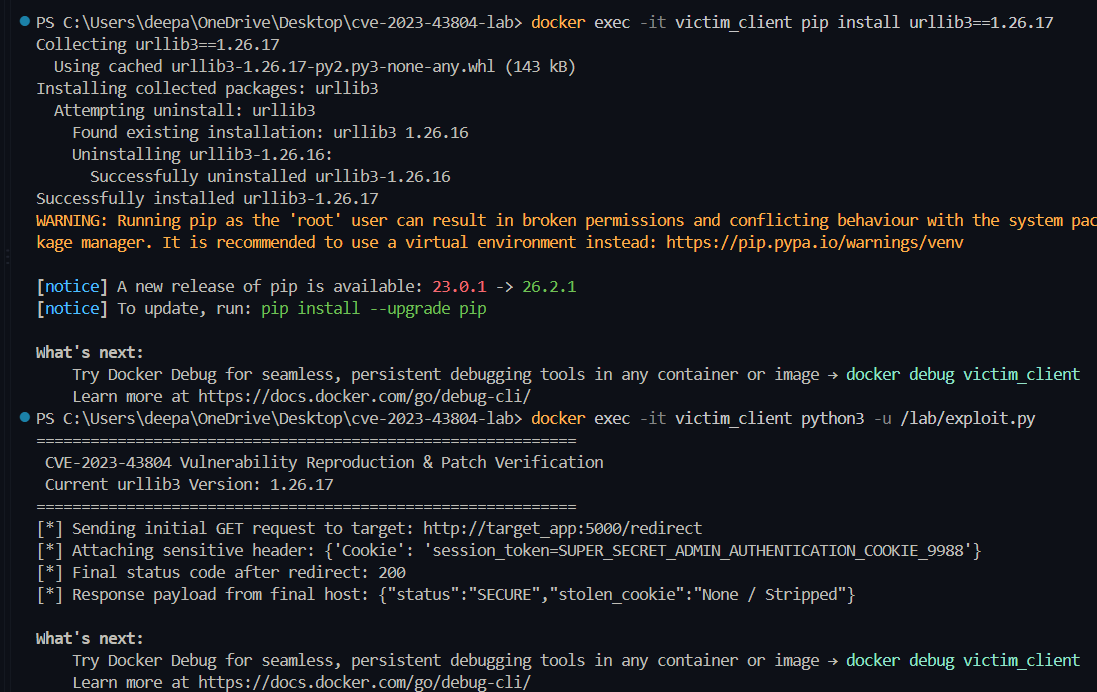 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 nosrevytsng/metabase-pre-auth-rce-poc
CVE-2023-38646
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 ysaxon/pyrocms-ssti-fix
A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.