
TransparentTorProxy
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
command-and-controldefensive-toolsdns-analysis+6
37
onyks-os/transparenttorproxyA Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 openresty/lua-resty-limit-traffic
Lua library for limiting and controlling traffic in OpenResty/ngx_lua
 gmh5225/evmbench-certora-agent-harness
Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…
 ecapuano/web-traffic-generator
A quick and dirty HTTP/S "organic" traffic generator.
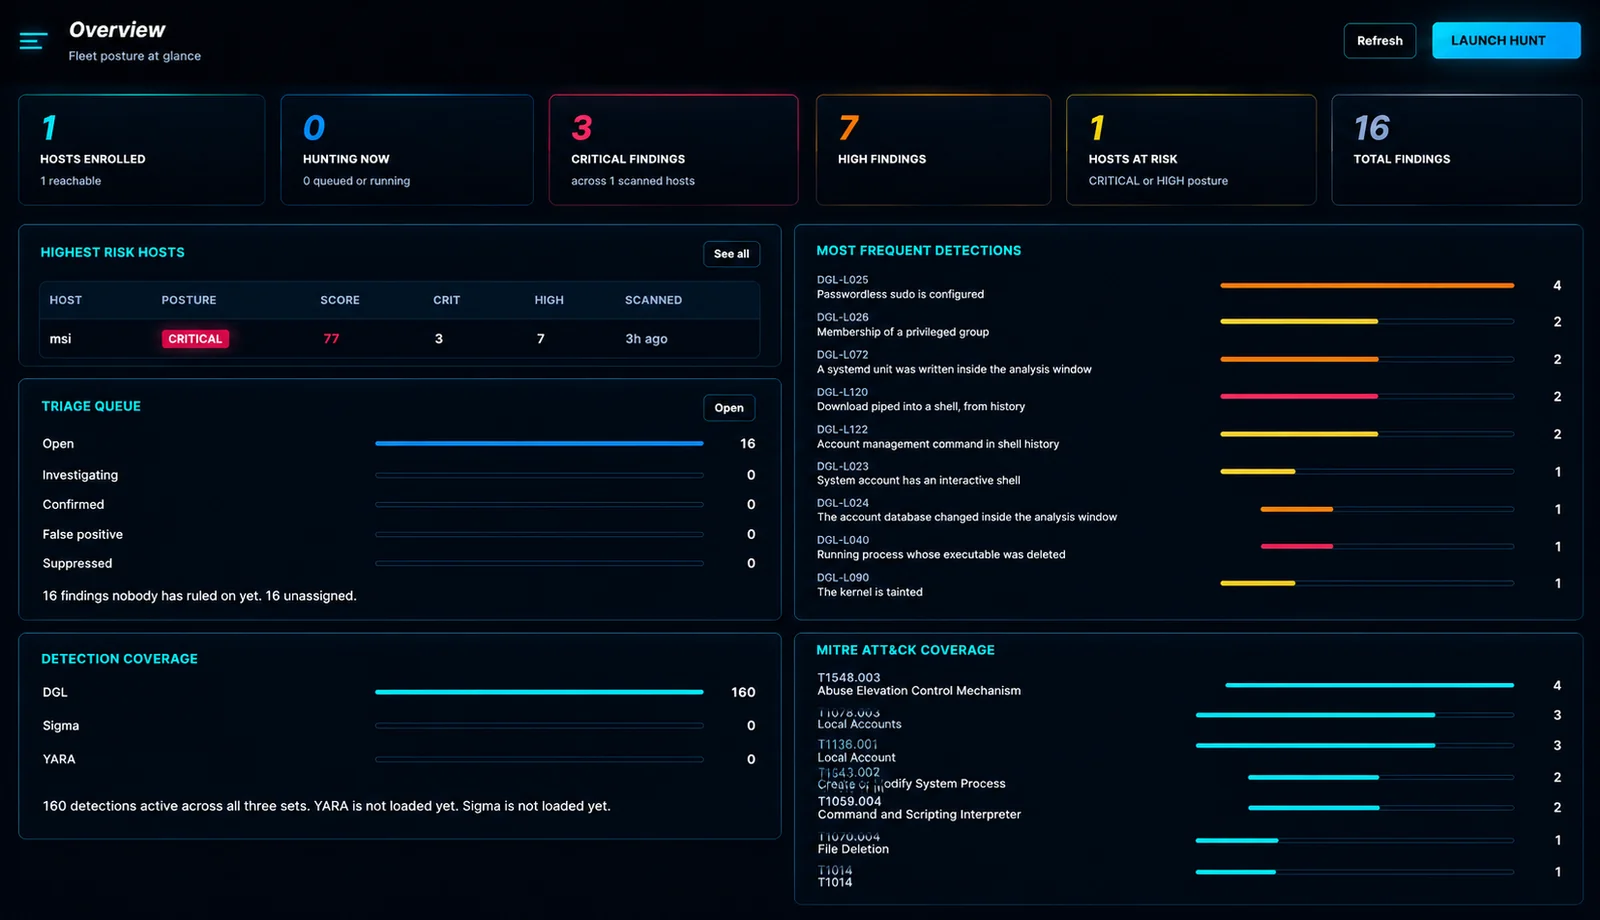 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 infiniroot/nginx-mitigate-log4shell
Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script
 hansnielsen/tiffdisabler
Disables ImageIO TIFF support to protect against CVE-2016-4631
 google/safetext
Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
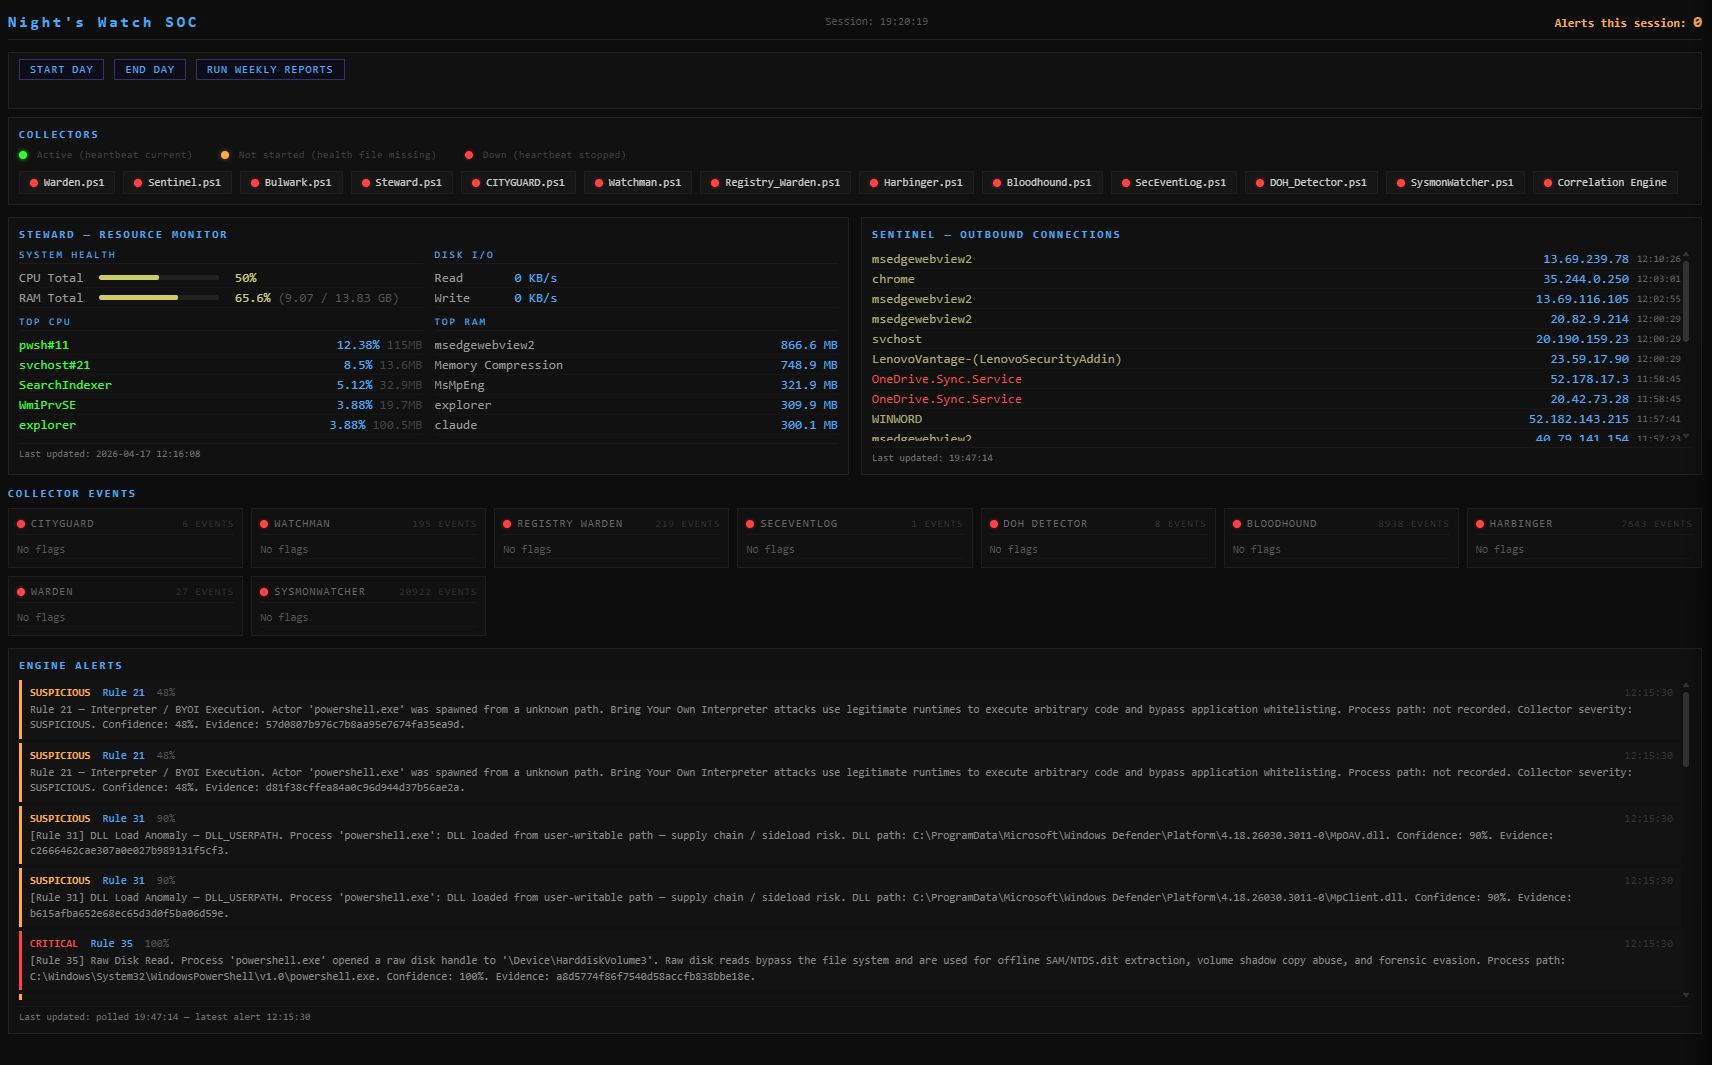 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel