
sudowp-hooks-visualizer
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
code-analysisdebuggerseducation+4
2
sudo-wp/sudowp-hooks-visualizerA security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 lauriewired/jadxecute
JADX-gui scripting plugin for dynamic decompiler manipulation
 chichou/vscode-frida
Unofficial frida extension for VSCode
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 lmacken/pyrasite
Inject code into running Python processes
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
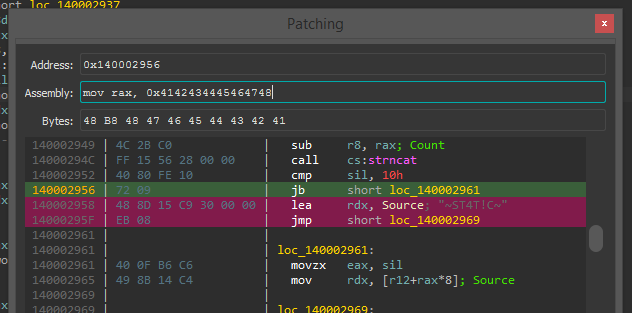 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM