
Flutter-Reverse-Engineering-Labs
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
android-securitybinary-analysisctf+6
59
brnpl/flutter-reverse-engineering-labsHands-on challenges for learning how to reverse engineer Flutter applications.
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 frida/frida
Main repo for hosting release binaries
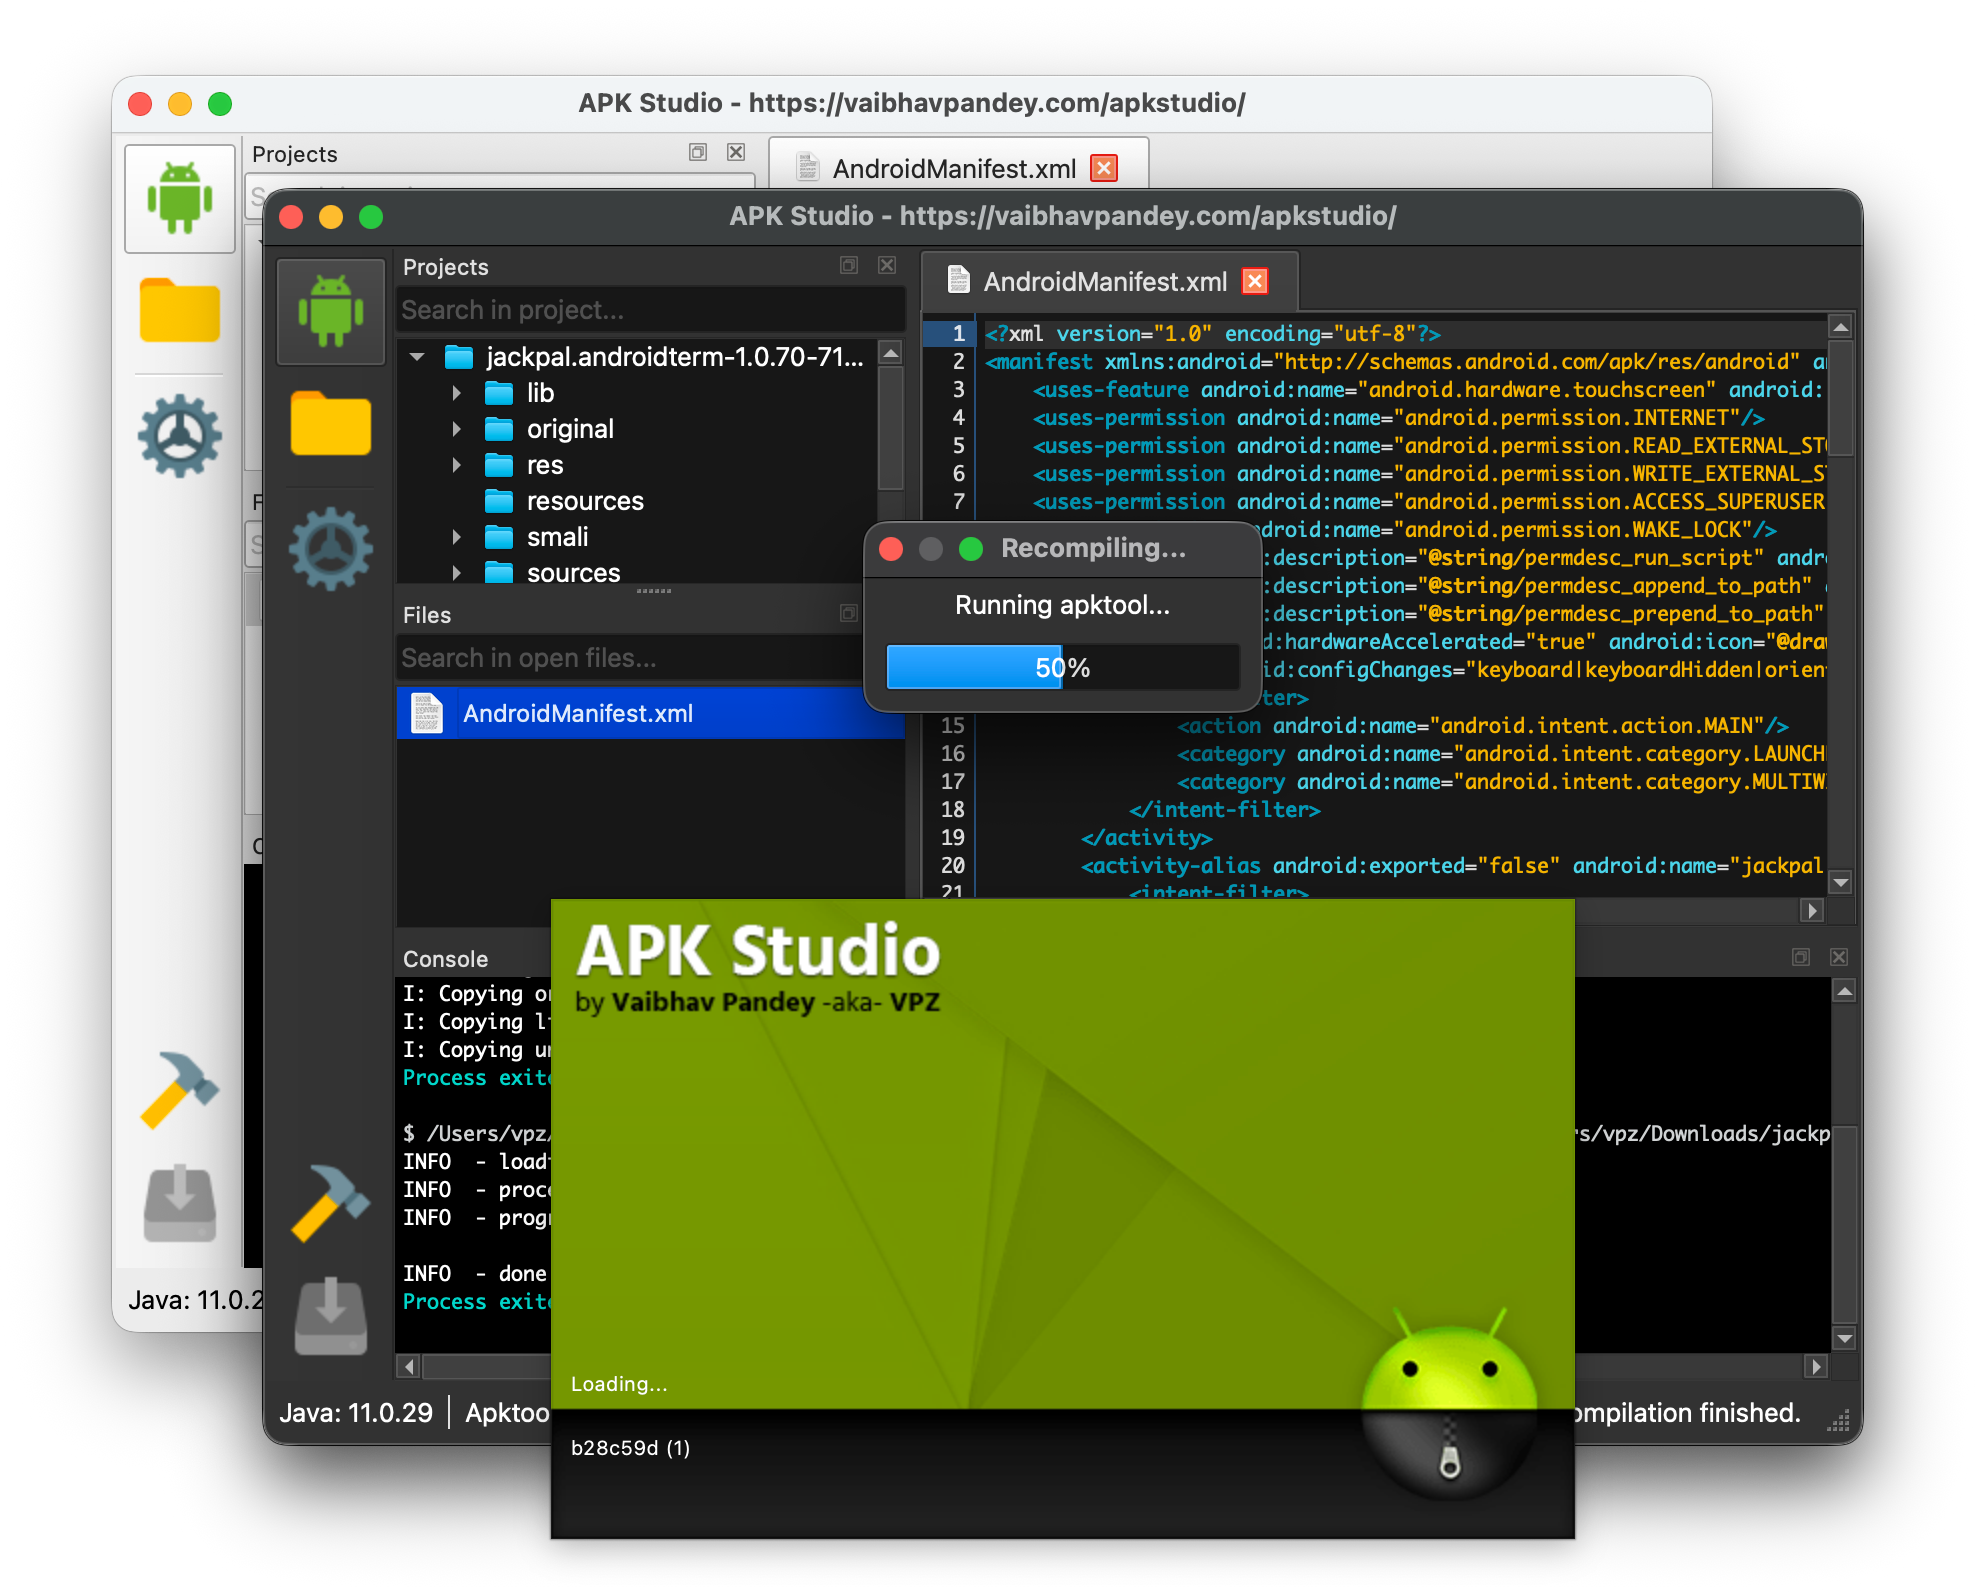 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
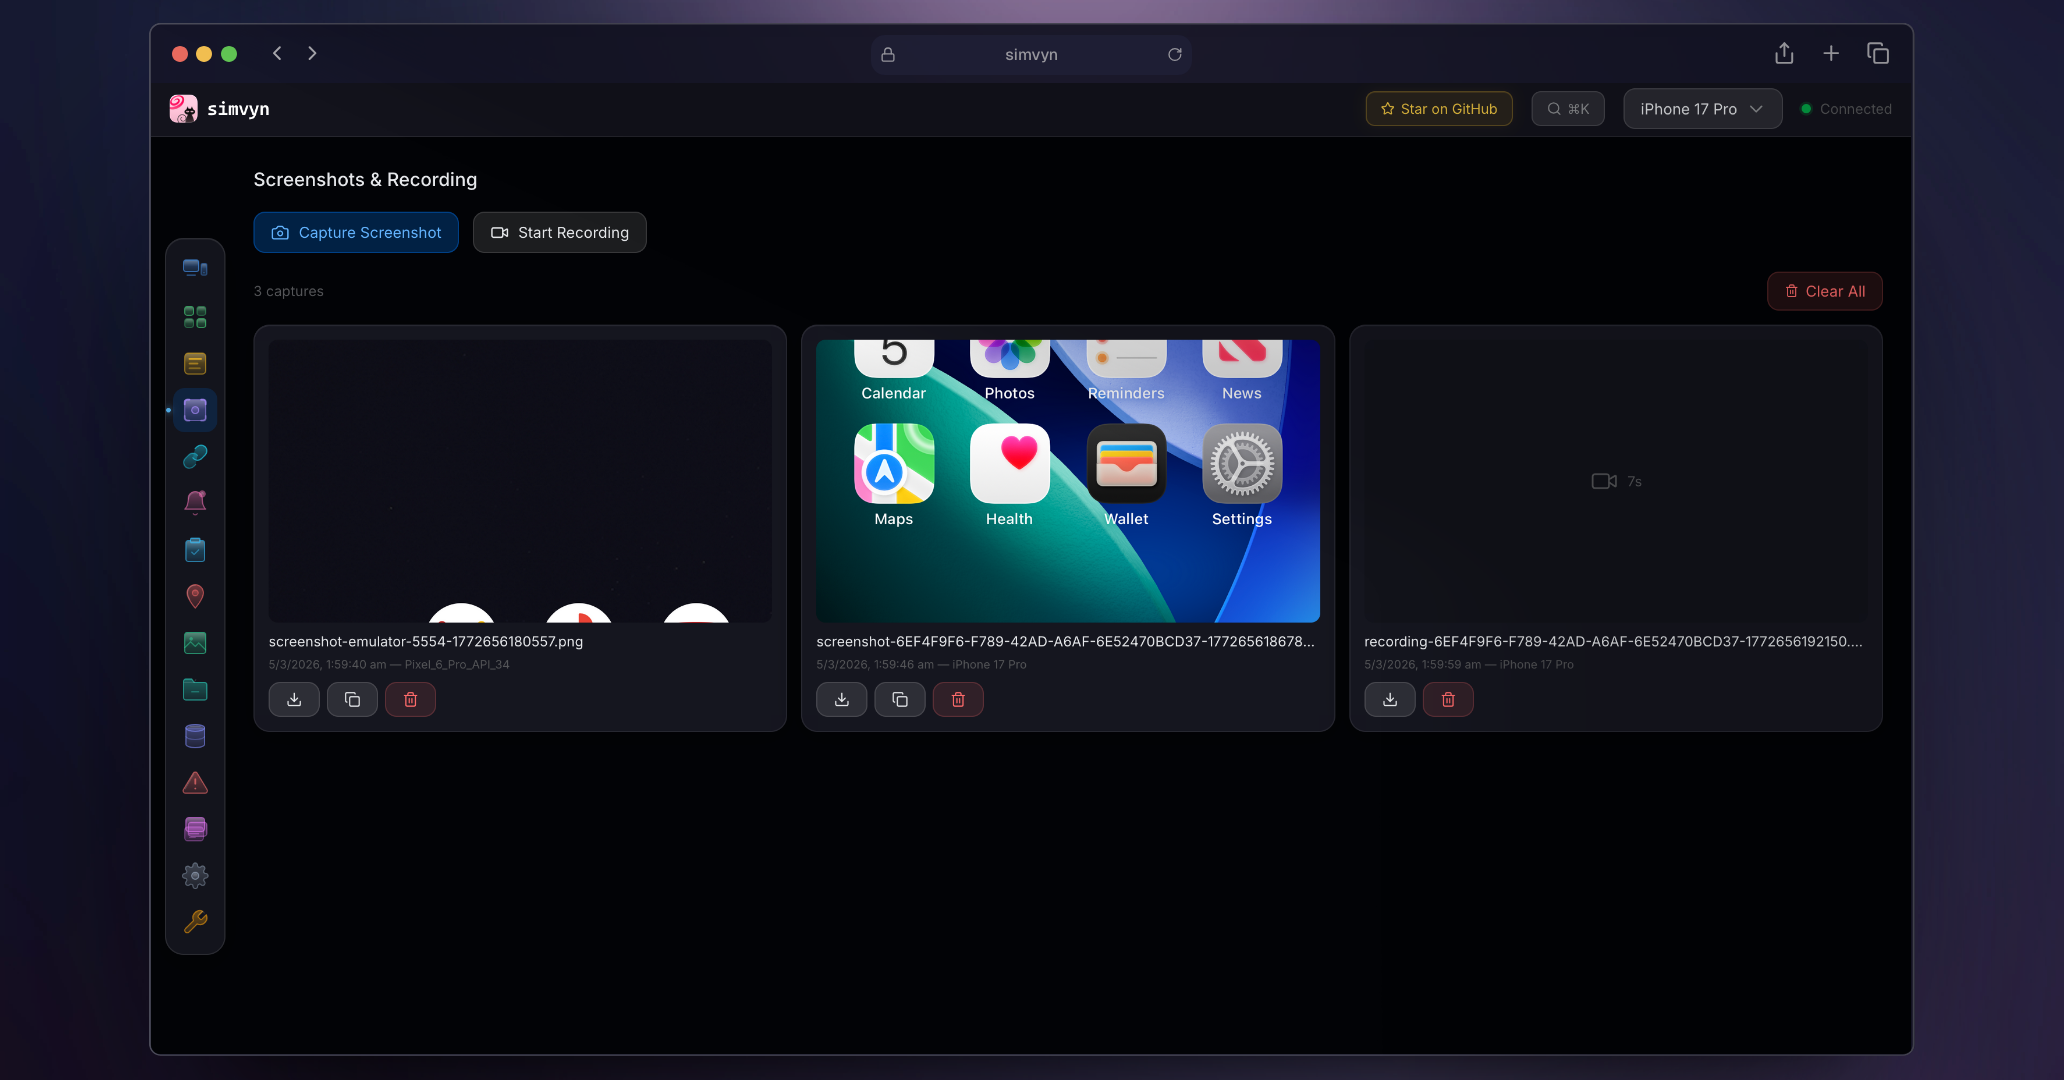 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
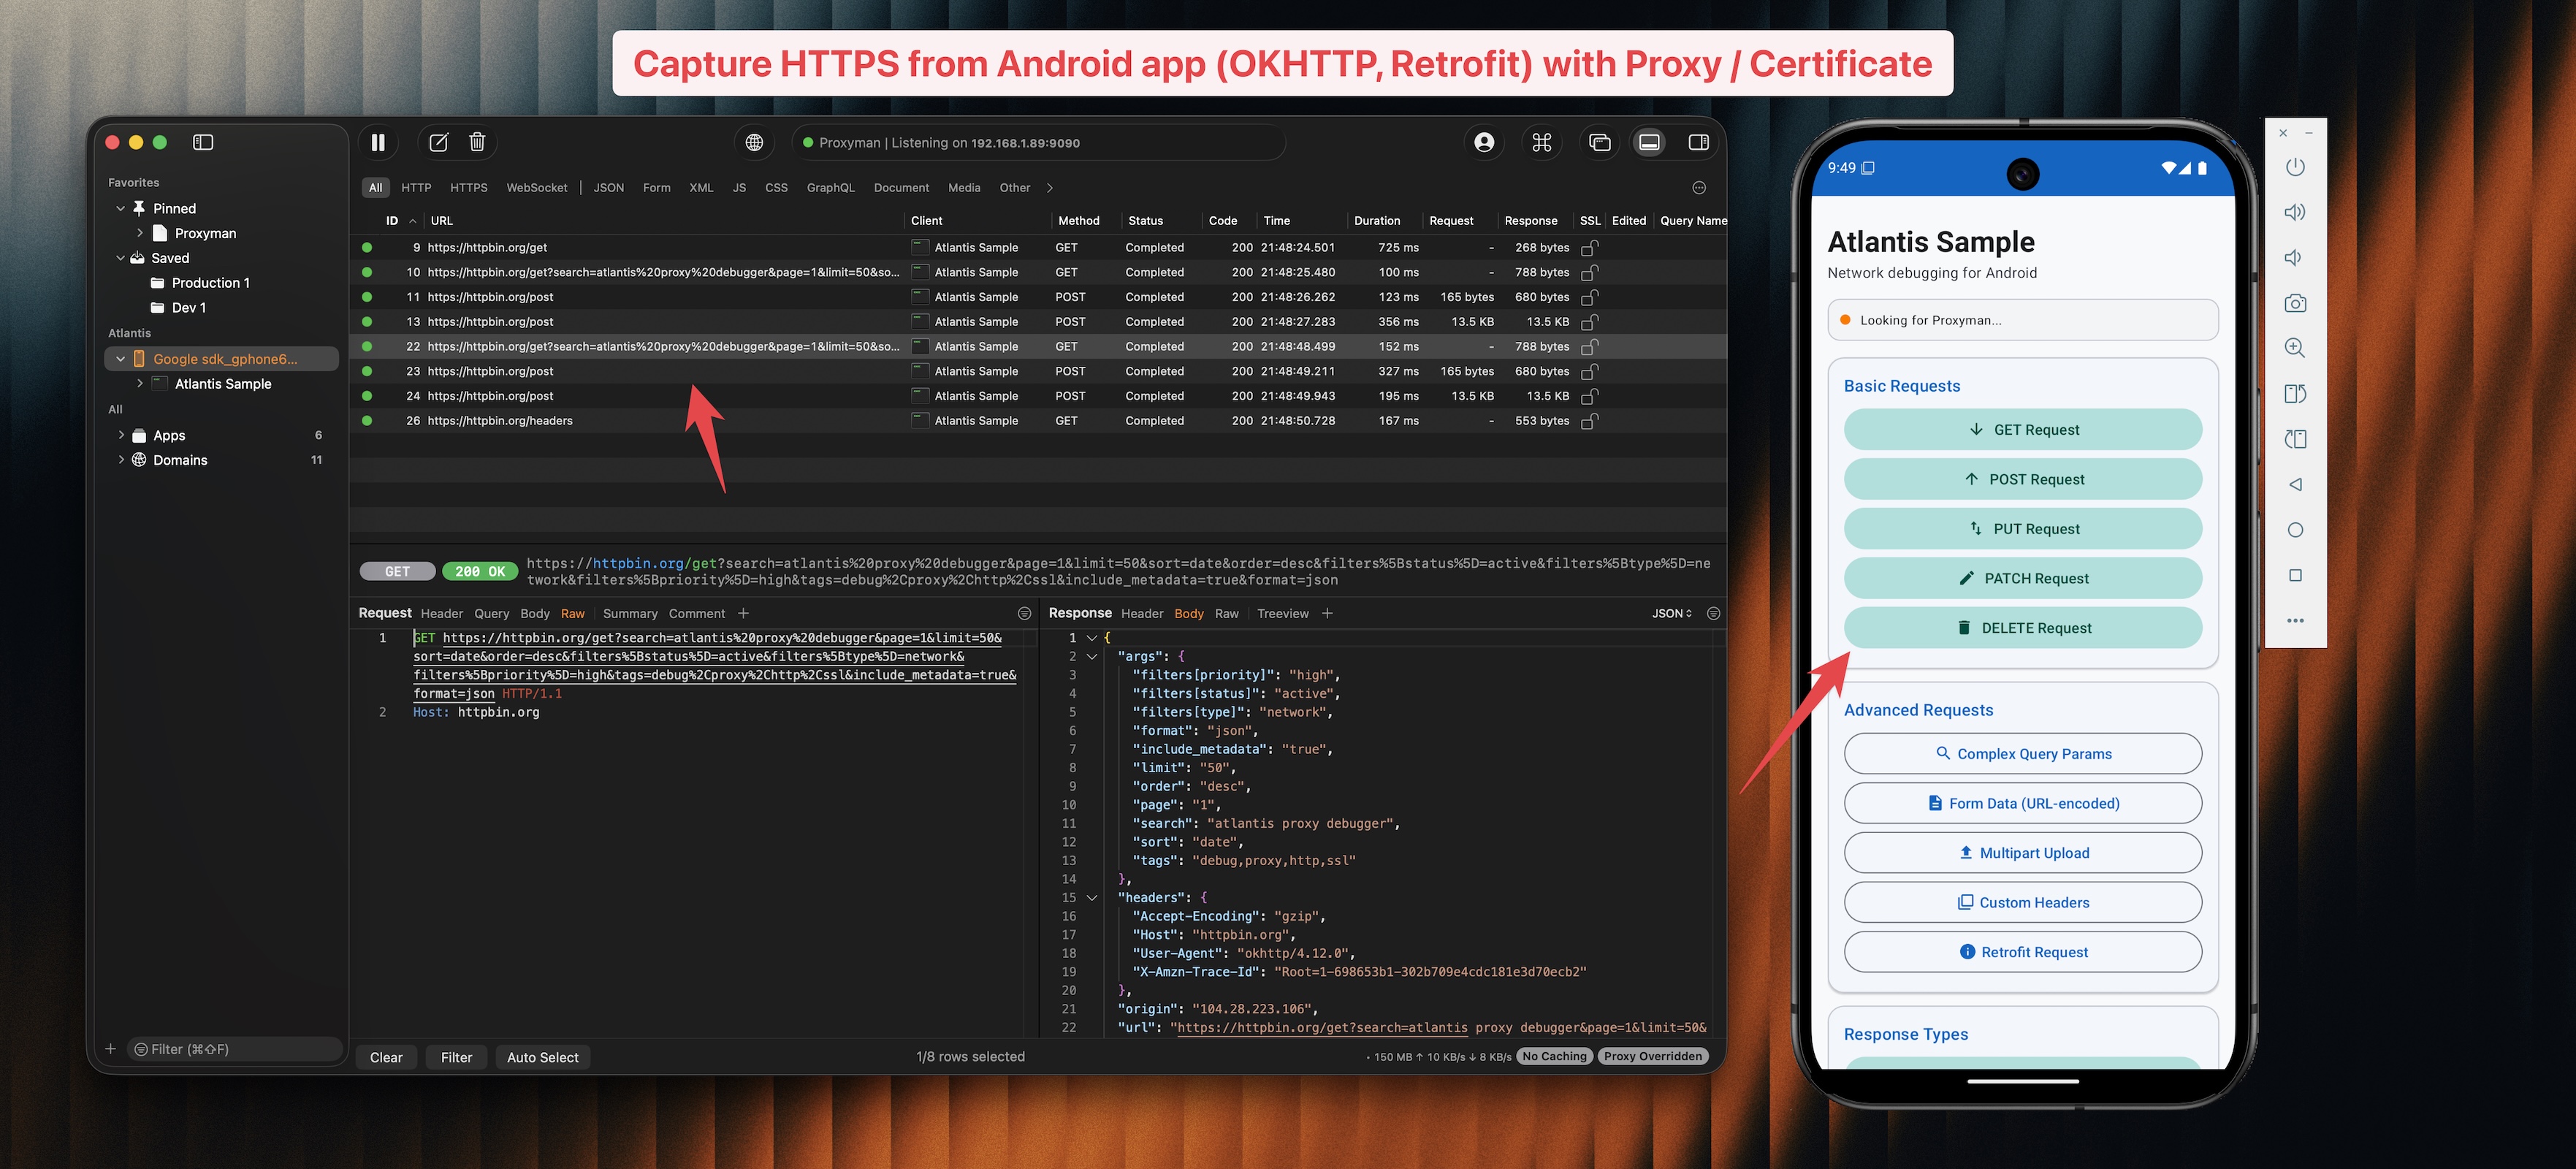 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 ilgobbo00/cve-2023-6241-pixel7_adaptation
Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…