
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
166 results
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
1267 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.
binary-analysiscode-analysisdebuggers+4
24510 months ago
drmemory preview

drmemory

GitHubdynamorio/drmemory

Memory Debugger for Windows, Linux, Mac, and Android

debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.7k9 months ago
showstopper preview

showstopper

GitHubcheckpointsw/showstopper

ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…

debuggerseducationmalware-analysis+1
2245 months ago
BlobRunner preview

BlobRunner

GitHuboalabs/blobrunner

Quickly debug shellcode extracted during malware analysis
debuggersmalware-analysisreverse-engineering+1
6414 years ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
1133 years ago
fhex preview

fhex

GitHubecho-devim/fhex

A Full-Featured HexEditor compatible with Linux/Windows/MacOS

binary-analysisdebuggersforensics+2
4371 year ago
jadx preview

jadx

GitHubskylot/jadx

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

android-securitybinary-analysisdebuggers+5
50.5k4 days ago
COM-Code-Helper preview

COM-Code-Helper

GitHubfboldewin/com-code-helper

Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
binary-analysisdebuggersmalware-analysis+1
1865 years ago
BugChecker preview

BugChecker

GitHubvitoplantamura/bugchecker

SoftICE-like kernel debugger for Windows 11
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1.1k3 years ago
AntiKernelDebug-POC preview

AntiKernelDebug-POC

GitHubgmh5225/antikerneldebug-poc

POC about how to detect windows kernel debug by pool tag.
debuggersdefensive-toolsmalware-analysis
123 years ago
cve-2026-62737-lab preview

cve-2026-62737-lab

GitHubdavidcarliez/cve-2026-62737-lab

Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…
binary-exploitationdebuggersexploitation+2
21 month ago
gftrace preview

gftrace

GitHubleandrofroes/gftrace

A command line Windows API tracing tool for Golang binaries.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1592 years ago
psr preview

psr

GitHubnccgroup/psr

Pointer Sequence Reverser - enable you to see how Windows C++ application is accessing a particular data member or object.

binary-analysisdebuggersdynamic-analysis-sandboxing+1
768 years ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
203 months ago
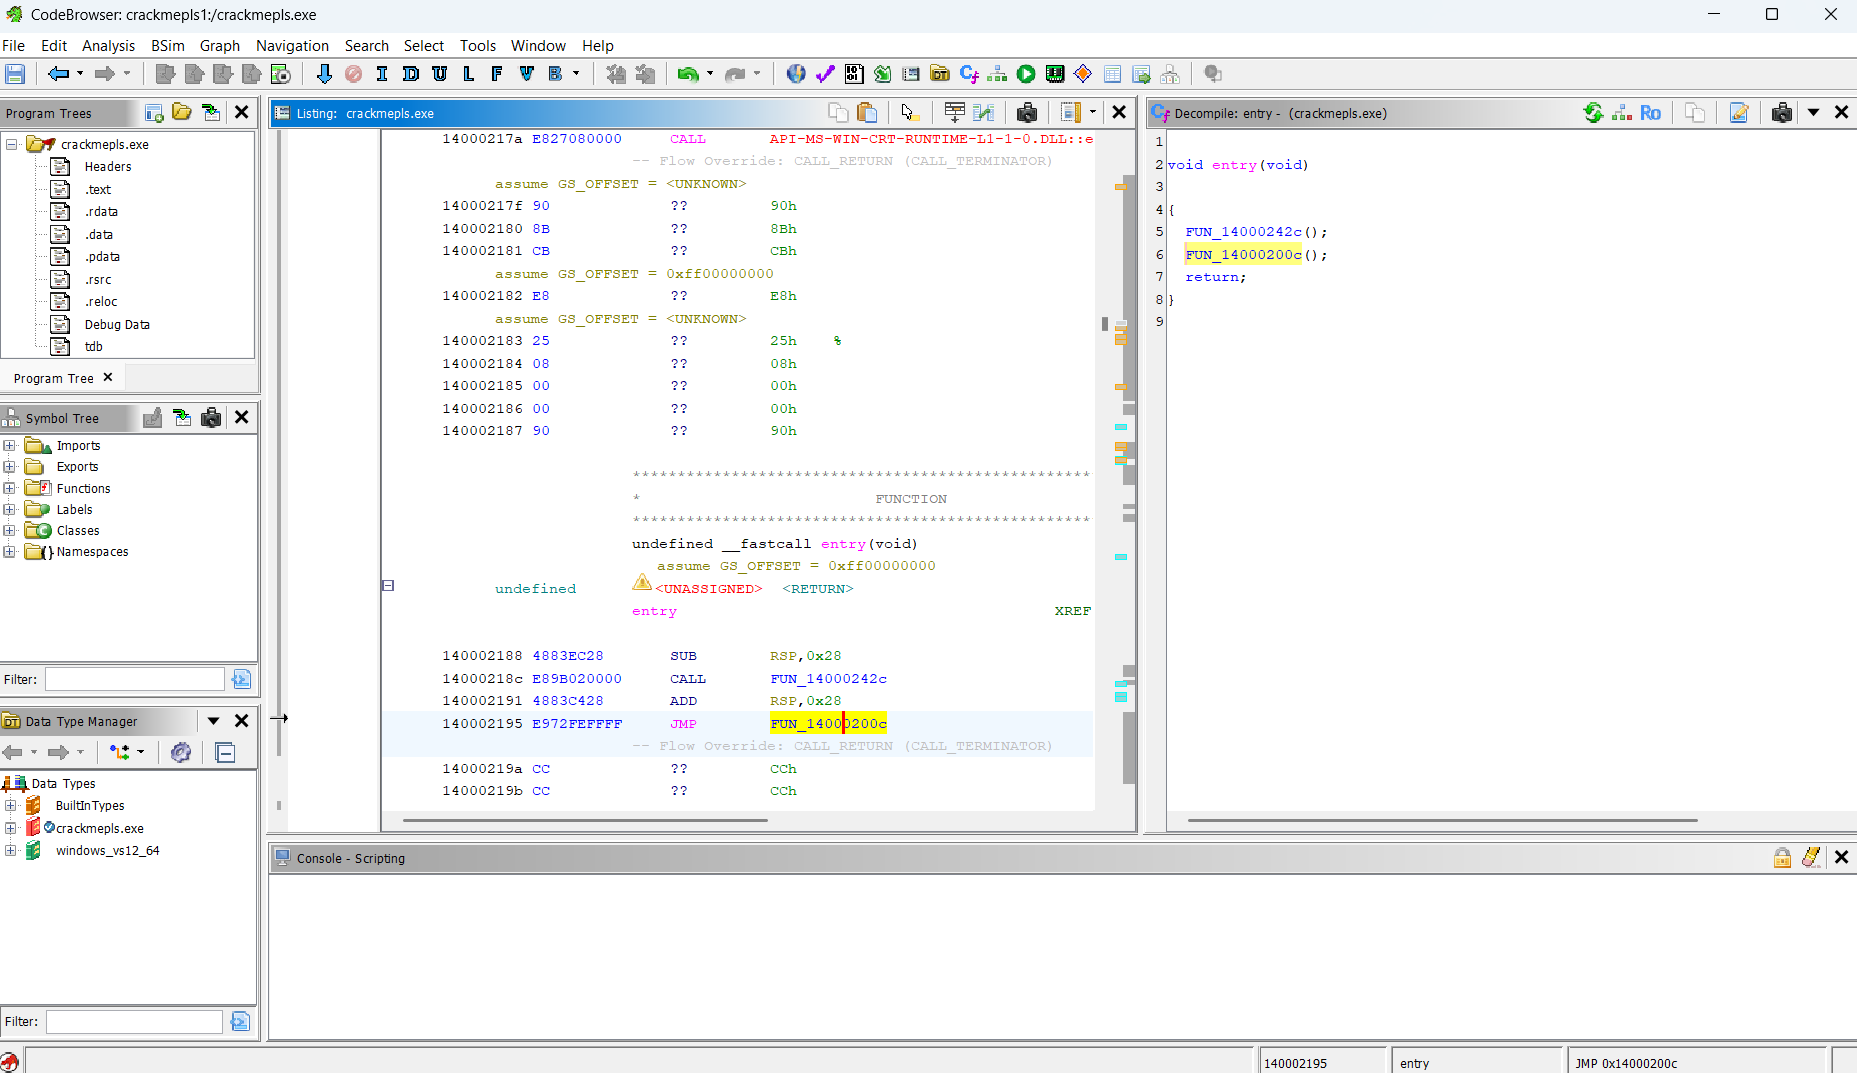
gemma_crackme_tutorial preview

gemma_crackme_tutorial

GitHubmarkoglasgow/gemma_crackme_tutorial

Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
ai-assisted-reversingbinary-analysisdebuggers+3
354 months ago
VAXD preview

VAXD

GitHubbicurico/vaxd

Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.

binary-analysisdebuggersdigital-forensics+7
172 months ago
Previous12…10Next