
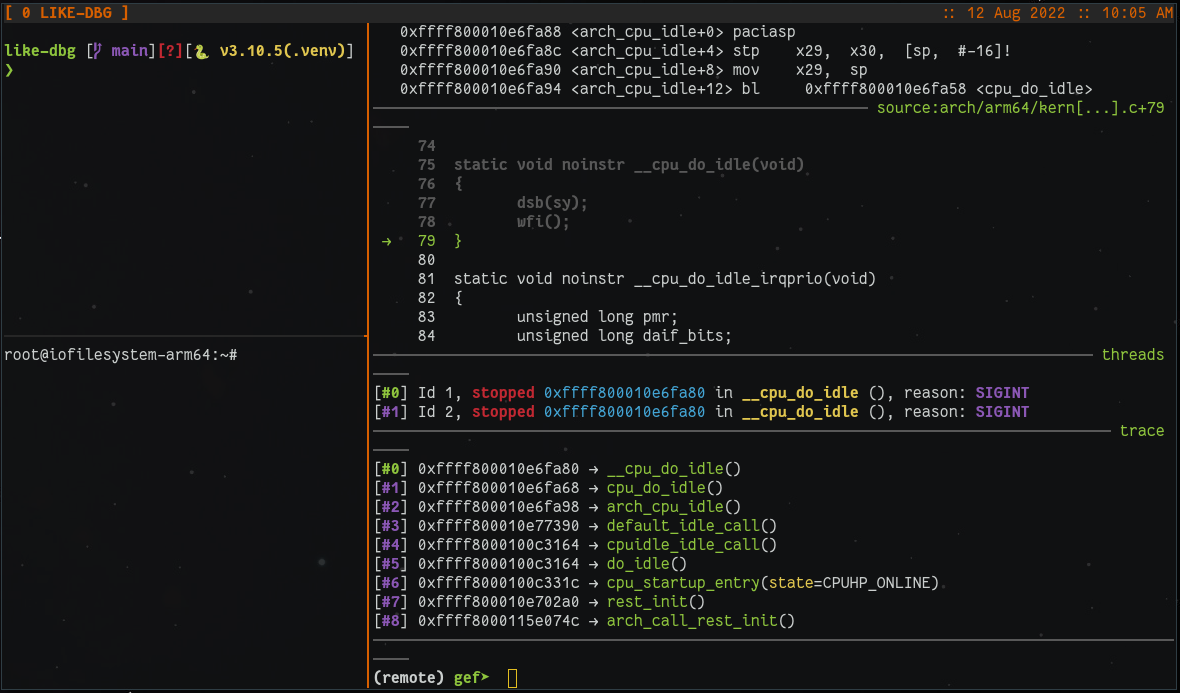
like-dbg
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
binary-exploitationctfdebuggers+2
0xricksanchez/like-dbgFully dockerized Linux kernel debugging environment for Linux and MacOS
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
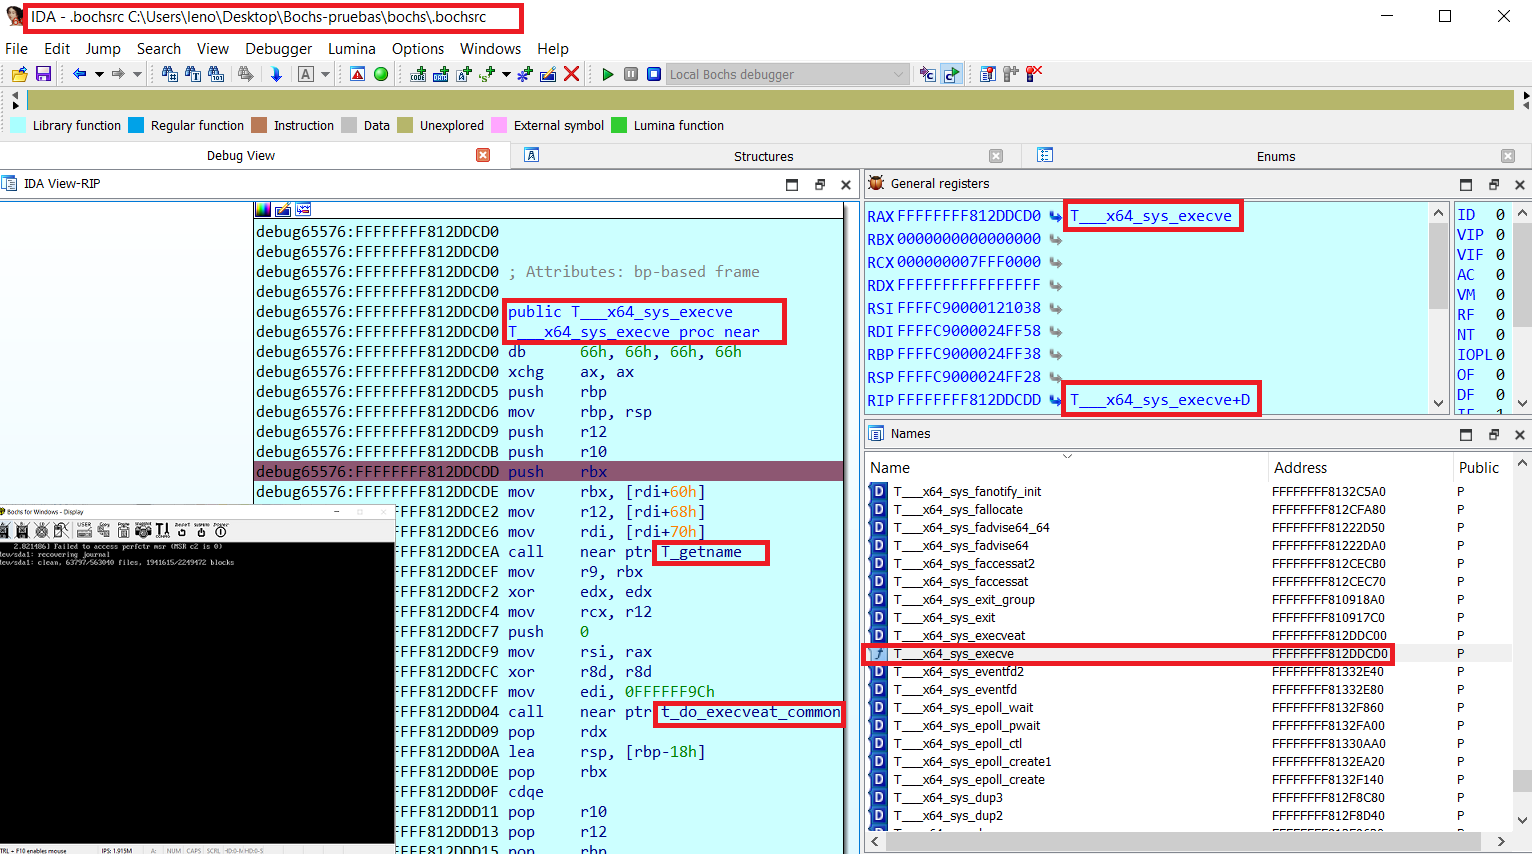 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 gmh5225/linux-kernel-debugger
Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.
 dsfau/cve-2018-1000199
Proof-of-concept exploit for Linux kernel ptrace debug register corruption (CVE-2018-1000199), demonstrating incorrect error handling in breakpoint…
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
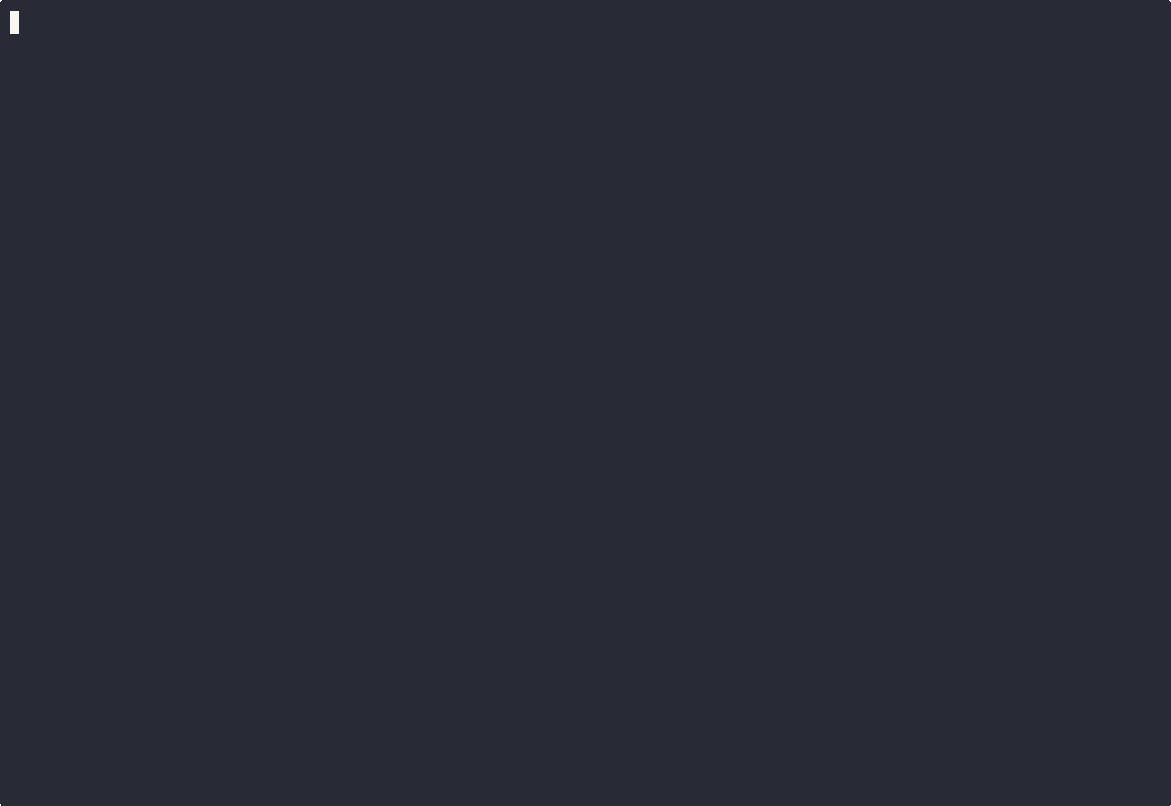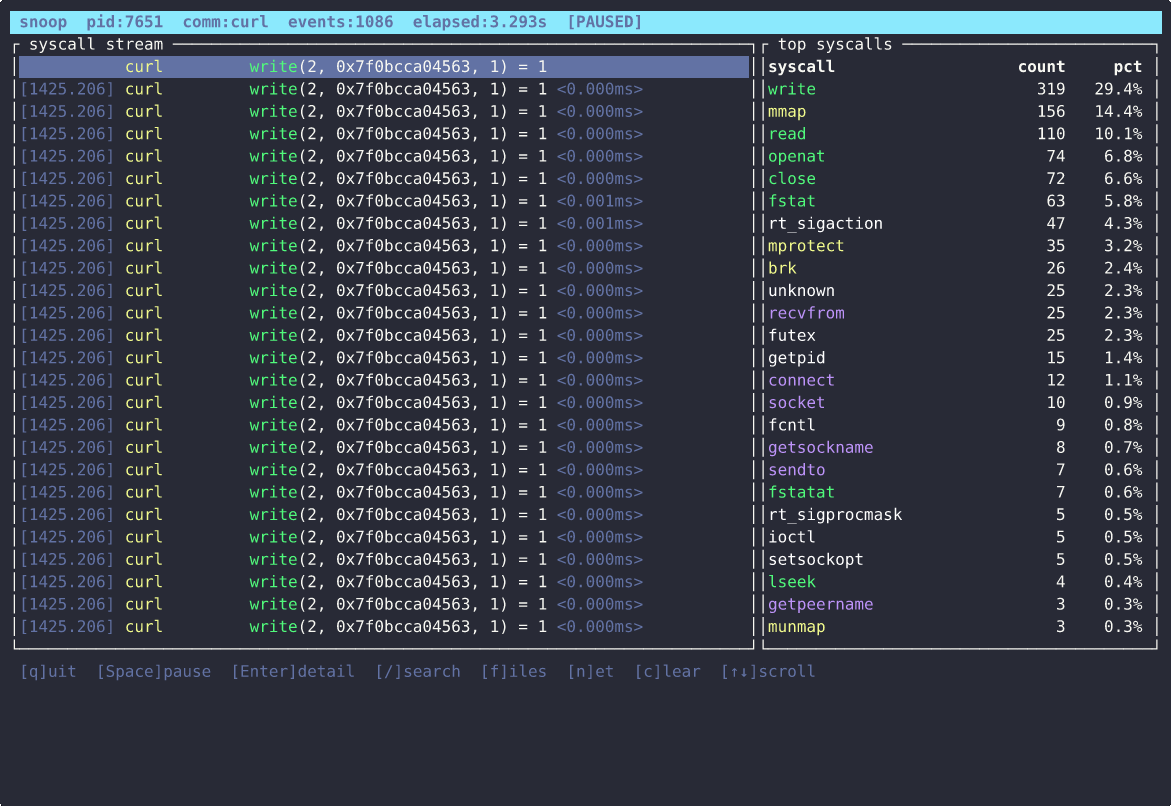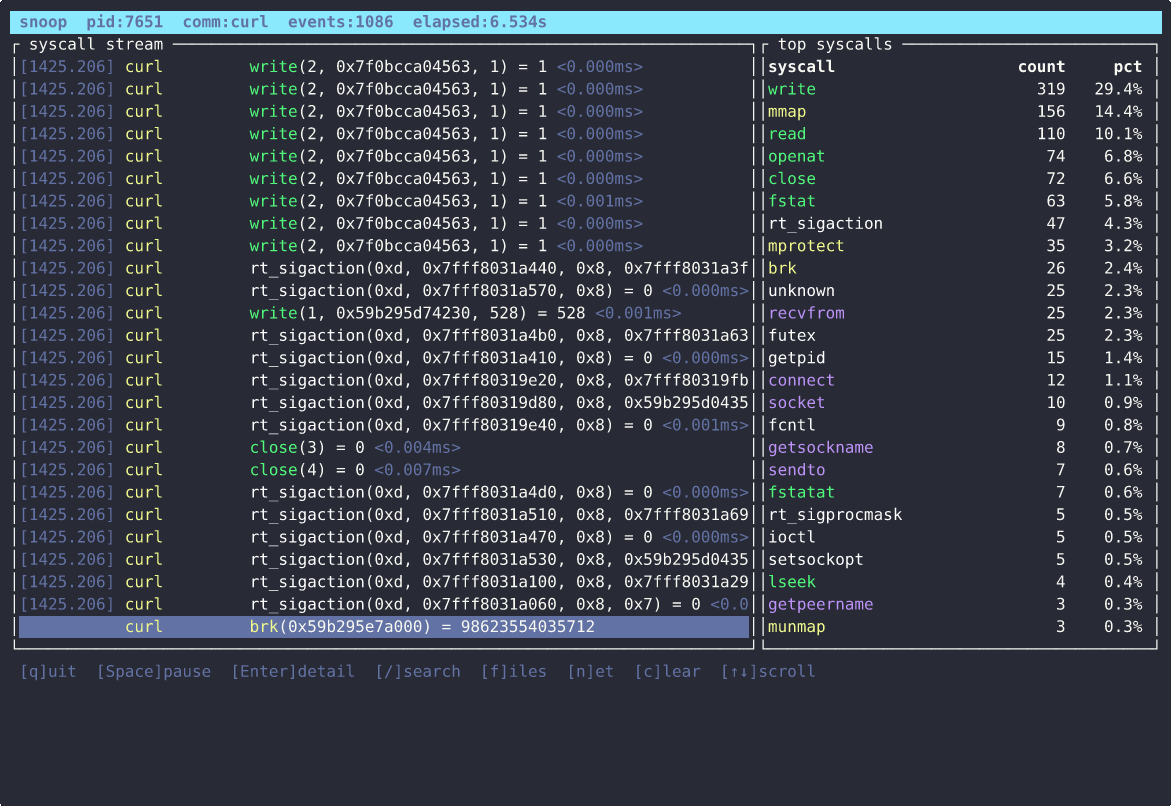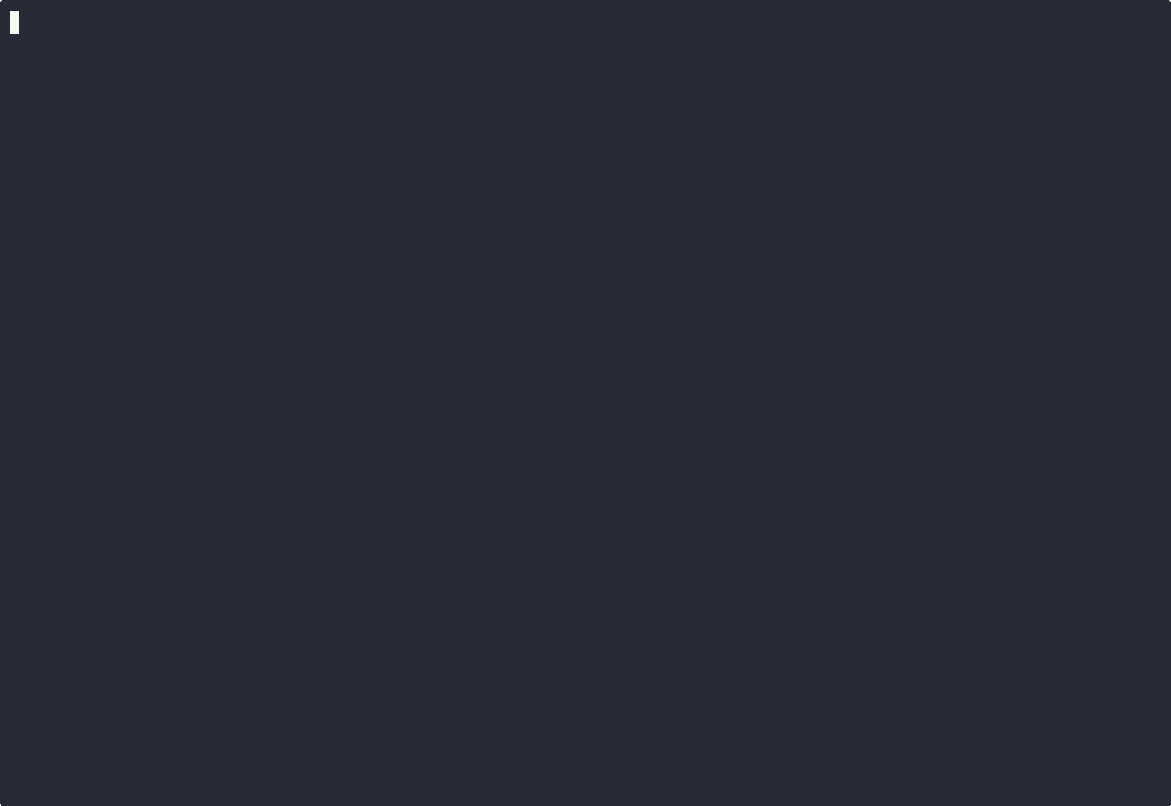 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
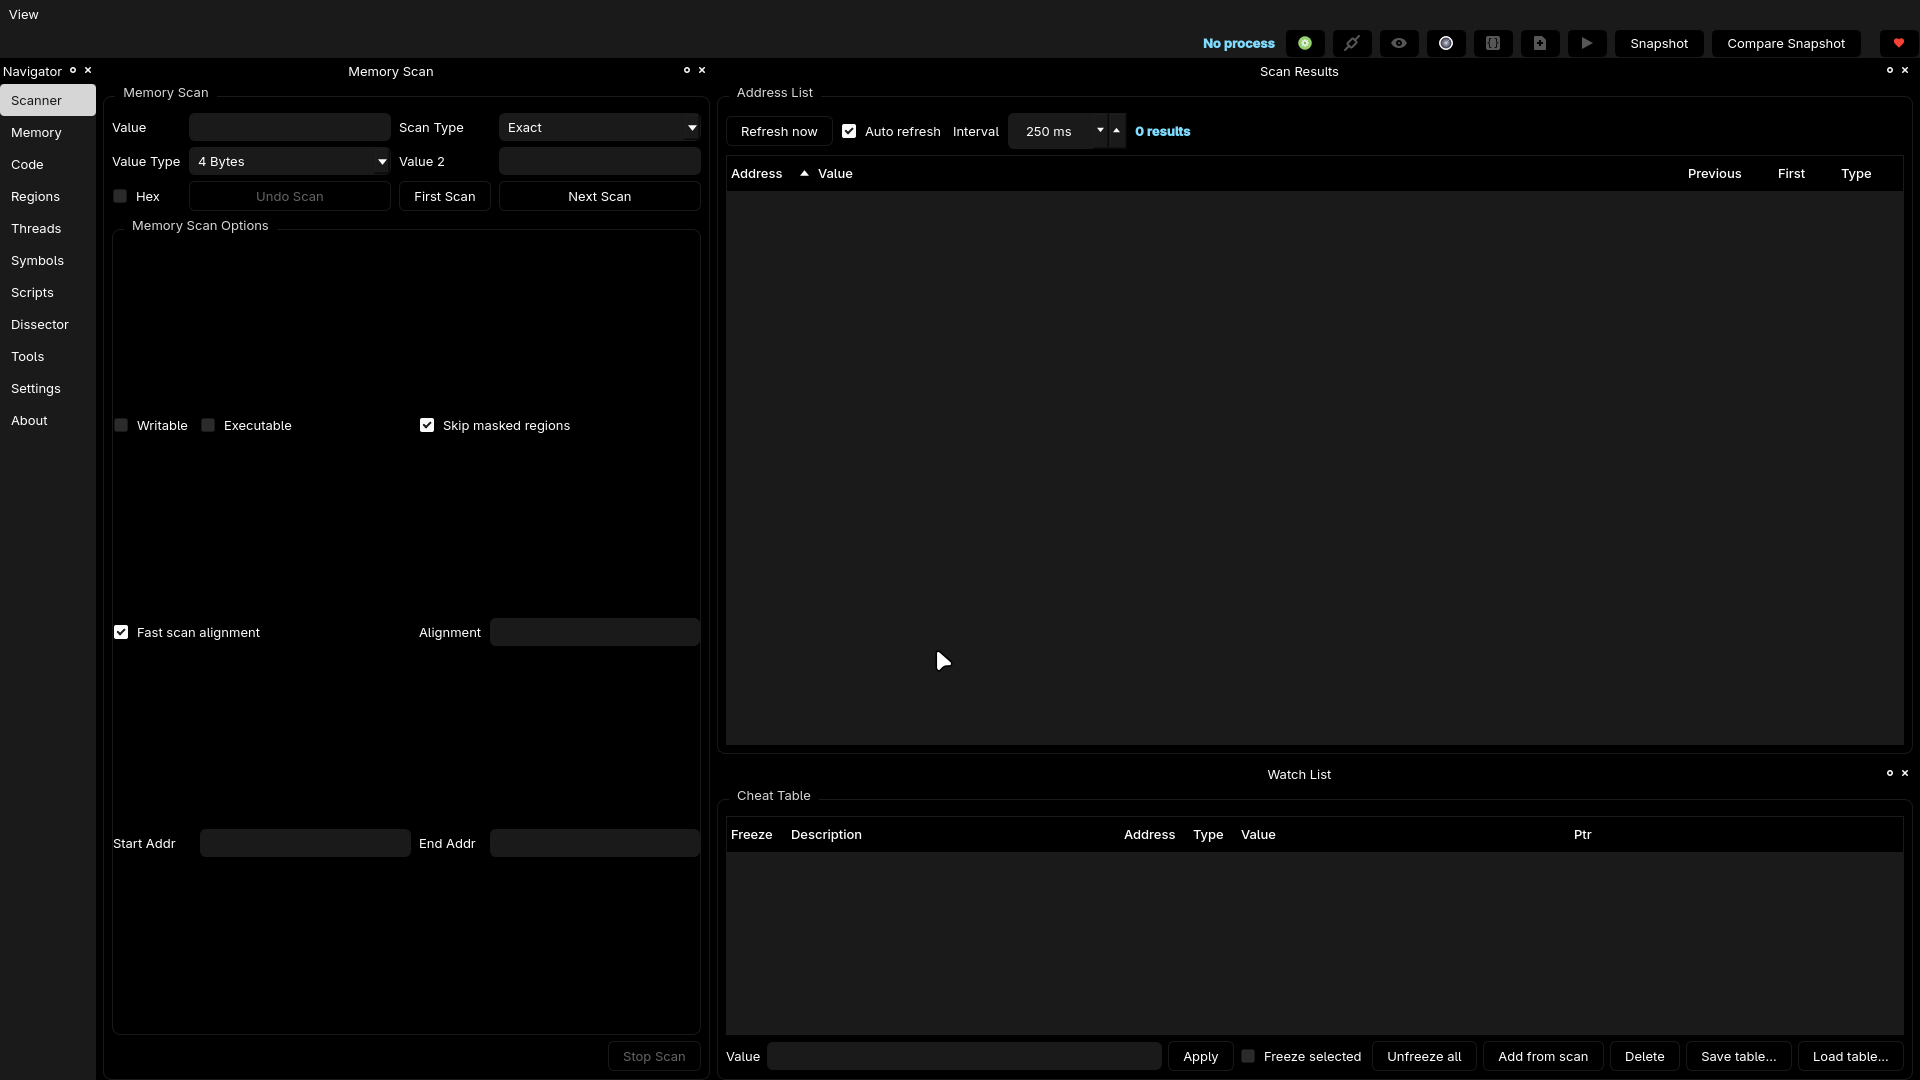 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.

 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 nccgroup/libslub
Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
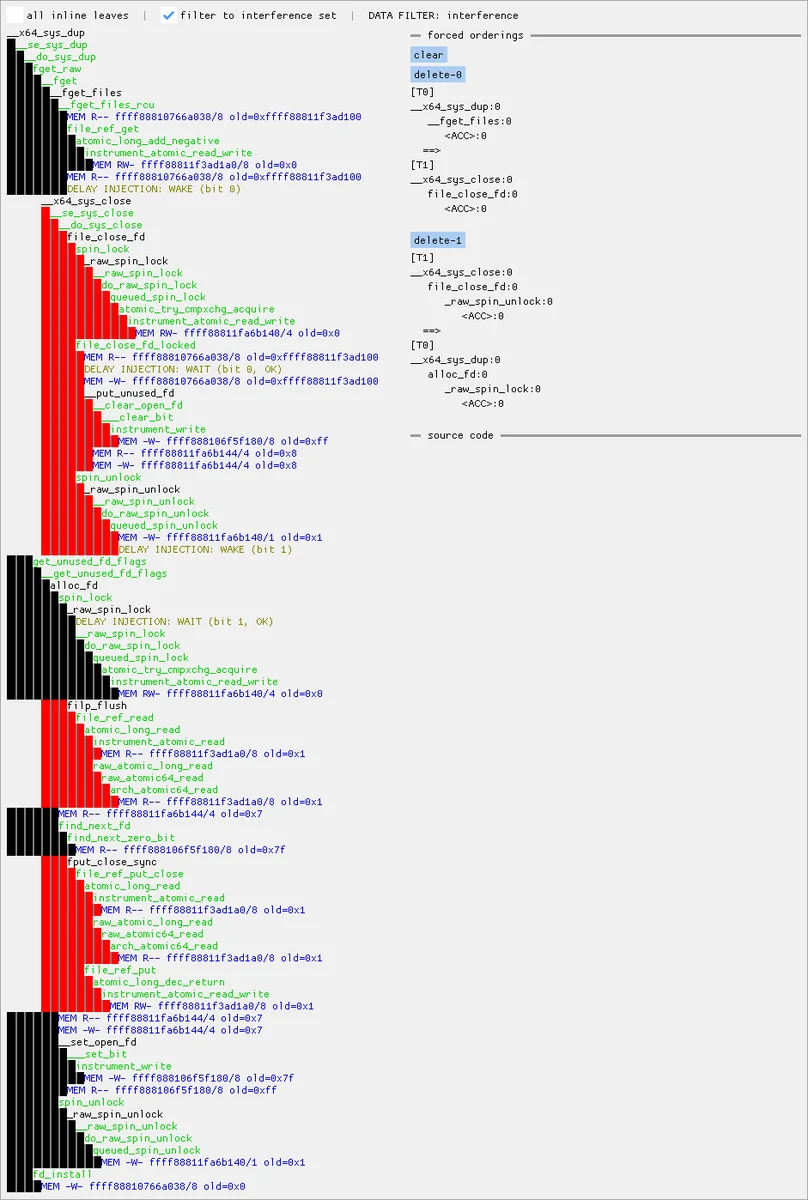 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…