

Malware-analysis-and-Reverse-engineering
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
binary-analysisctfcurated-resources+8
960
dump-guy/malware-analysis-and-reverse-engineeringSome of my publicly available Malware analysis and Reverse engineering.
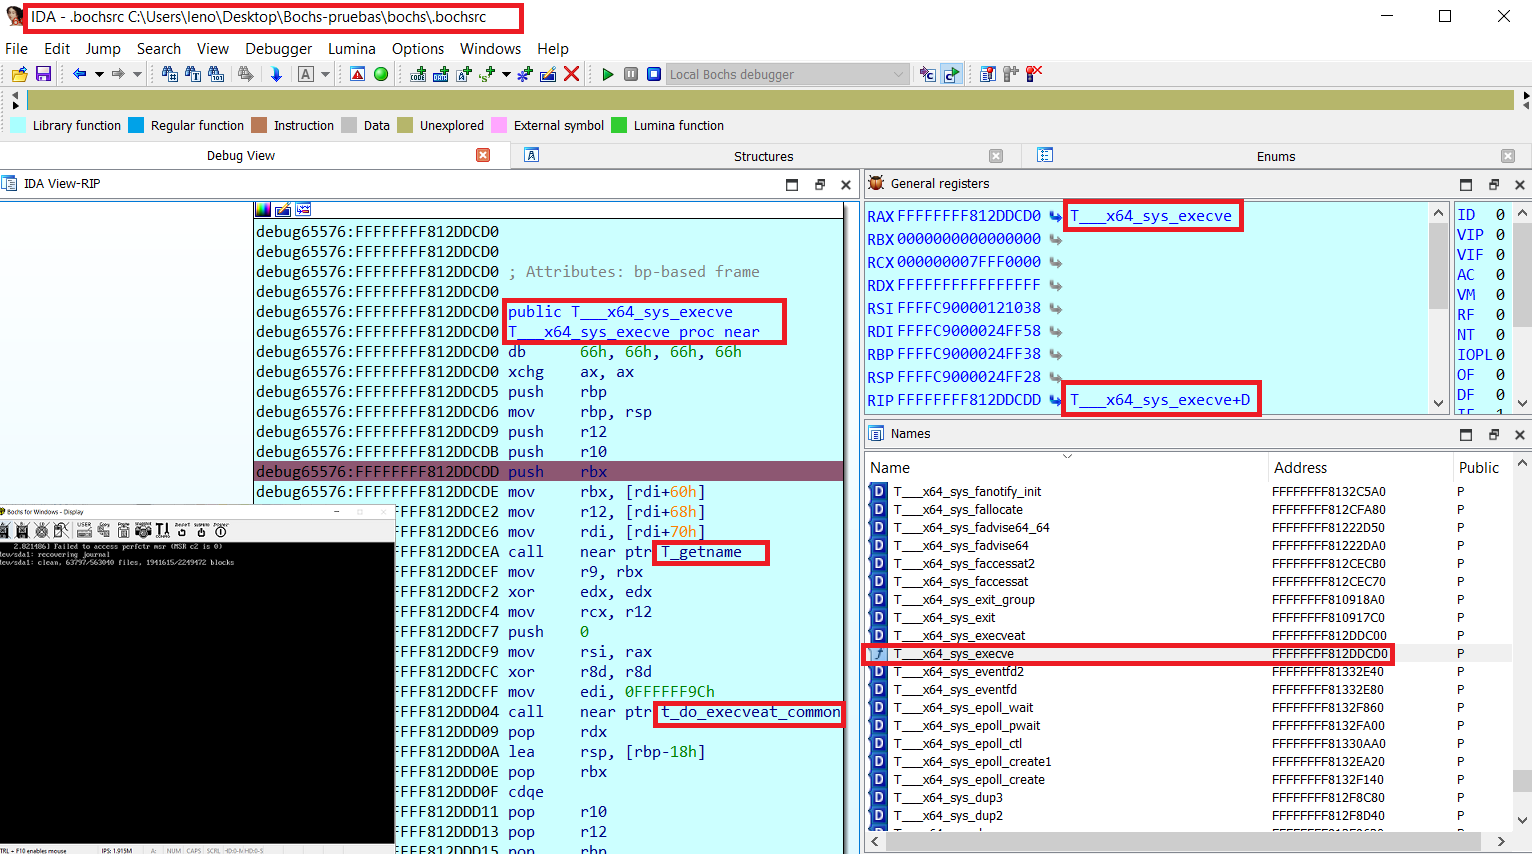 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…