
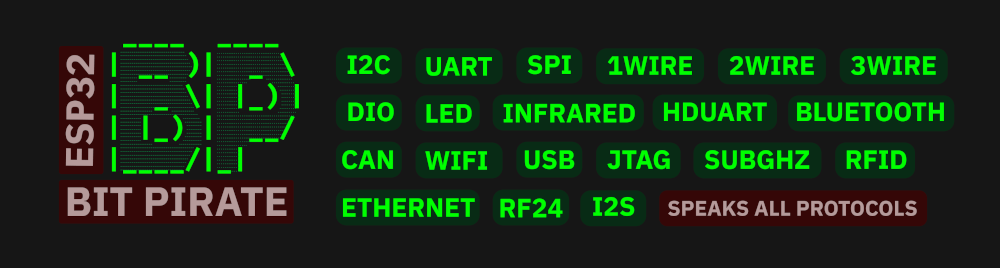
ESP32-Bit-Pirate
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
bluetooth-securitydebuggersembedded-systems-security+5
5.9k
geo-tp/esp32-bit-pirateA Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
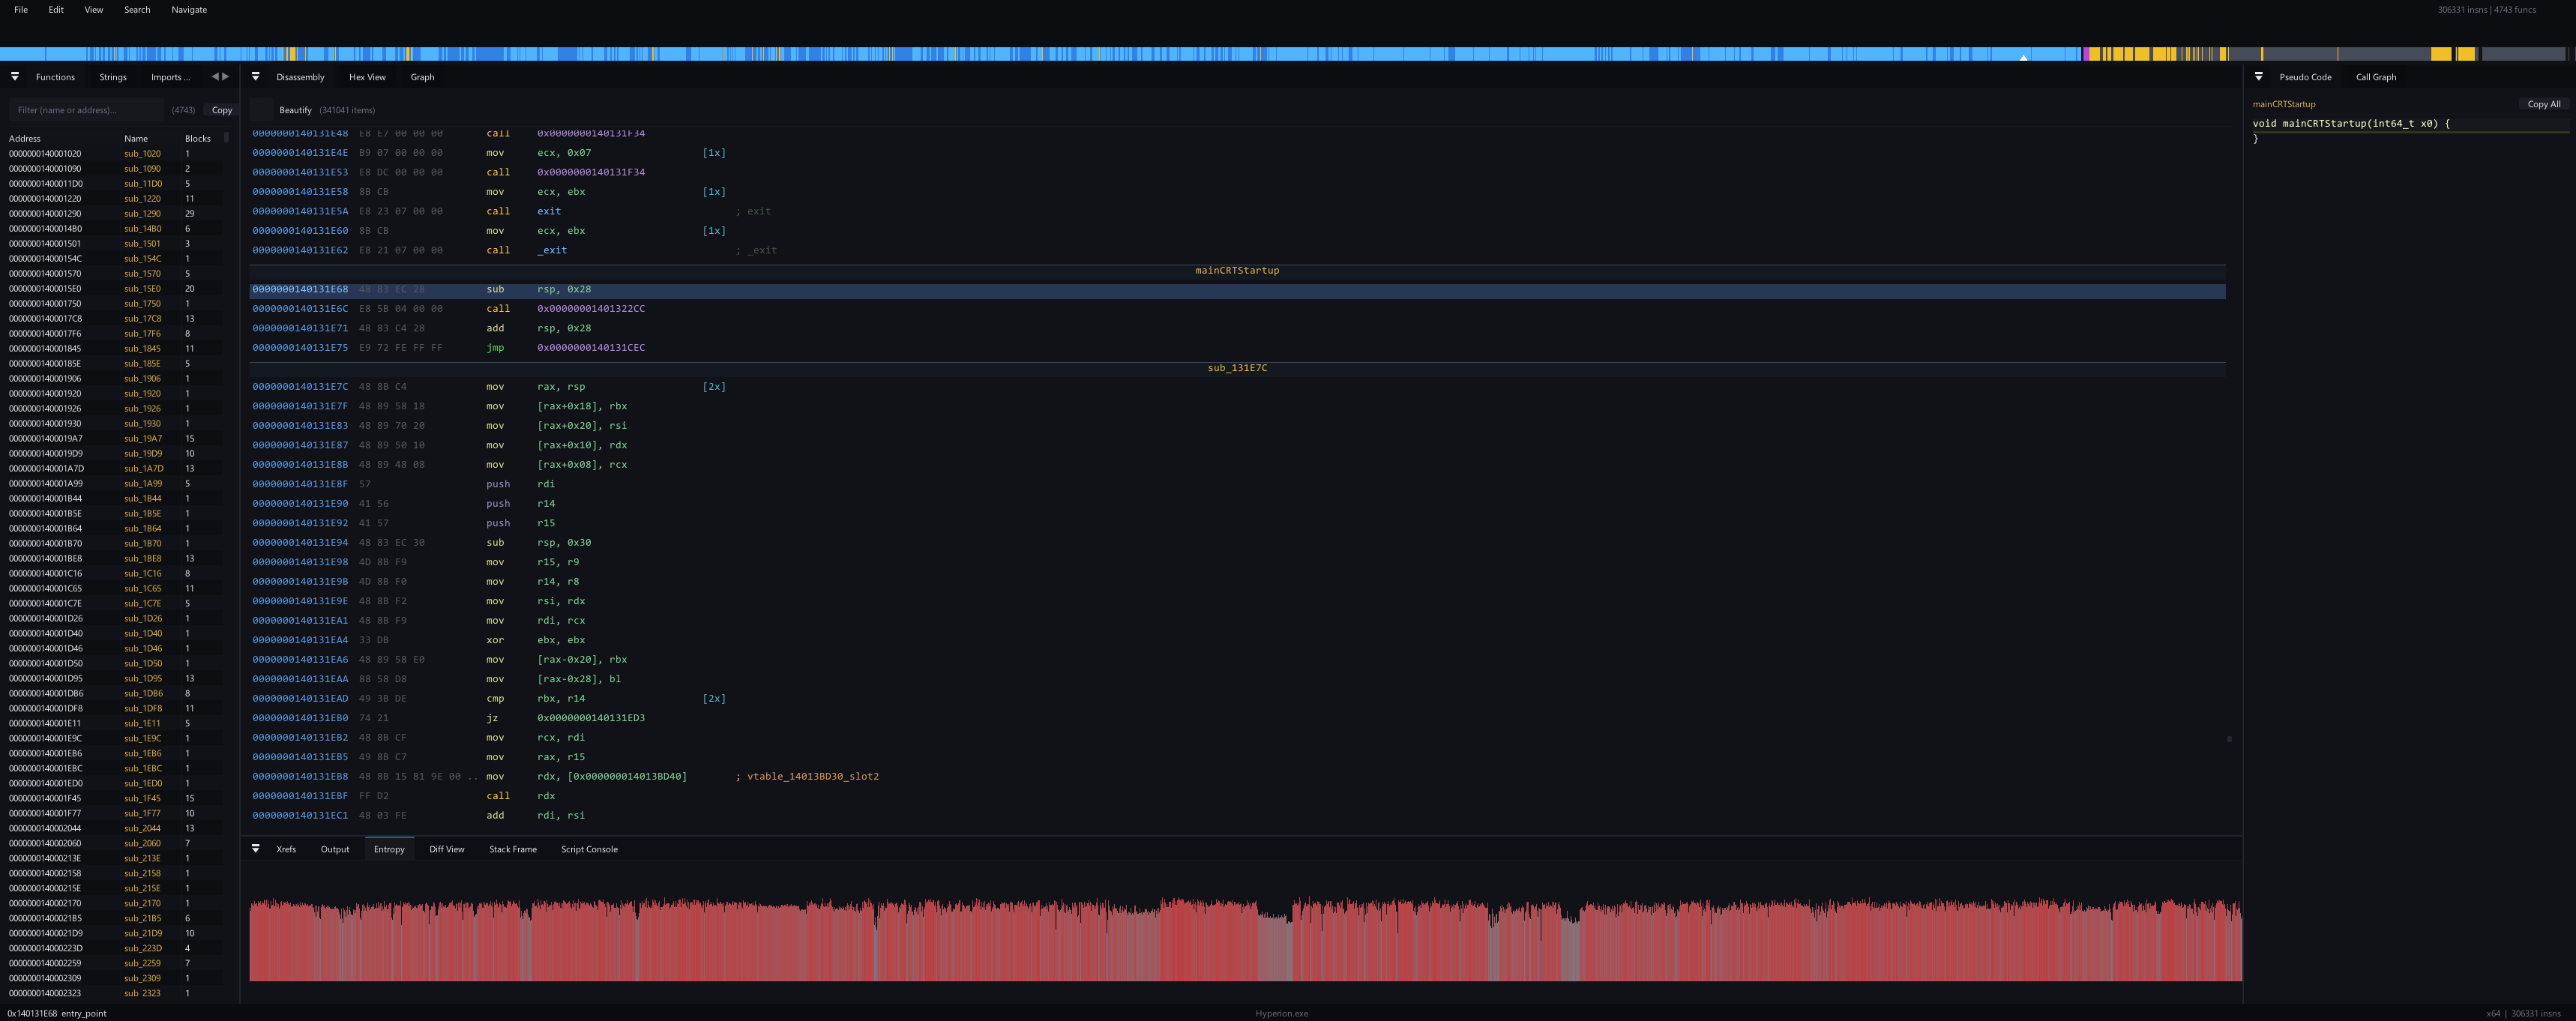 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
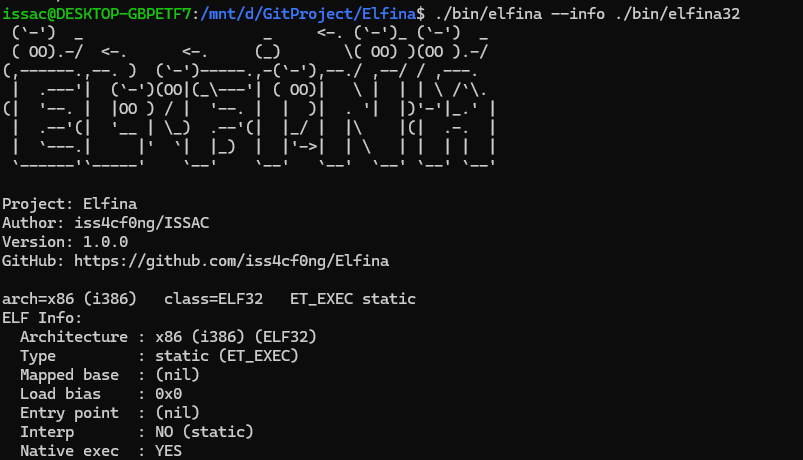 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)