

SwishDbgExt
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
debuggersdigital-forensicsincident-response+3
3997 years ago
magnetforensics/swishdbgextIncident Response & Digital Forensics Debugging Extension
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
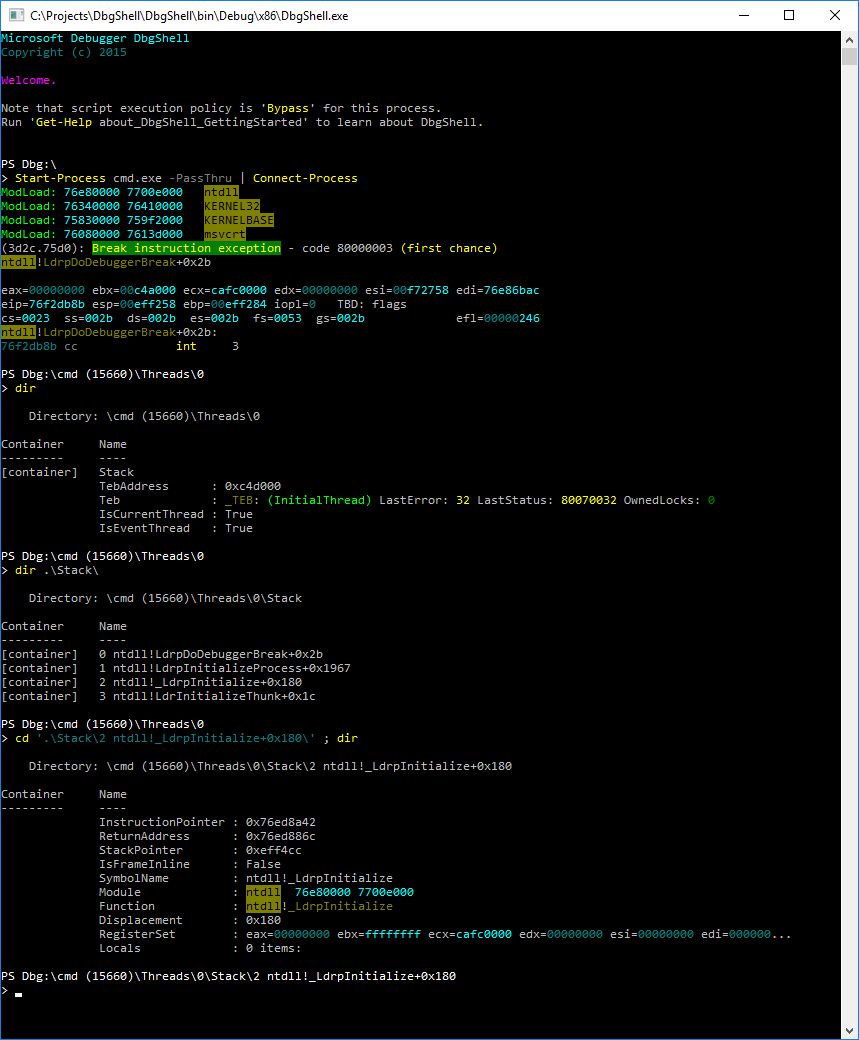 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data