
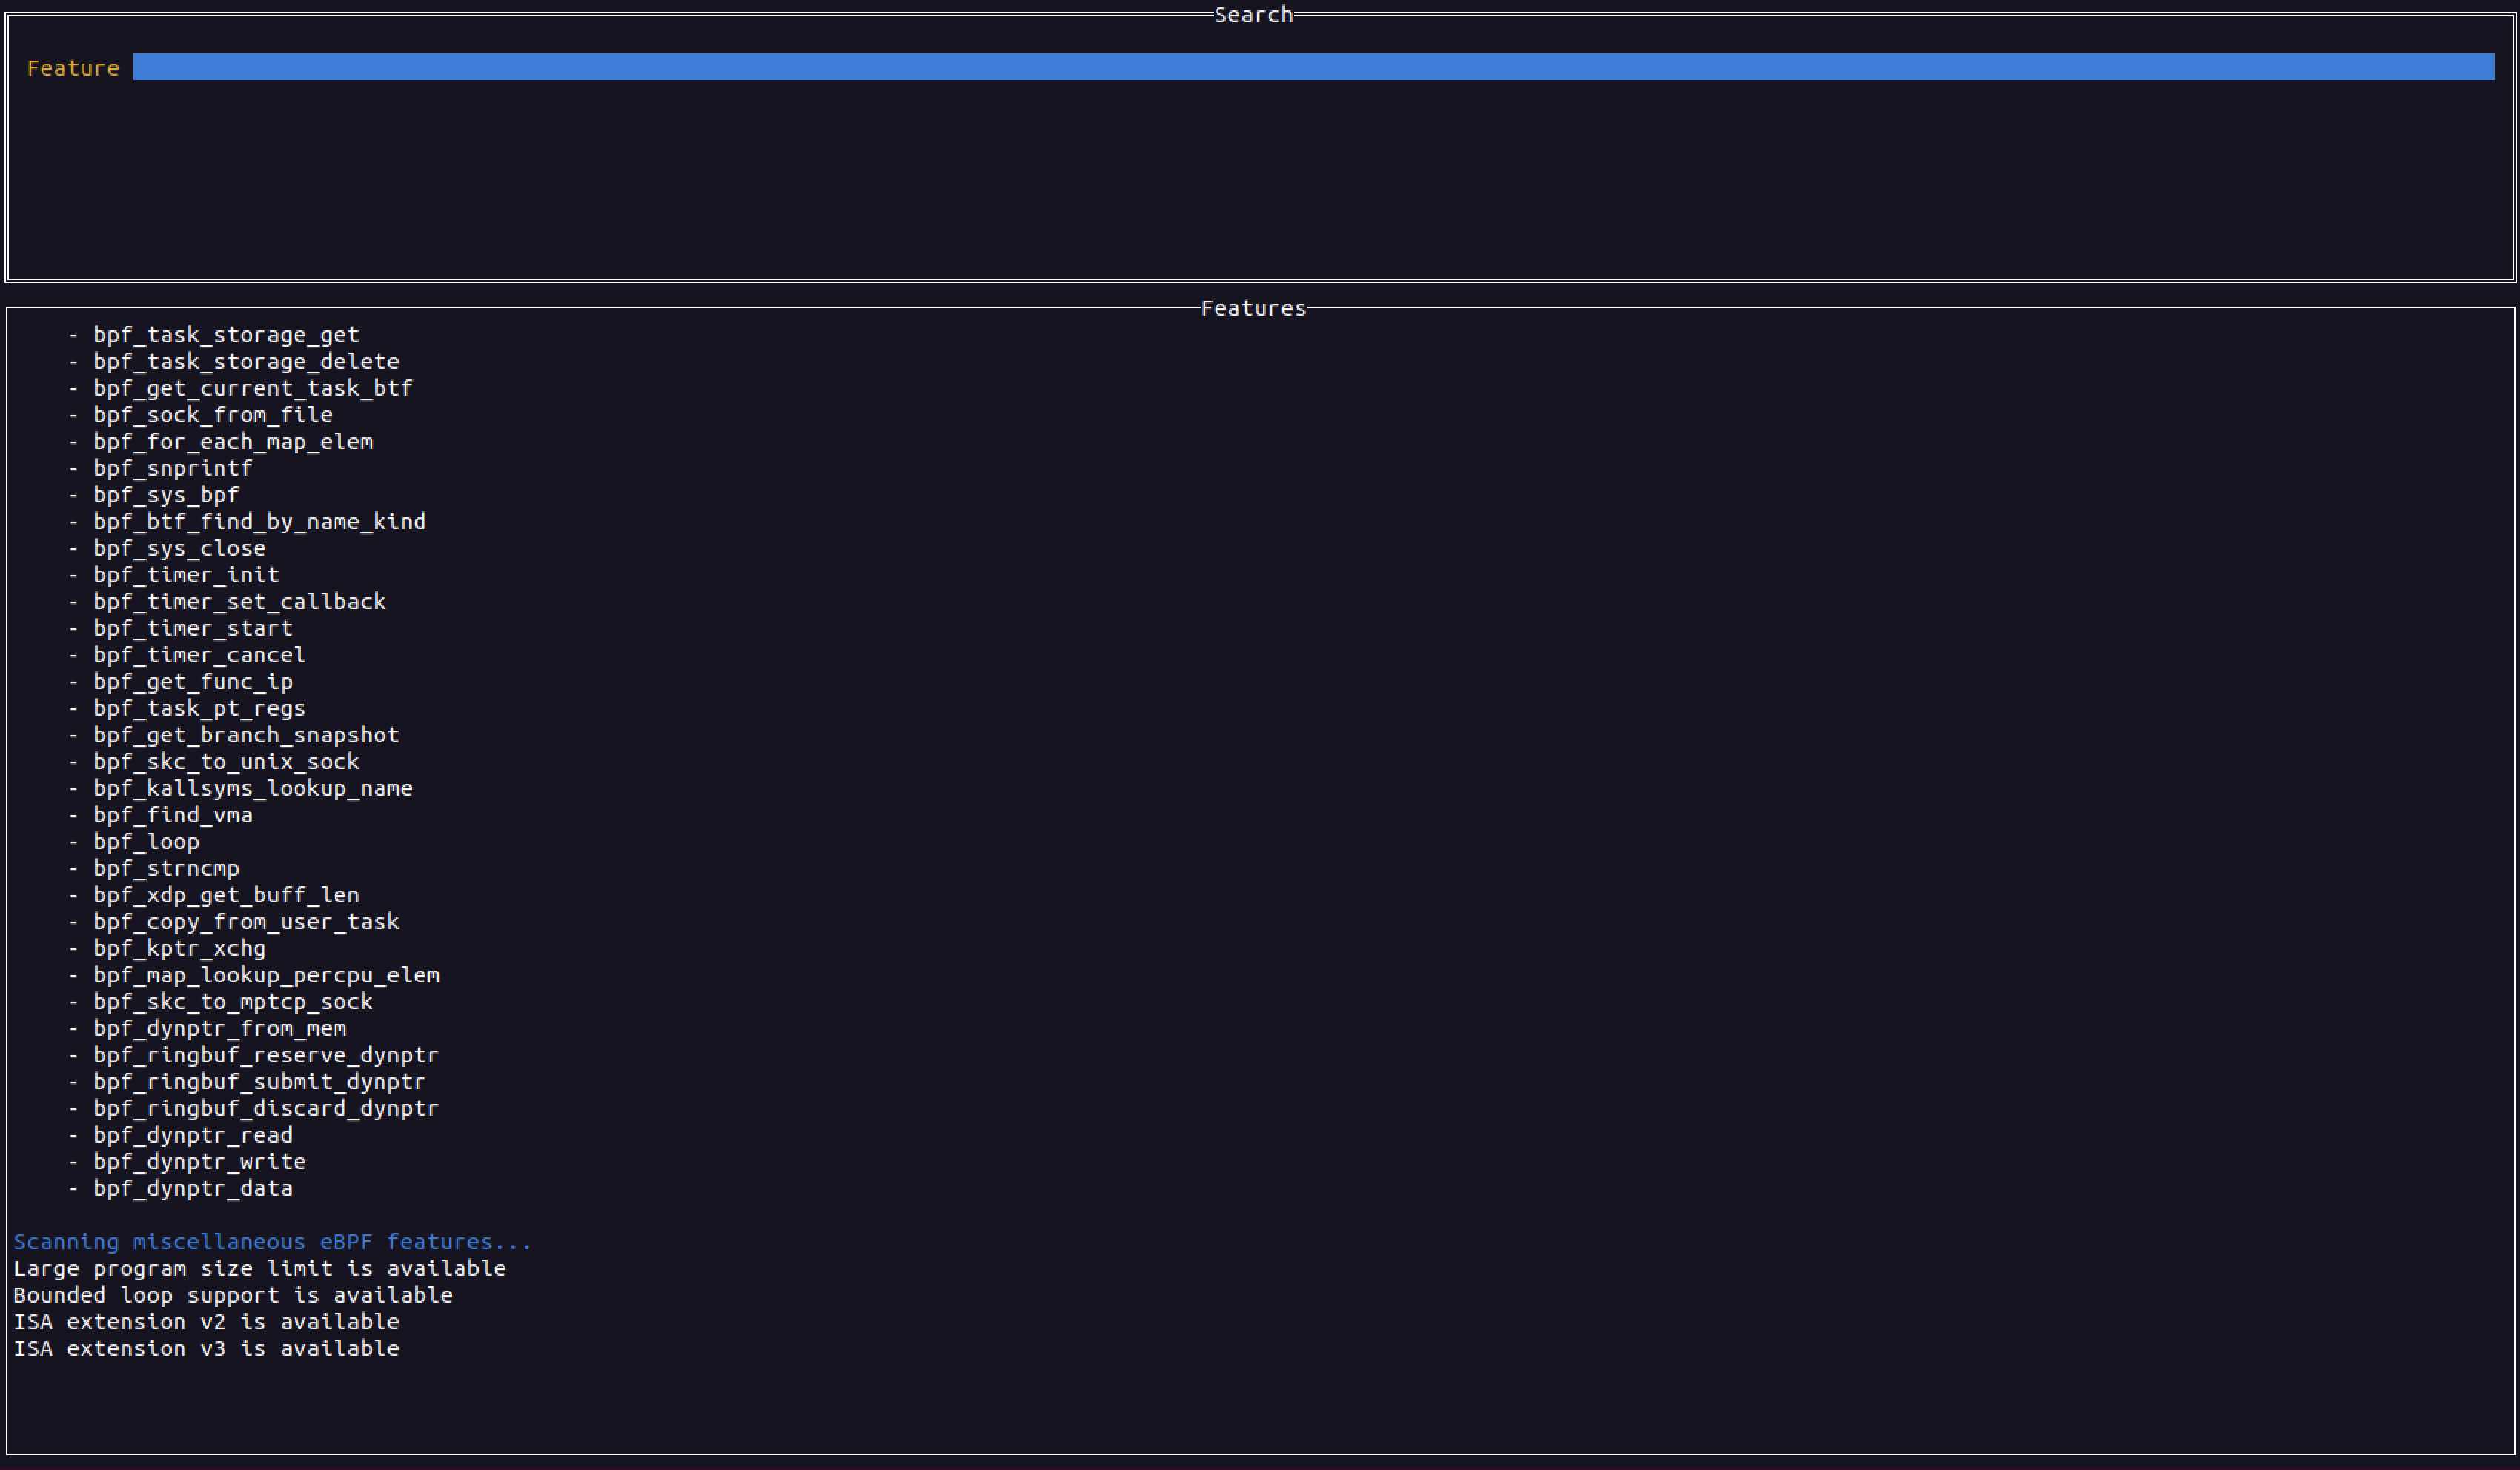
ebpfmon
 redcanaryco/ebpfmon
Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
debuggersdynamic-analysis-sandboxingutilities-frameworks
redcanaryco/ebpfmonTerminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
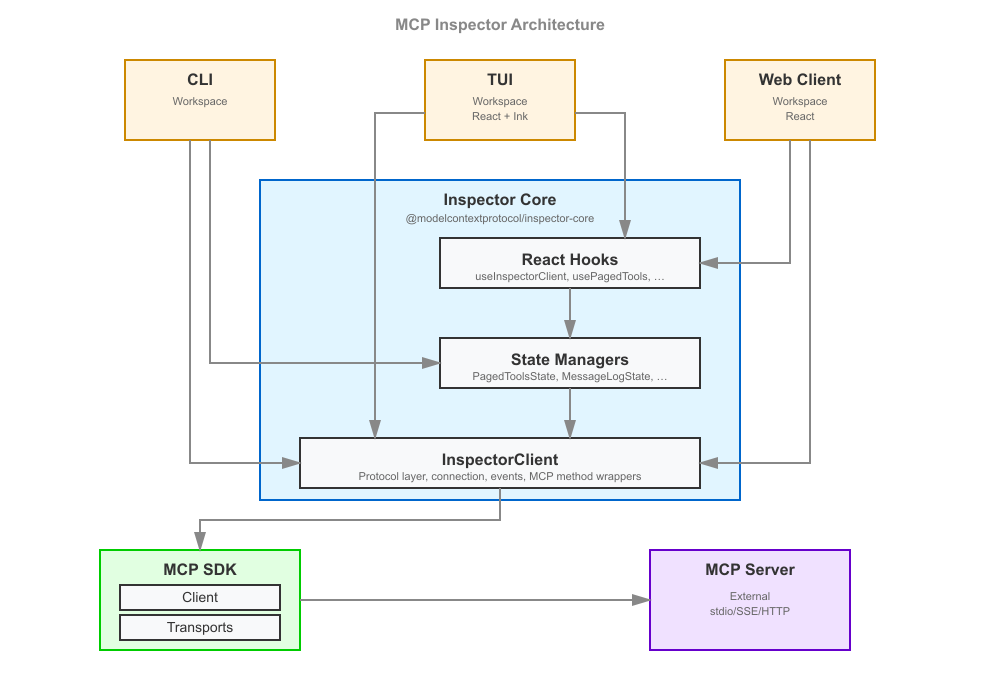 modelcontextprotocol/inspector
Inspect, debug, and visually test Model Context Protocol (MCP) servers from a web UI, CLI, or TUI, with tool/resource exploration, request logging,…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
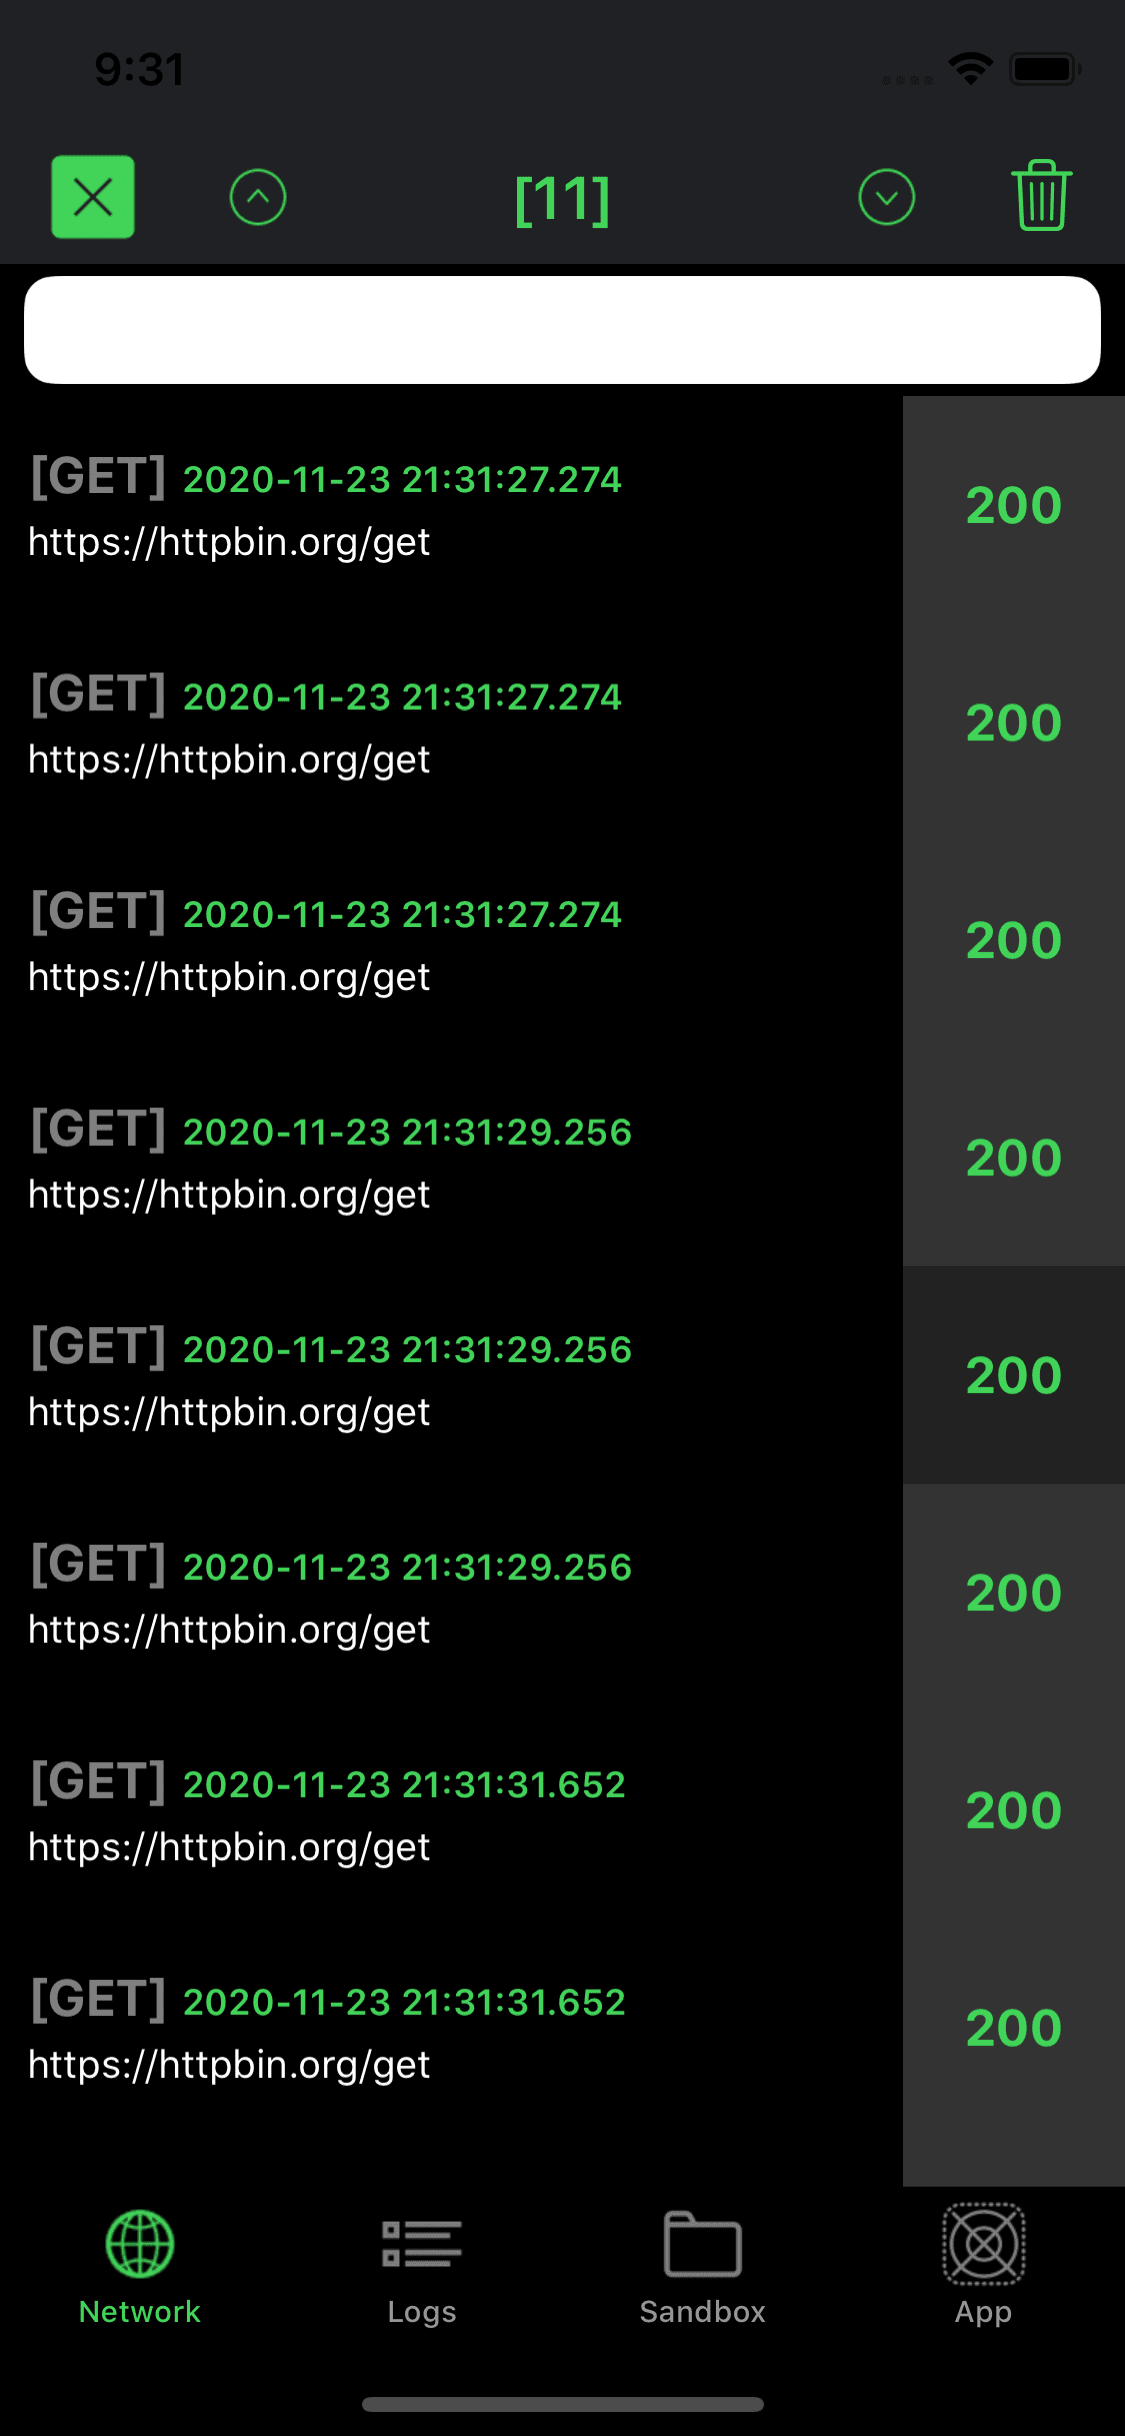 cocoadebug/cocoadebug
iOS Debugging Tool 🚀
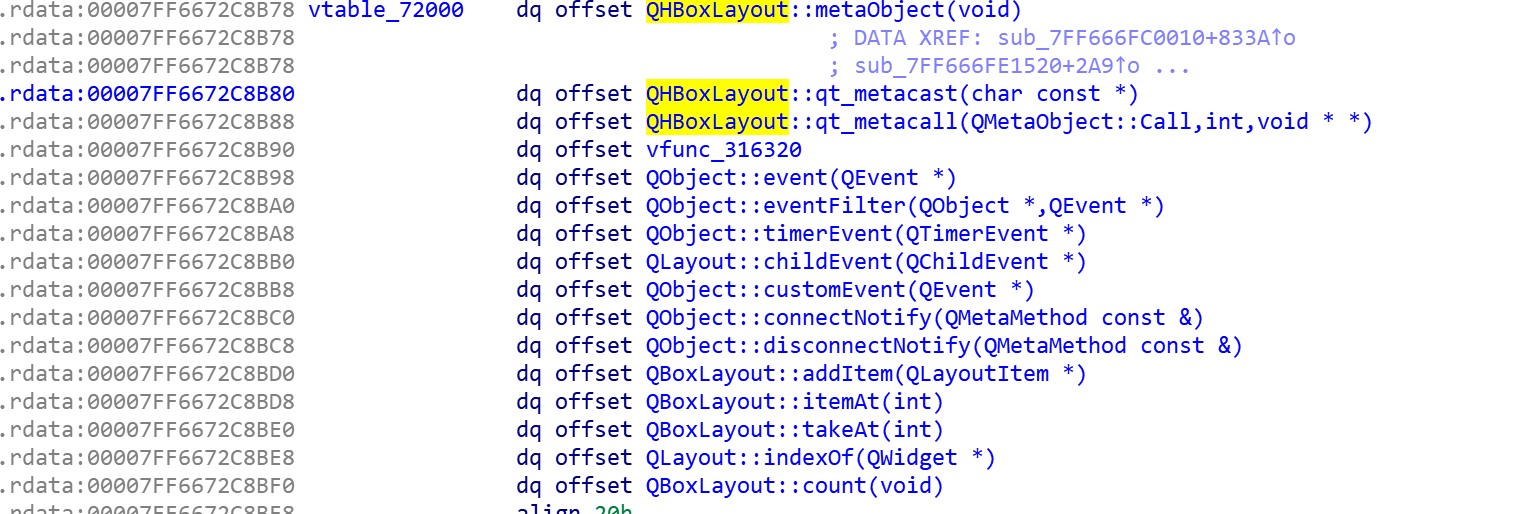 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
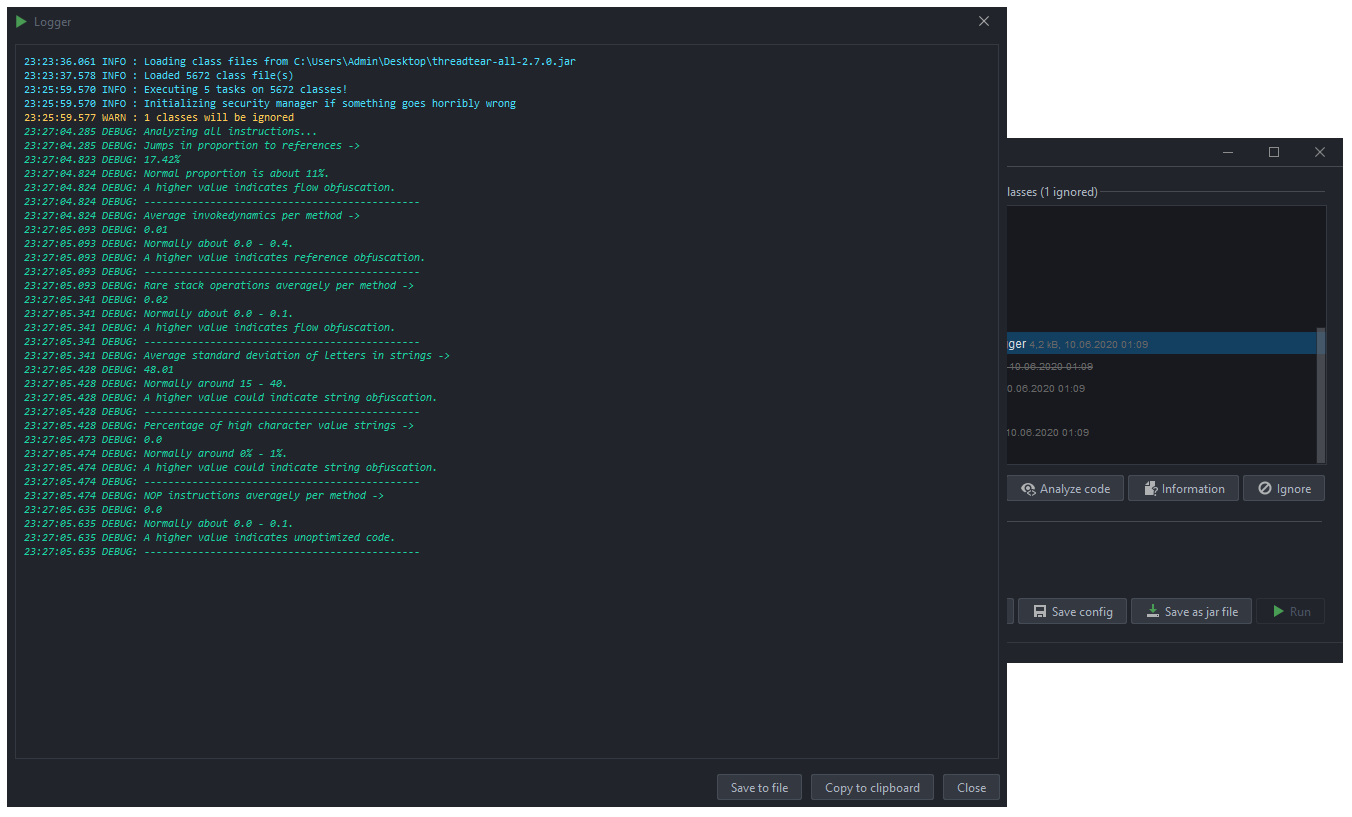 loerting/threadtear
Multifunctional java deobfuscation tool suite
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 t00sh/rop-tool
A tool to help you write binary exploits
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 nccgroup/asatools
Main repository to pull all NCC Group Cisco ASA-related tool projects.
 amossys/memitm
Tool to make in memory man in the middle