

dynamorio
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
dynamorio/dynamorioRuntime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
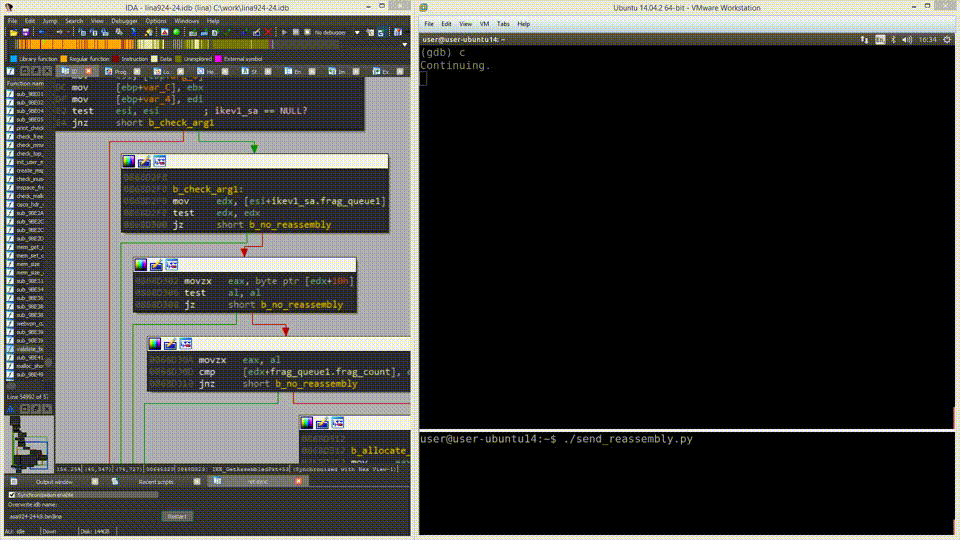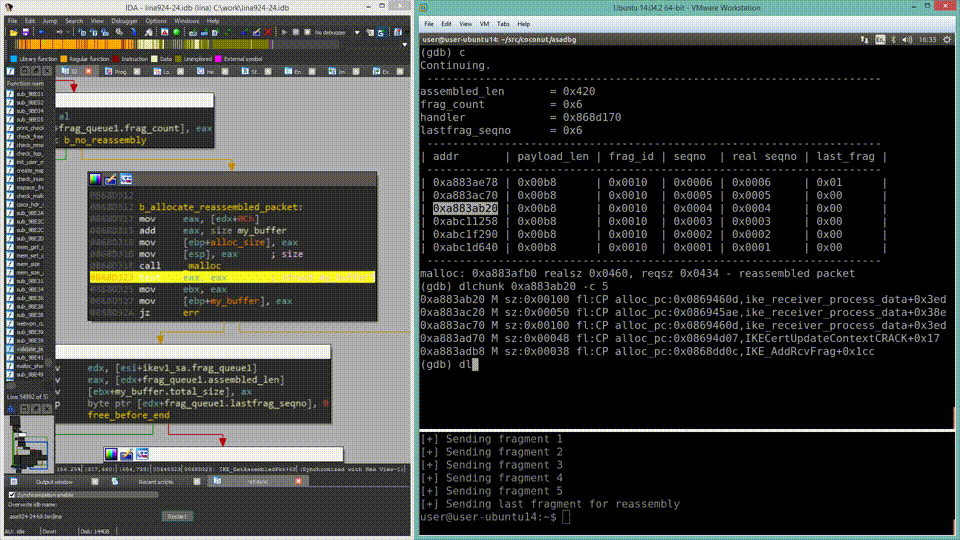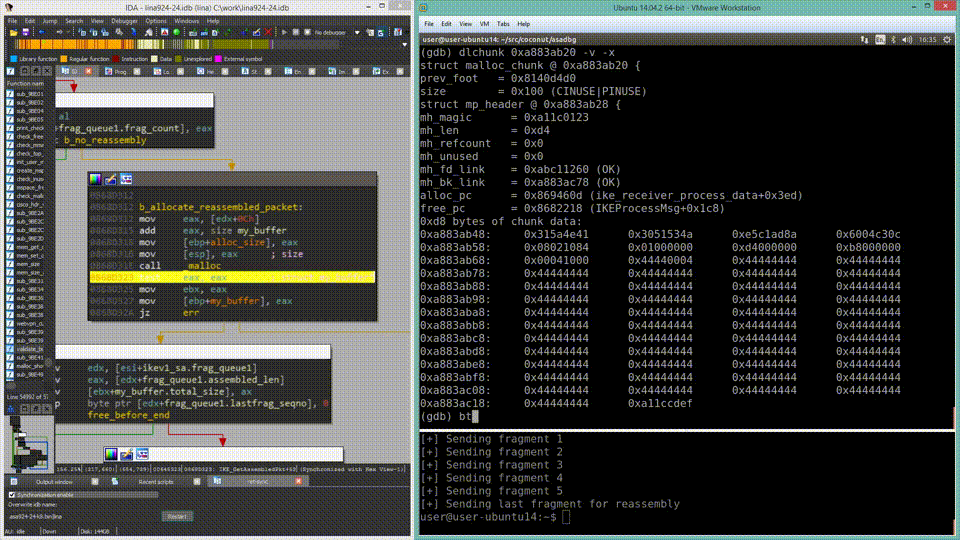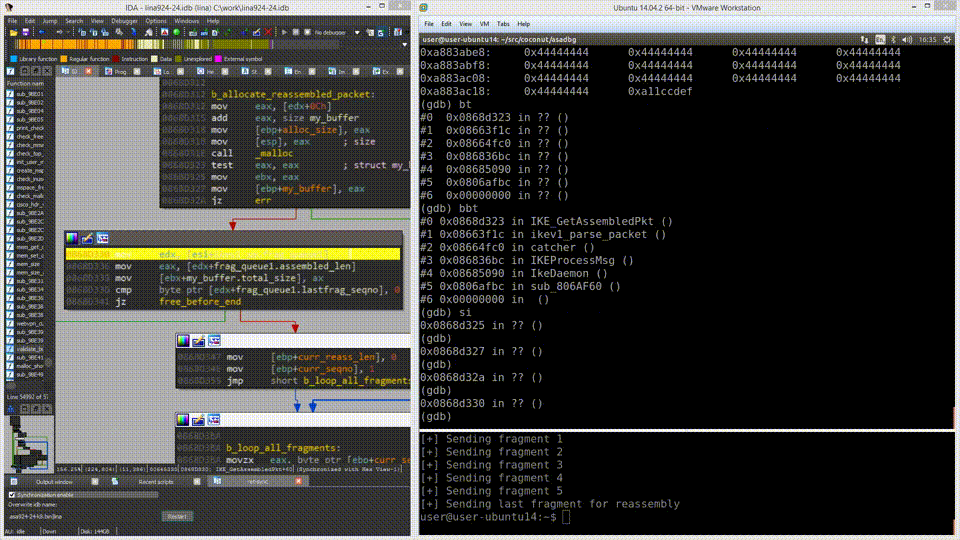 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 gallopsled/pwntools
CTF framework and exploit development library
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
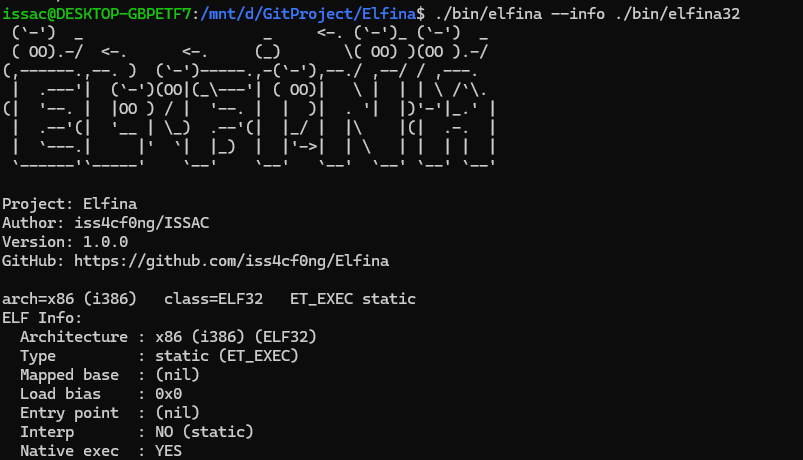 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....