
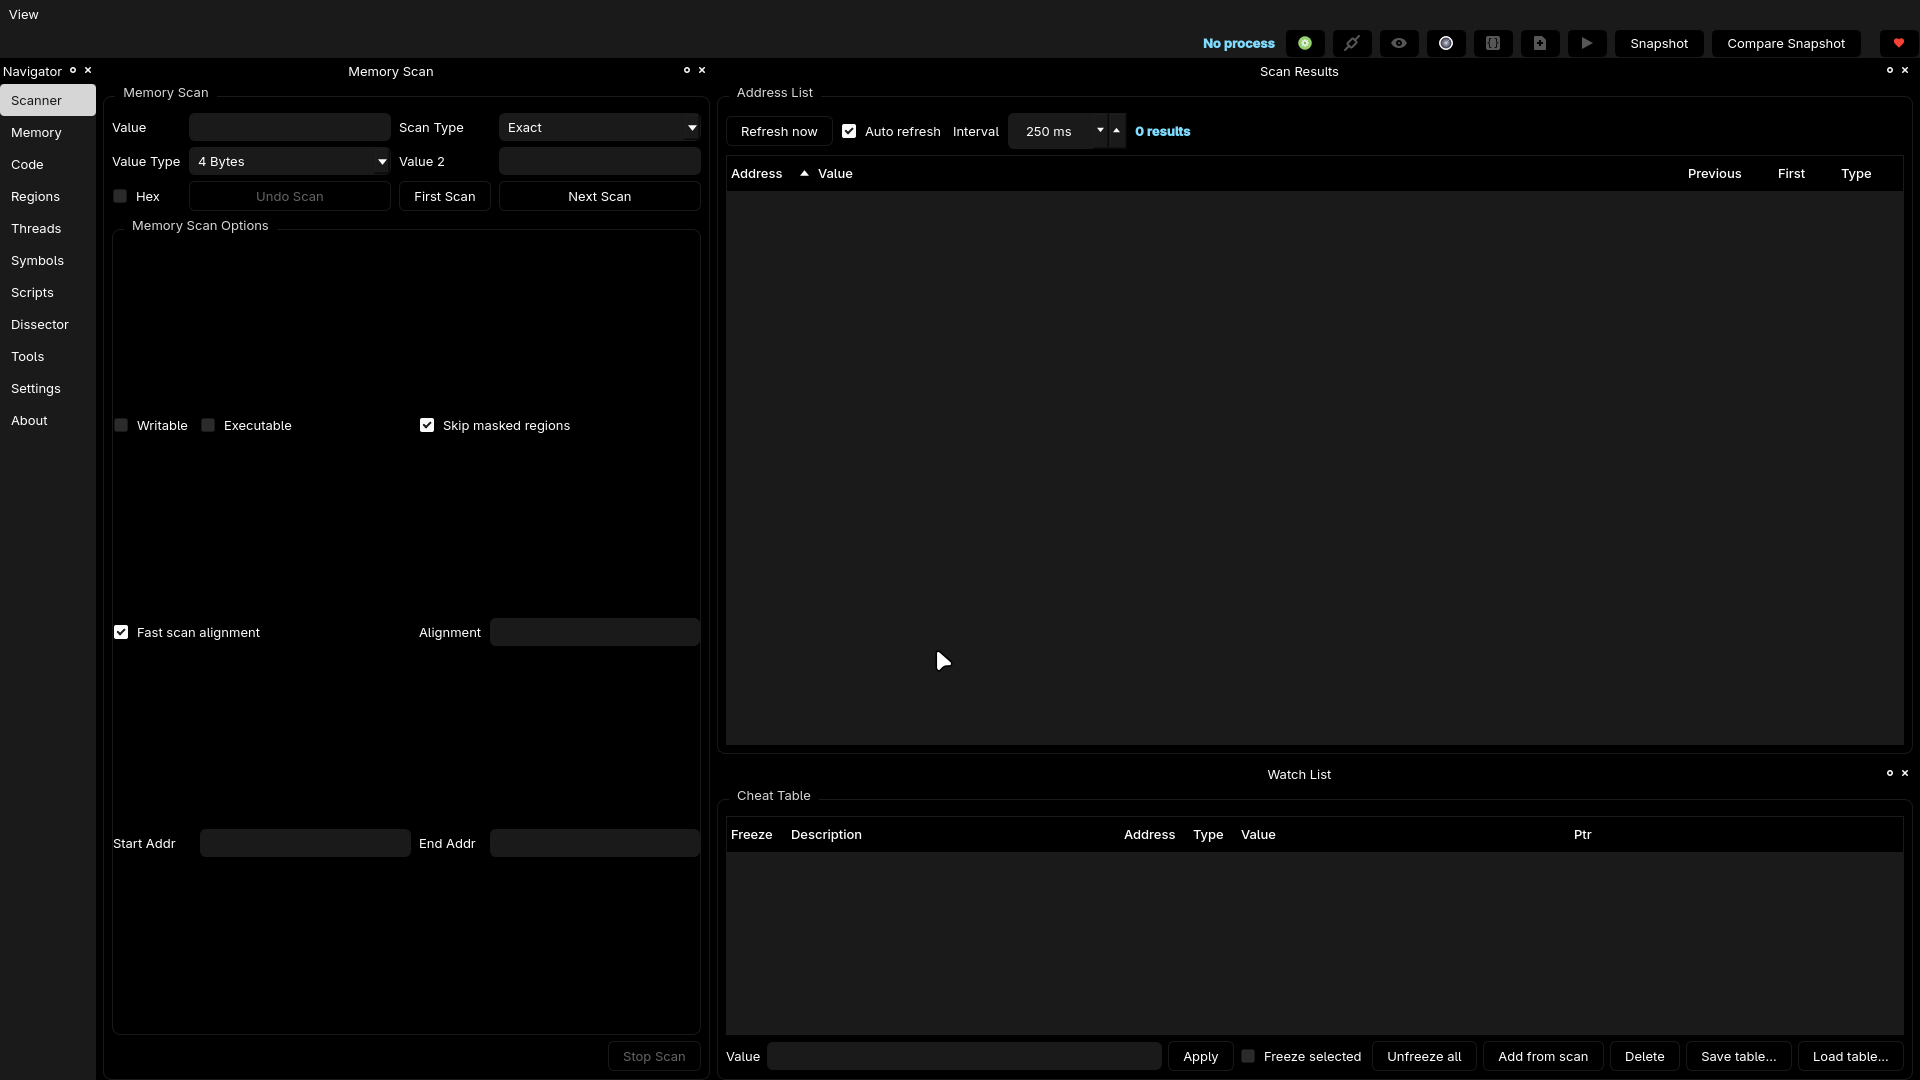
ComfyEngine
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
binary-analysisdebuggersdynamic-code-analysis+5
61
kashithecomfy/comfyengineComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
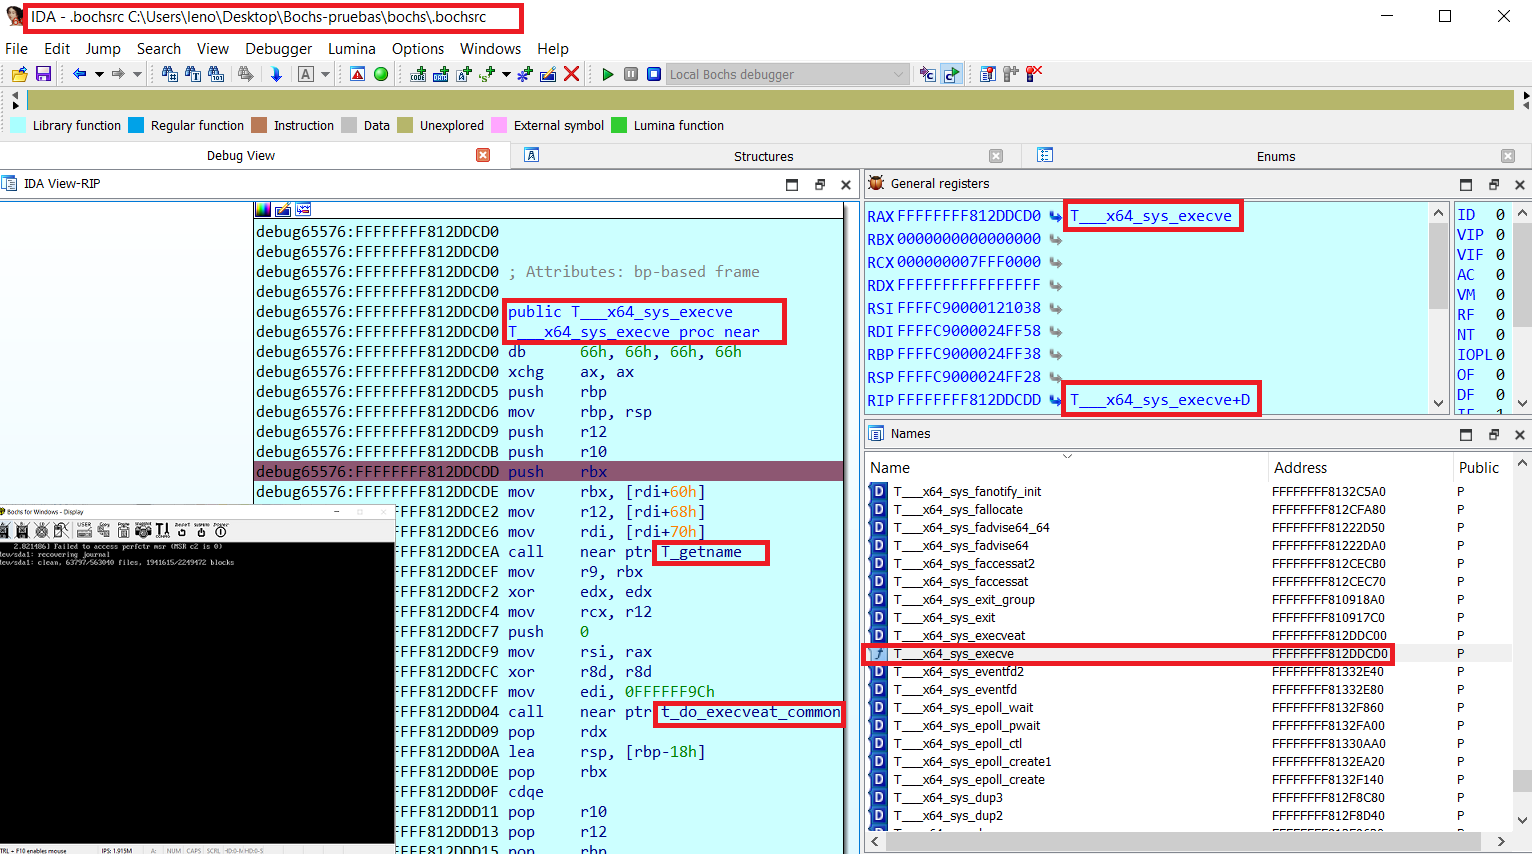 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 dsfau/cve-2018-1000199
Proof-of-concept exploit for Linux kernel ptrace debug register corruption (CVE-2018-1000199), demonstrating incorrect error handling in breakpoint…
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
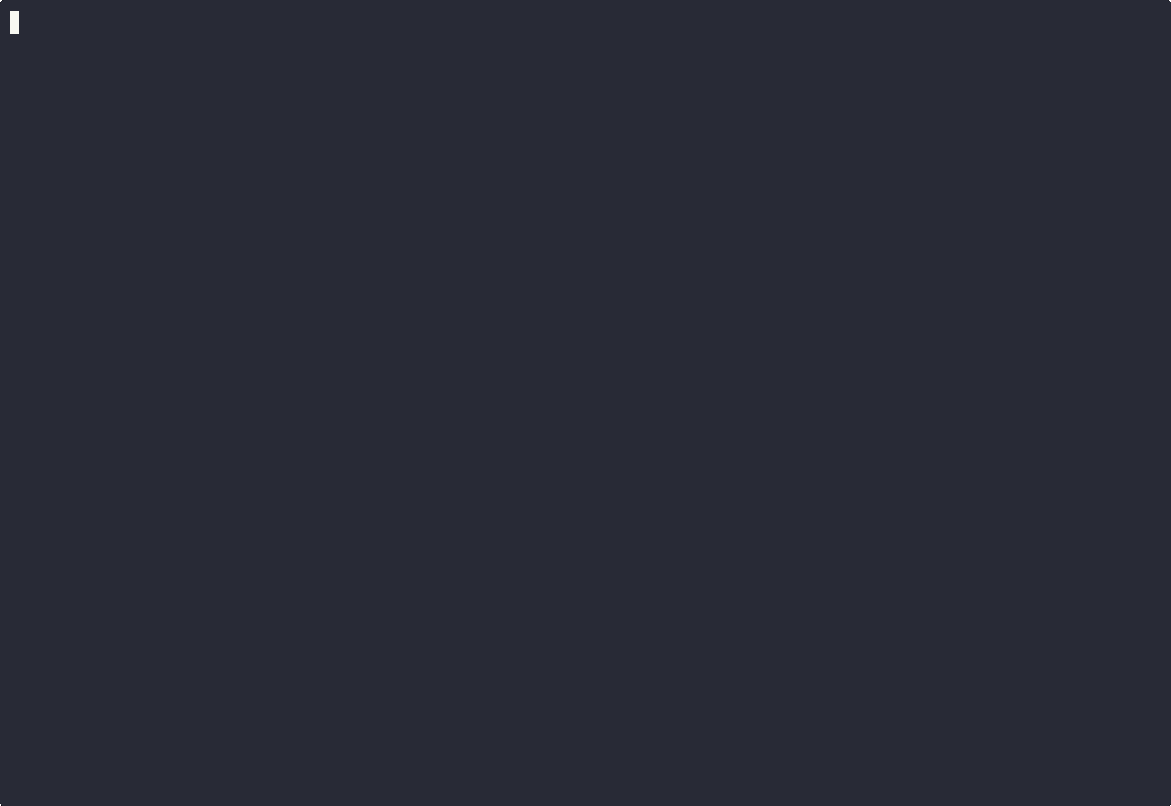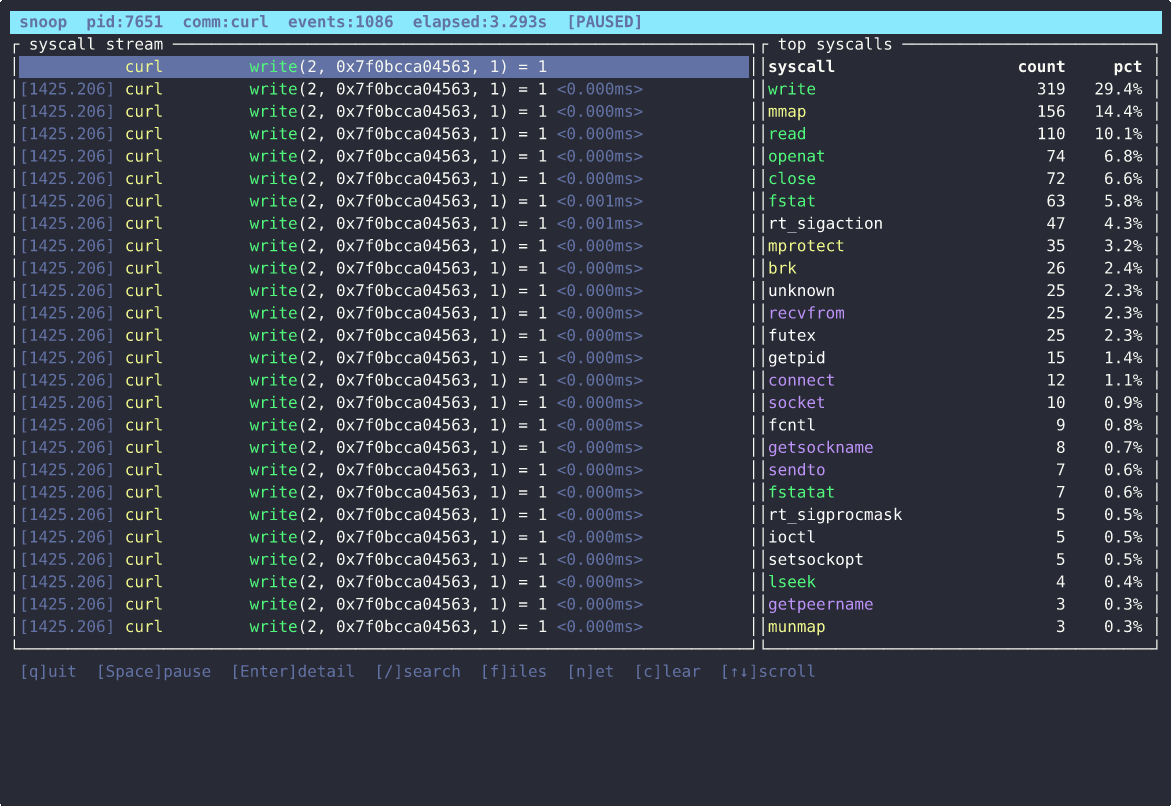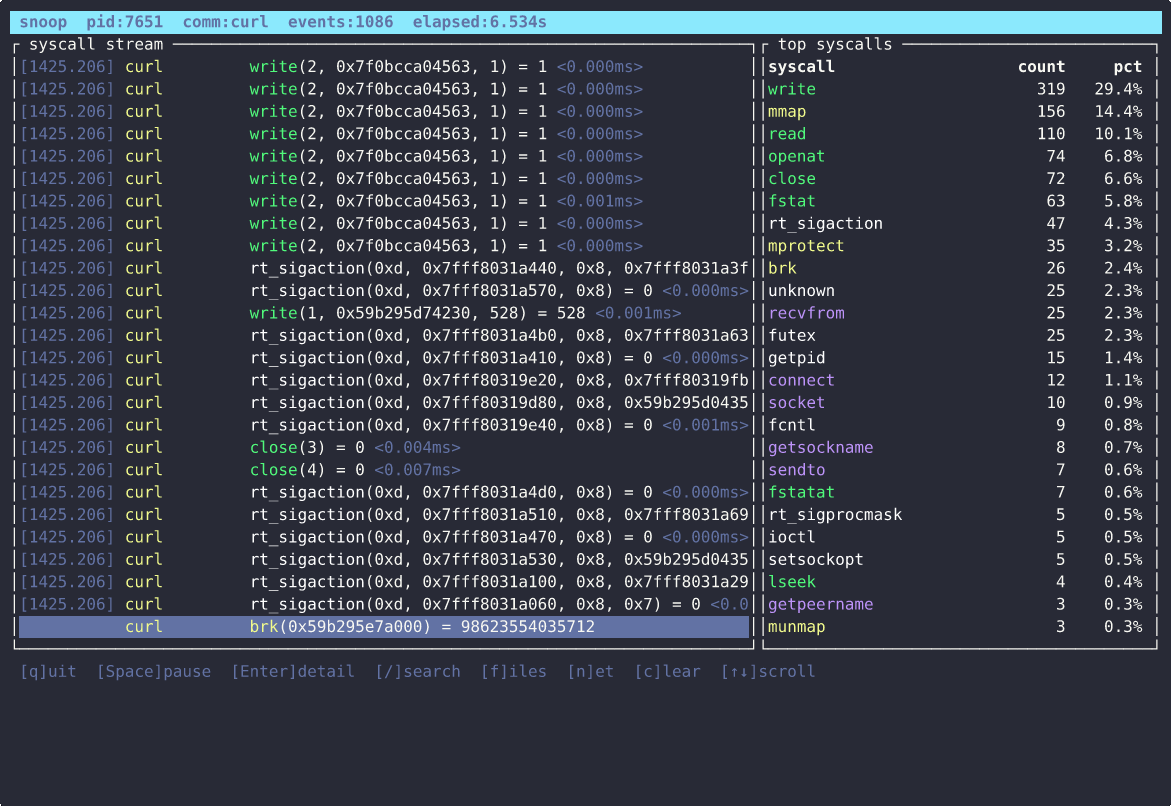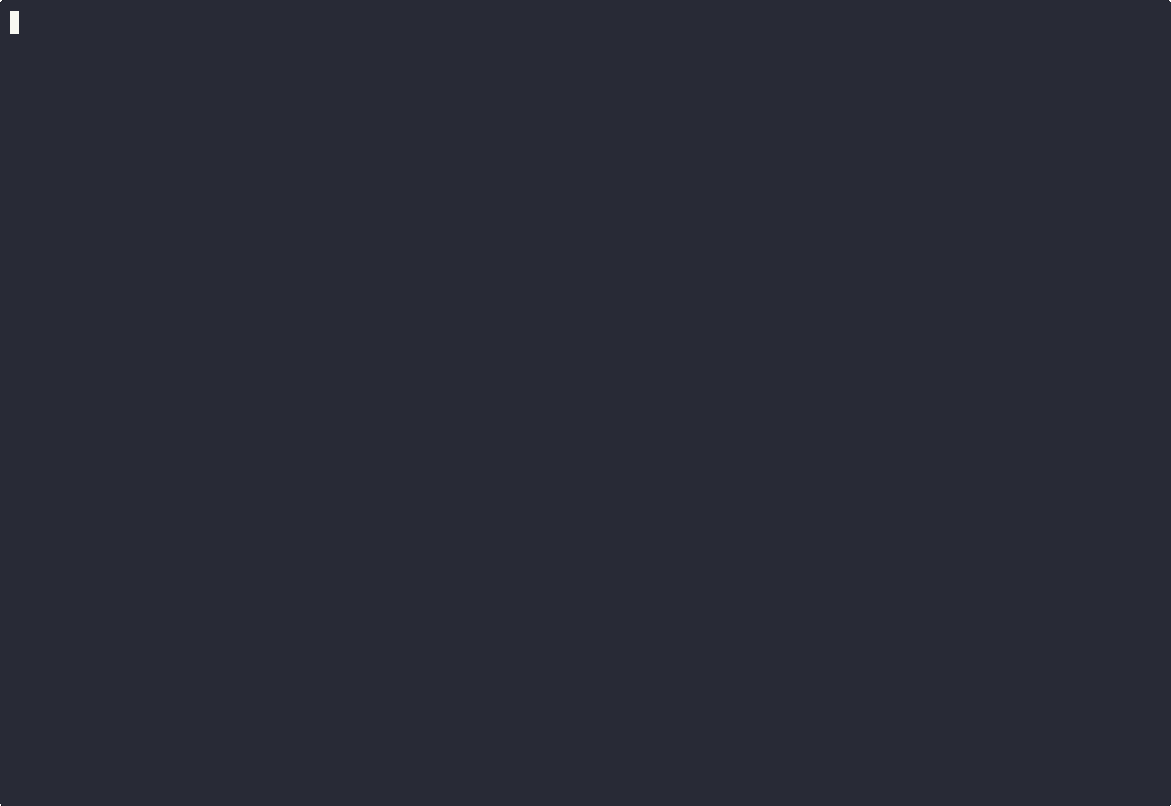 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 nccgroup/libslub
Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
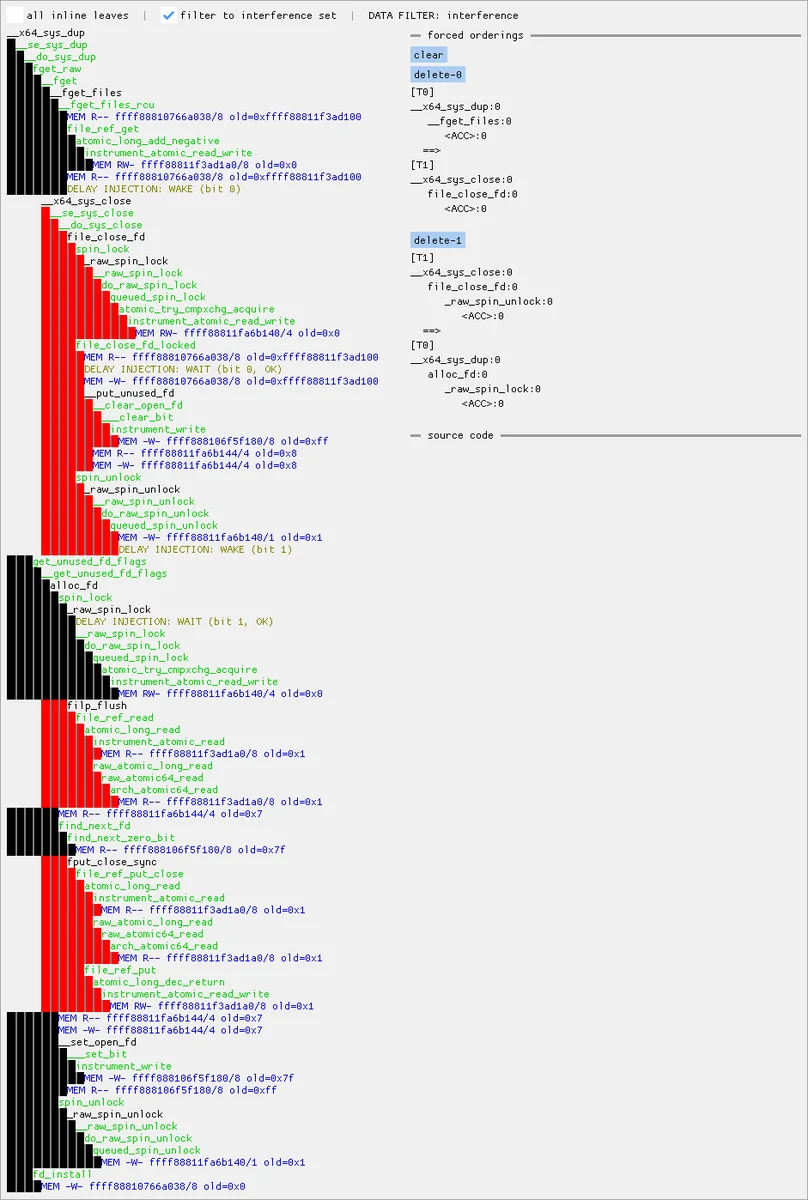 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.