
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
123 results
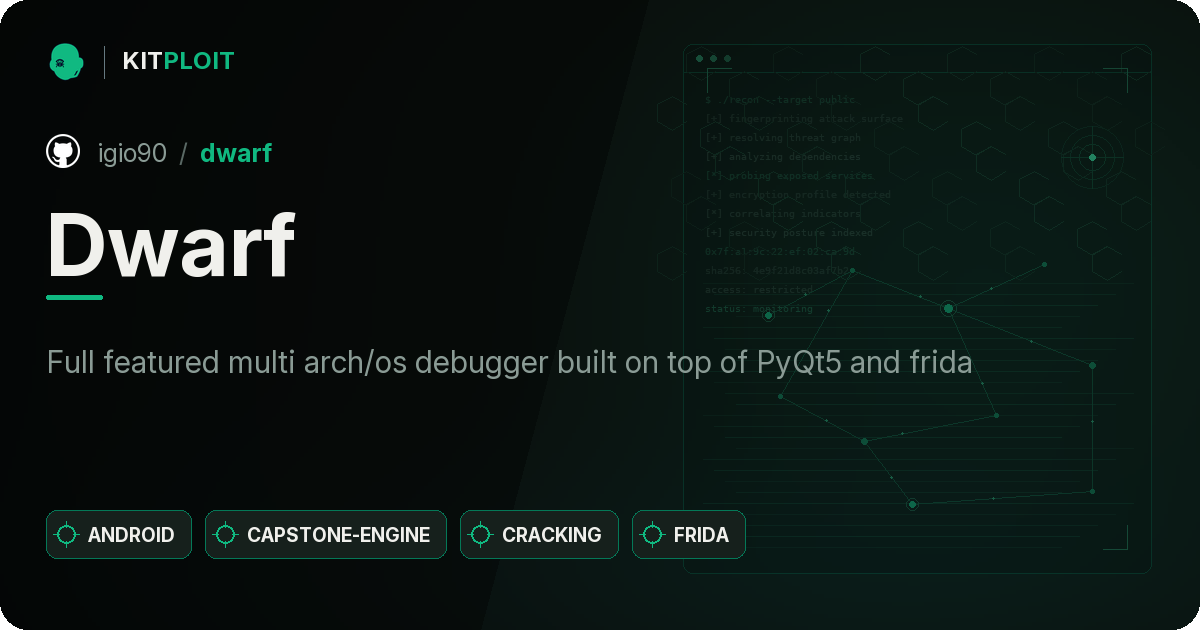
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
206
1 day ago
Dwarf preview

Dwarf

GitHubigio90/dwarf

Full featured multi arch/os debugger built on top of PyQt5 and frida
android-securitybinary-analysisdebuggers+4
1.3k2 years ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubelrajiii/cve-2025-5548

Buffer overflow in FreeFloat FTP Server 1.0

binary-exploitationdebuggerseducation+8
7 months ago
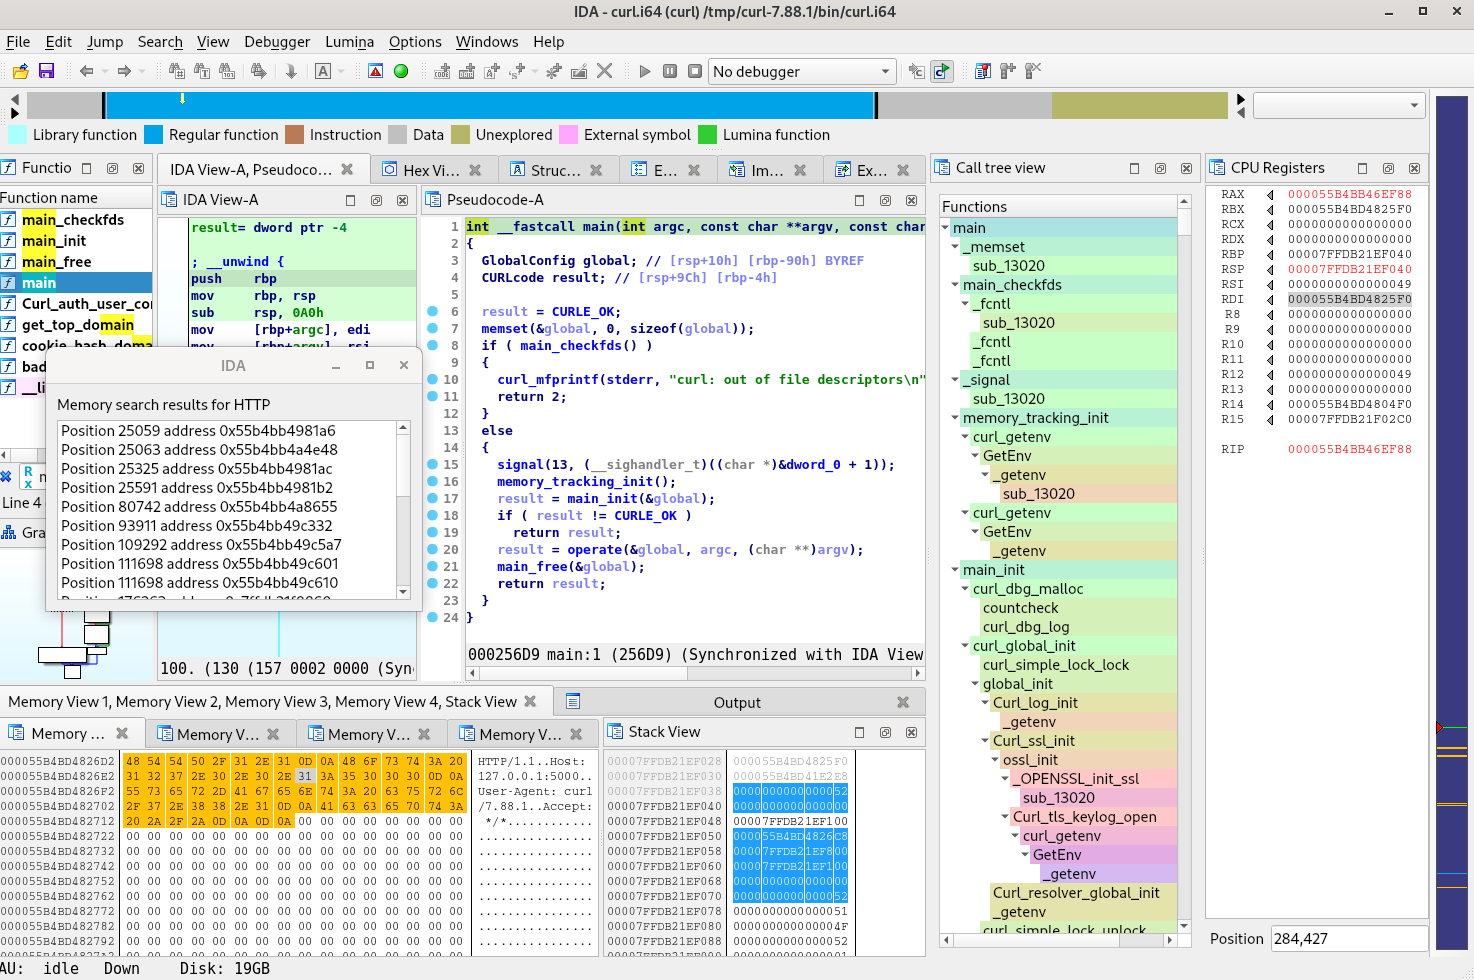
rizin preview

rizin

GitHubrizinorg/rizin

UNIX-like reverse engineering framework and command-line toolset.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
4.1k13 days ago
frinet preview

frinet

GitHubsynacktiv/frinet

Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
6244 months ago
VivisectION preview

VivisectION

GitHubatlas0fd00m/vivisection

Analysis Plugin and Tools for Vivisect
binary-analysisdebuggersdynamic-analysis-sandboxing+2
213 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubcharlyrr/cve-2025-5548

Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…

binary-exploitationdebuggerseducation+7
7 months ago
c0ntextomy preview

c0ntextomy

GitHubc0ntextomy/c0ntextomy

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
data-exfiltrationdebuggersexploitation+9
736 years ago
openocd preview

openocd

GitHubopenocd-org/openocd

Official OpenOCD Read-Only Mirror (no pull requests)
debuggersembedded-systems-securityfirmware-analysis+4
2.3k10 months ago
Jackalope preview

Jackalope

GitHubgoogleprojectzero/jackalope

Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
binary-analysisdebuggersdynamic-analysis-sandboxing+6
1.4k2 months ago
xnu preview

xnu

GitHubapple-oss-distributions/xnu

Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
debuggersembedded-systems-securityfirmware-analysis+2
3.5k1 year ago
EhTrace preview

EhTrace

GitHubk2/ehtrace

ATrace is a tool for tracing execution of binaries on Windows.

binary-analysiscode-analysisdebuggers+4
24311 months ago
dynamorio preview

dynamorio

GitHubdynamorio/dynamorio

Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k15h 41m ago
DotNetHookerToolkit preview

DotNetHookerToolkit

GitHubsensepost/dotnethookertoolkit

Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
binary-analysiscode-analysisdebuggers+4
118 months ago
CVE-2023-52356-libtiff-analysis preview

CVE-2023-52356-libtiff-analysis

GitHubyardenbenita/cve-2023-52356-libtiff-analysis

Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
binary-analysisdebuggerseducation+2
1 month ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…

binary-exploitationdebuggerseducation+7
52 months ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
binary-analysisdebuggersdigital-forensics+10
8.9k28 days ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
Previous1234567Next