

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 fuzzysecurity/powershell-suite
My musings with PowerShell
 rehints/hexrayscodexplorer
Hex-Rays Decompiler plugin for better code navigation
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
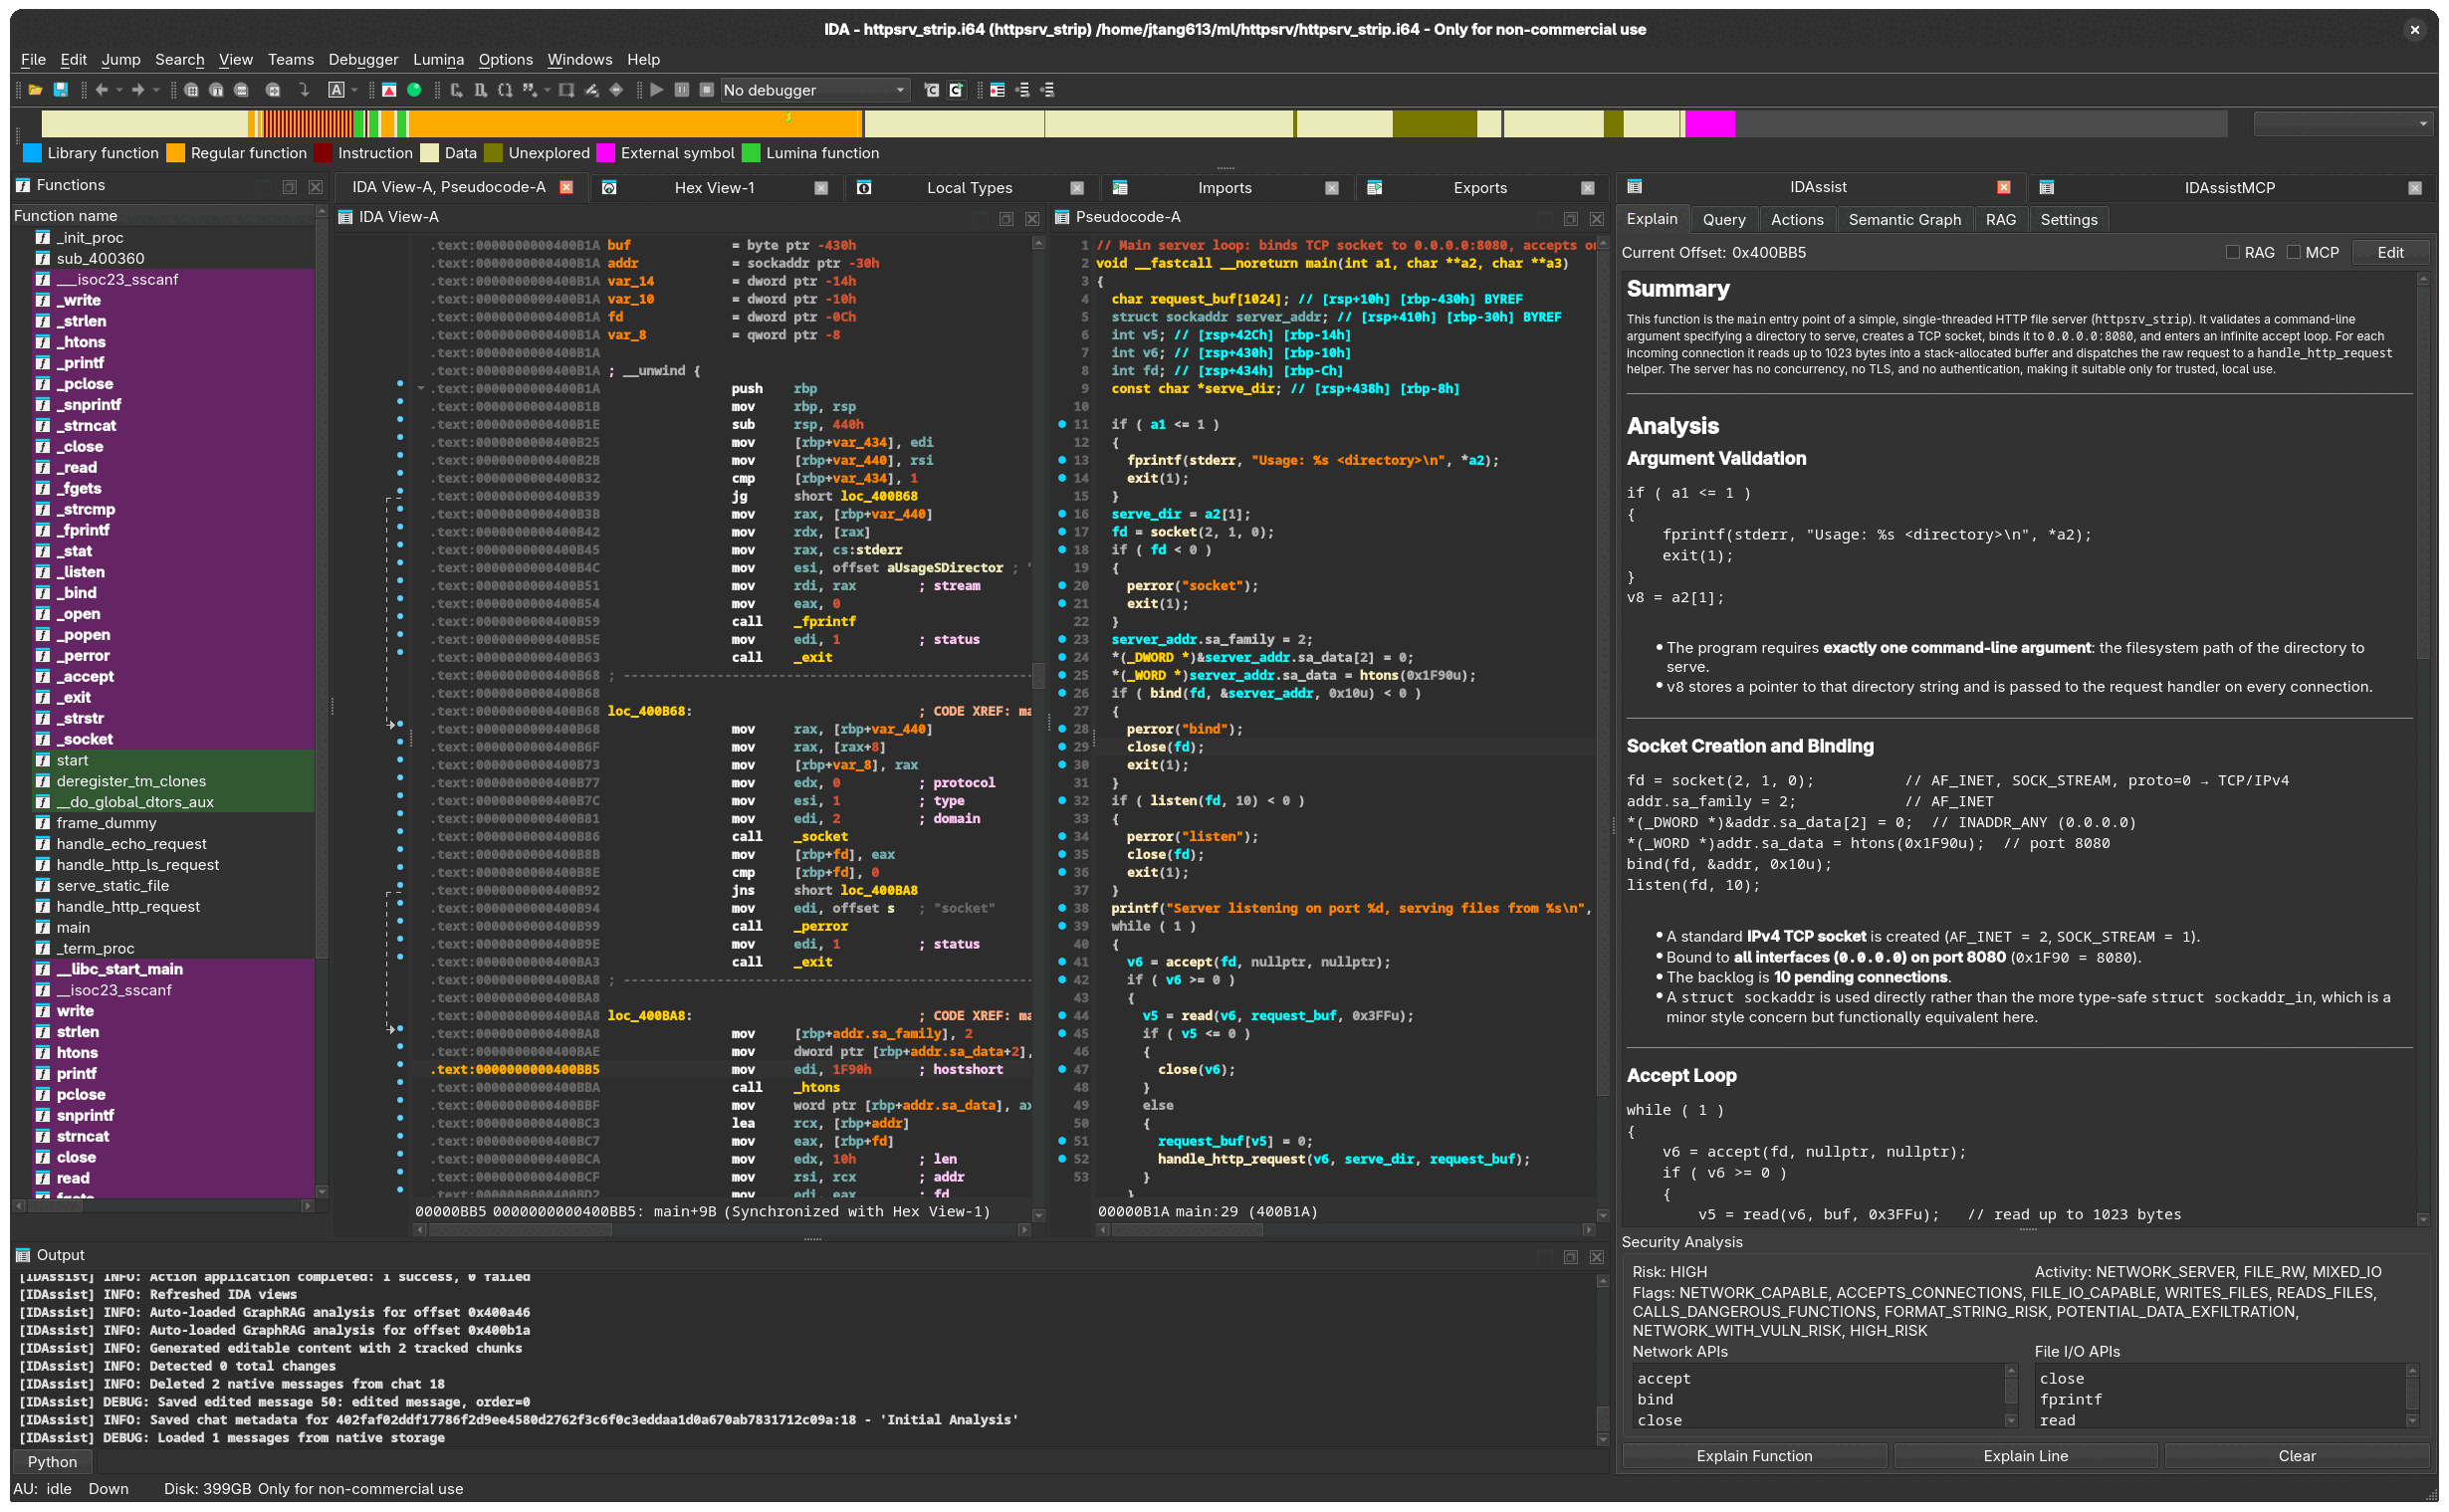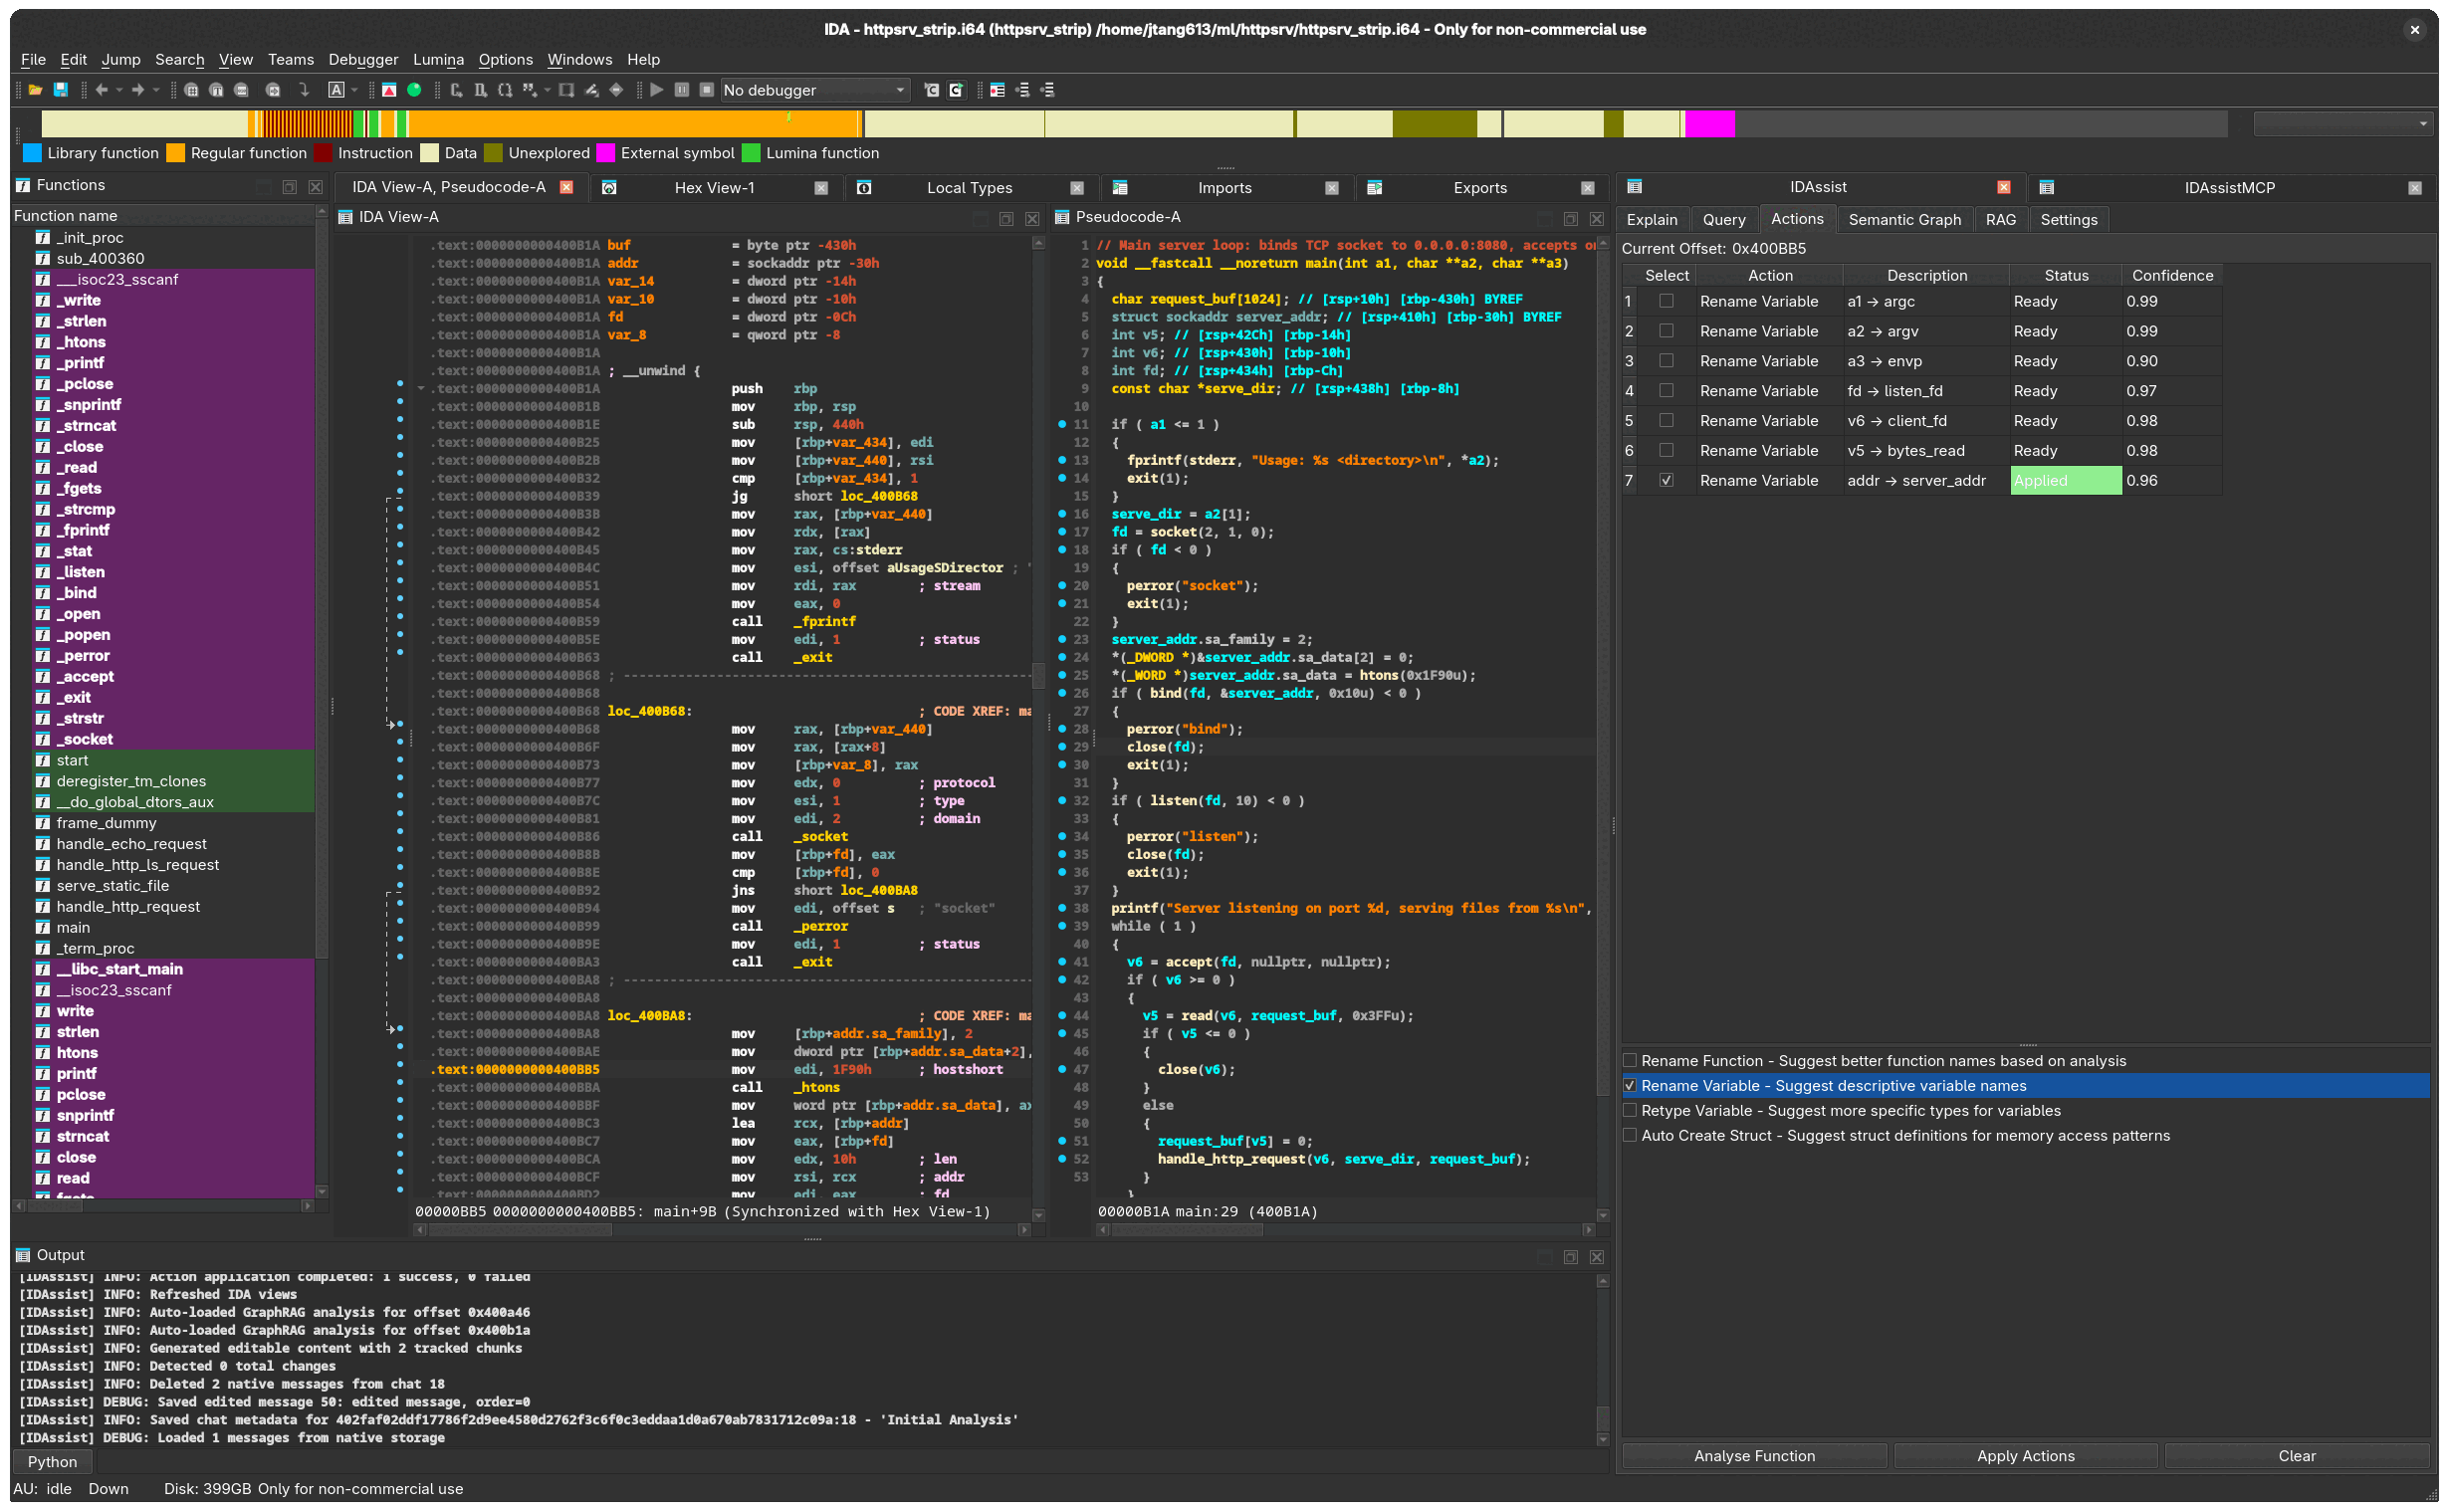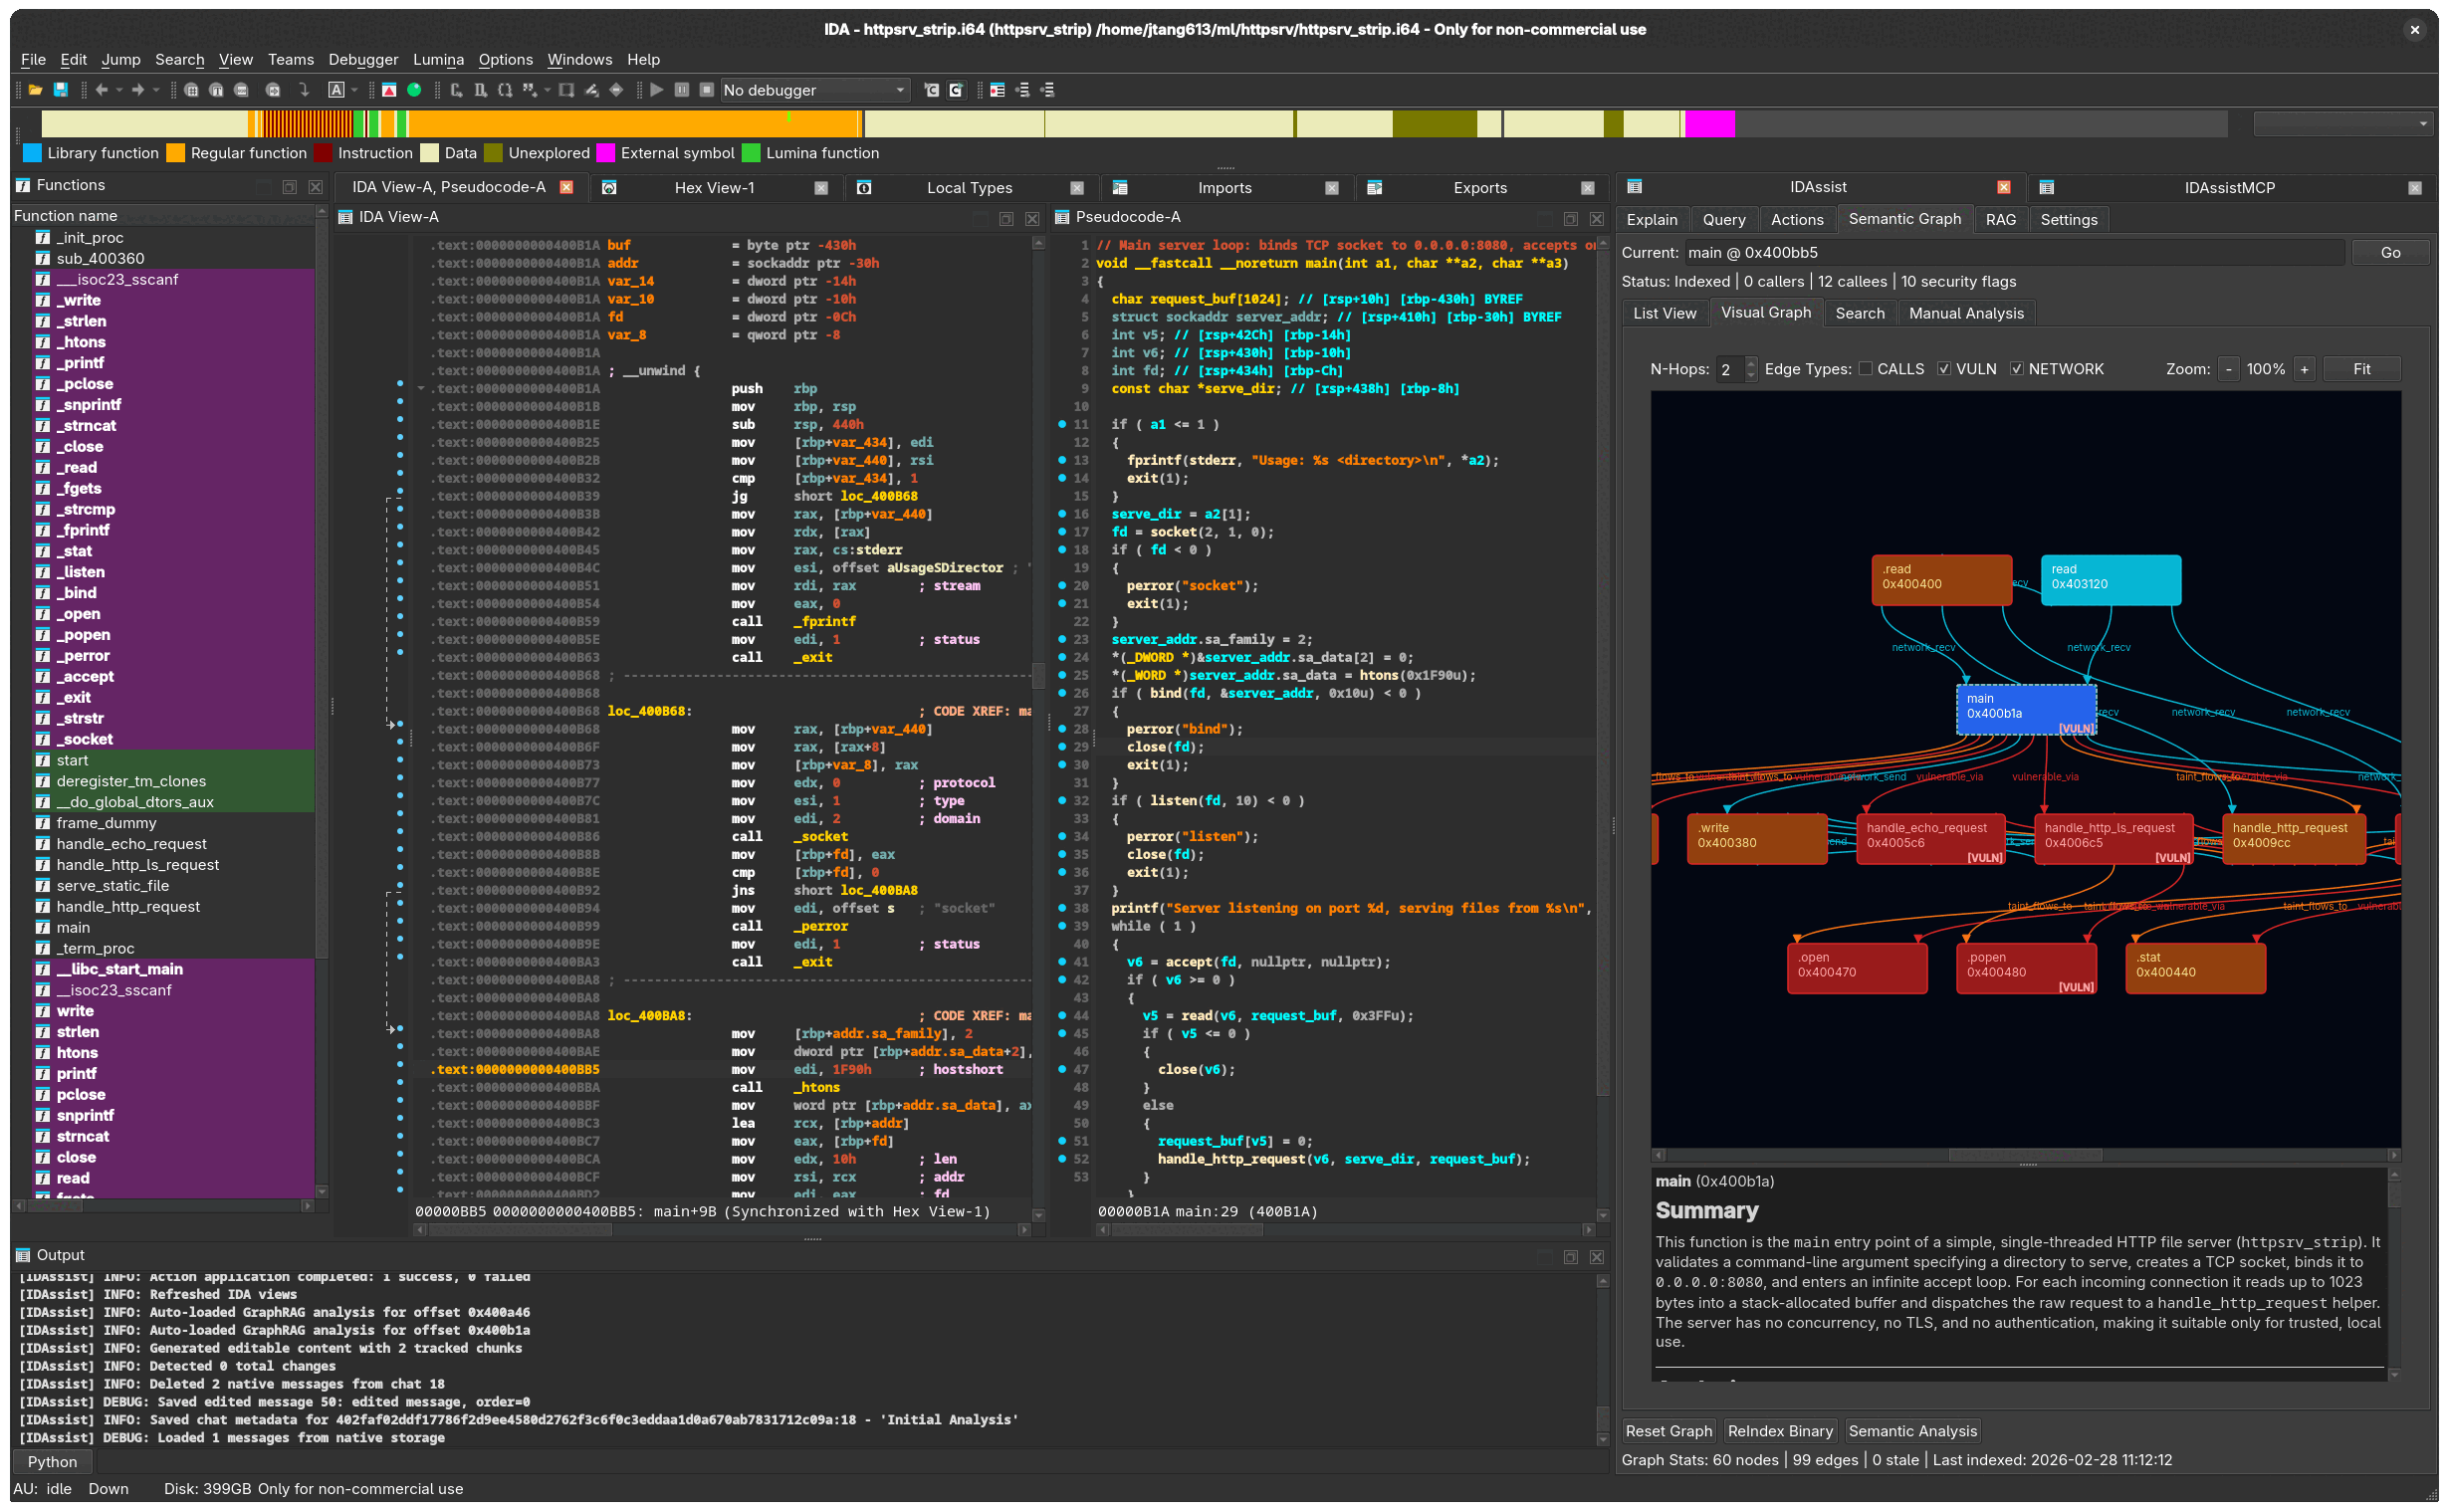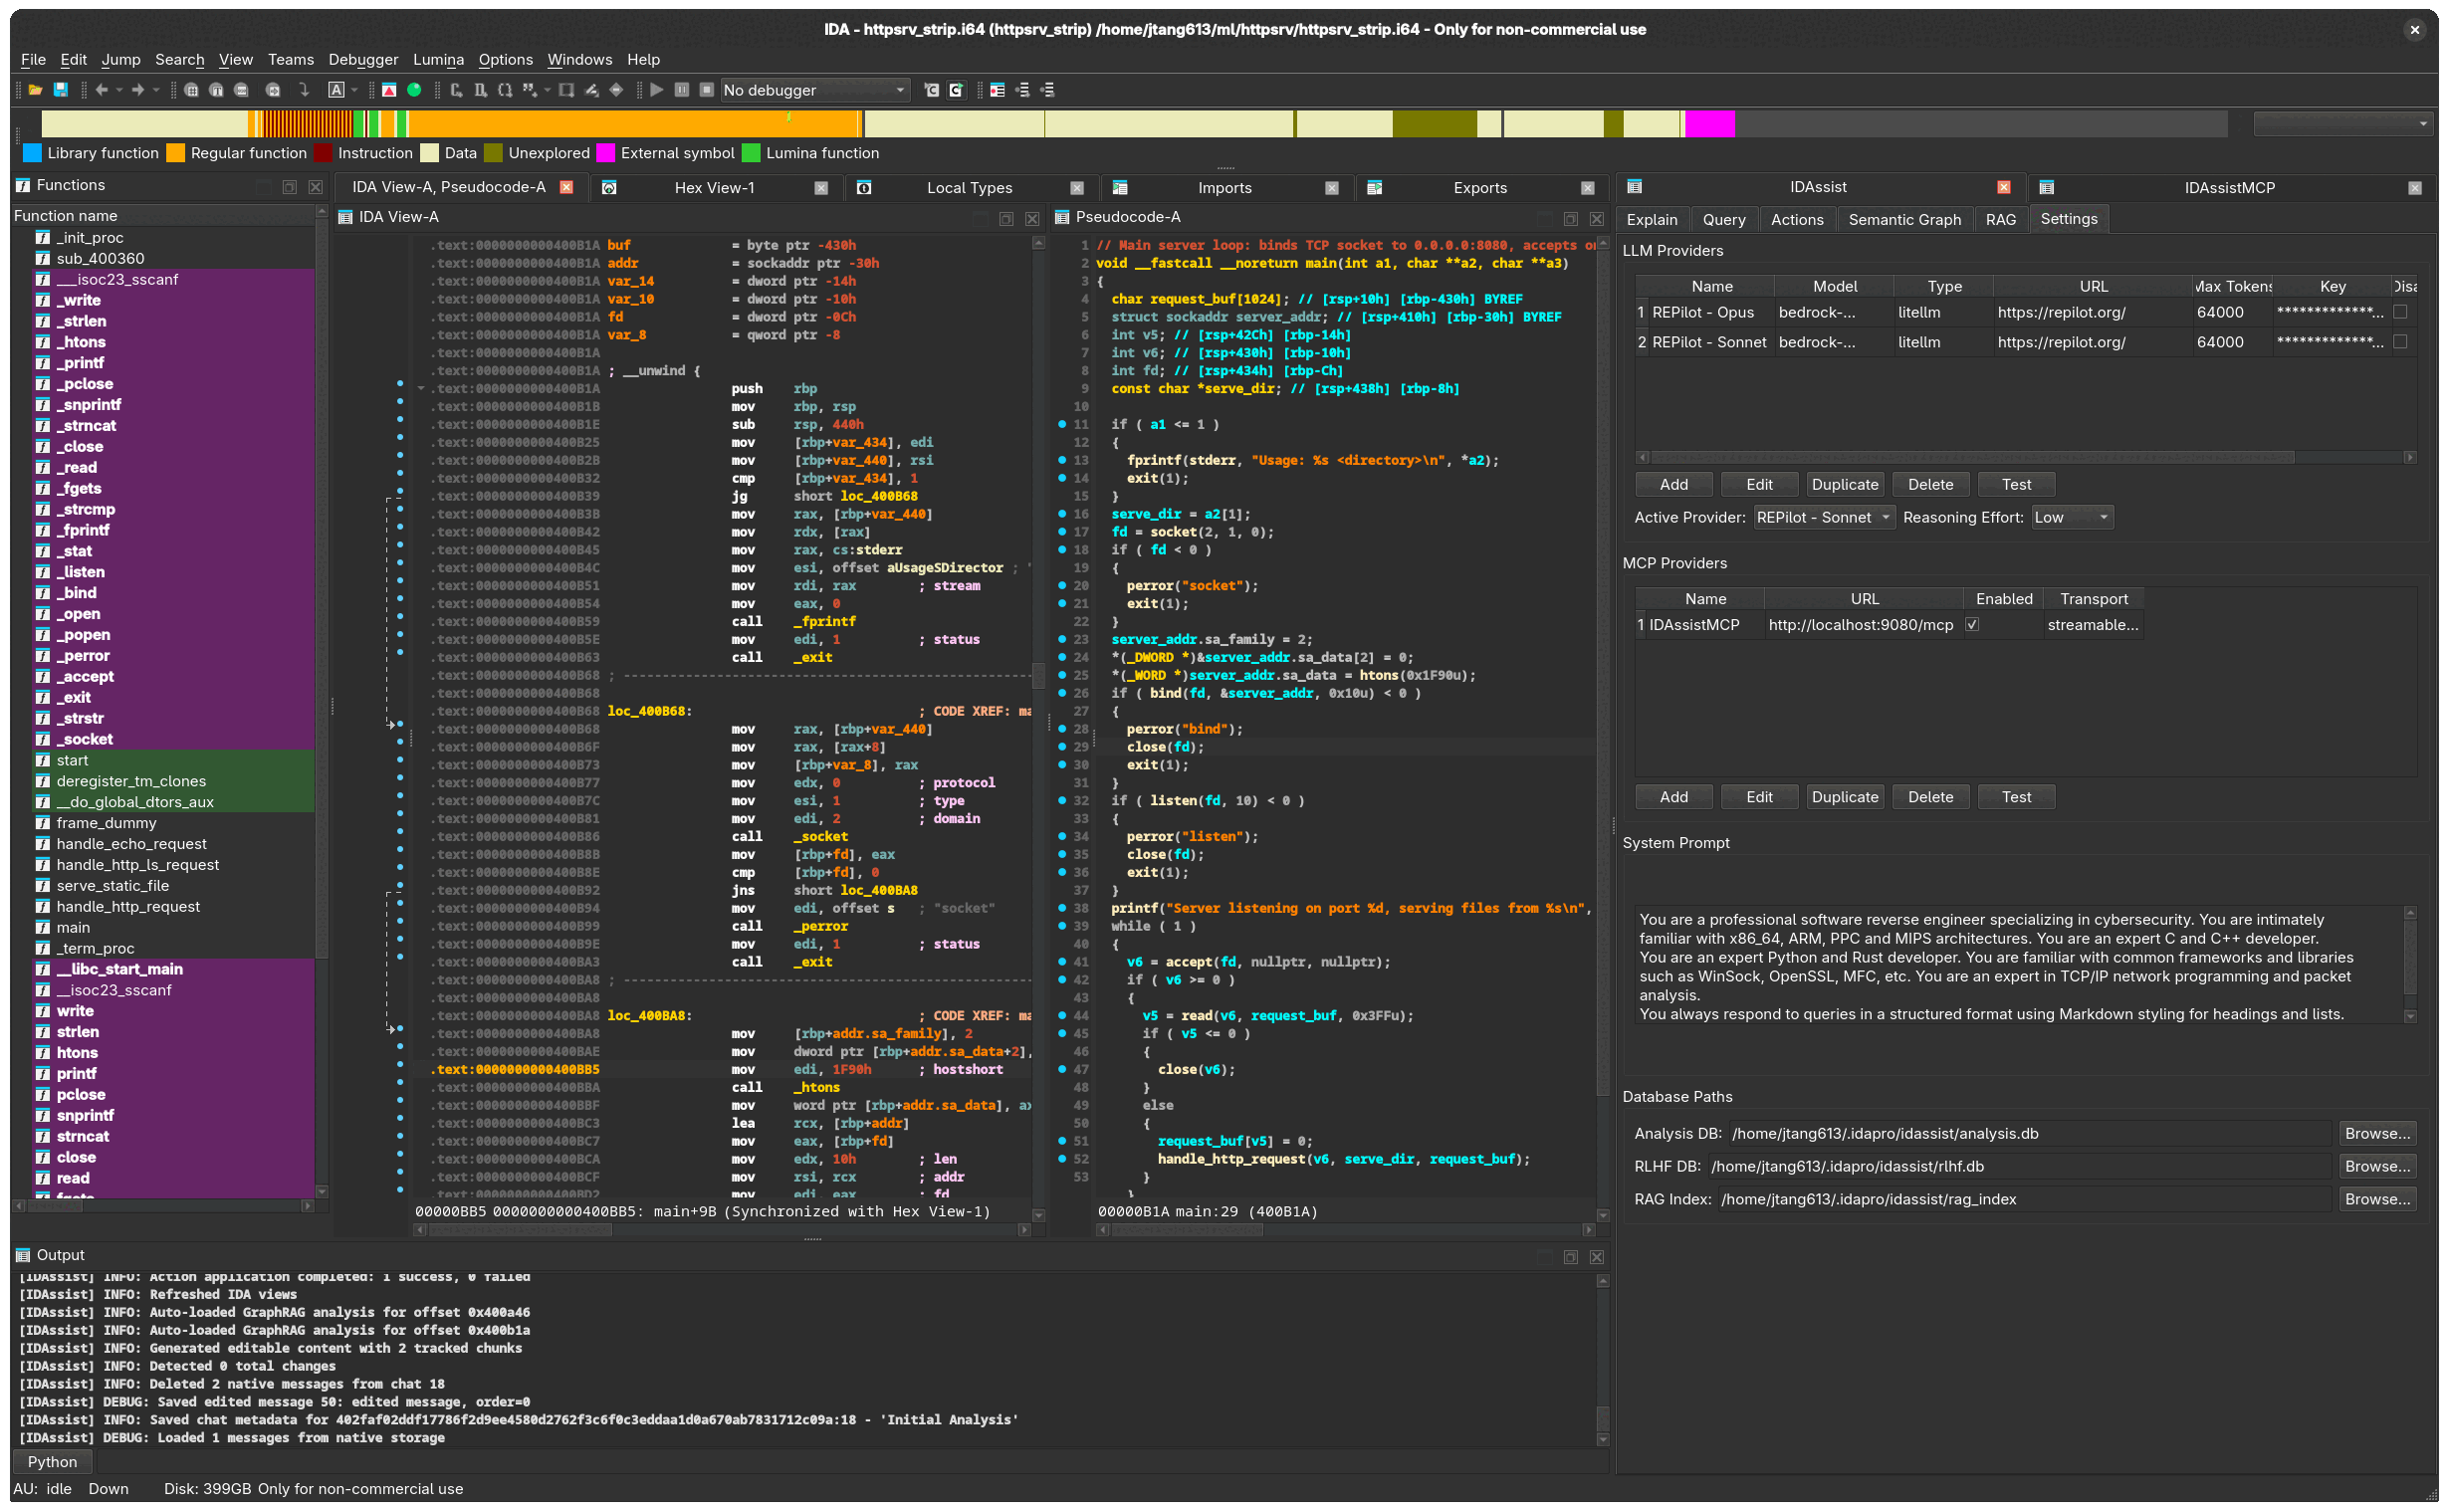 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

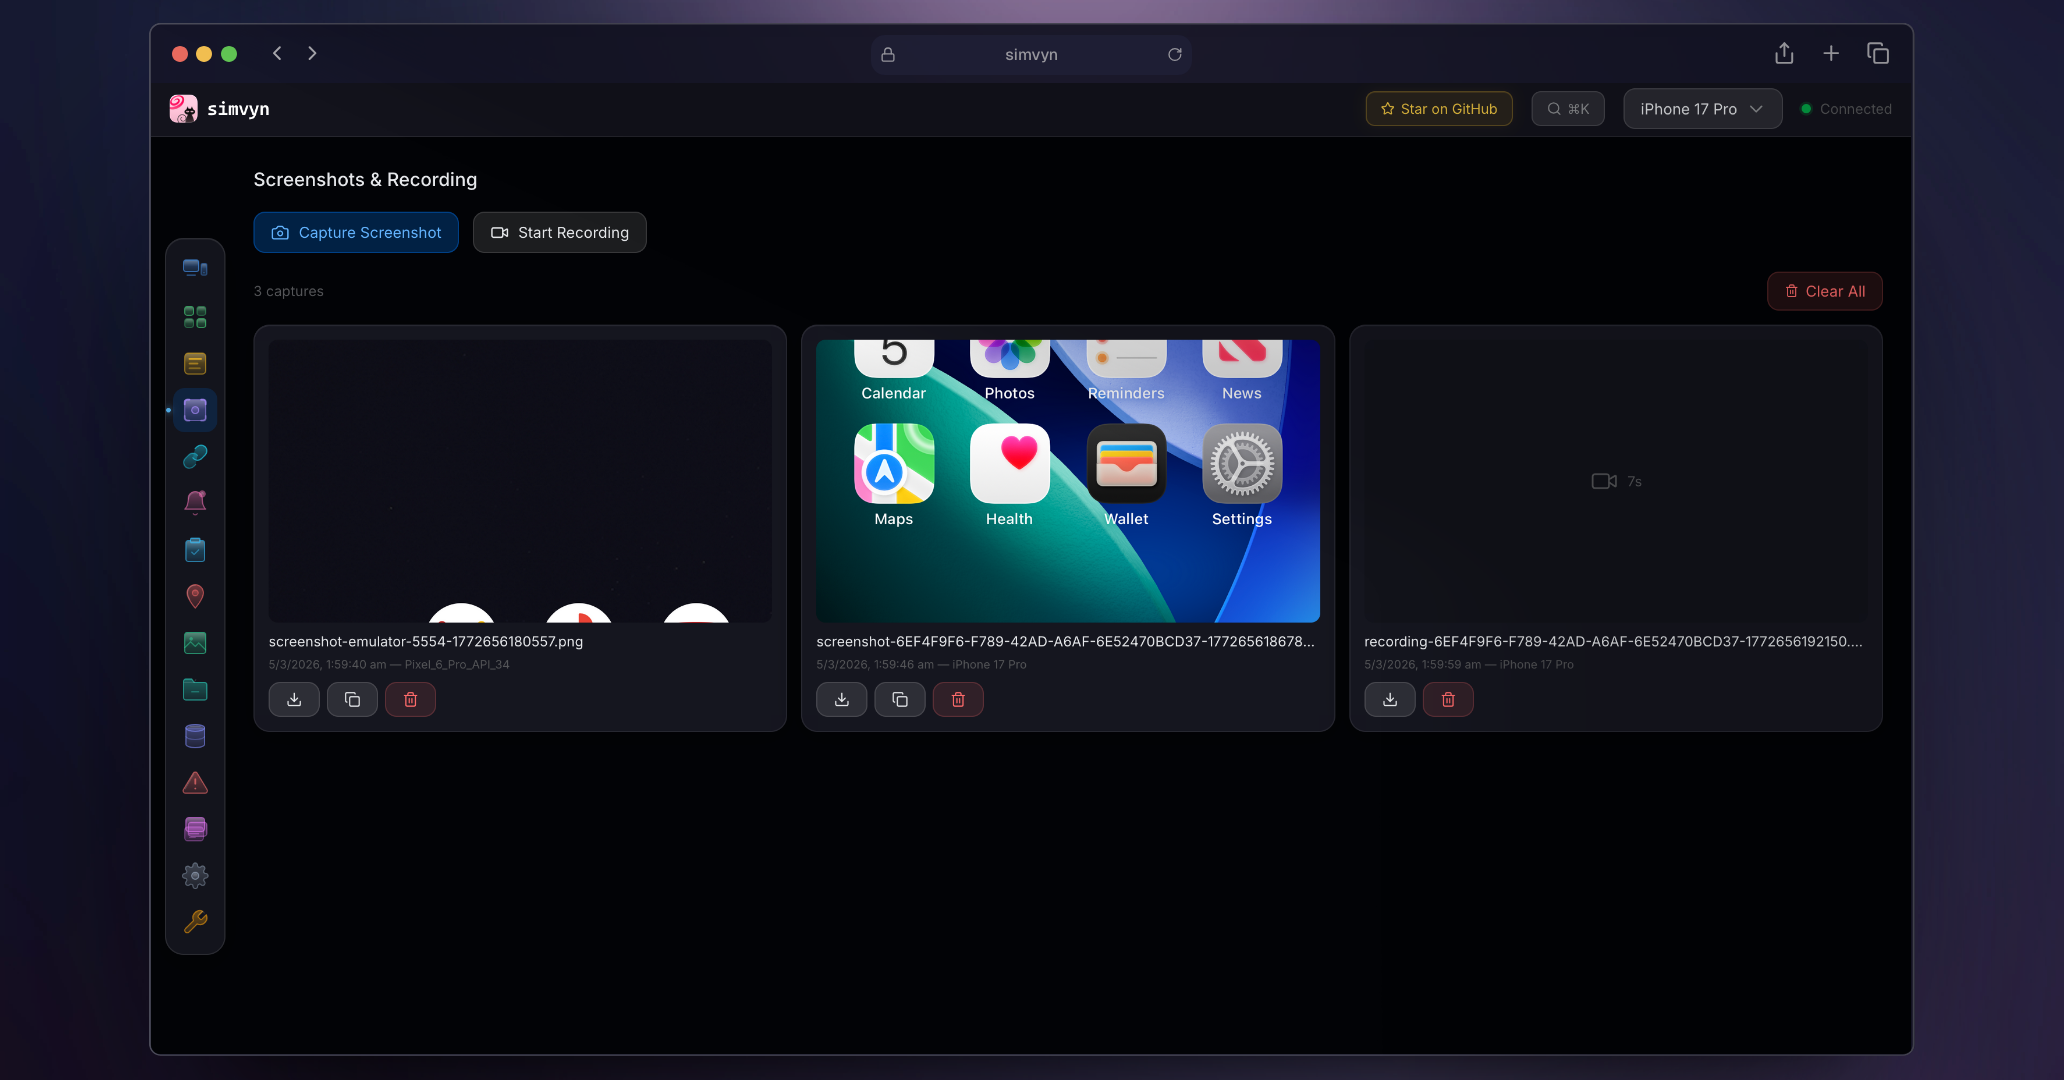 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
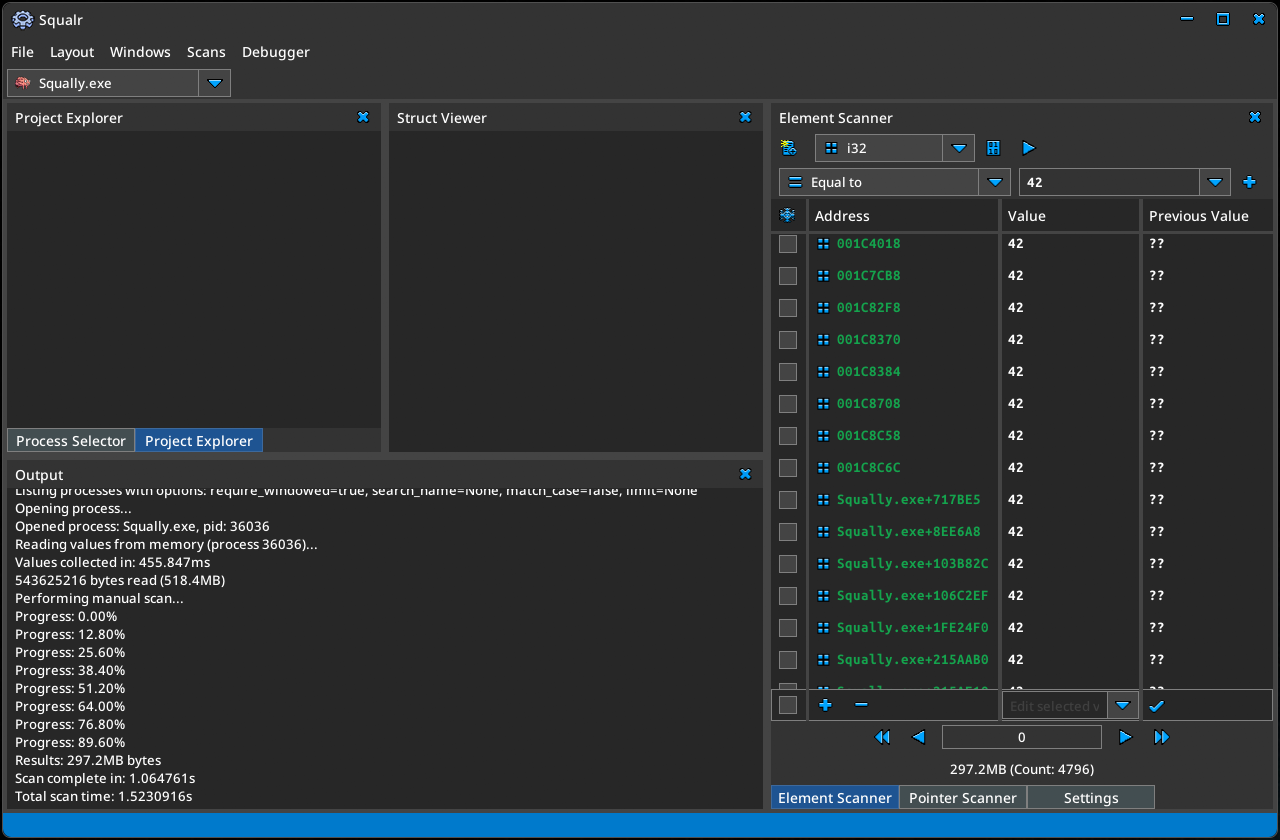 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect