
cdb
 pownjs/cdb
Automate common Chrome Debug Protocol tasks to help debug web applications from the command-line and actively monitor and intercept HTTP requests and…
debuggersnetwork-mappingpenetration-testing+2
725 years ago
pownjs/cdbAutomate common Chrome Debug Protocol tasks to help debug web applications from the command-line and actively monitor and intercept HTTP requests and…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
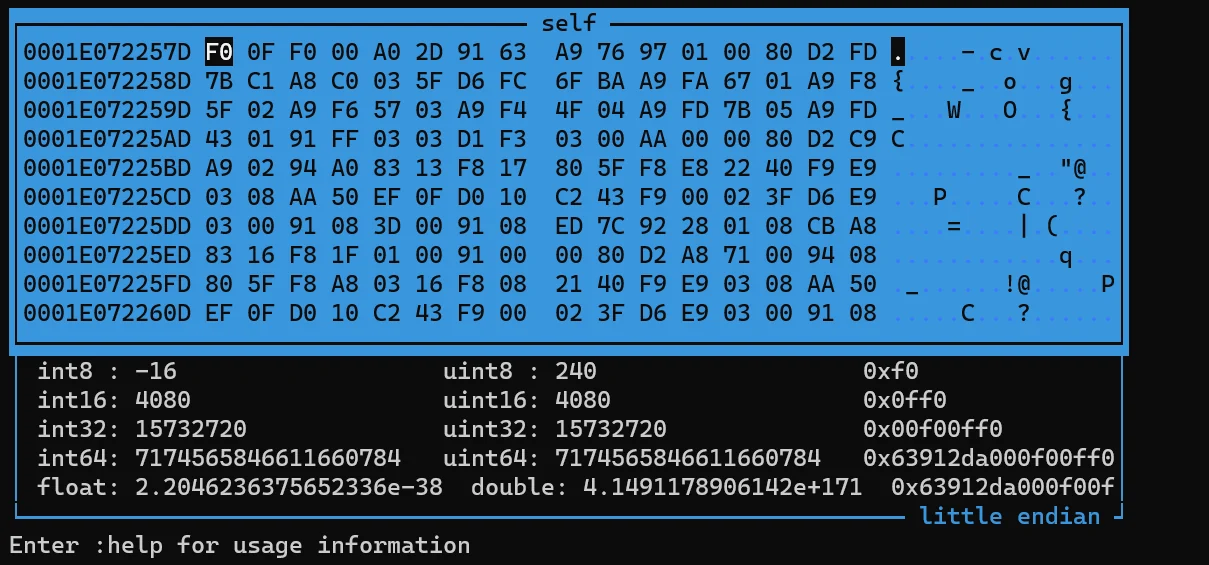 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
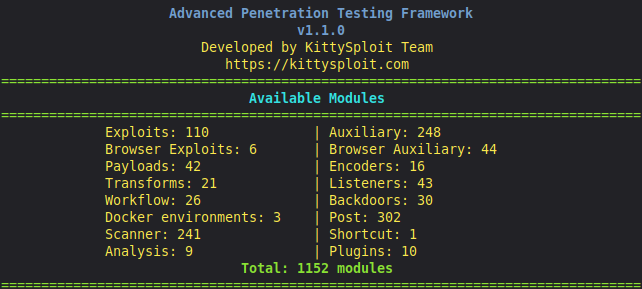 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
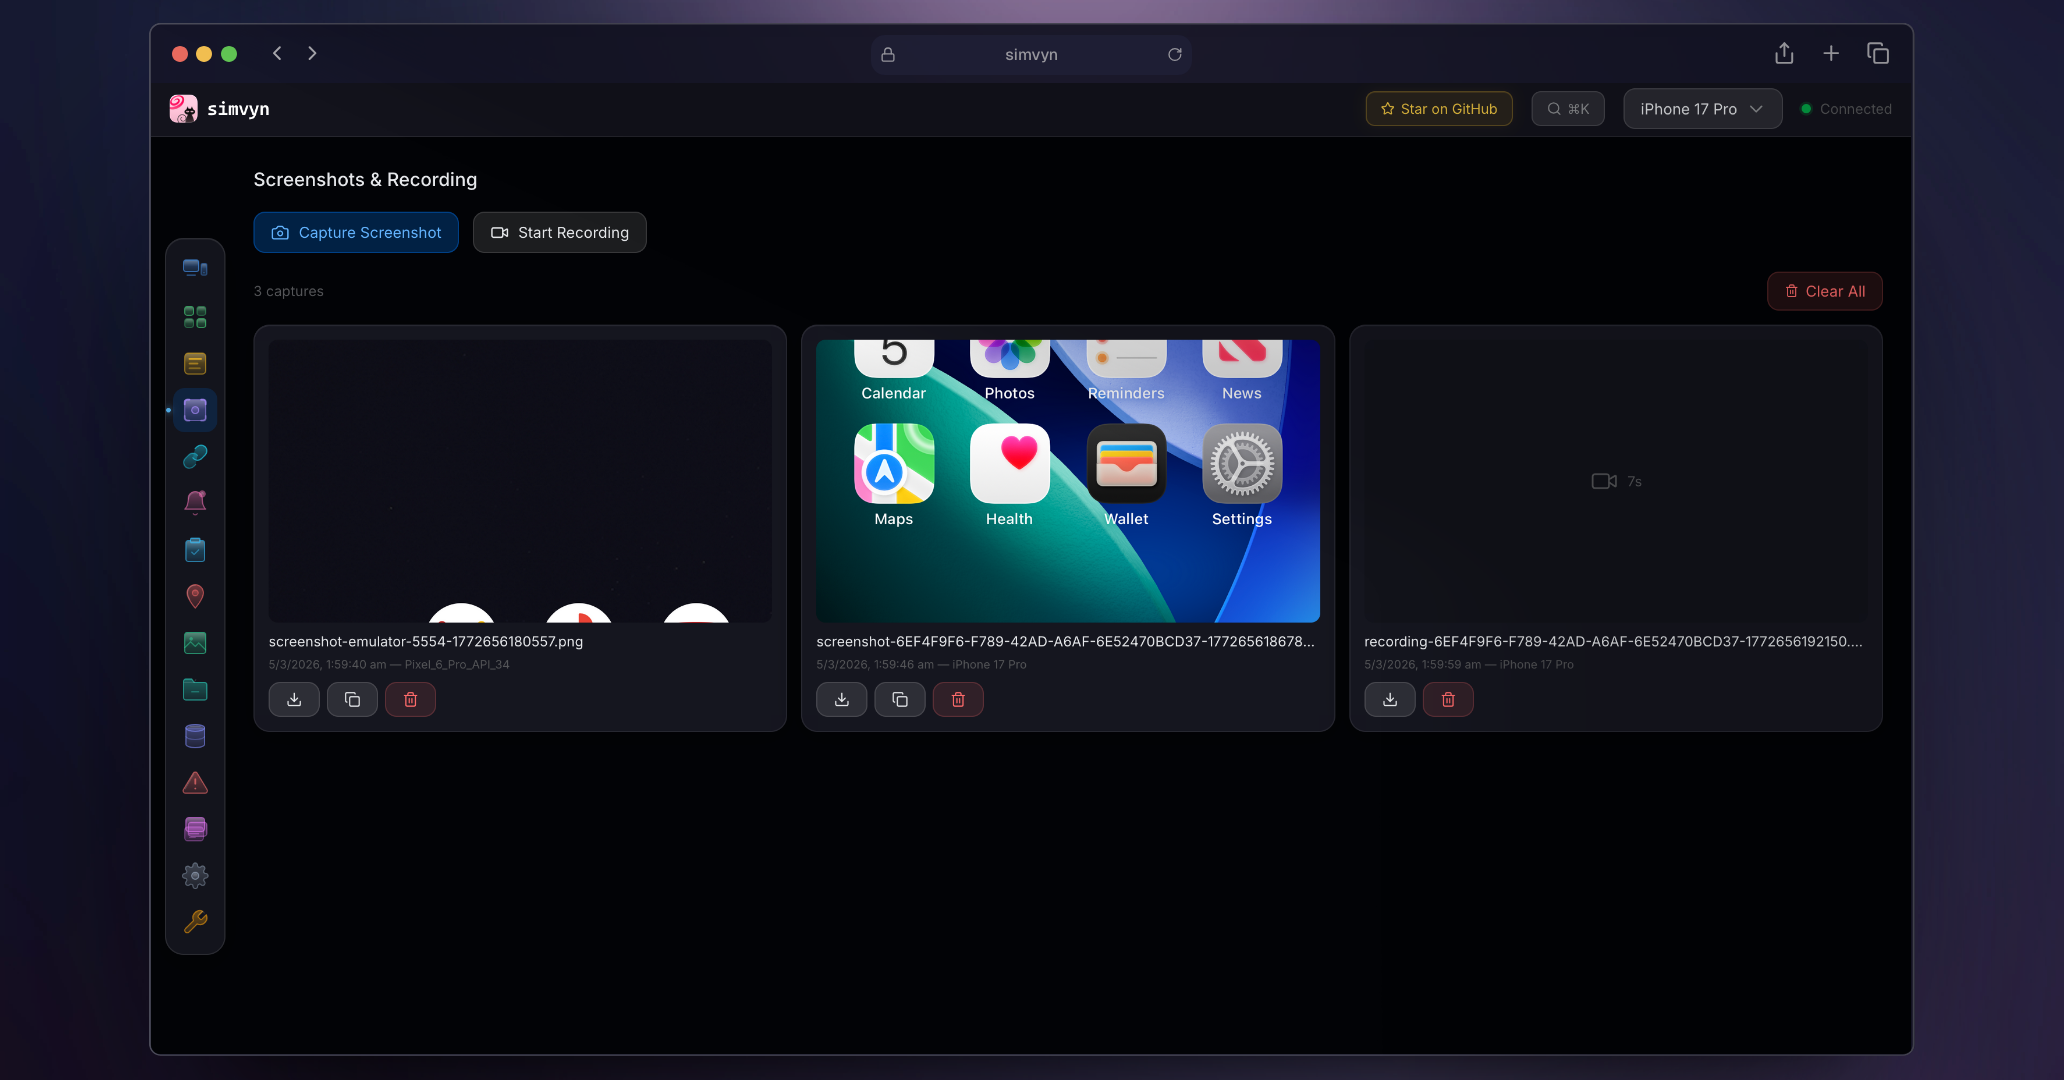 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
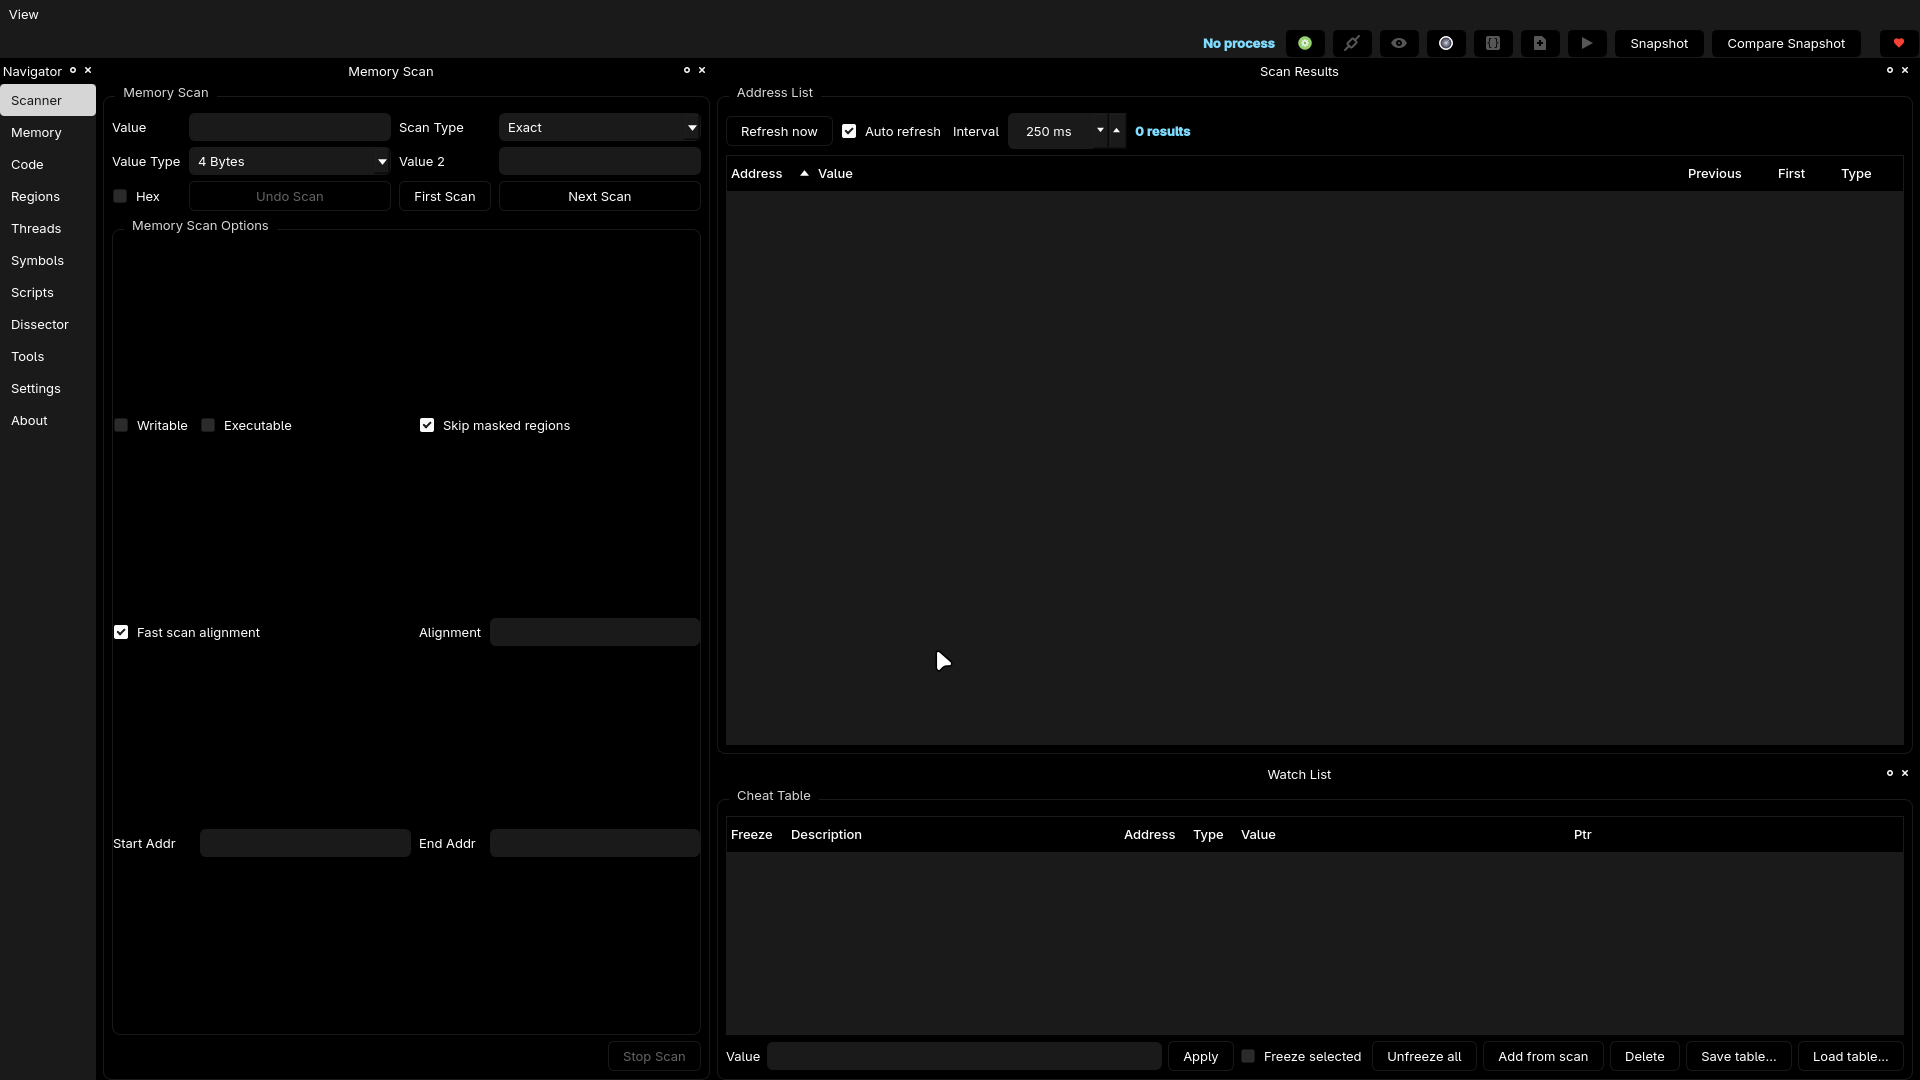 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 frida/frida
Main repo for hosting release binaries
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
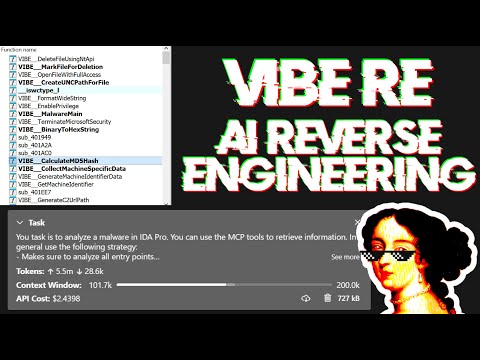 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux