
Blackbone
 darthton/blackbone
Windows memory hacking library
binary-analysisdebuggersdynamic-analysis-sandboxing+9
darthton/blackboneWindows memory hacking library
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
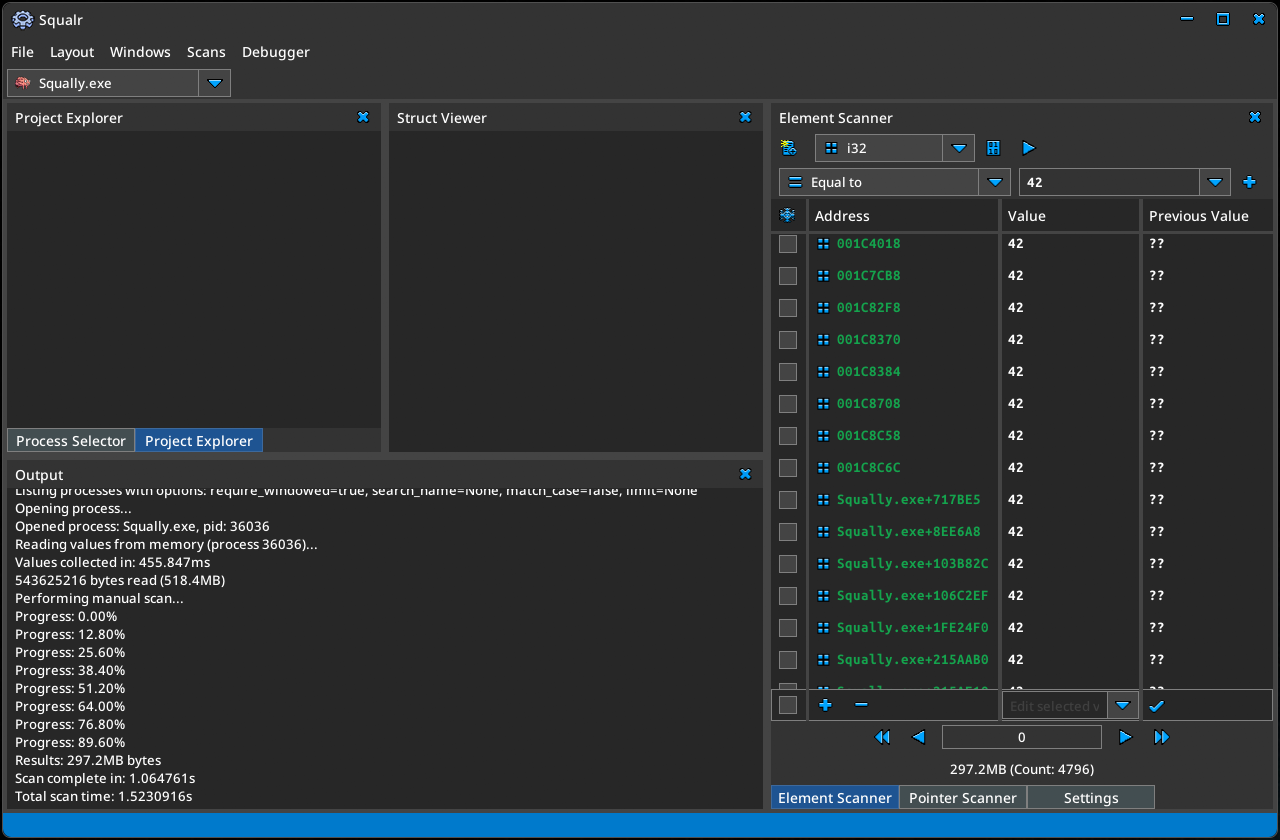 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources