
HookTools
 gmh5225/hooktools
Basic injectable for analyzing the behavior of evasive malware
binary-analysisdebuggersdefensive-tools+3
gmh5225/hooktoolsBasic injectable for analyzing the behavior of evasive malware
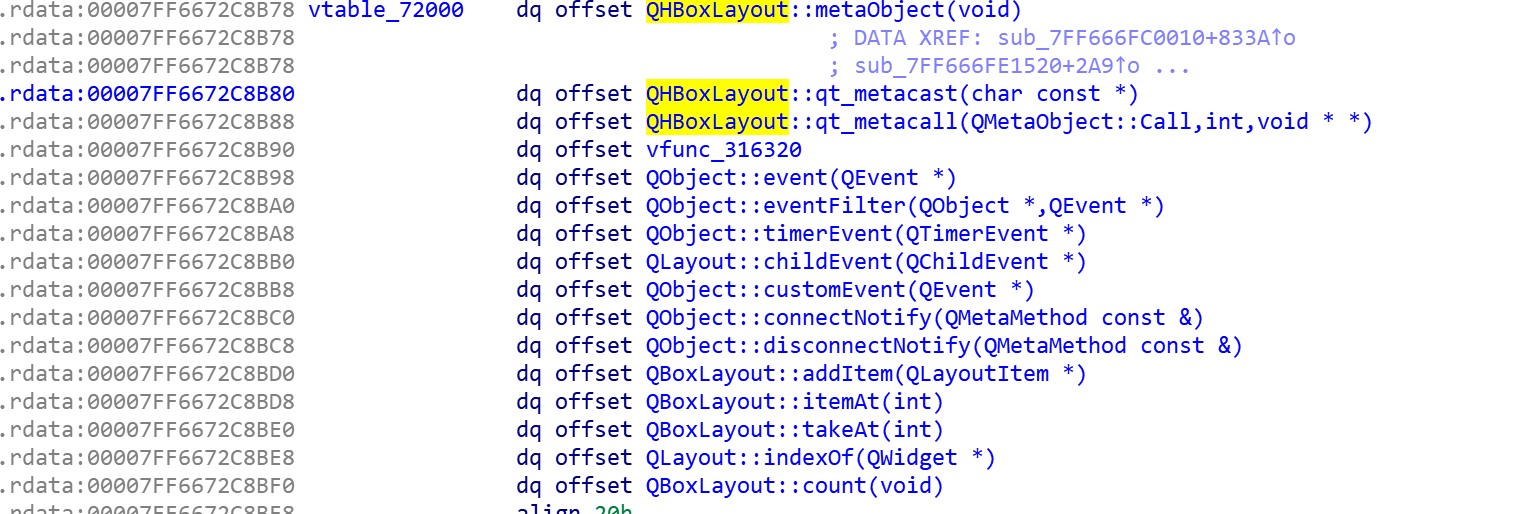 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.

 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
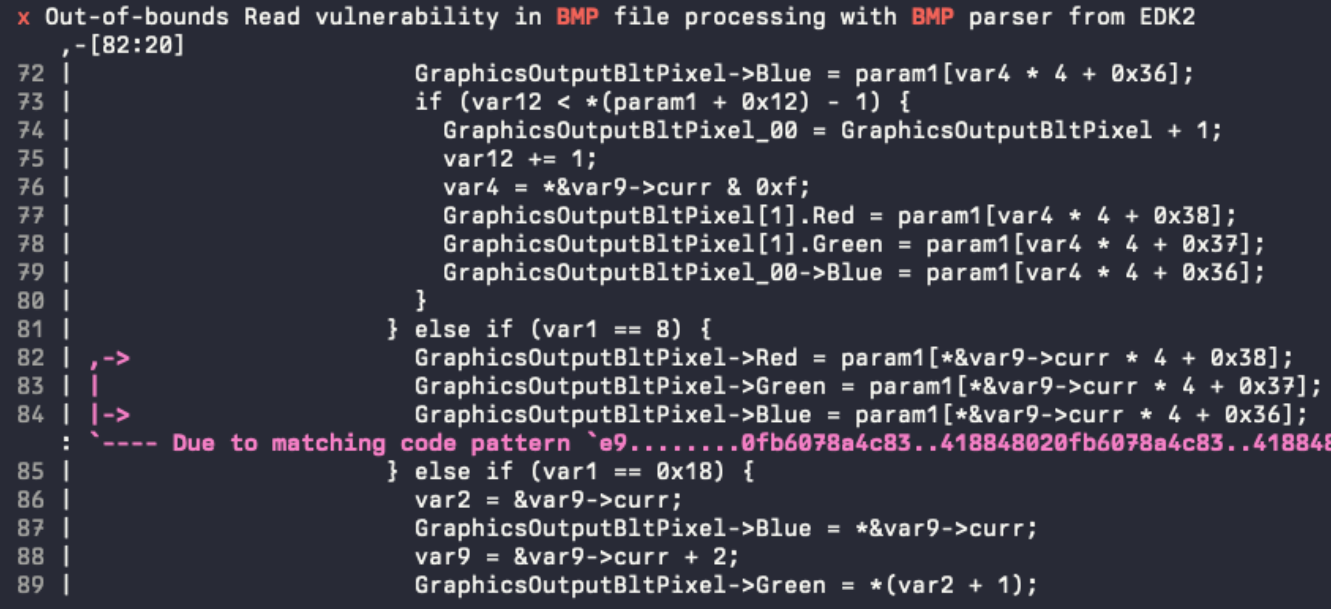 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
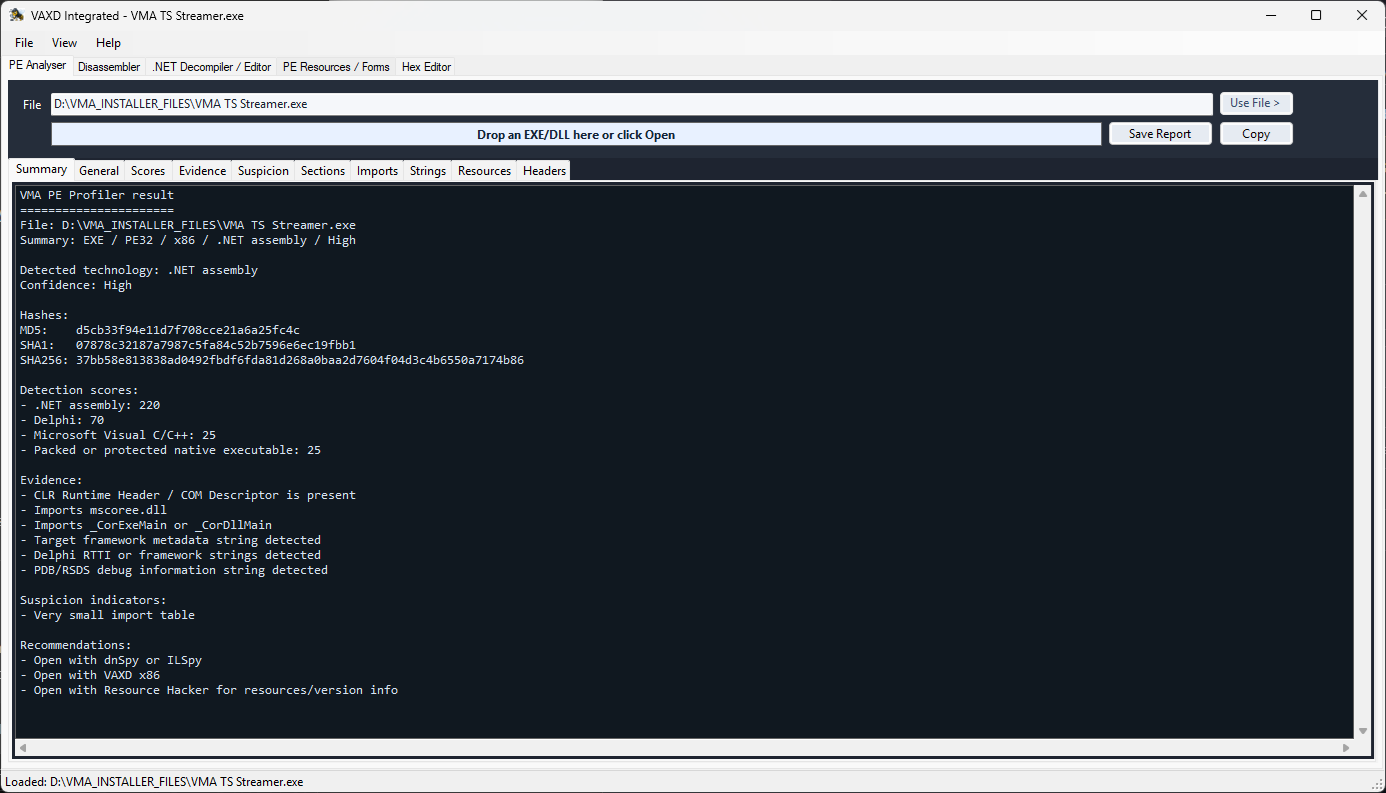 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 guardicore/ipcdump
BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…
 madmin3r/unconfuserex
Deobfuscator for ConfuserEx 2.
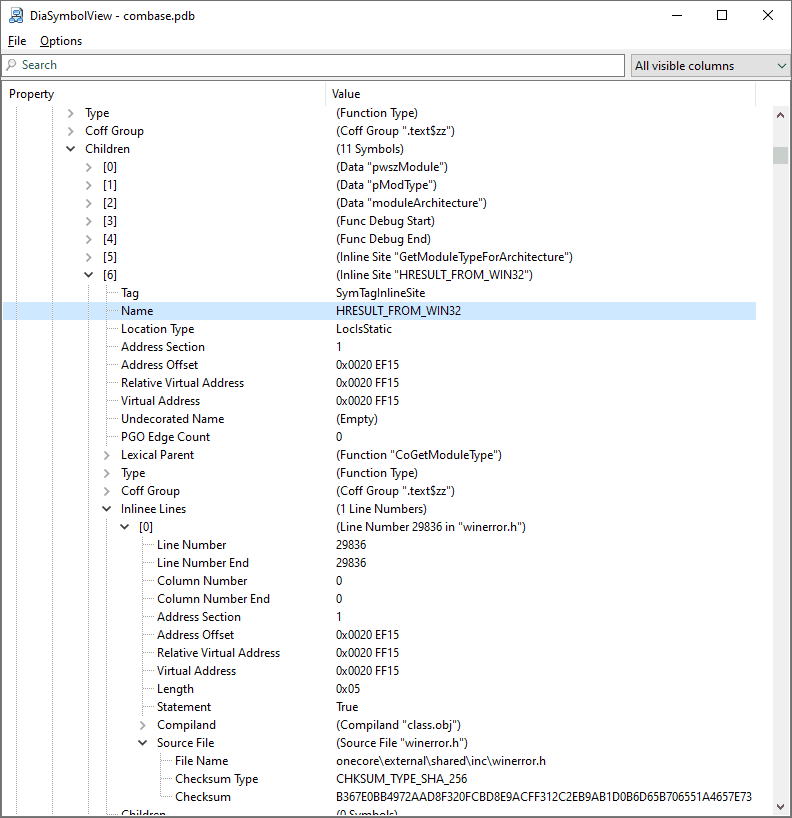 diversenok/diasymbolview
PDB file inspection tool
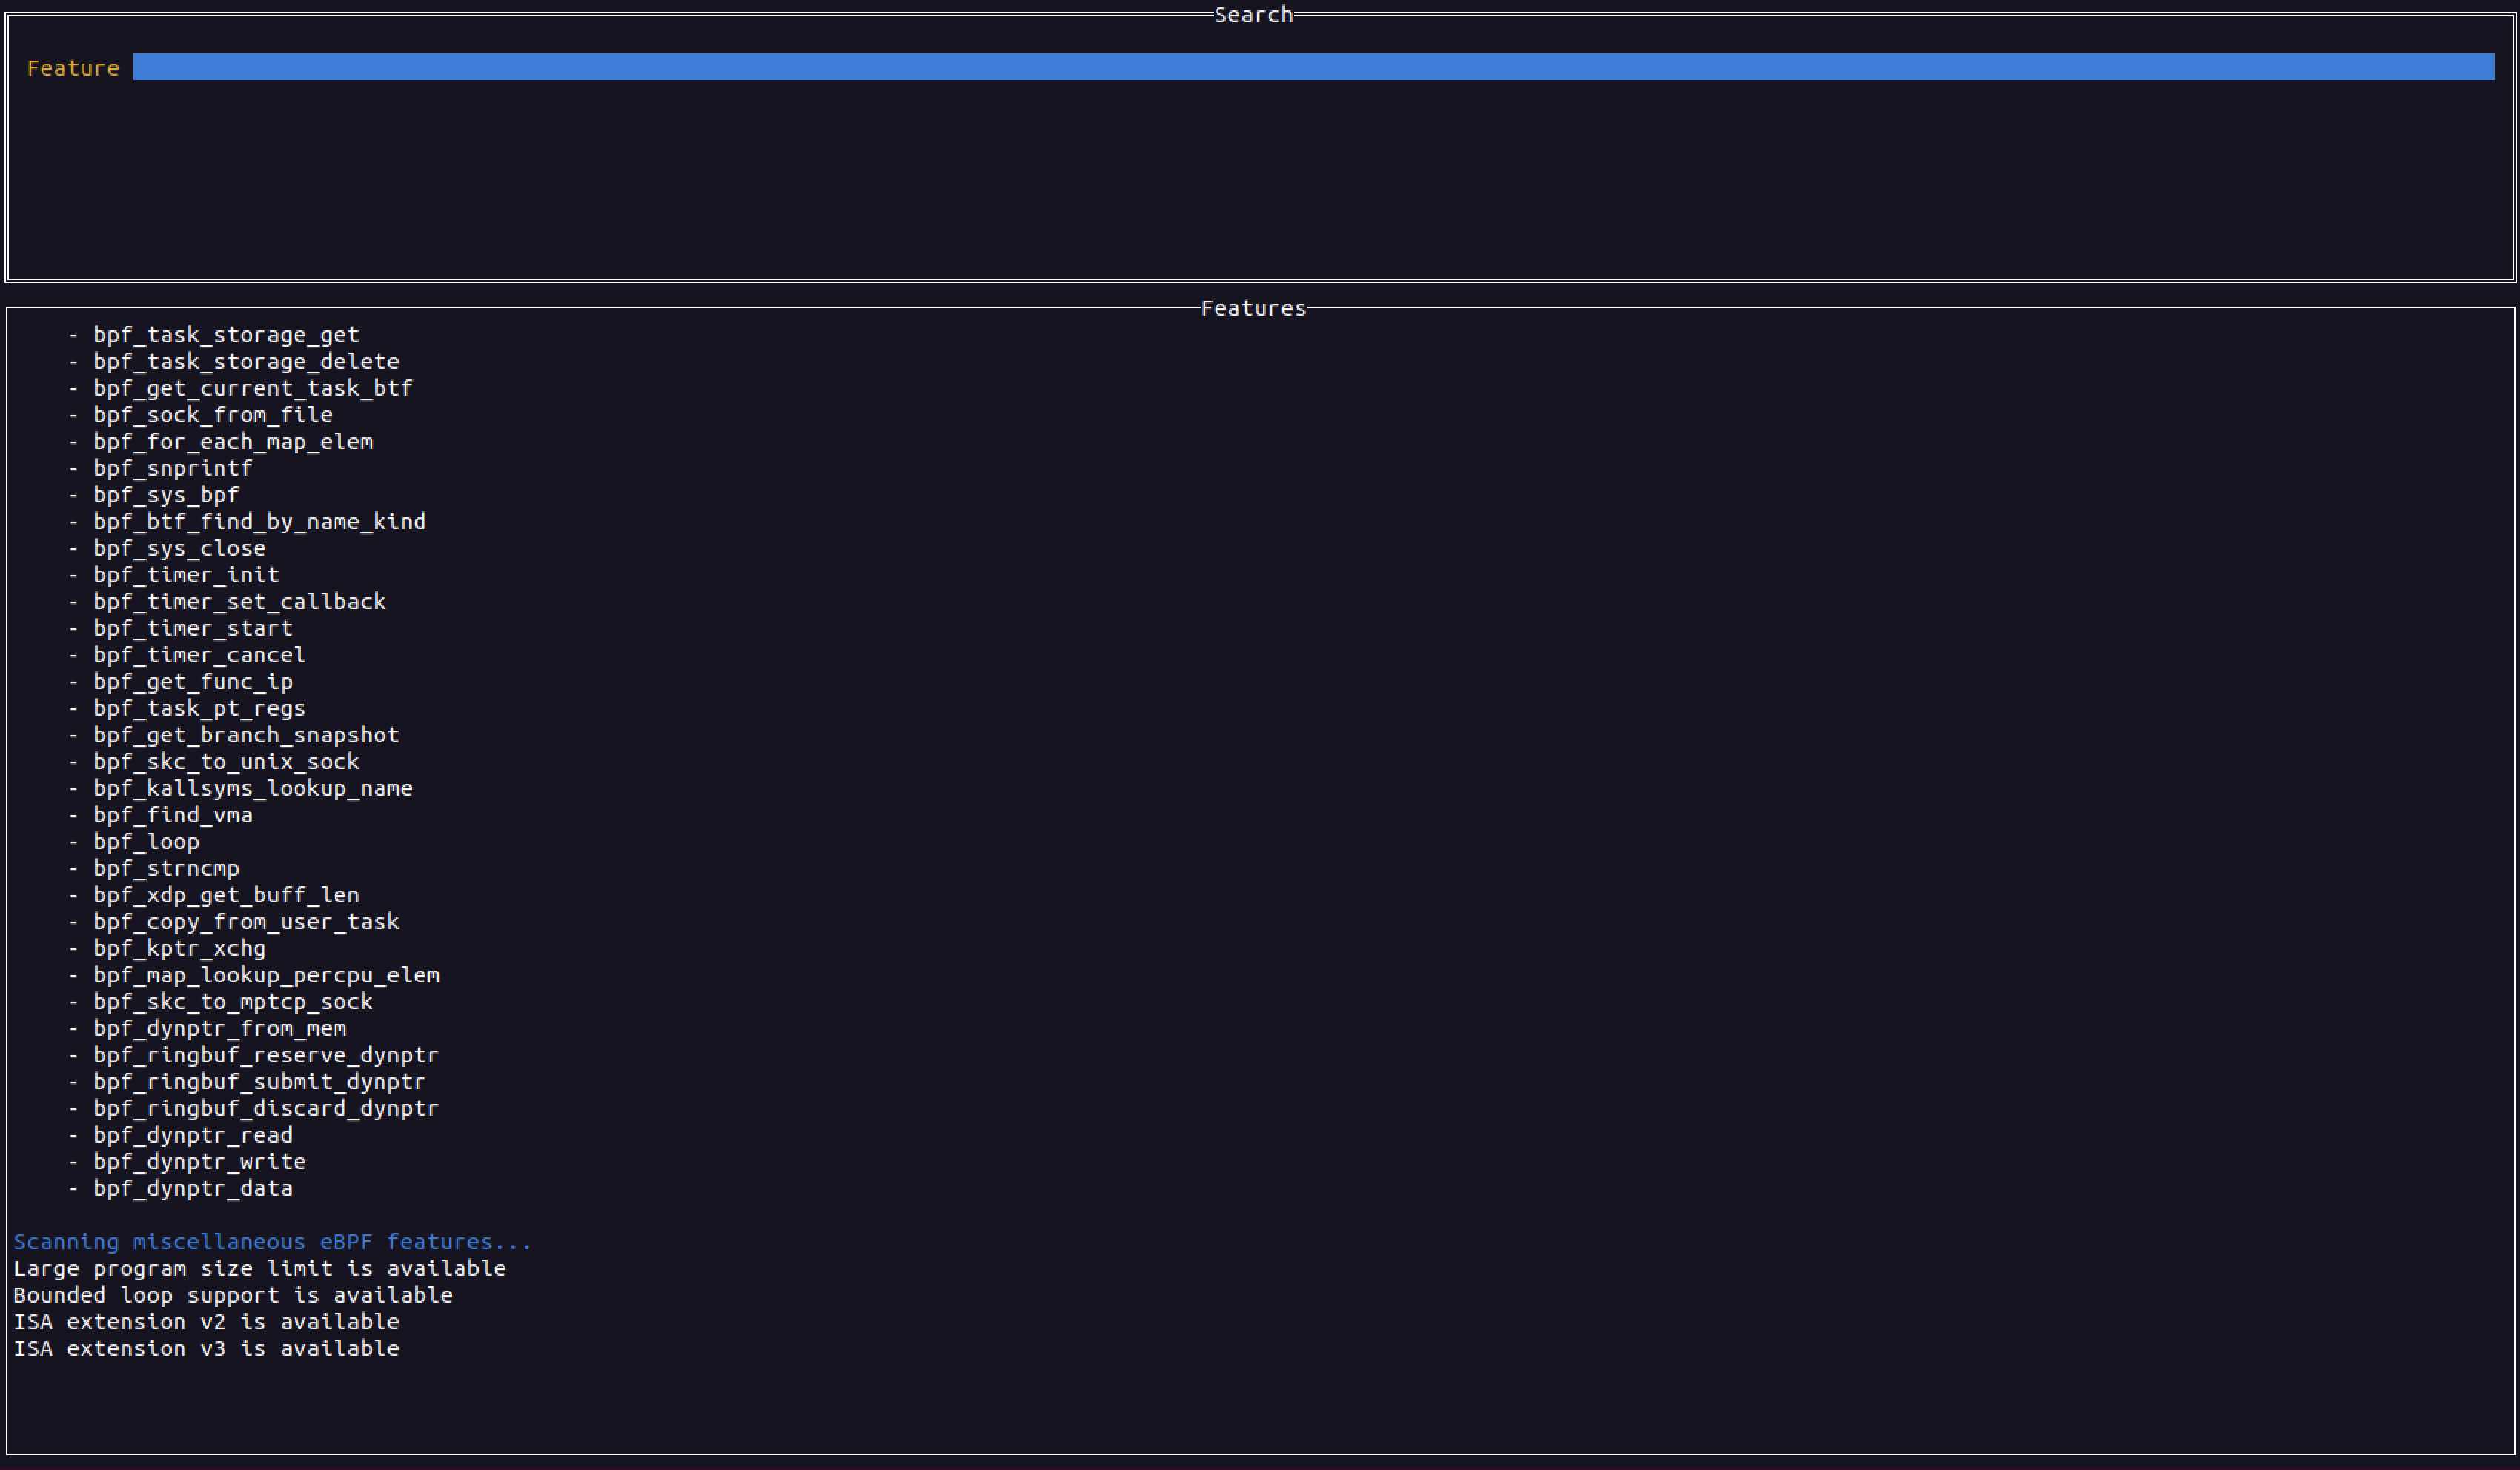 redcanaryco/ebpfmon
Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…