

CVE-2023-25136
 business1sg00d/cve-2023-25136
Looking into the memory when sshd 9.1p1 aborts due to a double free bug.
binary-analysisdebuggersexploitation+2
1
business1sg00d/cve-2023-25136Looking into the memory when sshd 9.1p1 aborts due to a double free bug.
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 smarttfoxx/cve-2025-65320
Demonstrates cleartext storage of license keys in memory in Abacre Restaurant POS, enabling license activation bypass via debugger and memory dump…
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
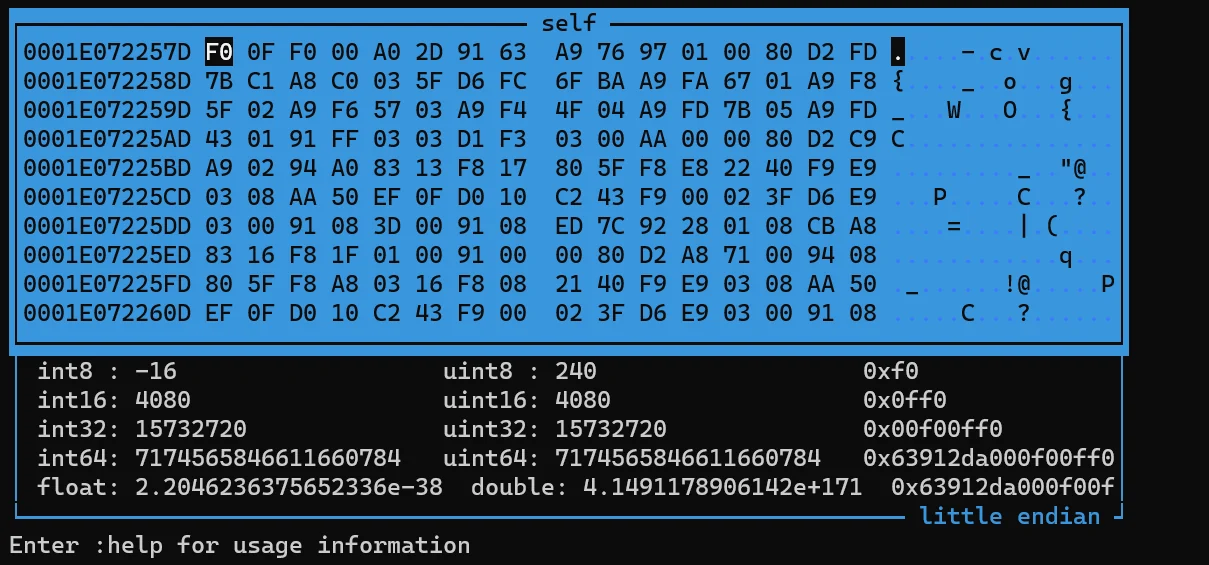 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 nidhihcl/linux-4.19.72_cve-2022-29581
Linux kernel 4.19.72 with a targeted patch or exploit for CVE-2022-29581, demonstrating a specific kernel vulnerability for security research and…
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.
 shaikusaf/linux-4.19.72_cve-2020-14356
Linux kernel source tree modified for CVE-2020-14356, providing a reference for vulnerability analysis and exploitation research.
 shaikusaf/linux-4.19.72_cve-2020-10757
Linux kernel source tree modified to demonstrate CVE-2020-10757, a use-after-free vulnerability in the AF_PACKET socket, for educational and research…
 day6reak/cve-2014-4140
Technical notes and debugger analysis for CVE-2014-4140, a use-after-free vulnerability in MSHTML's CHtmRootParseCtx::AddText leading to remote code…
 day6reak/cve-2014-1773
Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…

 beraphin/cve-2017-16943
Technical analysis and proof-of-concept for CVE-2017-16943, a use-after-free in Exim's receive_msg function, demonstrating heap manipulation and RIP…
 renukaselvar/libunwind_cve-2015-3239
C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…
 renukaselvar/libunwind_cve-2015-3239_after
Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…