

lisa.py
 ant4g0nist/lisa.py
LLDB MCP Integration + other helpful commands
ai-assisted-reversingbinary-analysisdebuggers+2
7561 year ago
ant4g0nist/lisa.pyLLDB MCP Integration + other helpful commands
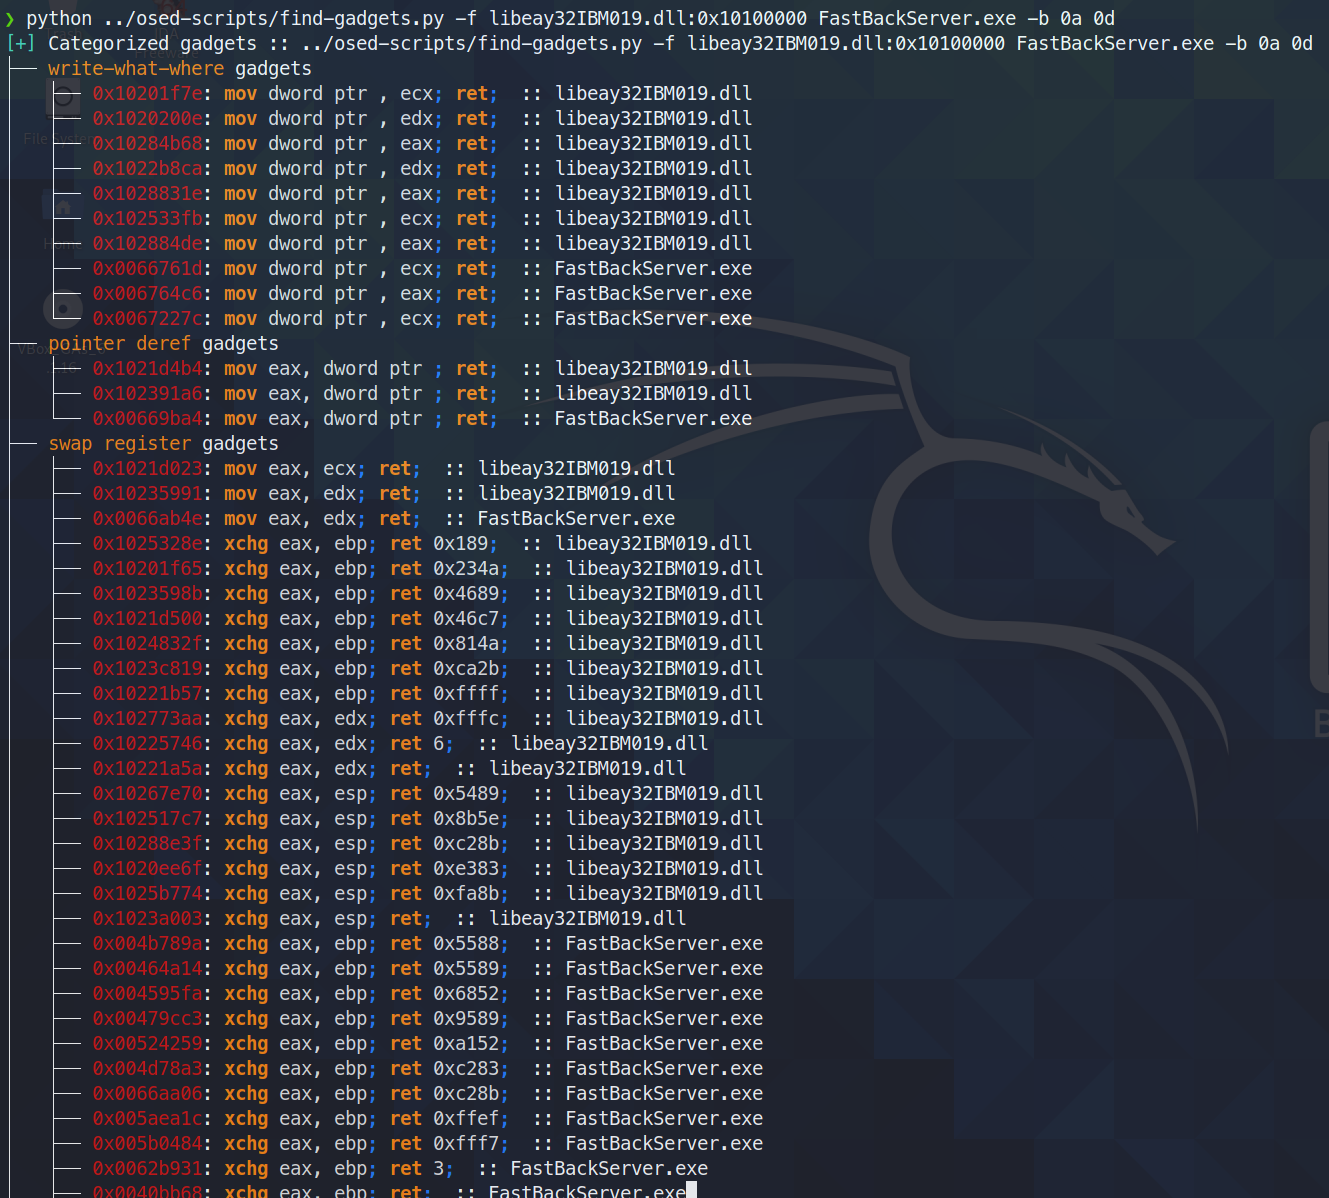 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 nccgroup/libptmalloc
Heap analysis tooling for ptmalloc
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 das-labor/panopticon
A libre cross-platform disassembler.
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
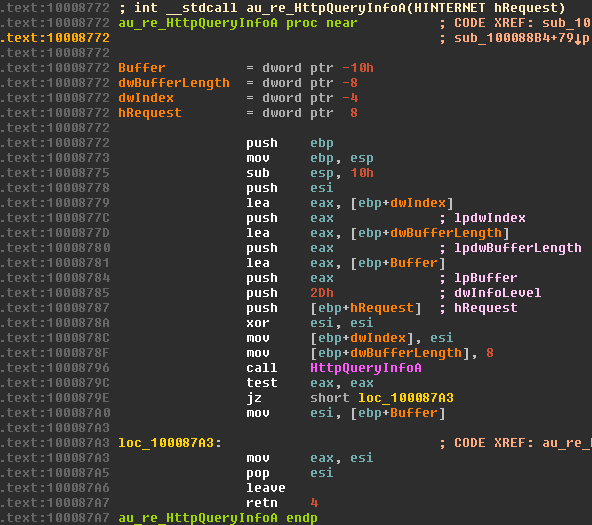 a1ext/auto_re
IDA PRO auto-renaming plugin with tagging support
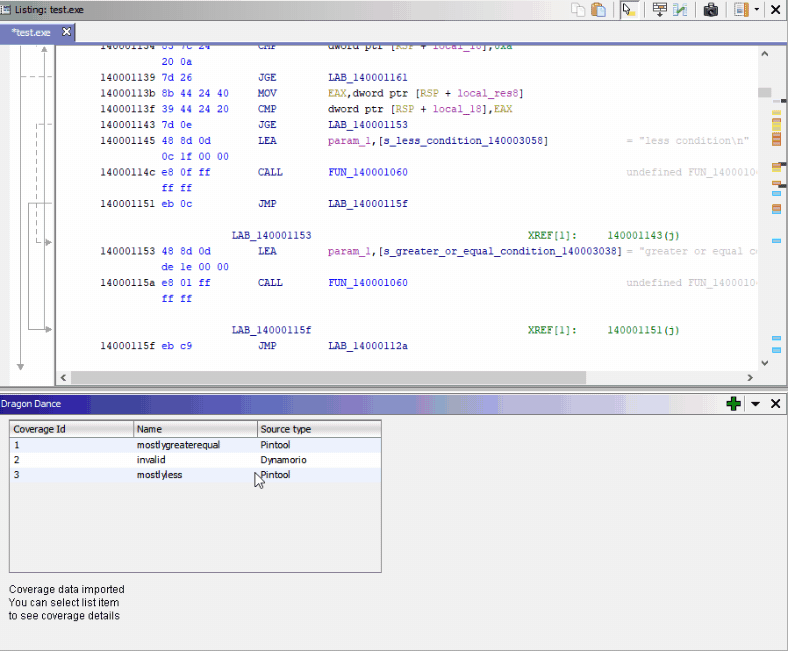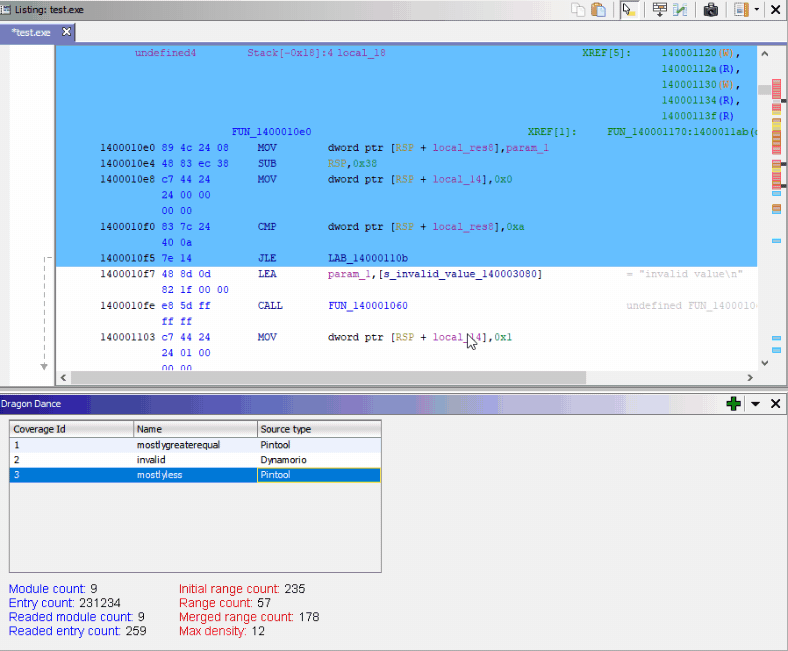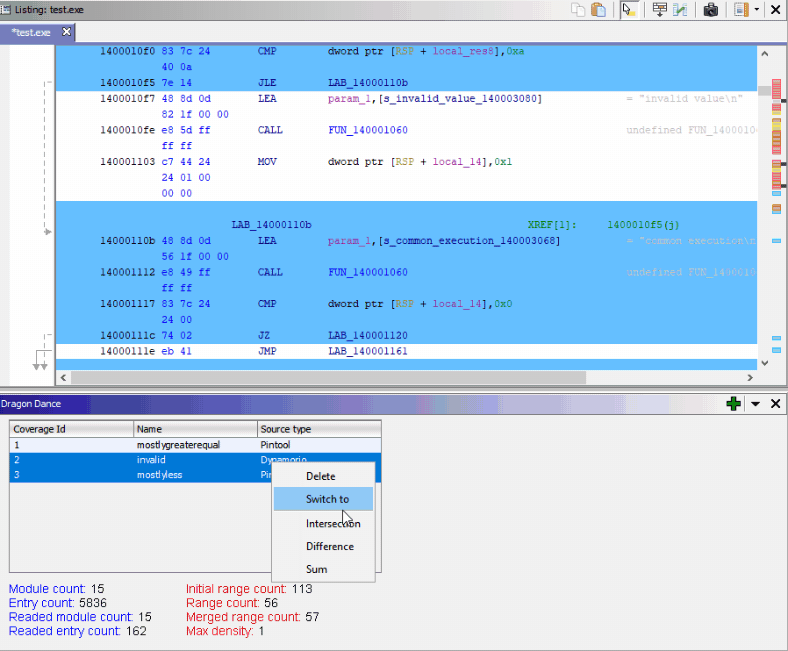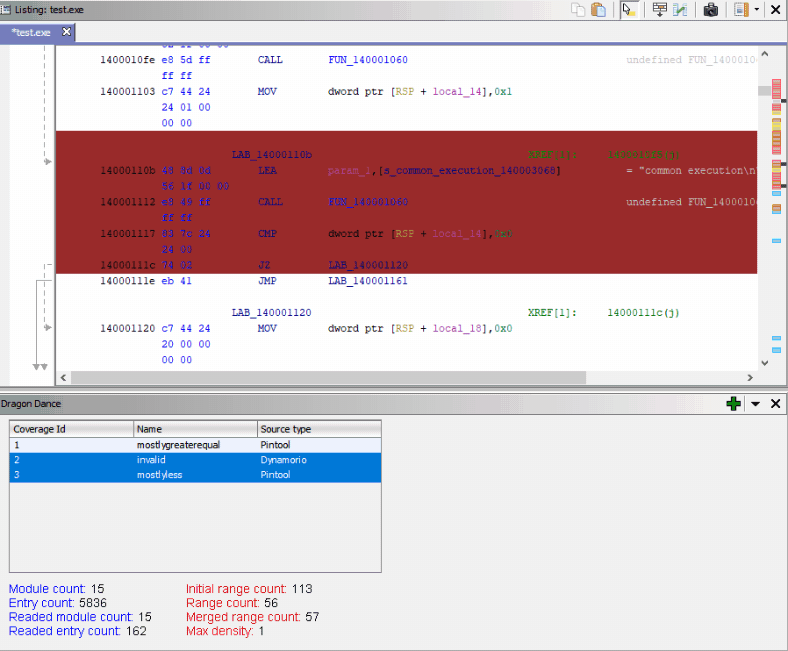 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
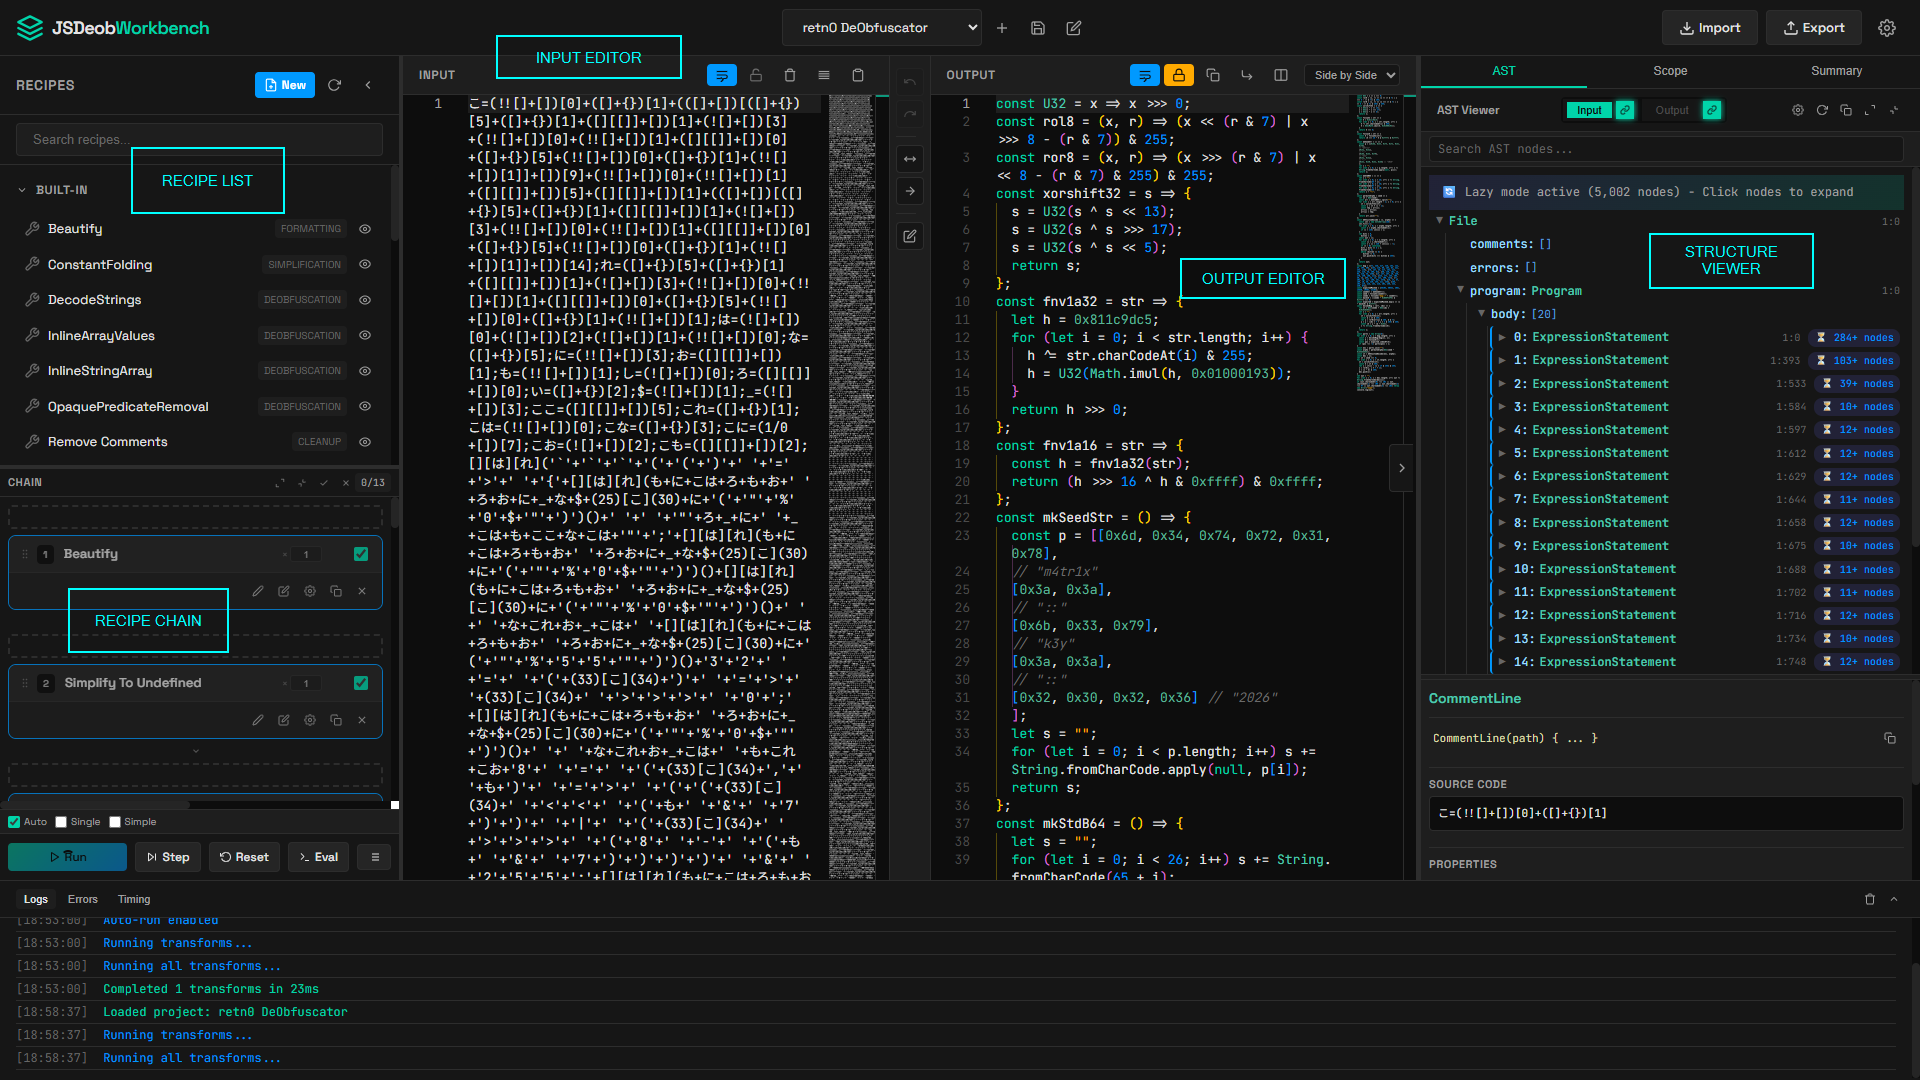 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 idarlingteam/idarling
Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 secrary/idenlib
idenLib - Library Function Identification [This project is not maintained anymore]