gemma_crackme_tutorial

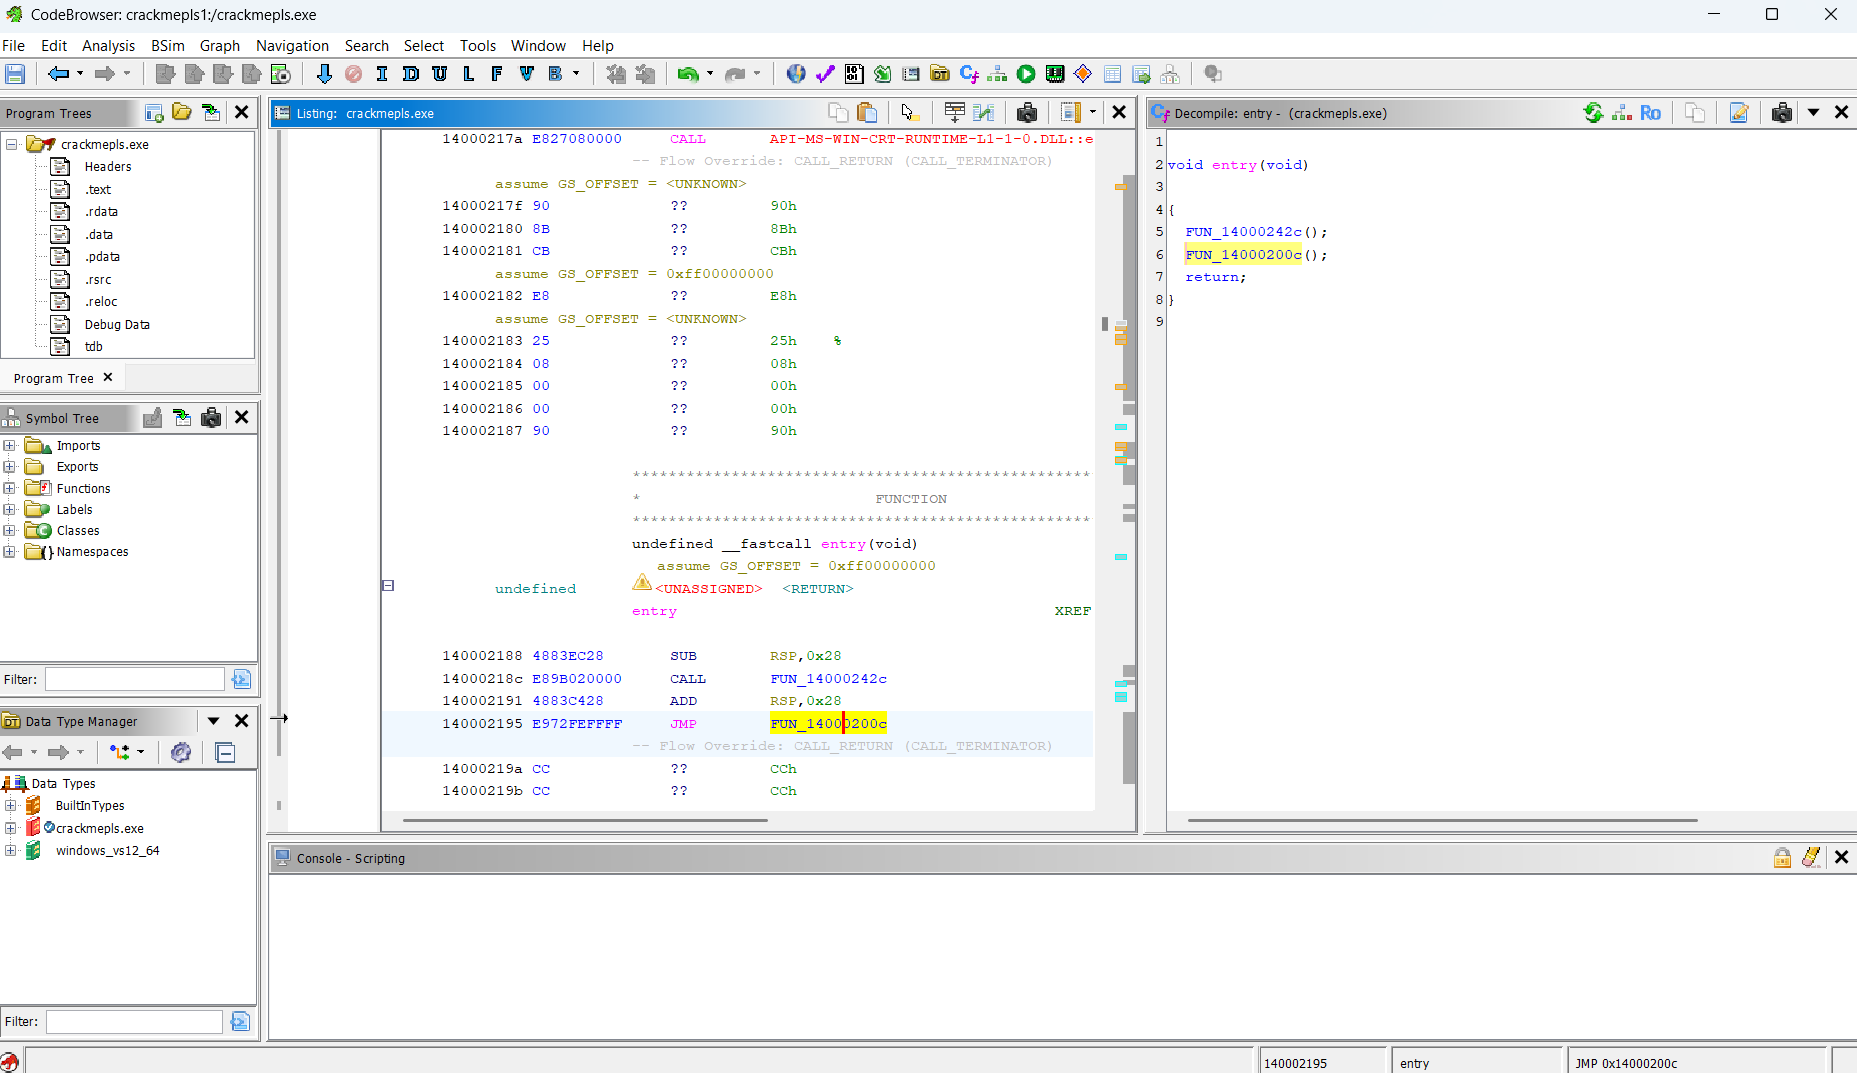
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…

Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…

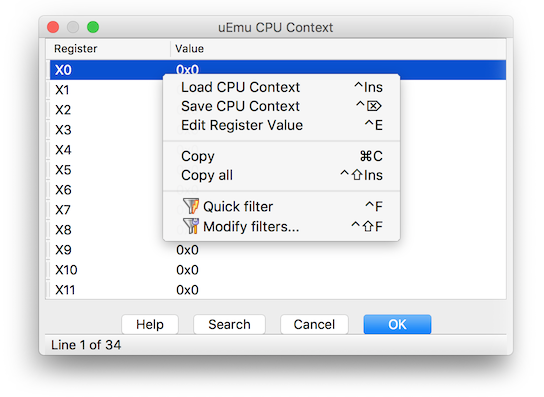
Tiny cute emulator plugin for IDA based on unicorn.

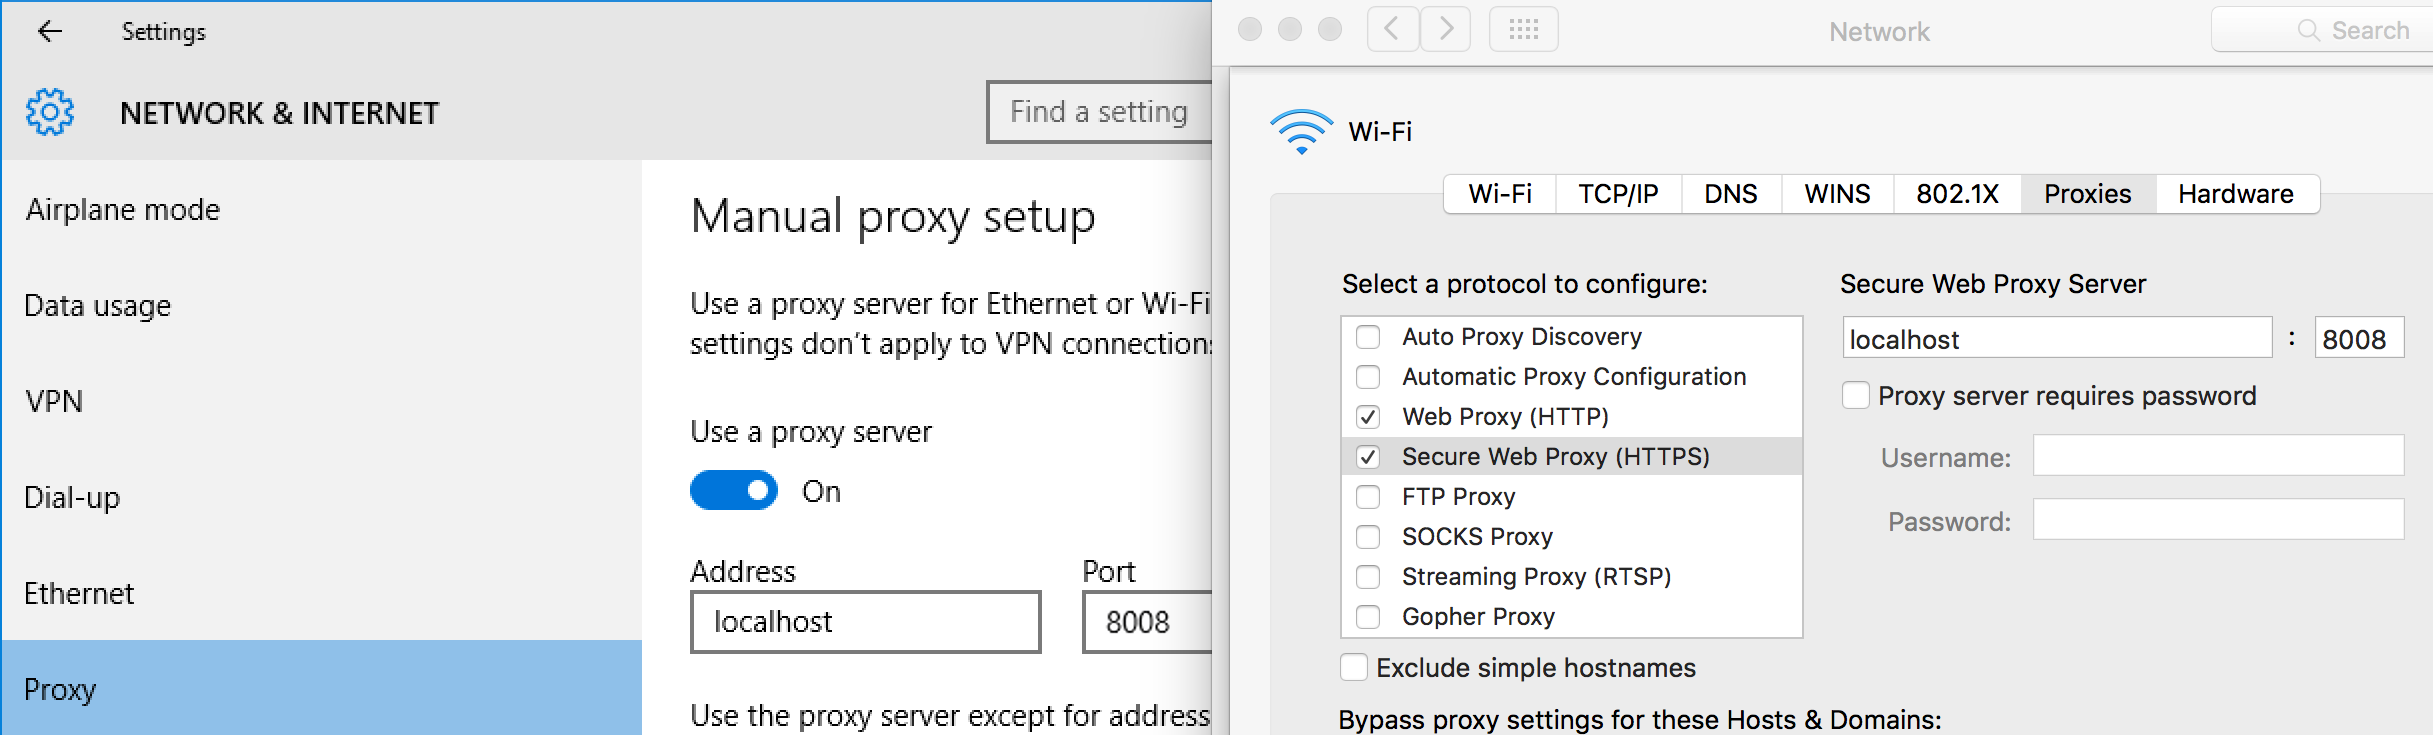
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.

A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.

IDA Pro plugin to examine the glibc heap, focused on exploit development

Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)

Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…

Proof-of-concept for CVE-2022-31902, a denial-of-service vulnerability in Notepad++ (x86) triggered by the Find All feature on crafted text files,…

Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)

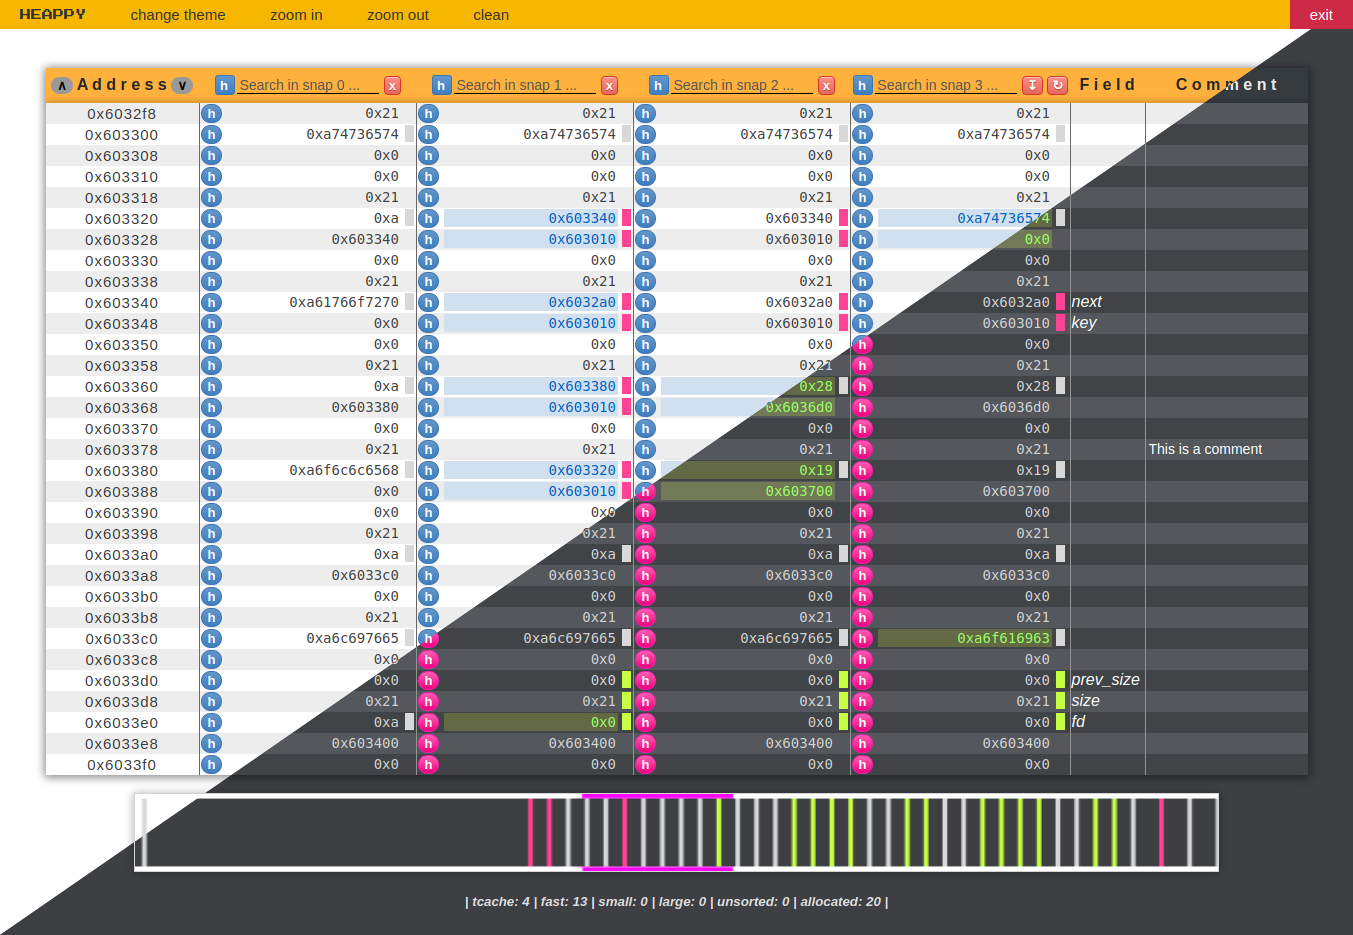
A happy heap editor to support your exploitation process :slightly_smiling_face:

A library for intercepting native functions by hooking KiFastSystemCall

Personal research into the Xbox Series Architecture

1day research effort

Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3