

N0xis
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
ai-assisted-reversingbinary-analysisbinary-exploitation+7
5
structio-labs/n0xisReverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 ibonok/cve-2026-94300
Self-contained PoC and analysis for CVE-2026-94300, a GSS-TSIG use-after-free in BIND 9.20.29, with a debugger-assisted model of the…
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

 binaryhardening/cfgrip
Disassembles PE/ELF x86/x64 binaries, resolves indirect branches via GOT, jump tables, and register tracing, and exports the full control flow graph…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…
 pravin761/cve-2026-54107
Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 gmh5225/ollytlscatch
OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…
 landw-hub/cve-2025-50420
Proof-of-concept exploit for CVE-2025-50420 demonstrating infinite recursion in Poppler's pdfseparate via crafted /Annots dictionaries, causing…
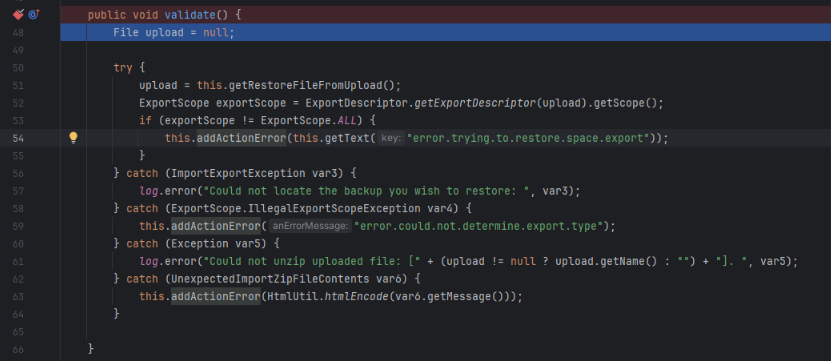 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…