
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
504 results
Voidgate preview

Voidgate

GitHubvxcrypt0r/voidgate

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
adversarial-attackdebuggersids-ips-evasion+3
598
2 years ago
makin preview

makin

GitHubsecrary/makin

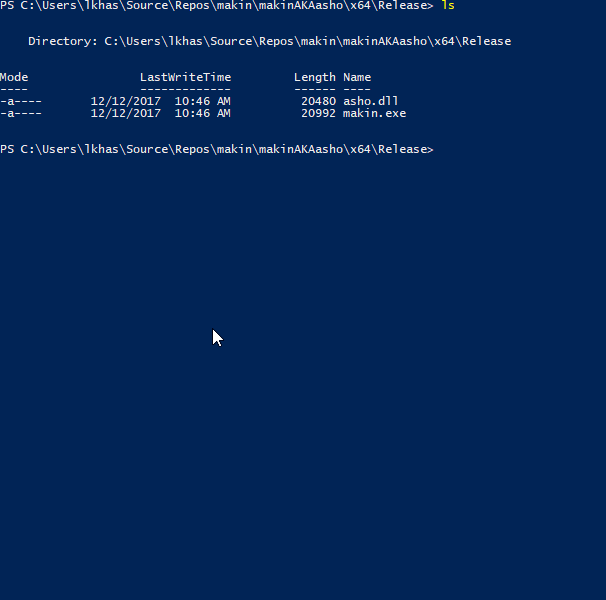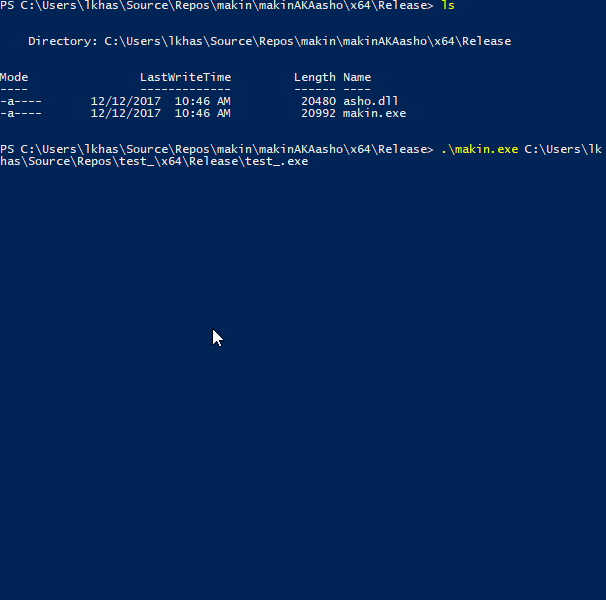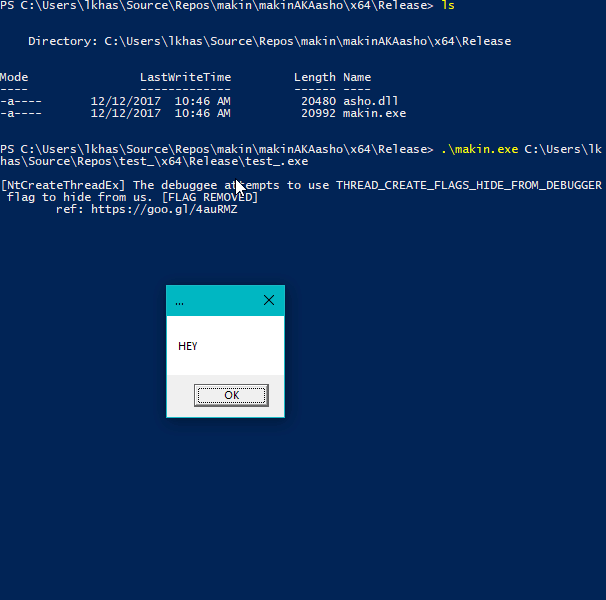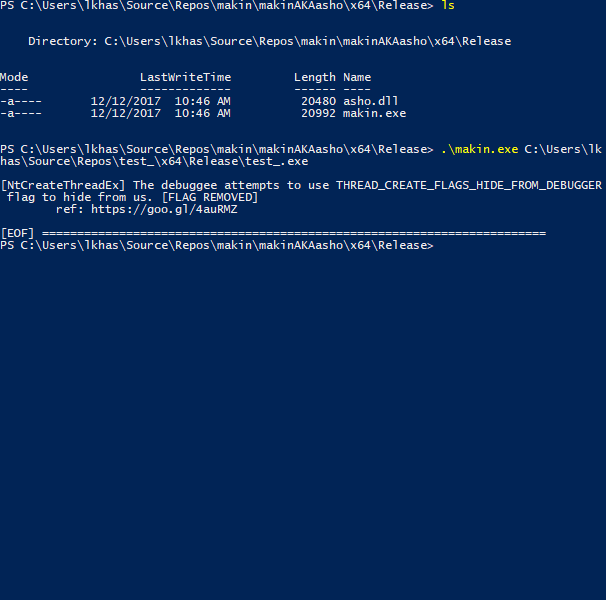
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
anti-botdebuggersdynamic-analysis-sandboxing+2
7427 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
43511 months ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4936 months ago
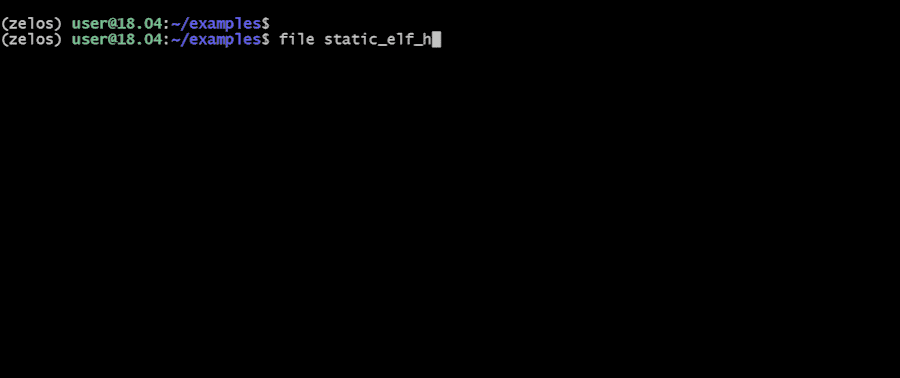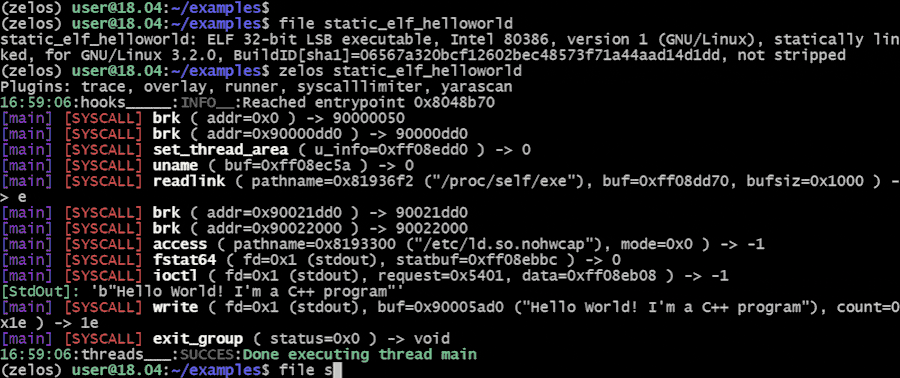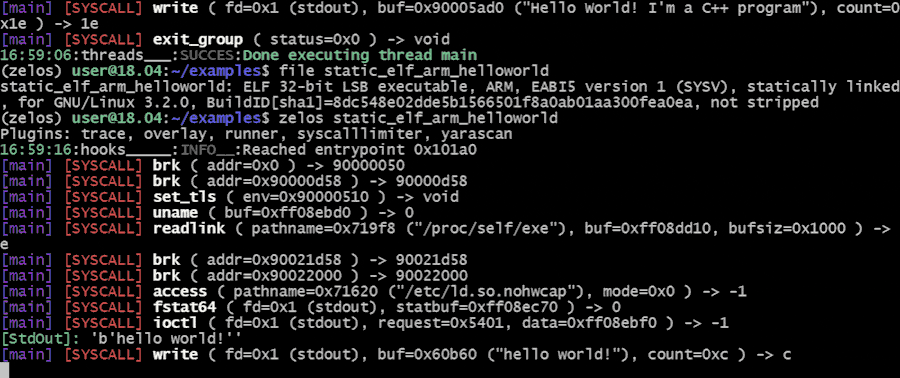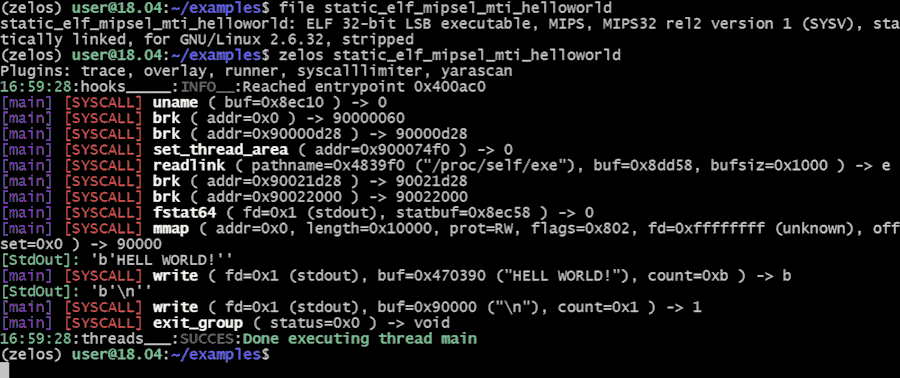
zelos preview

zelos

GitHubzeropointdynamics/zelos

A comprehensive binary emulation and instrumentation platform.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
4203 years ago
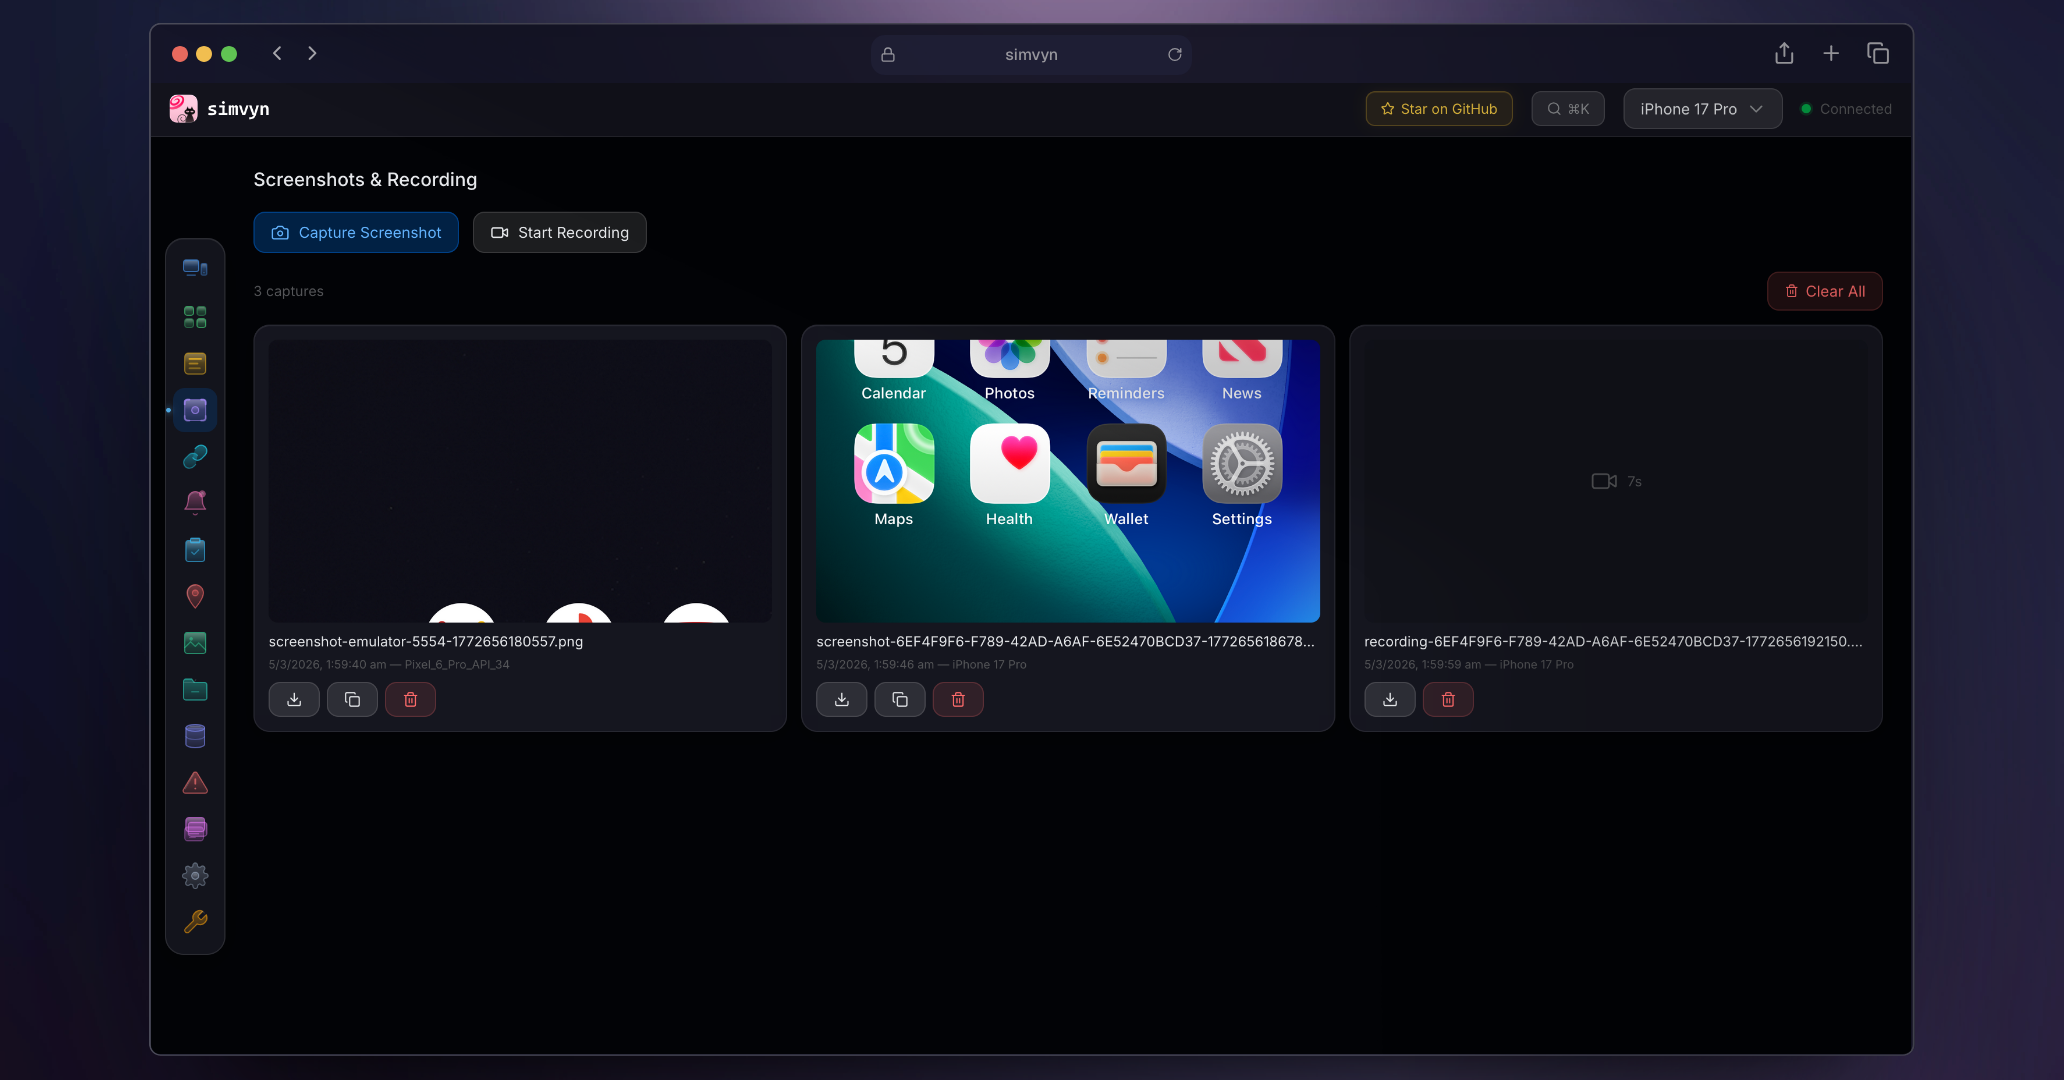
simvyn preview

simvyn

GitHubpranshuchittora/simvyn

Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

android-securitydatabase-securitydebuggers+9
4287 days ago
mcpsnoop preview

mcpsnoop

GitHubkerlenton/mcpsnoop

Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
api-security-testingdebuggersdynamic-analysis-sandboxing+5
3549 days ago
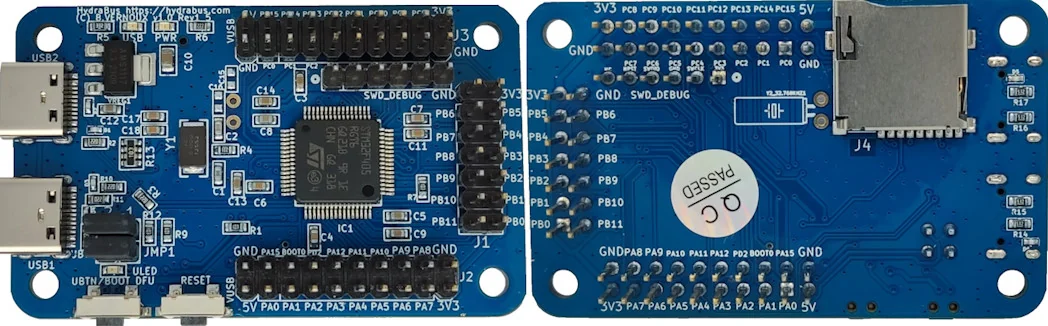
hydrafw preview

hydrafw

GitHubhydrabus/hydrafw

Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
debuggerseducationembedded-systems-security+6
4487 months ago
BugId preview

BugId

GitHubskylined/bugid

Detect, analyze and uniquely identify crashes in Windows applications
binary-analysisdebuggersdynamic-code-analysis+2
5251 year ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

debuggersdynamic-analysis-sandboxingforensics+1
2475 years ago
cerberus-re-skill preview

cerberus-re-skill

GitHubowenpawl/cerberus-re-skill

cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
binary-analysisdebuggersdynamic-analysis-sandboxing+7
19921 days ago
gdb-static preview

gdb-static

GitHubhugsy/gdb-static

Public repository of statically compiled GDB and GDBServer
binary-analysisdebuggersexploitation+3
3964 years ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
2188 days ago
ScratchABit preview

ScratchABit

GitHubpfalcon/scratchabit

Easily retargetable and hackable interactive disassembler with IDAPython-compatible plugin API
binary-analysisdebuggersreverse-engineering+1
4125 years ago
heaptrace preview

heaptrace

GitHubarinerron/heaptrace

helps visualize heap operations for pwn and debugging
binary-analysisctfdebuggers+1
3303 years ago
hwbp4mw preview

hwbp4mw

GitHubrad9800/hwbp4mw

Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
adversarial-attackdebuggersids-ips-evasion+2
2743 years ago
atlantis-android preview

atlantis-android

GitHubproxymanapp/atlantis-android

Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.

android-securityapi-security-testingdebuggers+3
4726 months ago
Previous1…456…28Next