
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
111 results
simvyn preview

simvyn

GitHubpranshuchittora/simvyn

Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

android-securitydatabase-securitydebuggers+9
431
12 days ago
pylane preview

pylane

GitHubnteseyes/pylane

An python vm injector with debug tools, based on gdb.
binary-analysisdebuggersdynamic-analysis-sandboxing+1
3593 years ago
STrace preview

STrace

GitHubmandiant/strace

A DTrace on Windows Reimplementation
debuggersdynamic-code-analysisincident-response+2
3794 months ago
atlantis-android preview

atlantis-android

GitHubproxymanapp/atlantis-android

Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
android-securityapi-security-testingdebuggers+3
4726 months ago
sigwire preview

sigwire

GitHubyeet-src/sigwire

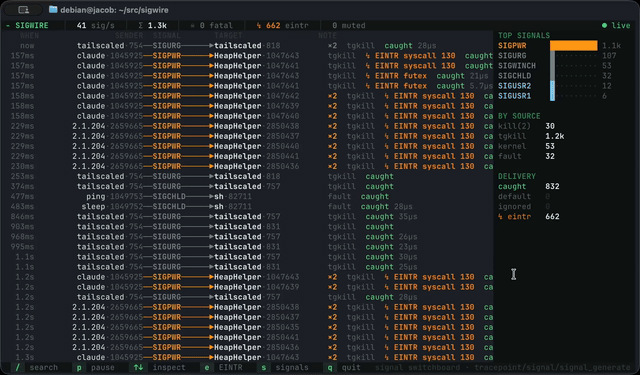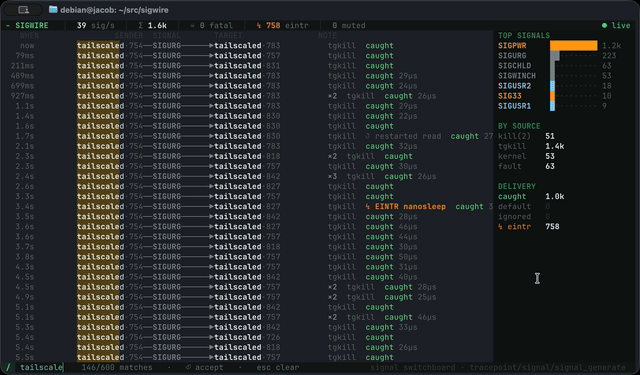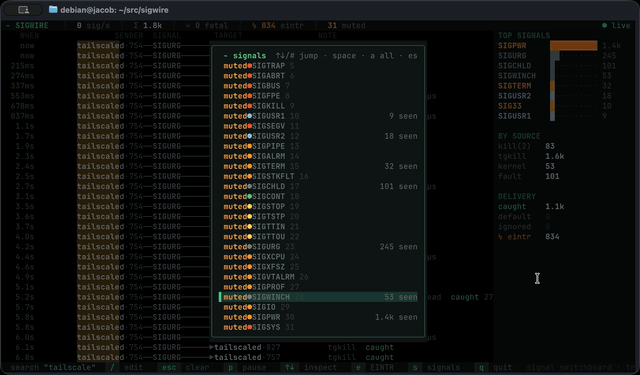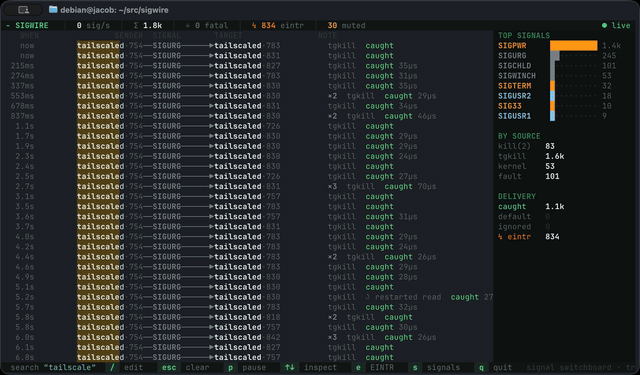
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
debuggersdynamic-analysis-sandboxingforensics+2
1611 month ago
cve-2019-2215 preview

cve-2019-2215

GitHubkangtastic/cve-2019-2215

Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215

android-securitybinary-exploitationdebuggers+4
1376 years ago
instrumentation_callbacks preview

instrumentation_callbacks

GitHubdeputation/instrumentation_callbacks

A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1664 years ago
Flutter-Reverse-Engineering-Labs preview

Flutter-Reverse-Engineering-Labs

GitHubbrnpl/flutter-reverse-engineering-labs

Hands-on challenges for learning how to reverse engineer Flutter applications.

android-securitybinary-analysisctf+6
5811 days ago
c0ntextomy preview

c0ntextomy

GitHubc0ntextomy/c0ntextomy

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
data-exfiltrationdebuggersexploitation+9
736 years ago
dapr preview

dapr

GitHubnccgroup/dapr

Driver Attack Platform for Linux

android-securitybinary-exploitationdebuggers+5
196 years ago
super-trouper preview

super-trouper

GitHubcrissyfield/super-trouper

MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
android-securitybinary-analysisdebuggers+5
227 days ago
renef-skills preview

renef-skills

GitHubvichhka-git/renef-skills

Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
android-securitybinary-analysisctf+9
153 months ago
CVE-2023-6241-Pixel7_Adaptation preview

CVE-2023-6241-Pixel7_Adaptation

GitHubilgobbo00/cve-2023-6241-pixel7_adaptation

Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241
android-securitybinary-exploitationdebuggers+5
151 year ago
CVE-2025-65320 preview

CVE-2025-65320

GitHubyonathanpy/cve-2025-65320

CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
binary-analysisdebuggersexploitation+3
26 months ago
CVE-2019-25485 preview

CVE-2019-25485

GitHubthemalwareguardian/cve-2019-25485

Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…
binary-exploitationdebuggerseducation+5
6 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubcharlyrr/cve-2025-5548

Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
binary-exploitationdebuggerseducation+7
6 months ago
CVE-2020-0022 preview

CVE-2020-0022

GitHubkalibb/cve-2020-0022

Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
android-securitybinary-exploitationbluetooth-security+9
7 months ago
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).

binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
Previous1234567Next