
cortex
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
ai-assisted-reversingai-securitybinary-analysis+7
3319 days ago
pdb333/cortexA Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 nccgroup/libptmalloc
Heap analysis tooling for ptmalloc
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 nccgroup/libdlmalloc
Heap analysis tooling for dlmalloc
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
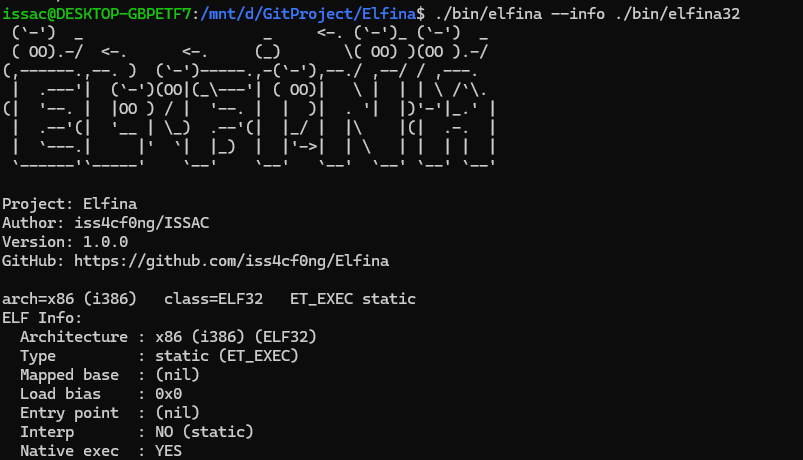 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
 ehabhussein/ollydbg-binary-execution-visualizer
reverse engineering, visual binary analysis
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 spiralbl0ck/blacklotus-analysis-stage2-bootkit-rootkit-stage
Z2A-BlackLotus Challenge stage 2 bootkit-rootkit analysis
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 nccgroup/libmempool
Heap analysis tooling for mempool
 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…