
ChromeKatz
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
data-exfiltrationdebuggersmemory-forensics+3
1.5k
meckazin/chromekatzDump cookies and credentials directly from Chrome/Edge process memory
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 ctxis/cape
Malware Configuration And Payload Extraction
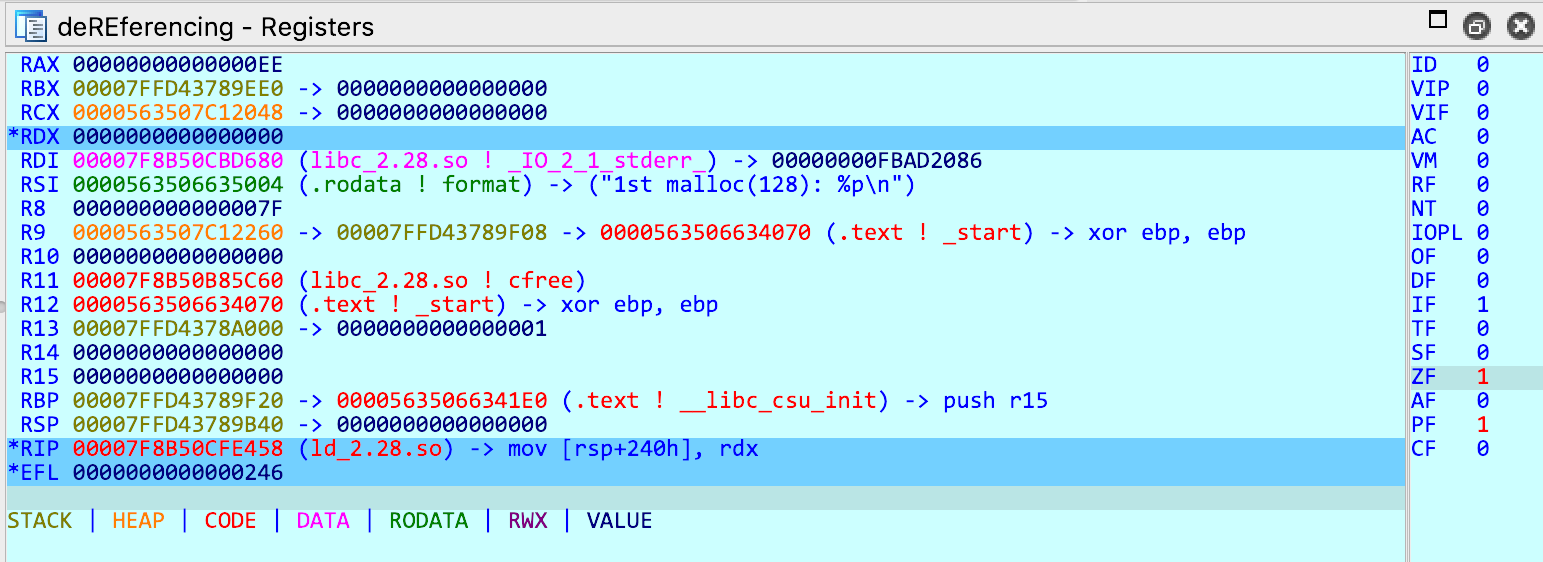 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
 0xnobody/vmpdump
A dynamic VMP dumper and import fixer, powered by VTIL.
 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 patois/dsync
IDAPython plugin that synchronizes disassembler and decompiler views
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
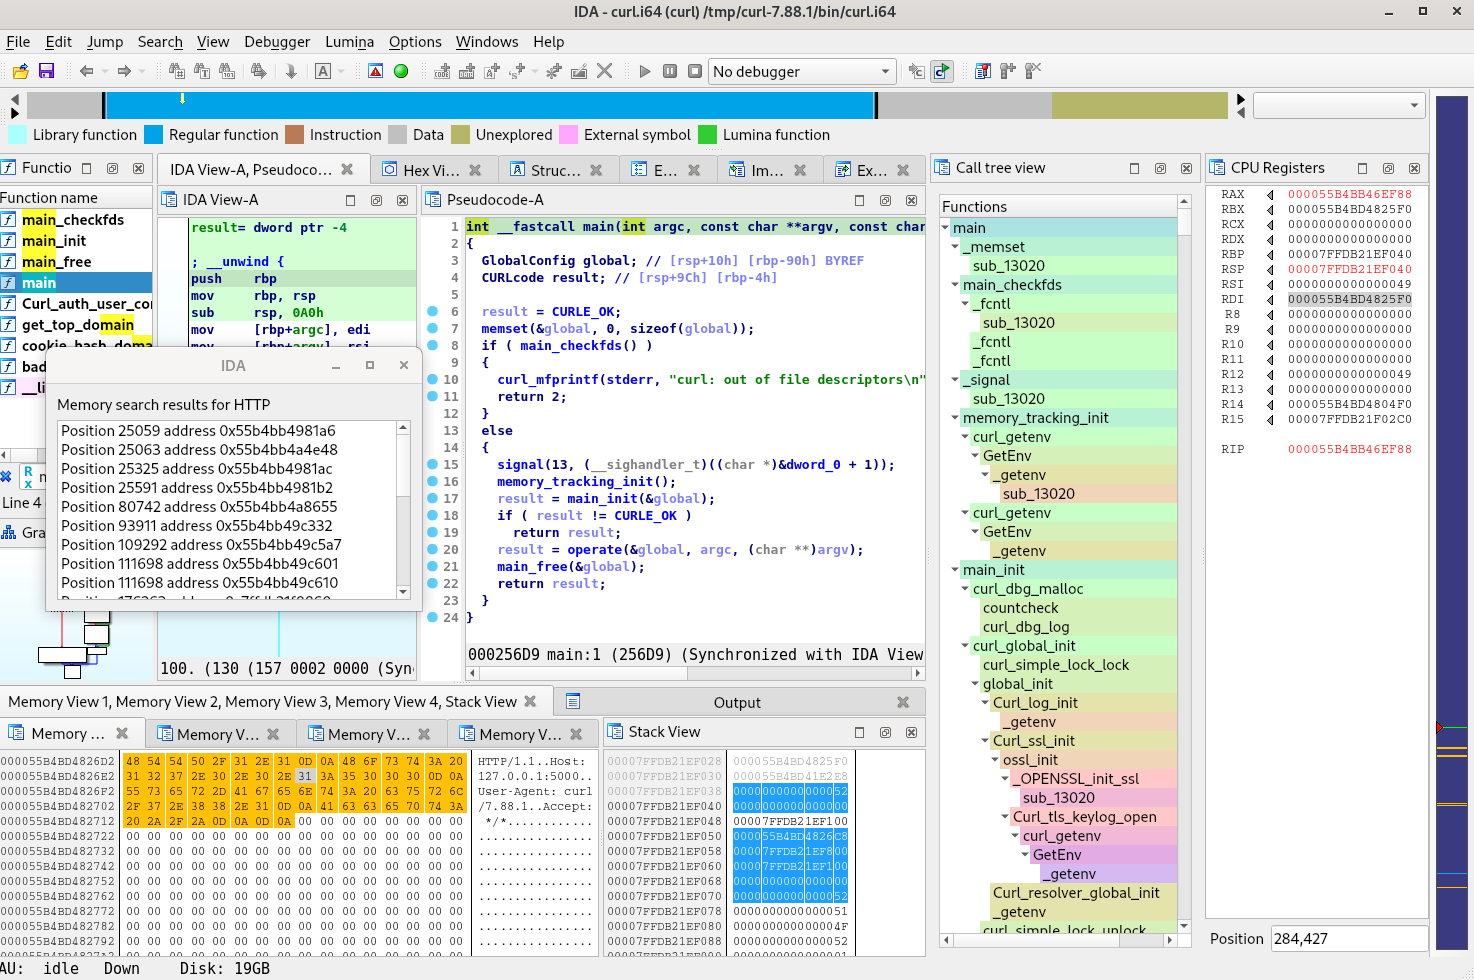 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
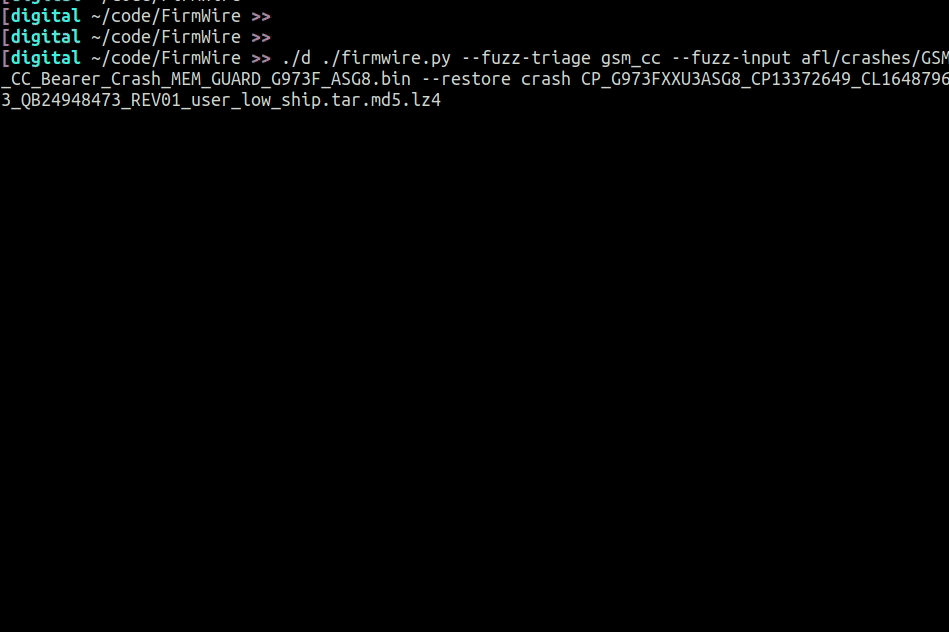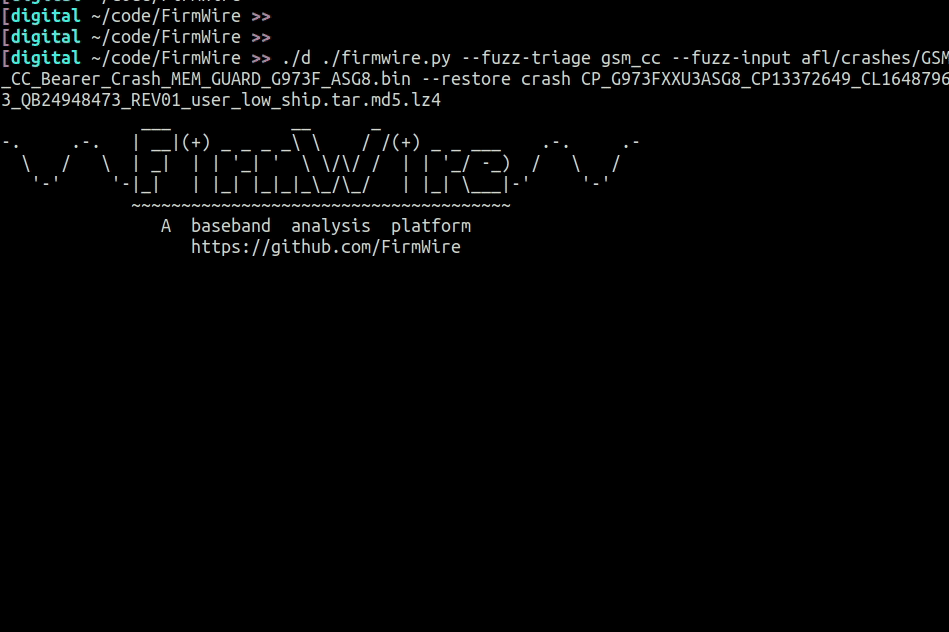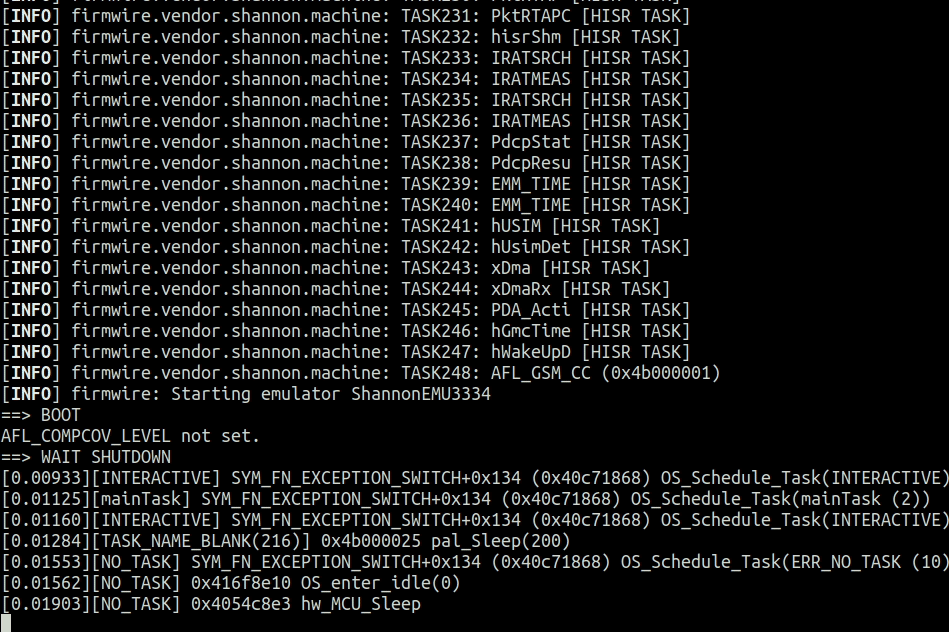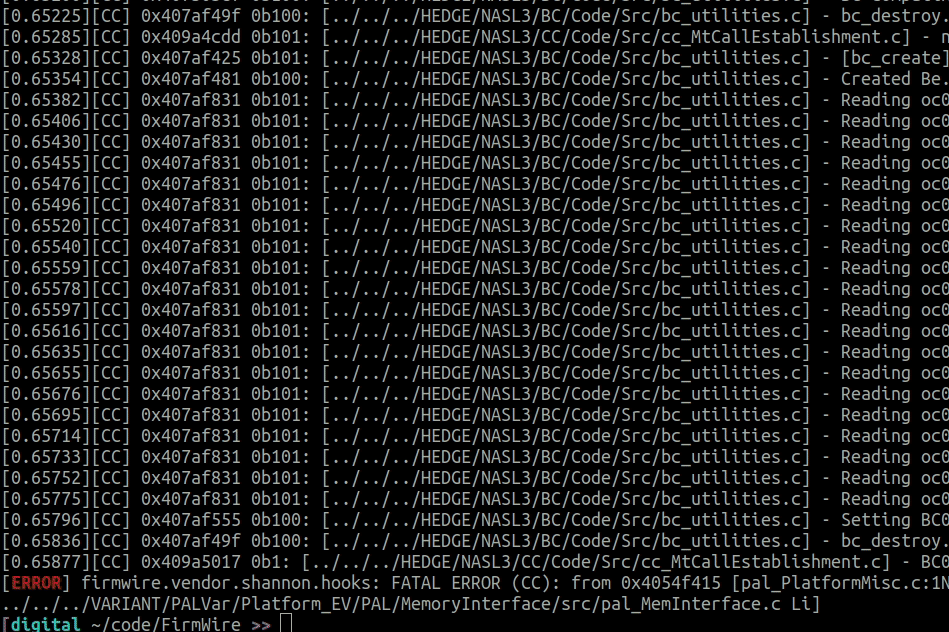 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
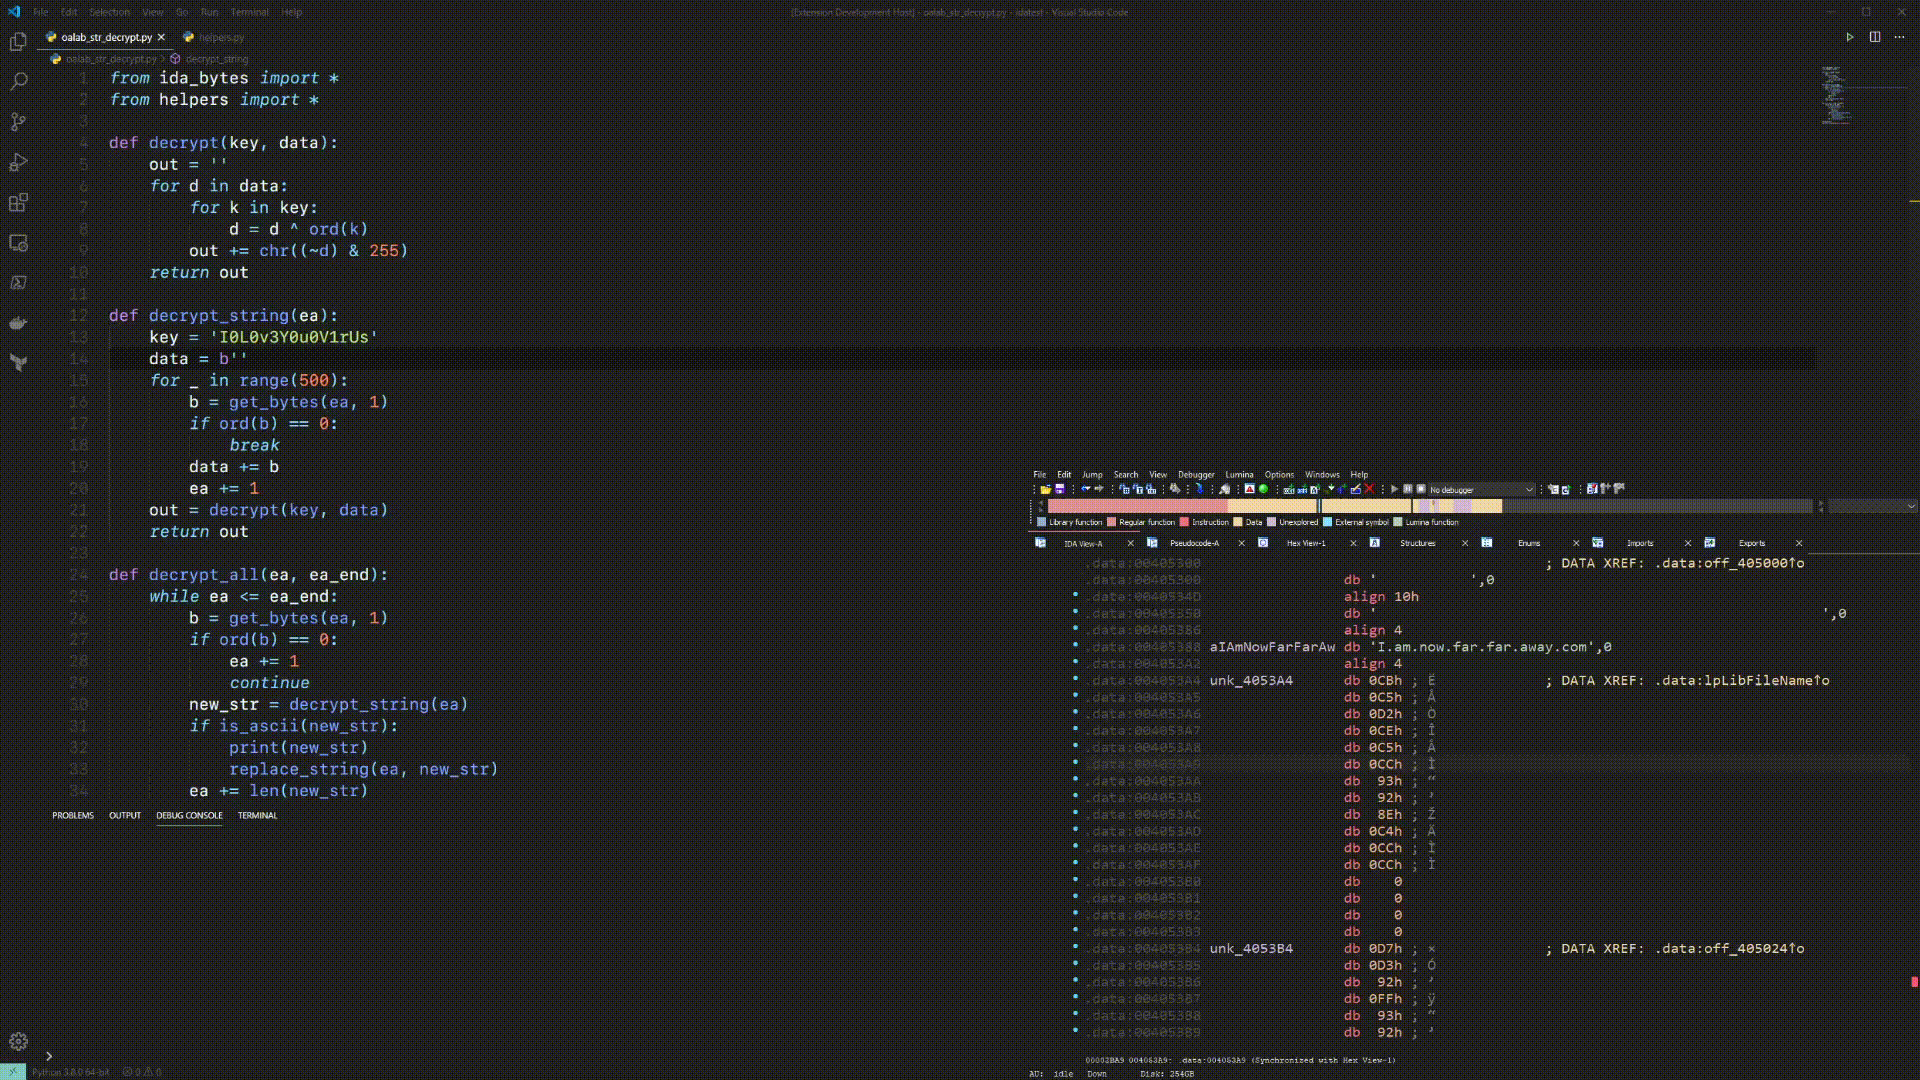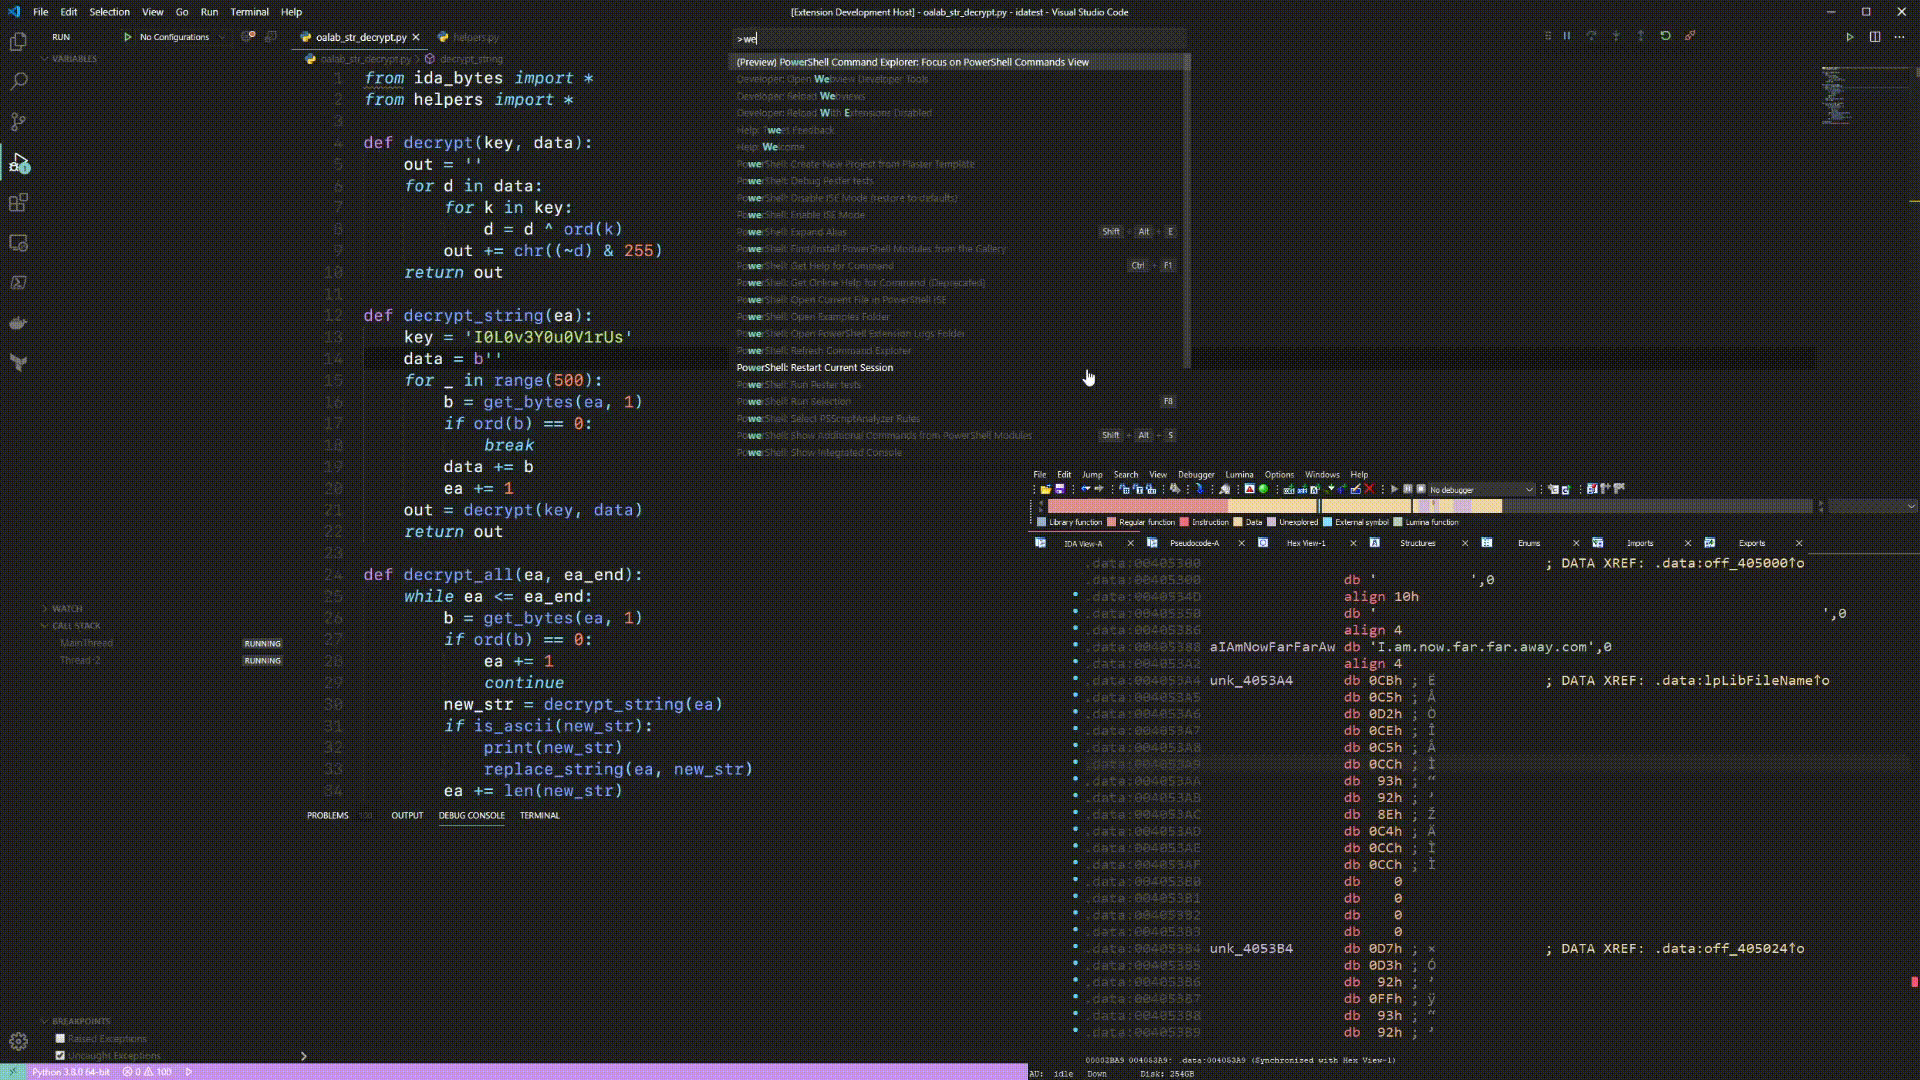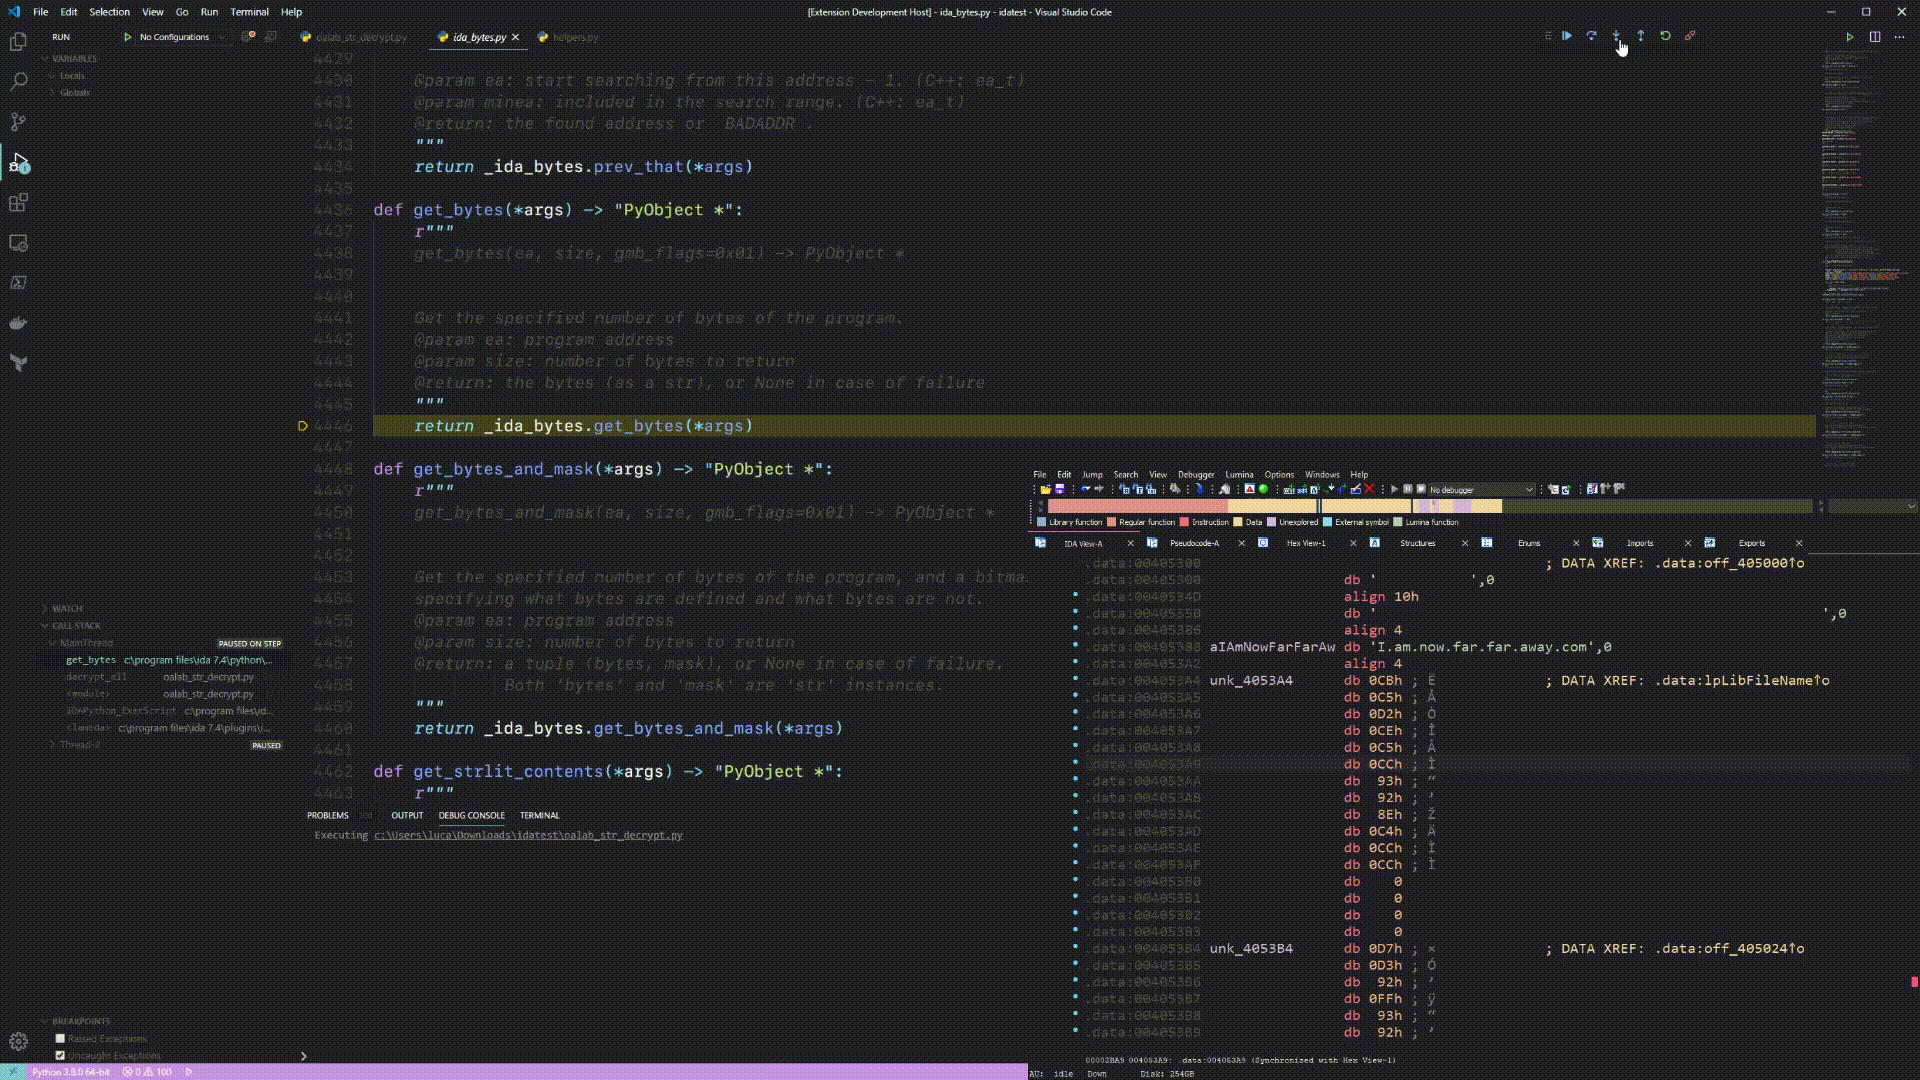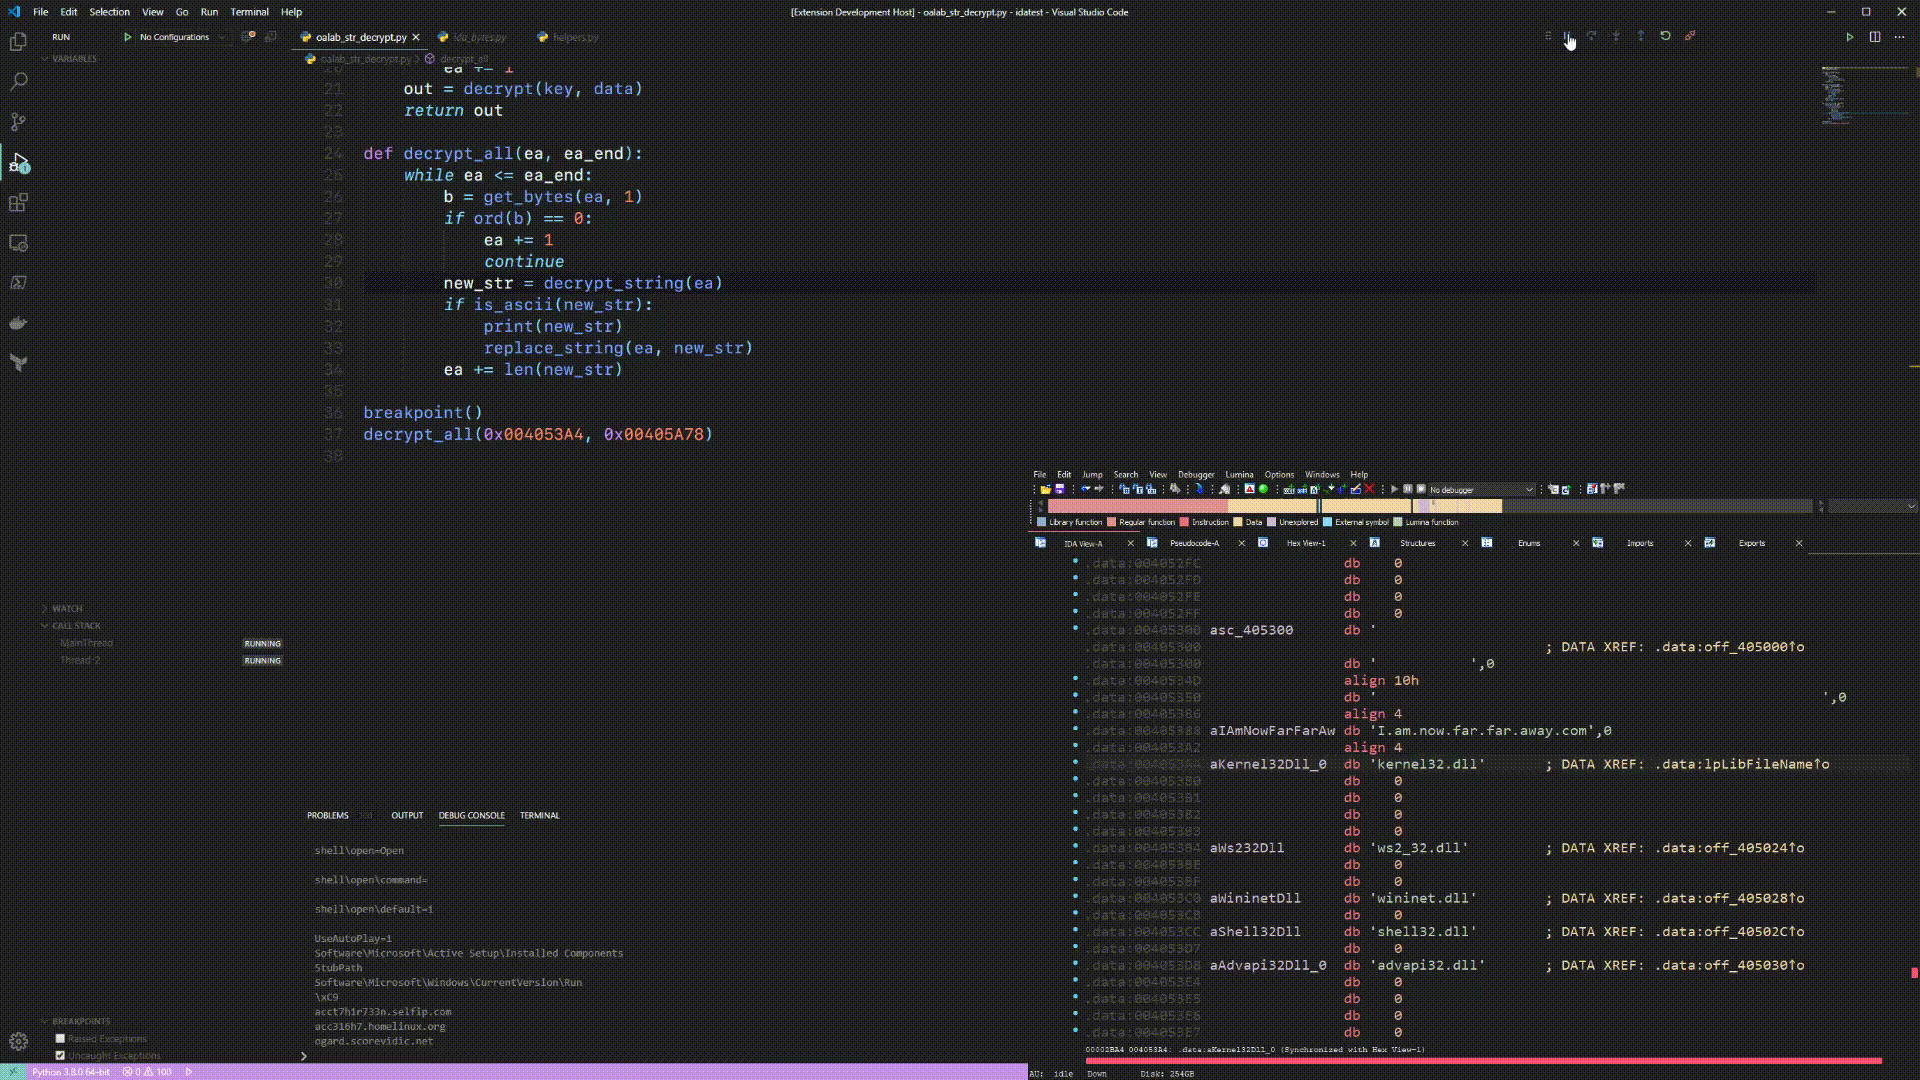 ioncodes/idacode
An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.