
PowerShellArsenal
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
binary-analysisdebuggersdynamic-analysis-sandboxing+6
902
mattifestation/powershellarsenalA PowerShell Module Dedicated to Reverse Engineering
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 zodiacon/alltools
All reasonably stable tools
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
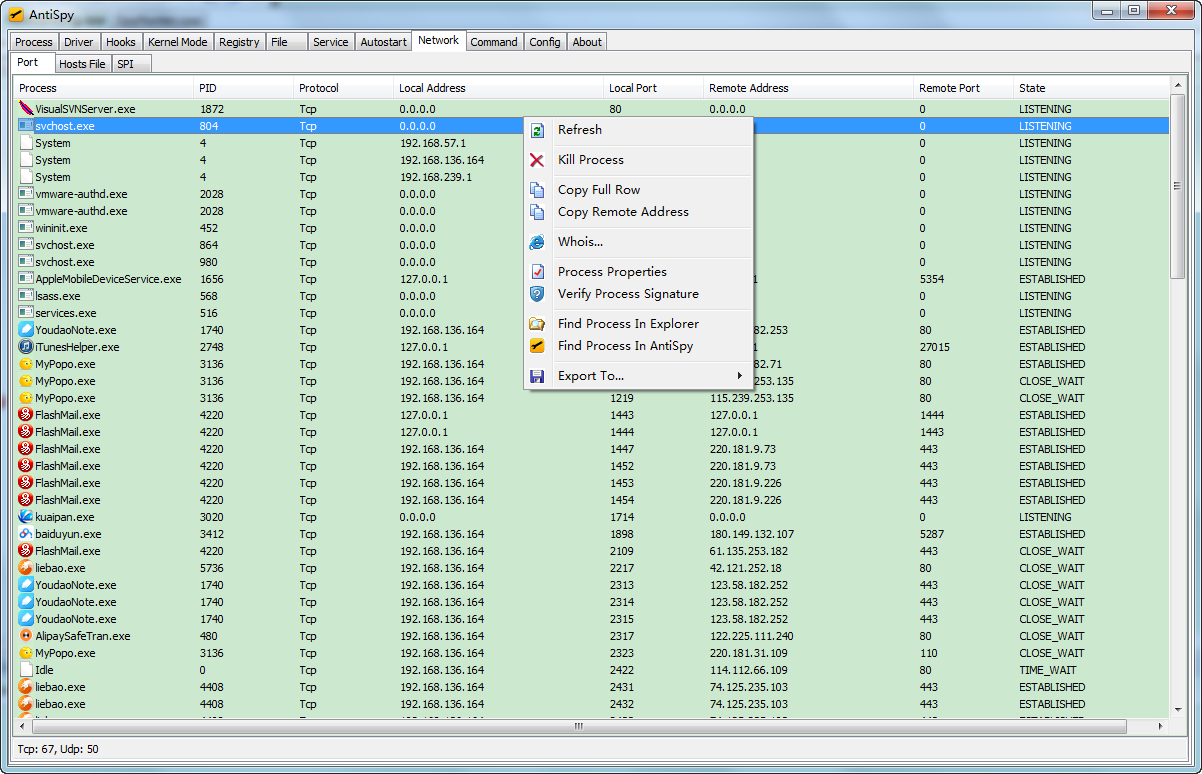 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 nickcano/xenoscan
Open source memory scanner written in C++
 thalium/icebox
Virtual Machine Introspection, Tracing & Debugging
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…