
Triple_fetch
 q1f3/triple_fetch
This is an exploit for CVE-2017-7047, Works on 10.3.2 and below.
binary-exploitationdebuggersexploitation+6
q1f3/triple_fetchThis is an exploit for CVE-2017-7047, Works on 10.3.2 and below.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 nteseyes/pylane
An python vm injector with debug tools, based on gdb.
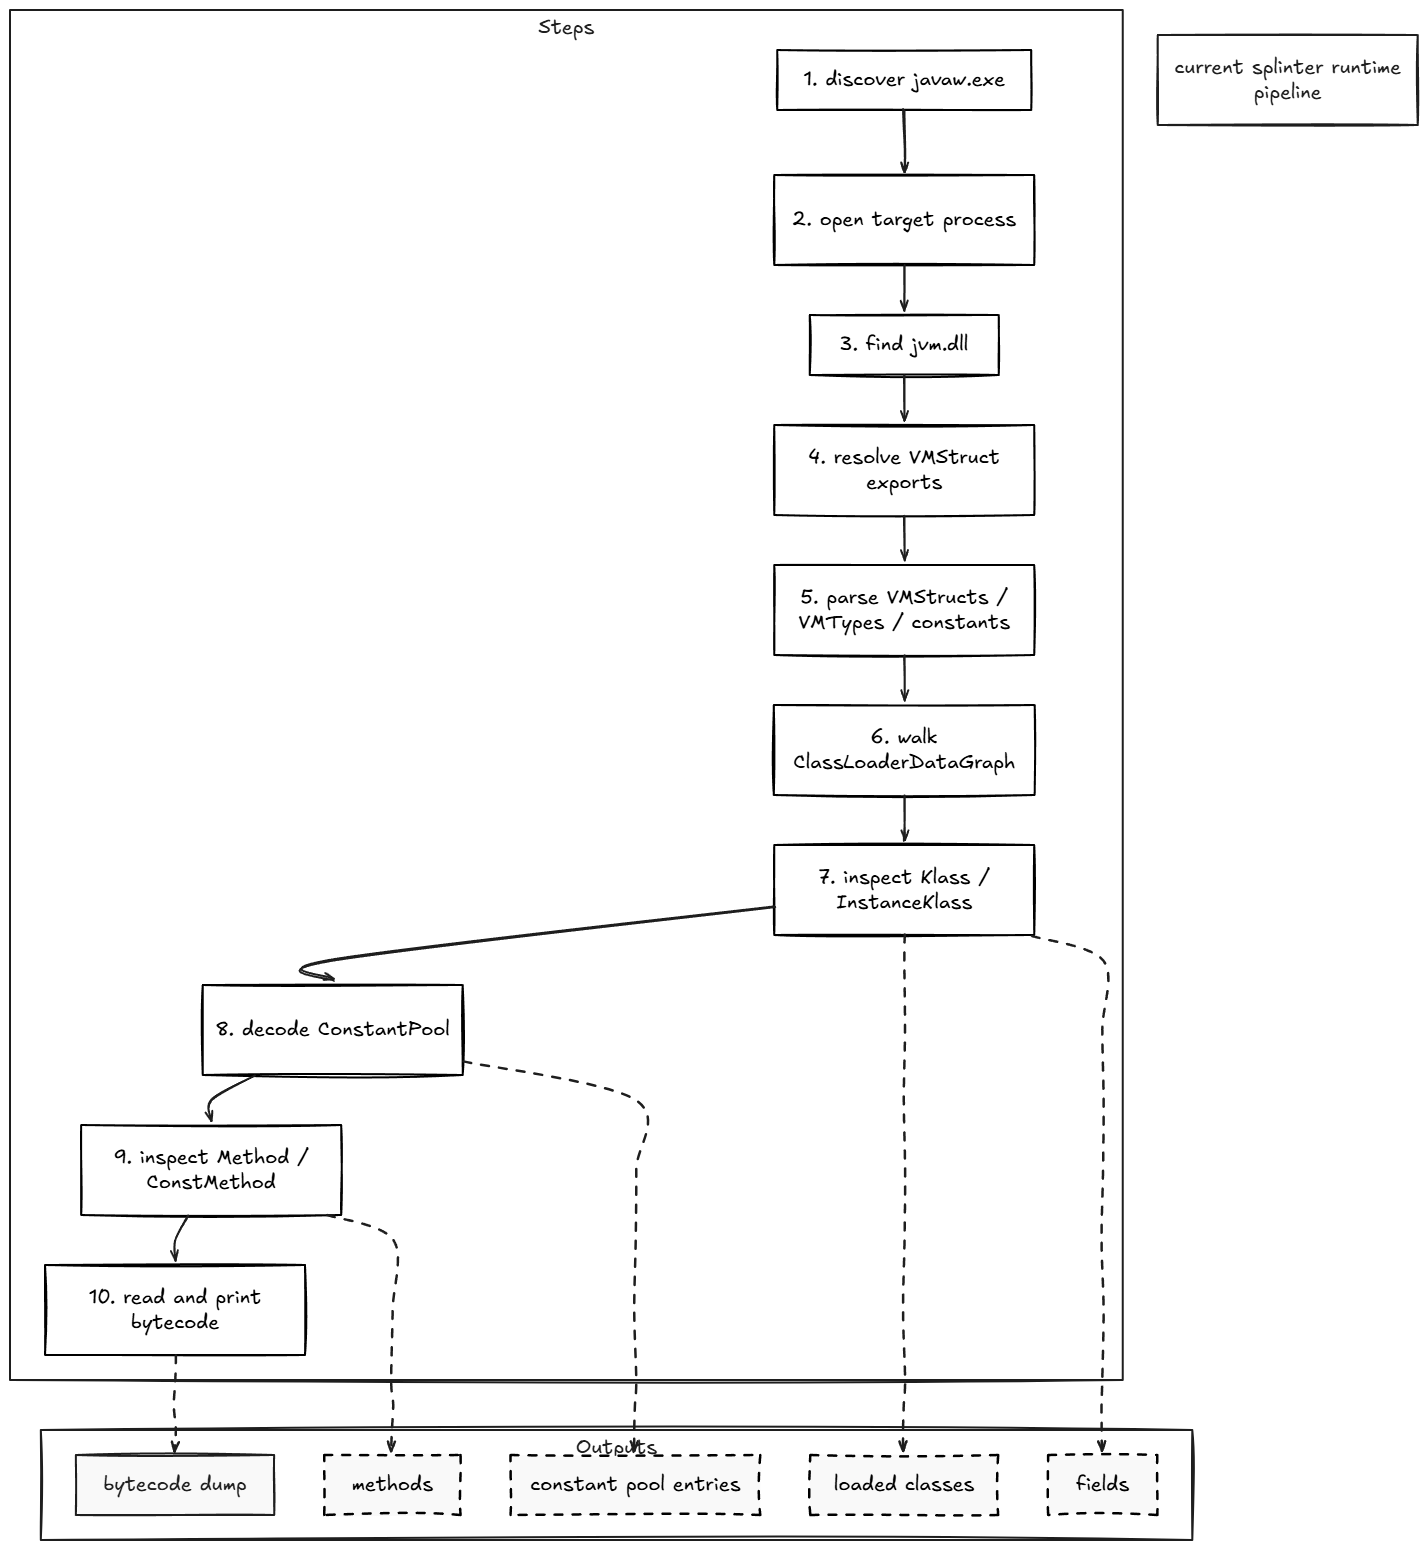 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 chichou/vscode-frida
Unofficial frida extension for VSCode

 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 cheat-engine/cheat-engine
Cheat Engine. A development environment focused on modding
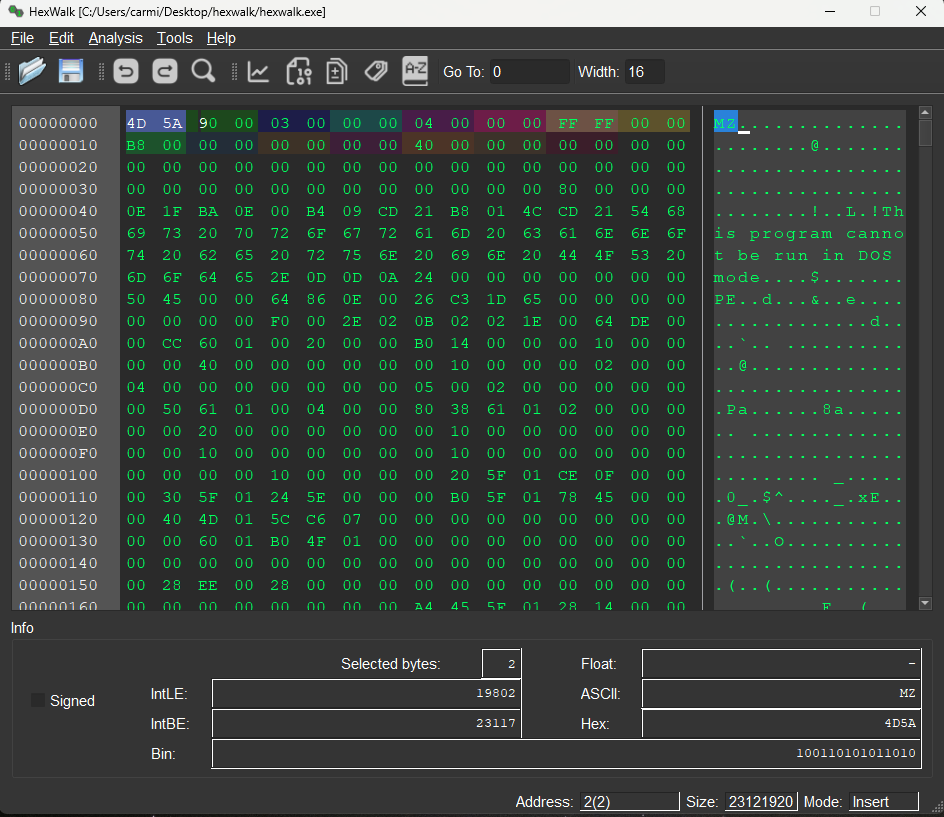 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
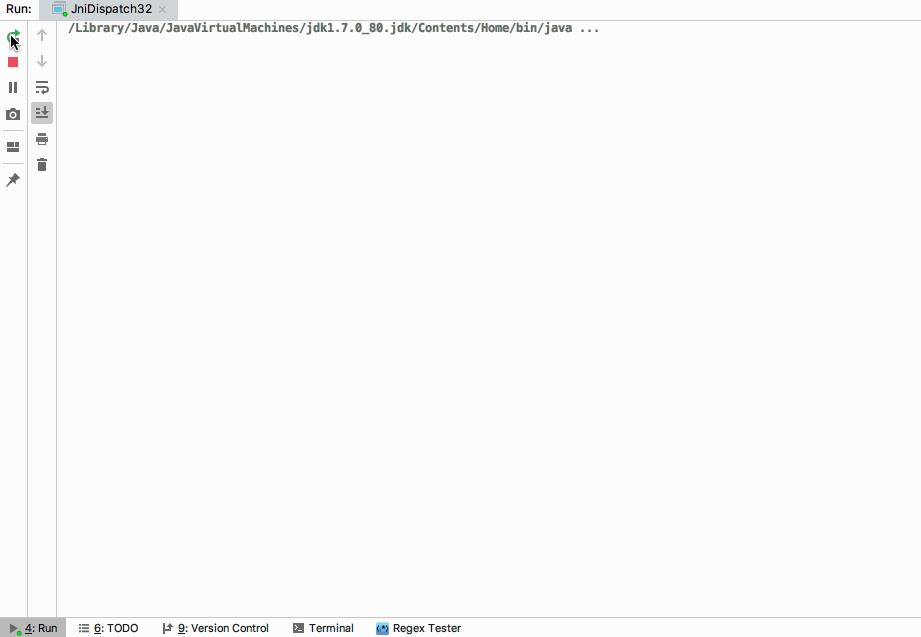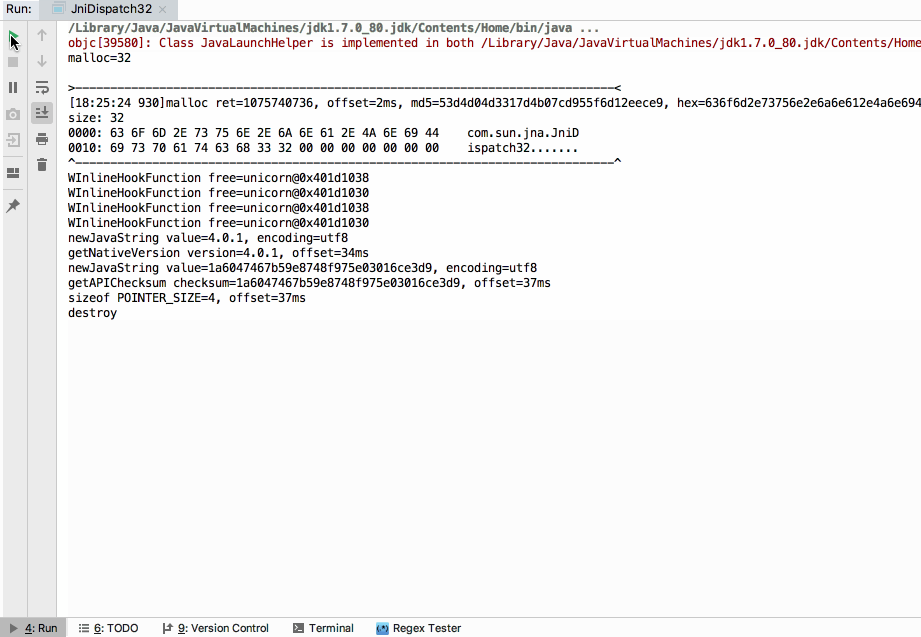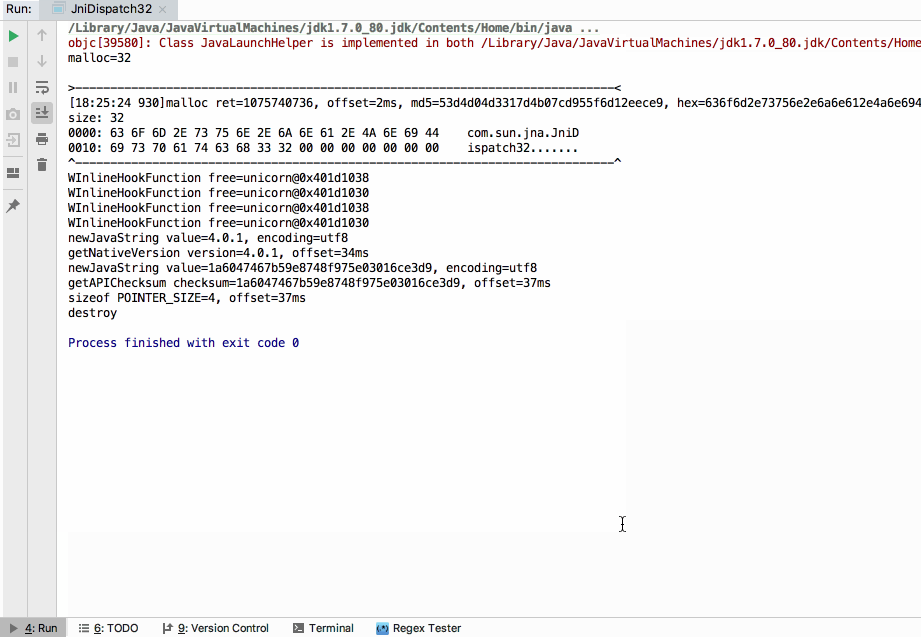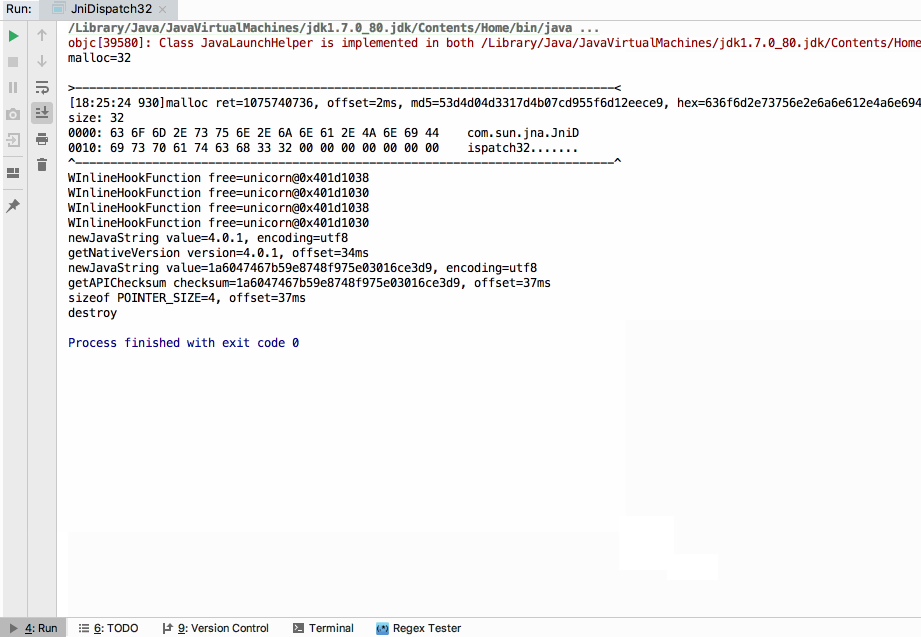 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 nowsecure/r2frida
Radare2 and Frida better together.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…