
Archived
IDArling
 idarlingteam/idarling
Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
binary-analysisdebuggerseducation+2
670
 das-labor/panopticon
A libre cross-platform disassembler.
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
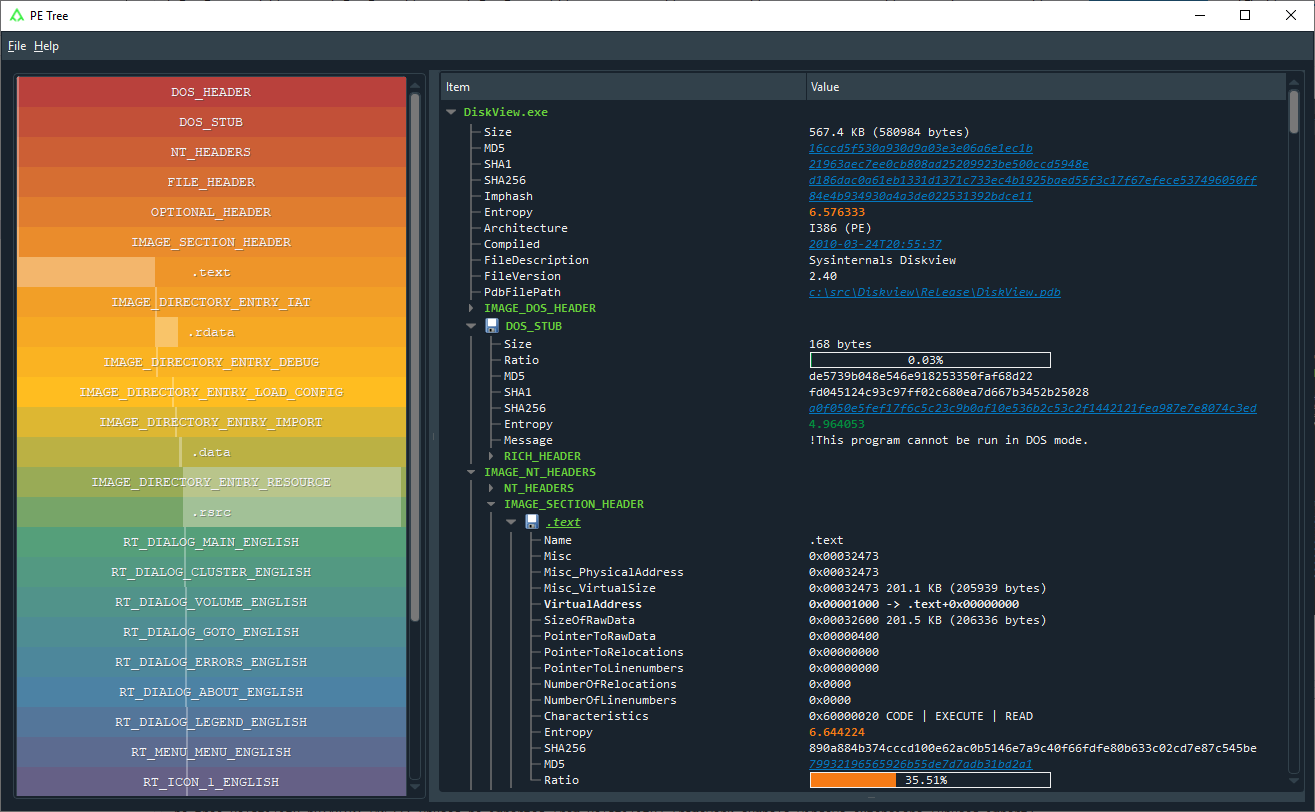 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 gmh5225/fracture-
🐈⬛ WIP Suite for reverse engineering JVM applications
 hugsy/recon_2024_windbg_workshop
Workshop materials for mastering WinDbg debugging in kernel and user mode, with KdNet setup, demos, and a Time Travel Debugging challenge for binary…
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#