

go-sniffer
 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
database-securitydebuggersnetwork-security+2
40t/go-sniffer🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 fr0gger/awesome-ida-x64-olly-plugin
A curated list of IDA x64DBG, Ghidra and OllyDBG plugins.
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 chichou/vscode-frida
Unofficial frida extension for VSCode
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
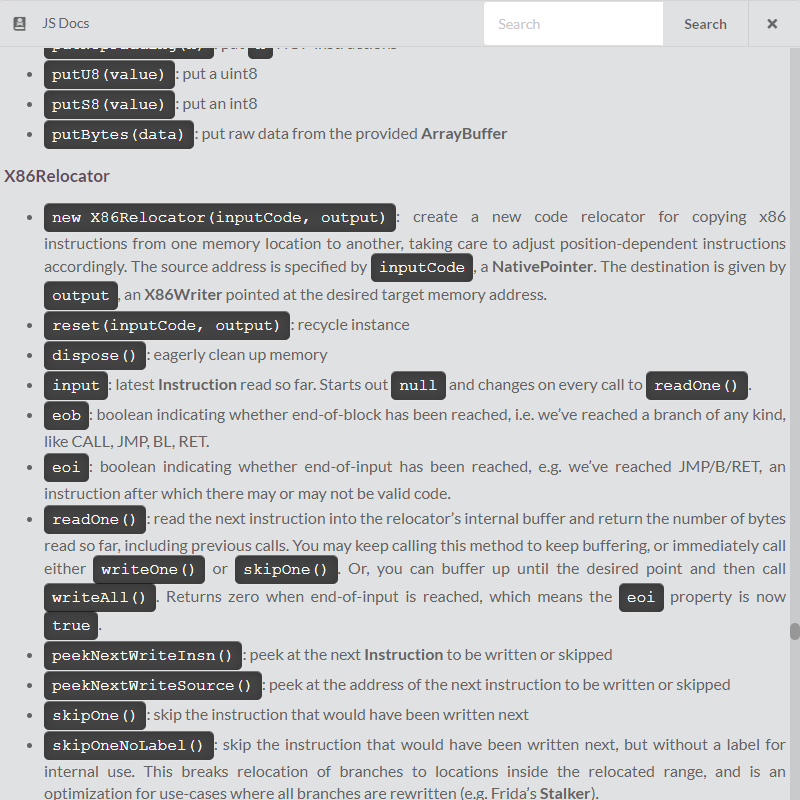 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
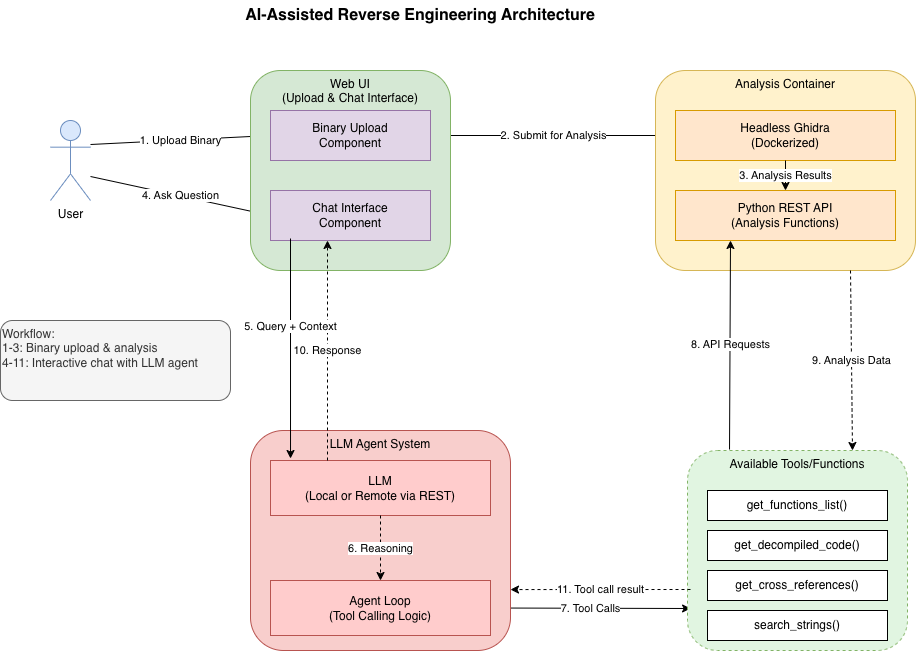 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
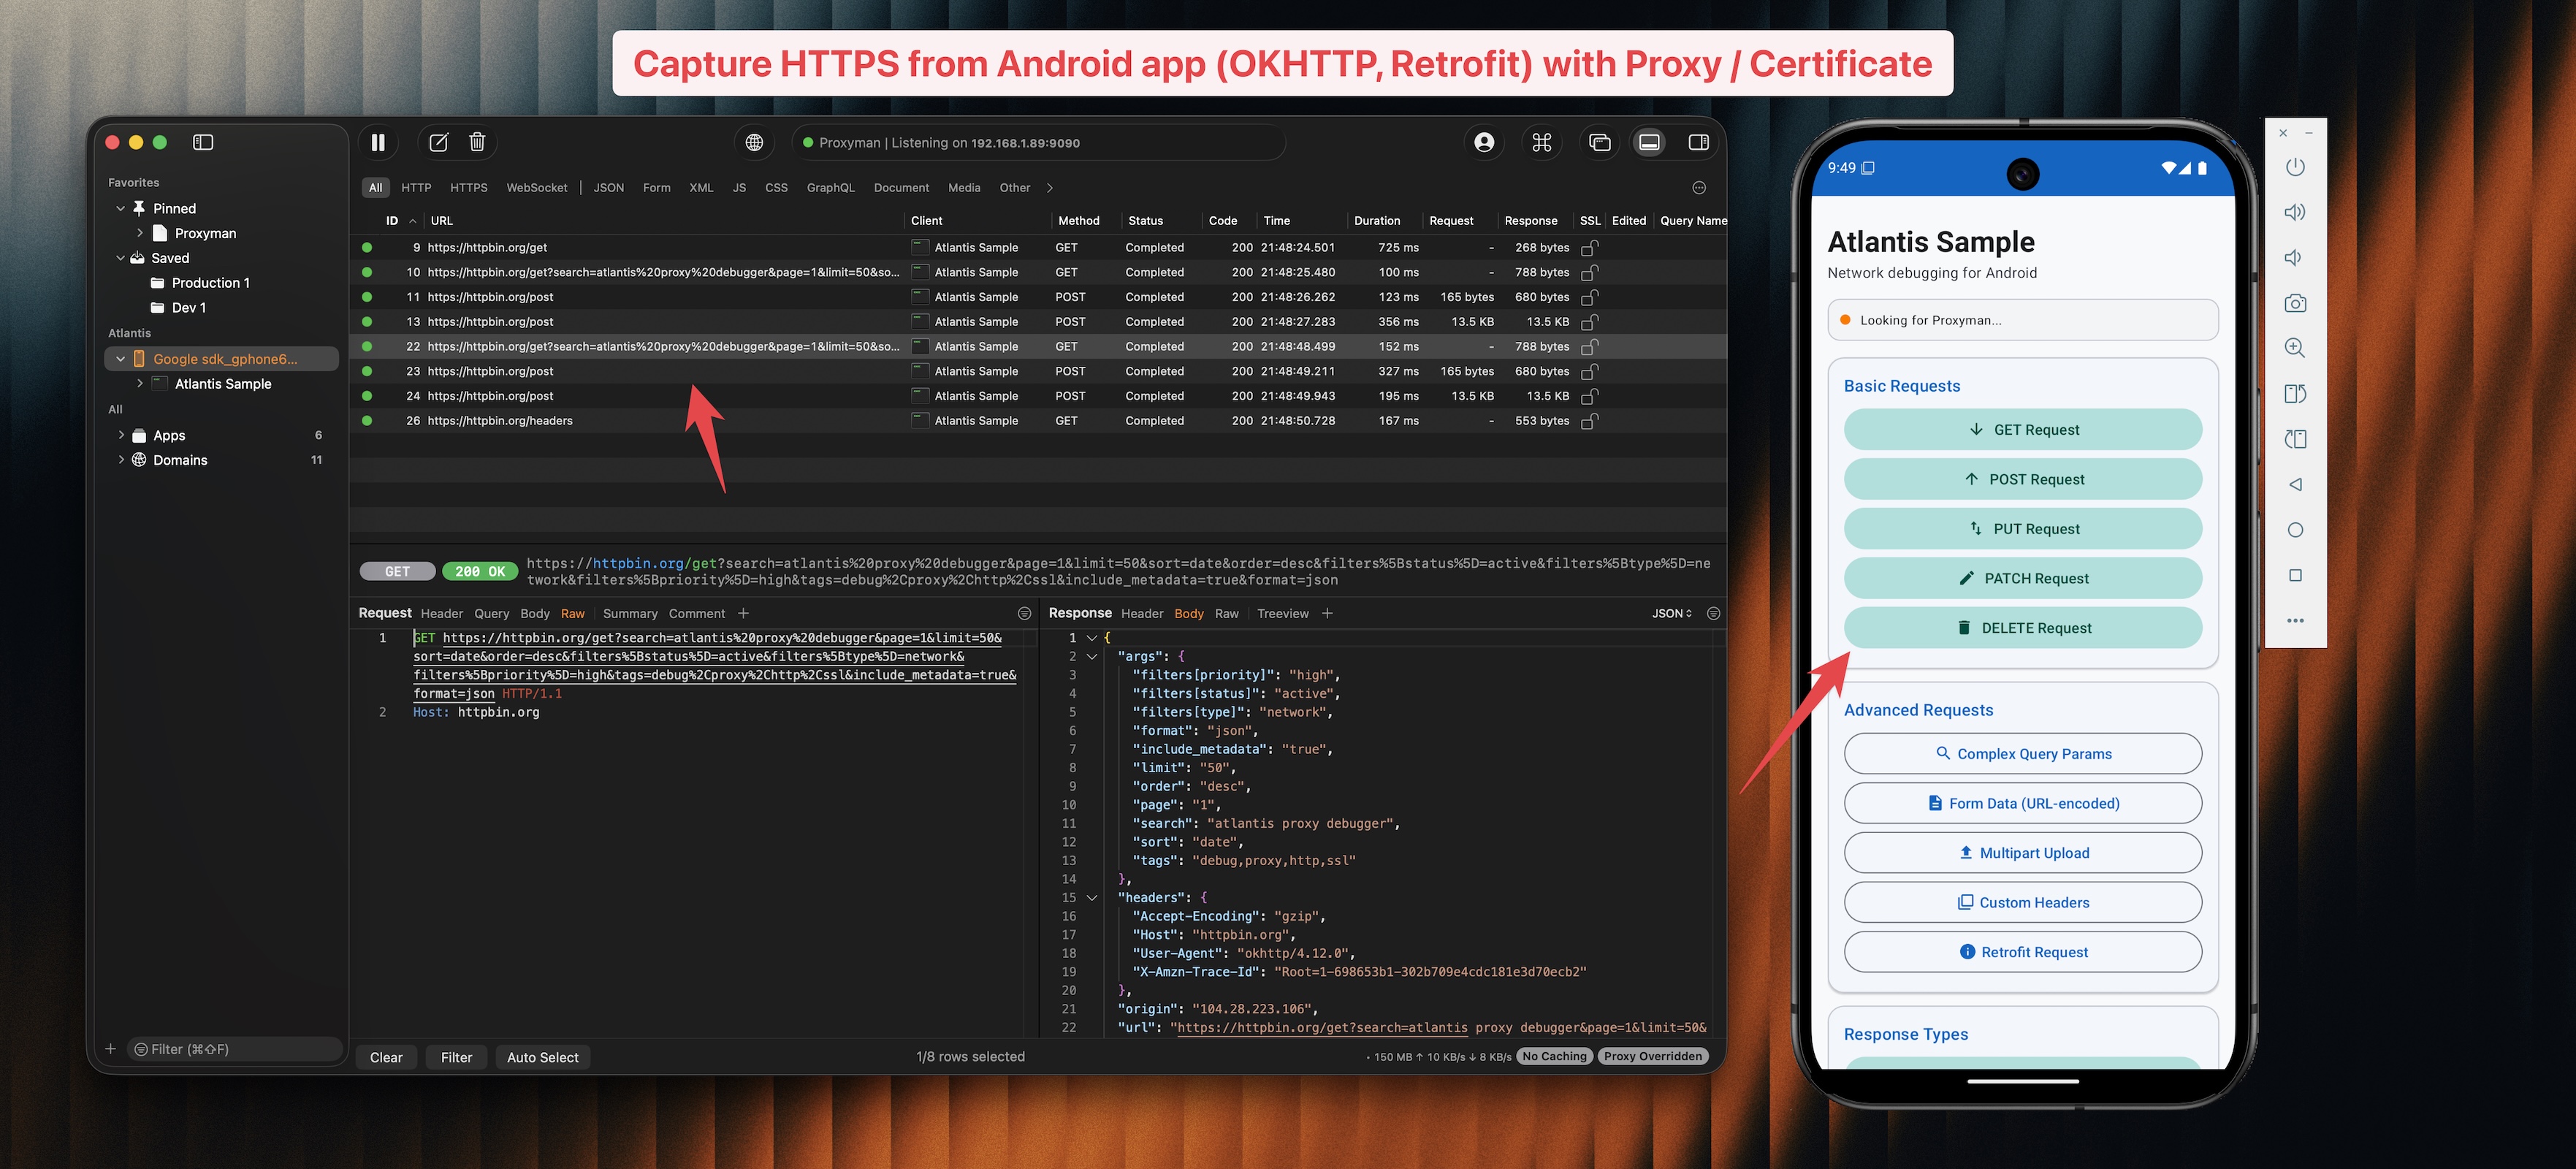 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
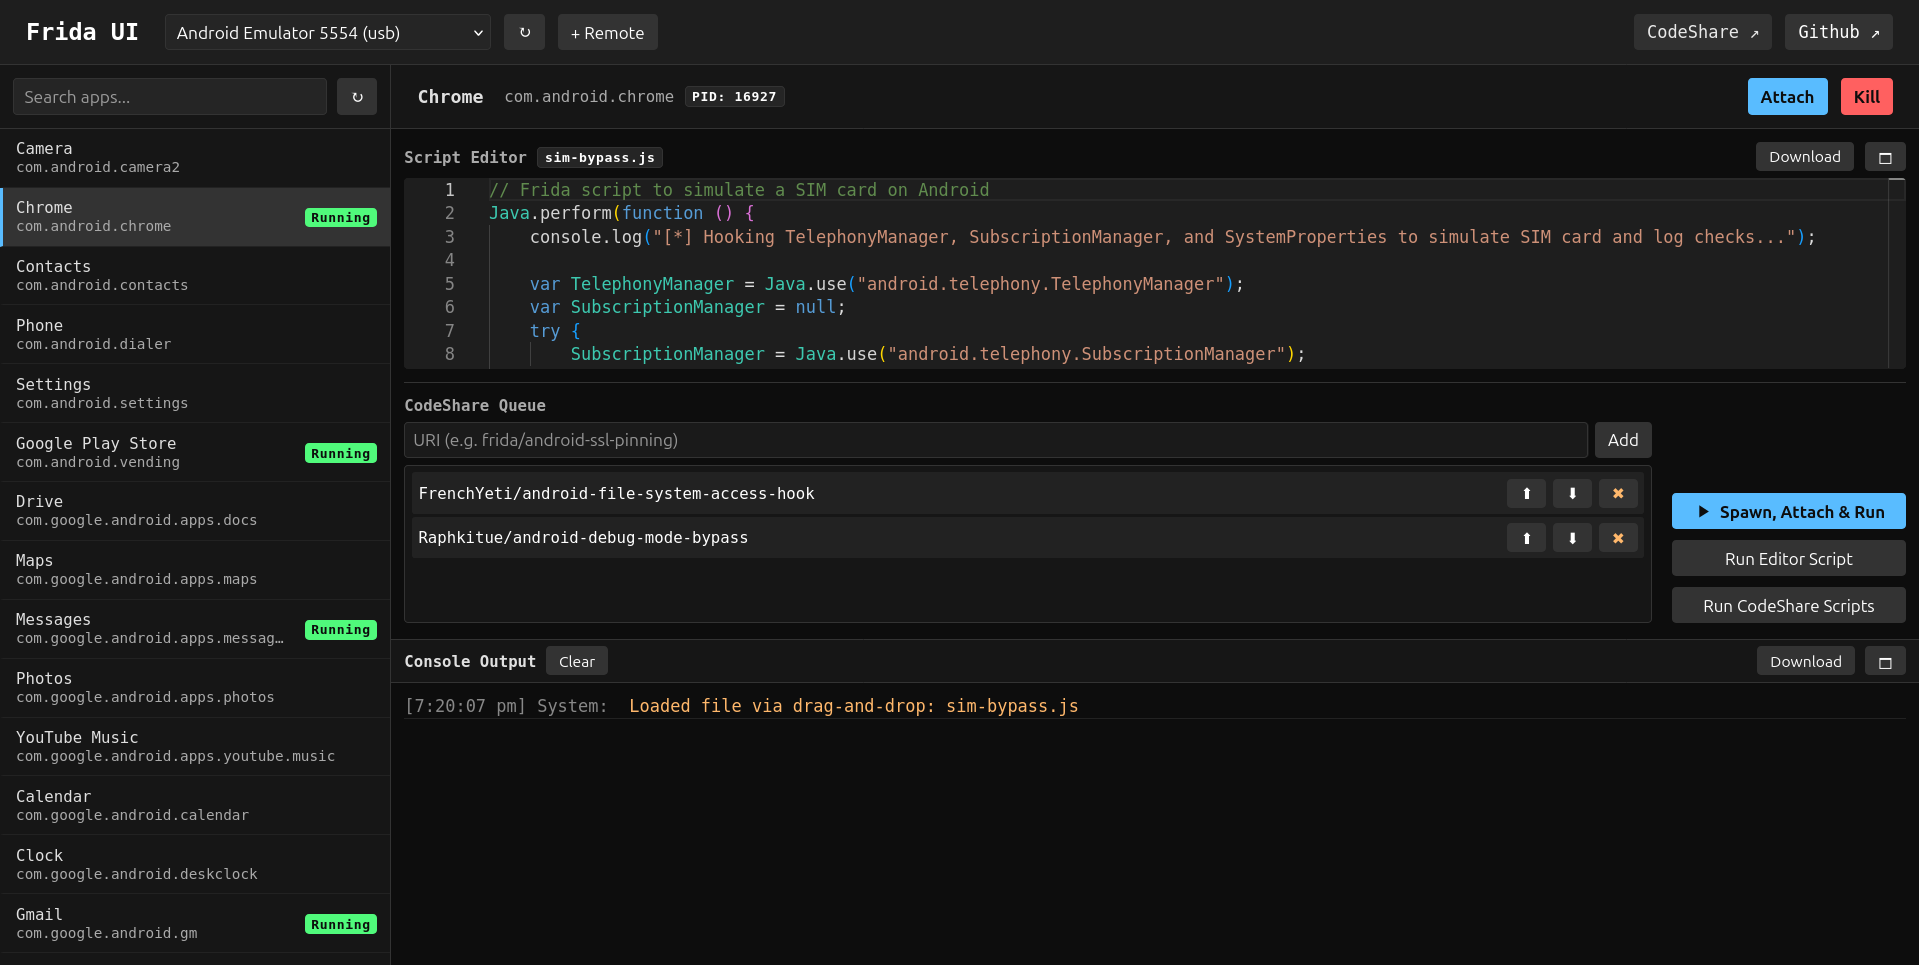 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
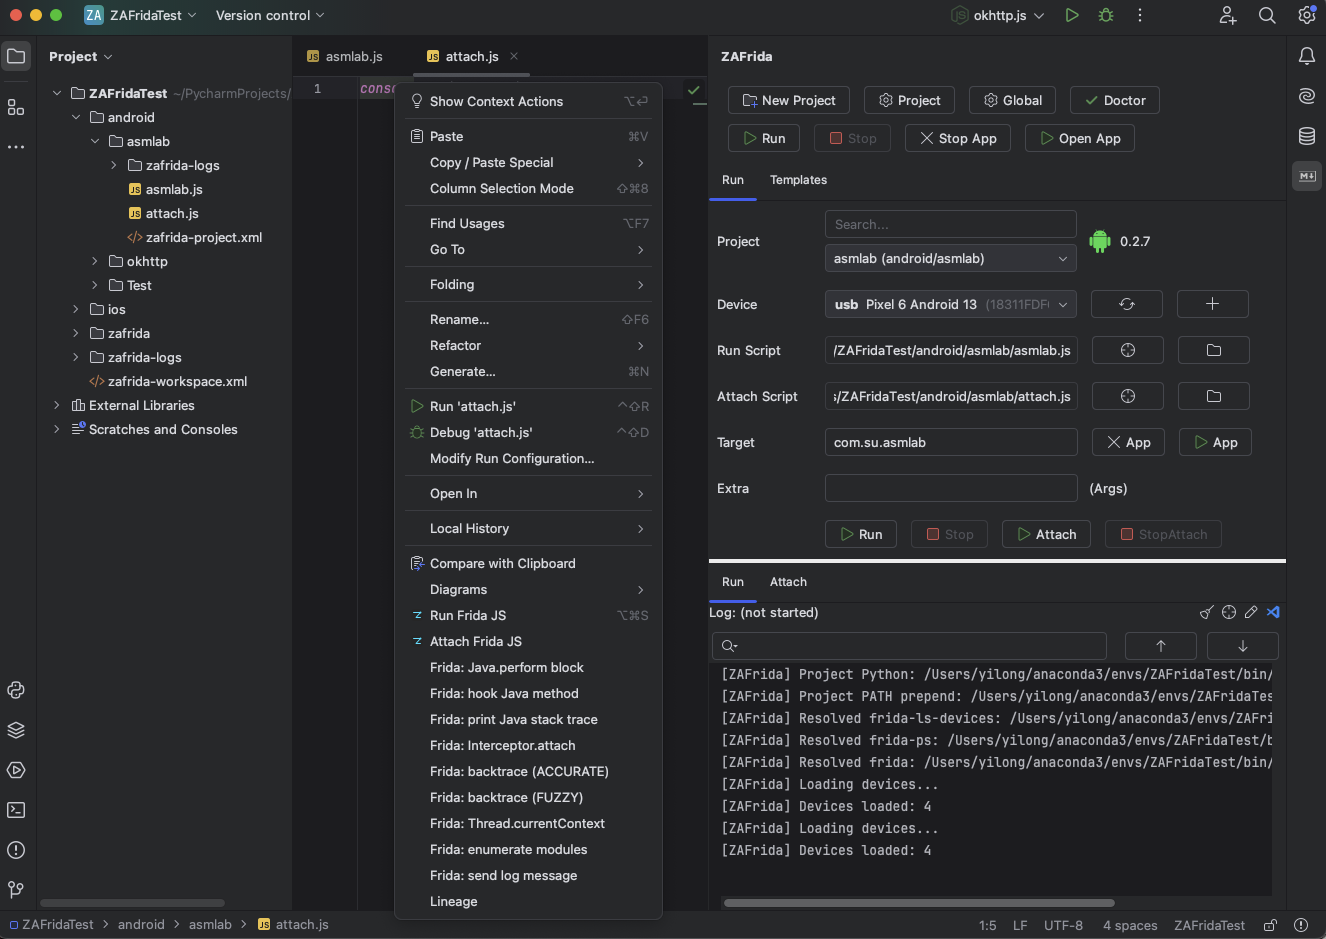 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.